-
-
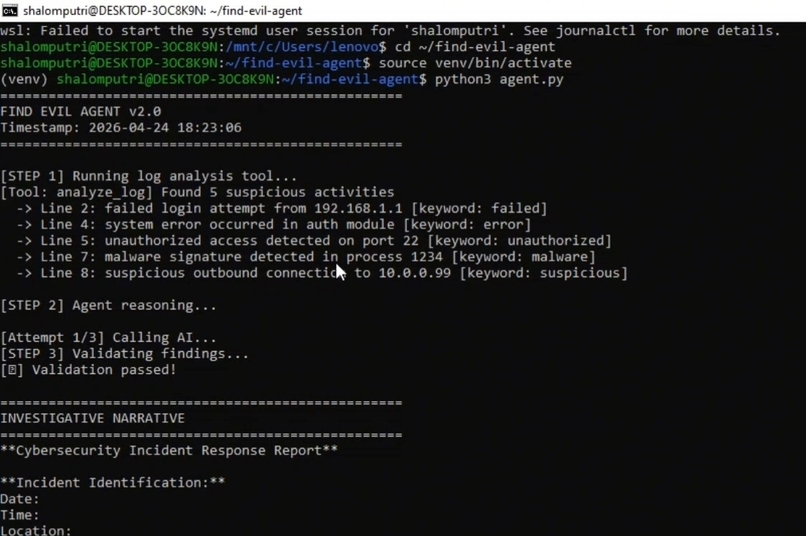
Running
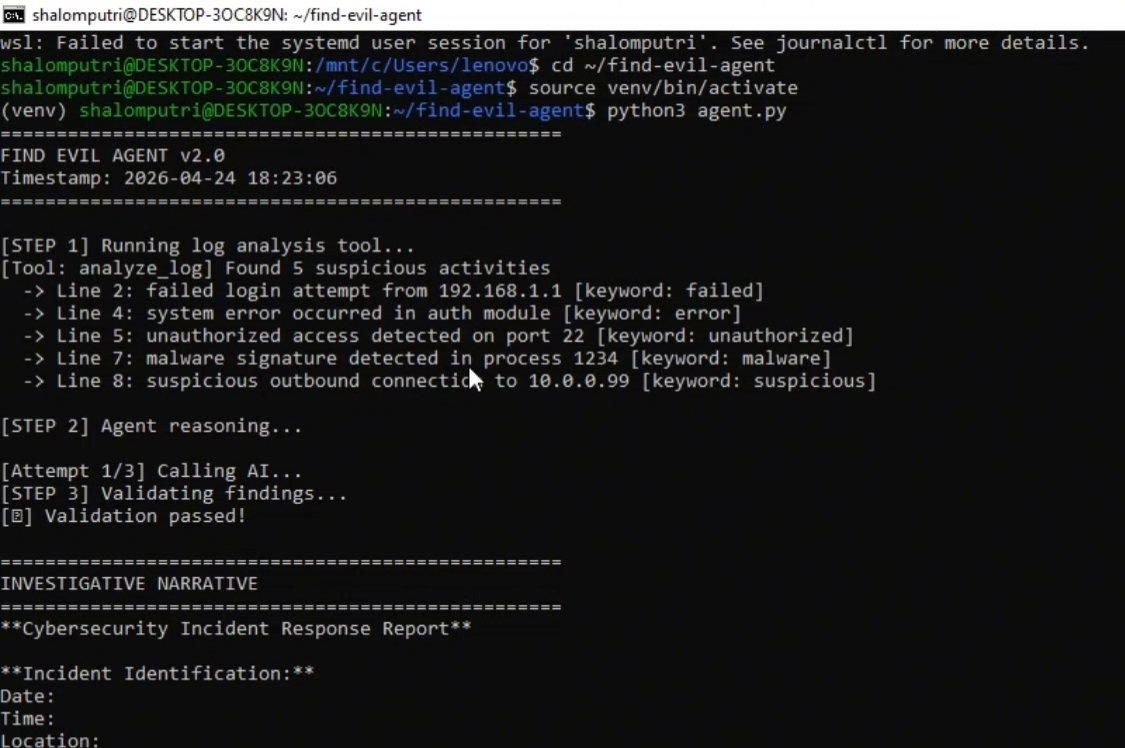
Inspiration
as a beginner in cybersecurity, i was inspired by the growing threat of cyber attacks that happen in minutes. i wanted to build something that could respond automatically. a defender that never sleeps.
What it does
find evil agent is an autonomous cybersecurity incident response agent that:
- analyzes system logs and detects suspicious activities with exact line-number tracking
- uses AI (Groq Llama 3.1) to generate structure investigative narratives -validates its own findings and self corrects if the AI response is inaccurate -export a complate JSON report for audit trail.
How we built it
-python 3.12 on ubuntu WSL2 (windows) -Groq API with Llama 3.1 model for AI Reasoning -Custom log analysis tool with keyword detection -sel correction loop with up to 3 retry attempts -JSON report export for accuracy documentation
Challenges we ran into
-setting up WSL2 and resolving DNS connectivity issues -managing API rate limits during development -ensuring the AI validation logic was accurate and consistent
Accomplishments that we're proud of
-how autonomous AI agents work in cybersecurity -how to build self correcting AI systems -log analysis and incident response fundamentals
What we learned
-support for more log formats (windows event logs, syslog) -real time log monitoring -web dashboard for visualization

Log in or sign up for Devpost to join the conversation.