Inspiration
A green pipeline does not prove that money is still correct.
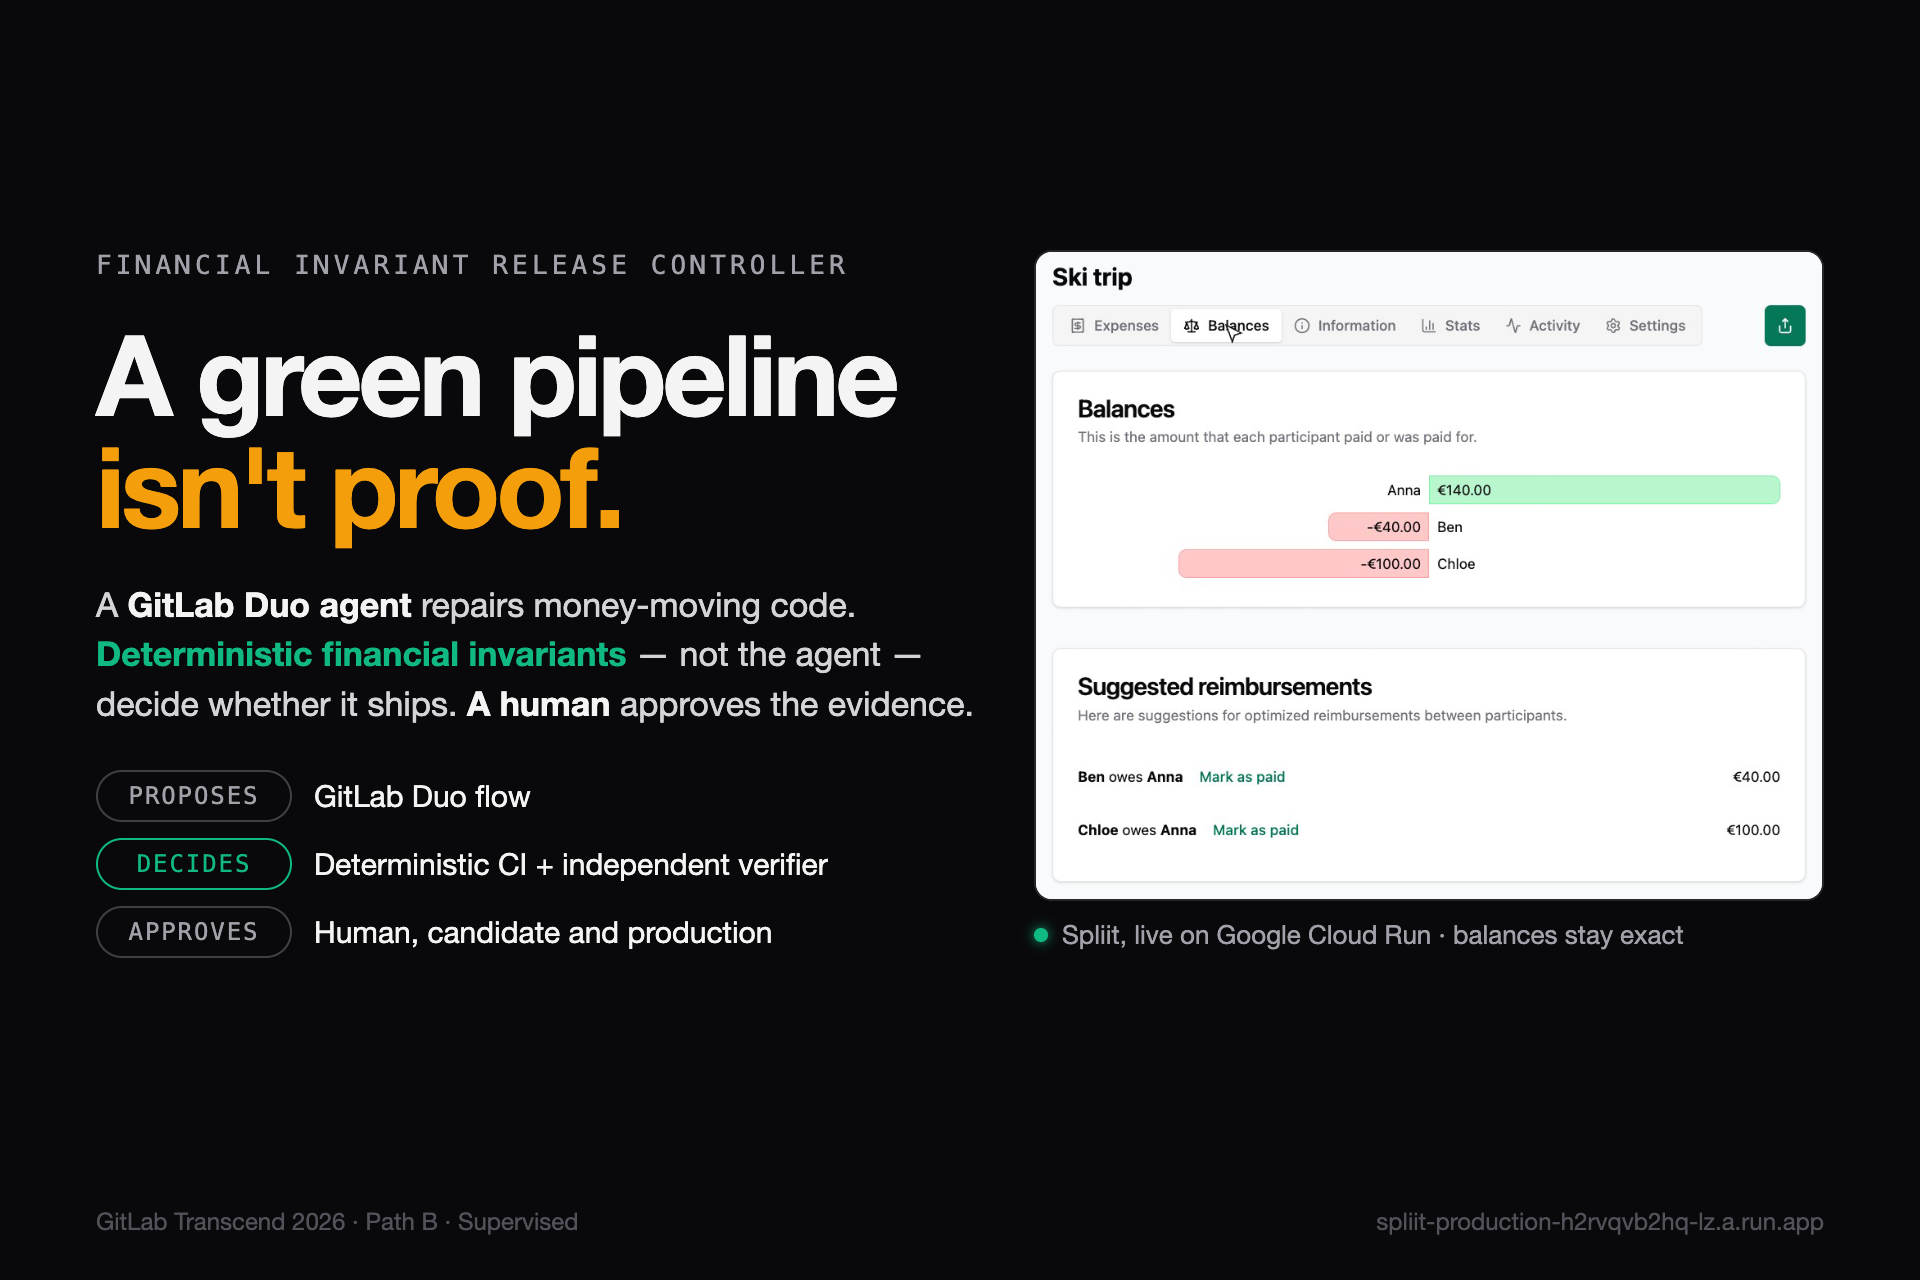
Financial Invariant Release Controller is a supervised GitLab Duo delivery system for small teams that maintain money-moving code: shared expenses, billing, credits, reimbursements, or ledger-like state.
A GitLab Duo agent can repair code, but it is never trusted to decide whether the release is safe. Deterministic financial invariants, protected policy, an independent verifier, and two human approvals decide that.
Path B · Bring Your Own · Supervised · deployed on Google Cloud Run
Inspiration
Traditional CI answers: “Does the code build?”
Financial systems need a harder answer: “After this change, is the money still correct?”
This matters even more with coding agents. An agent can make a pipeline green by weakening the assertion that would have caught its mistake. We wanted a release path where an agent does useful work, while code—not the model—remains the release authority.
What it does
We brought the MIT-licensed expense-sharing app Spliit to GitLab and added a supervised financial release controller.
Before: expense creation and the audit Activity were independent writes. A failed command could leave a false audit event. A retry could create duplicate financial state or fail after a write had already happened.
After:
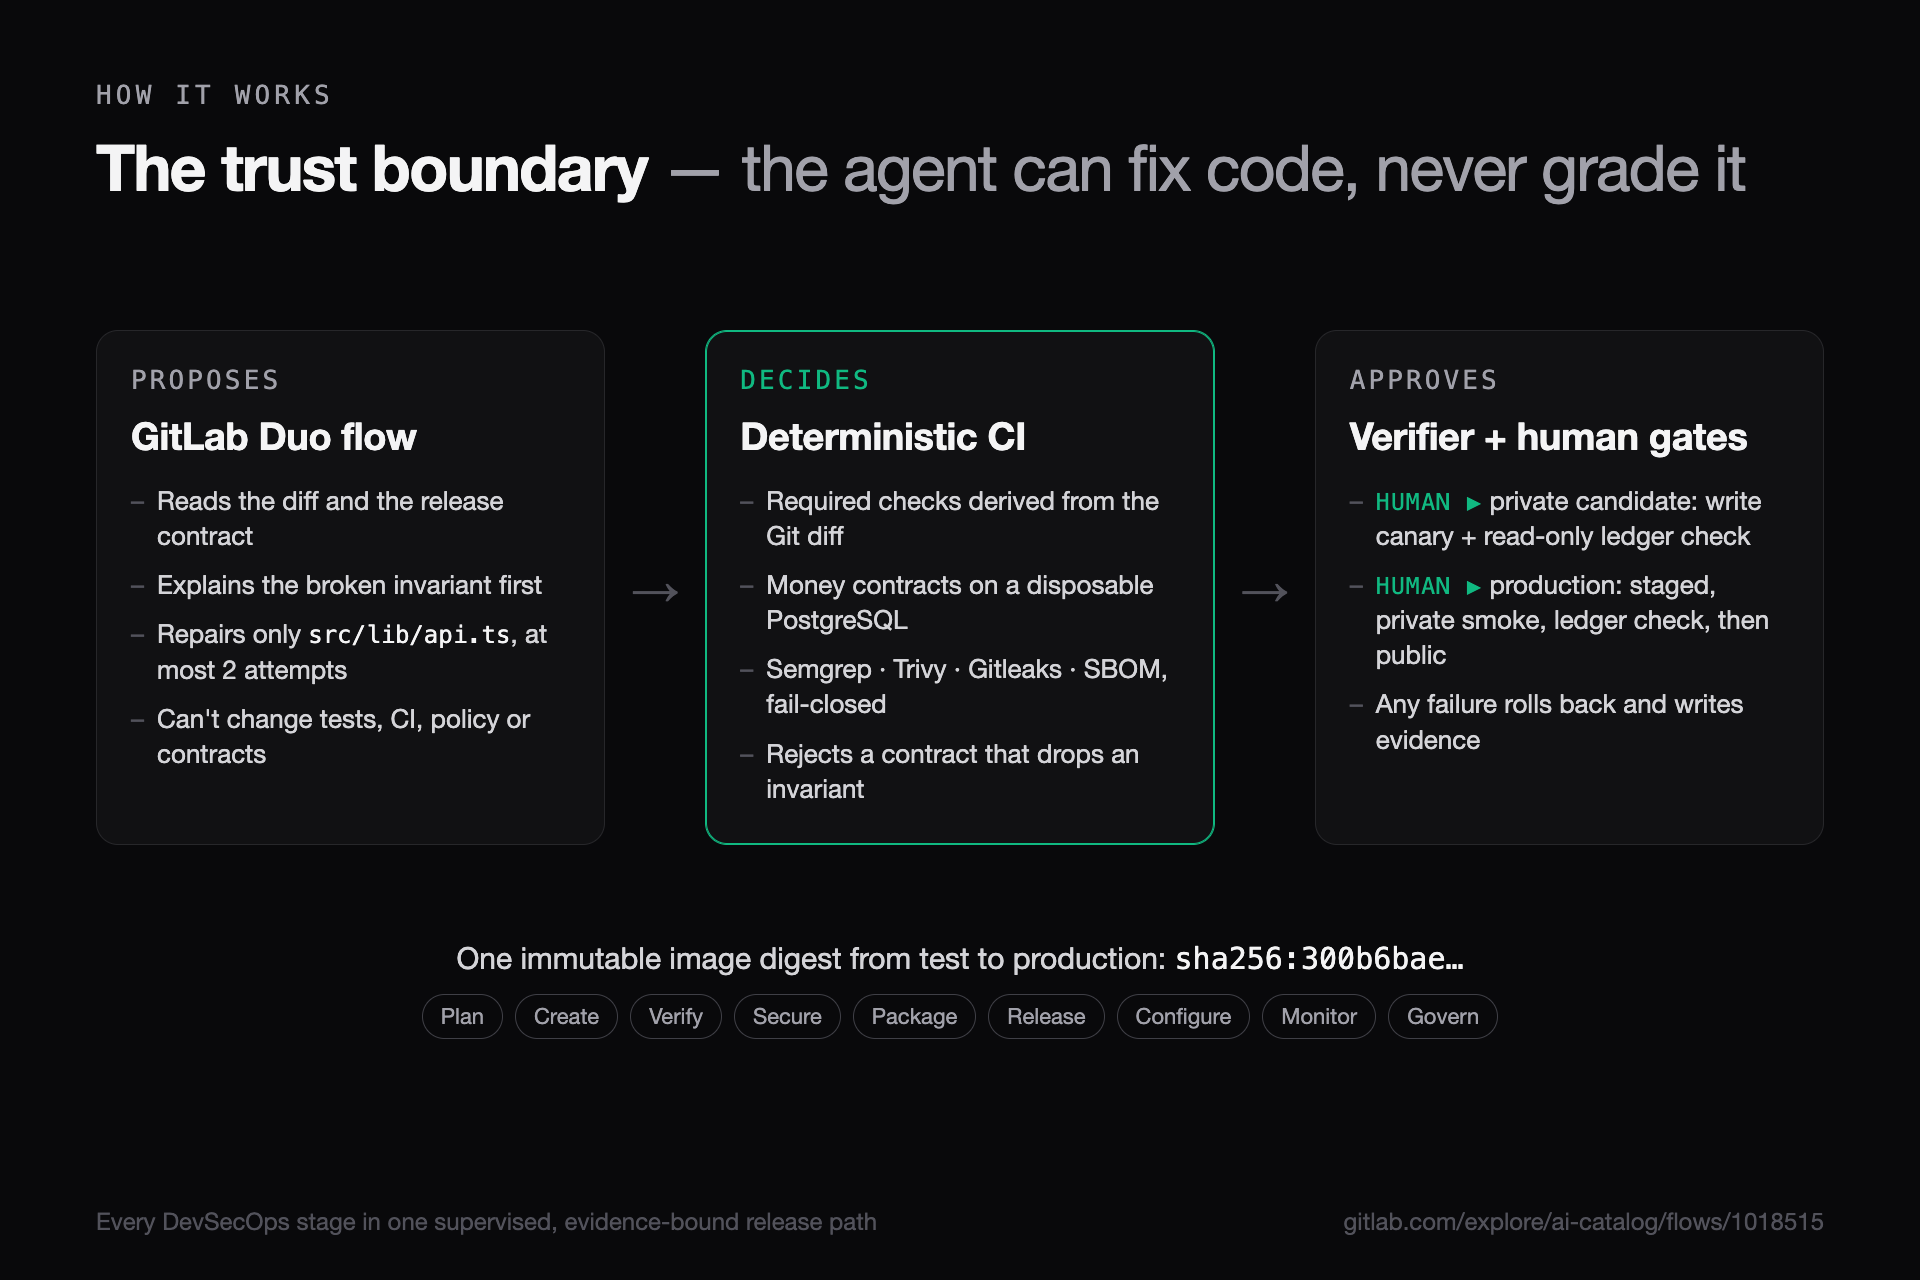
- A GitLab Duo custom flow reads the merge request, failure evidence, and release contract. It identifies the affected financial invariant and makes the smallest permitted repair.
- The repair is constrained: one source file, a bounded number of attempts, and no access to tests, CI, policy, contracts, or infrastructure.
- Deterministic CI derives mandatory checks from the Git diff—not from the agent’s opinion. It runs disposable-PostgreSQL regressions, migration rehearsal, security checks, and contract verification.
- An independent verifier project rebuilds and tests the exact reviewed candidate, then binds its verdict to immutable application and contract-runner image digests.
- A human starts a private Cloud Run candidate promotion. A write canary retries the same expense command and requires exactly one expense and one audit event. A read-only verifier checks financial invariants.
- A second human approval starts production. The same immutable digest is staged with no traffic, smoke-tested privately, verified against the production ledger, and only then exposed publicly.
Why it is different
The innovation is the trust boundary:
Agents act. Code decides. Humans approve evidence.
The agent can propose and implement a repair, but it cannot choose, weaken, or grade the checks that authorize its own release.
- The Git diff determines which invariants are mandatory.
- Policy is monotonic: an agent may tighten a release contract, never weaken it.
- Agent-authored changes to tests, policy, CI, contracts, or infrastructure fail closed.
- A separate verifier independently validates the reviewed source tree and exact image digest.
- Candidate and production are distinct supervised approvals.
Real evidence
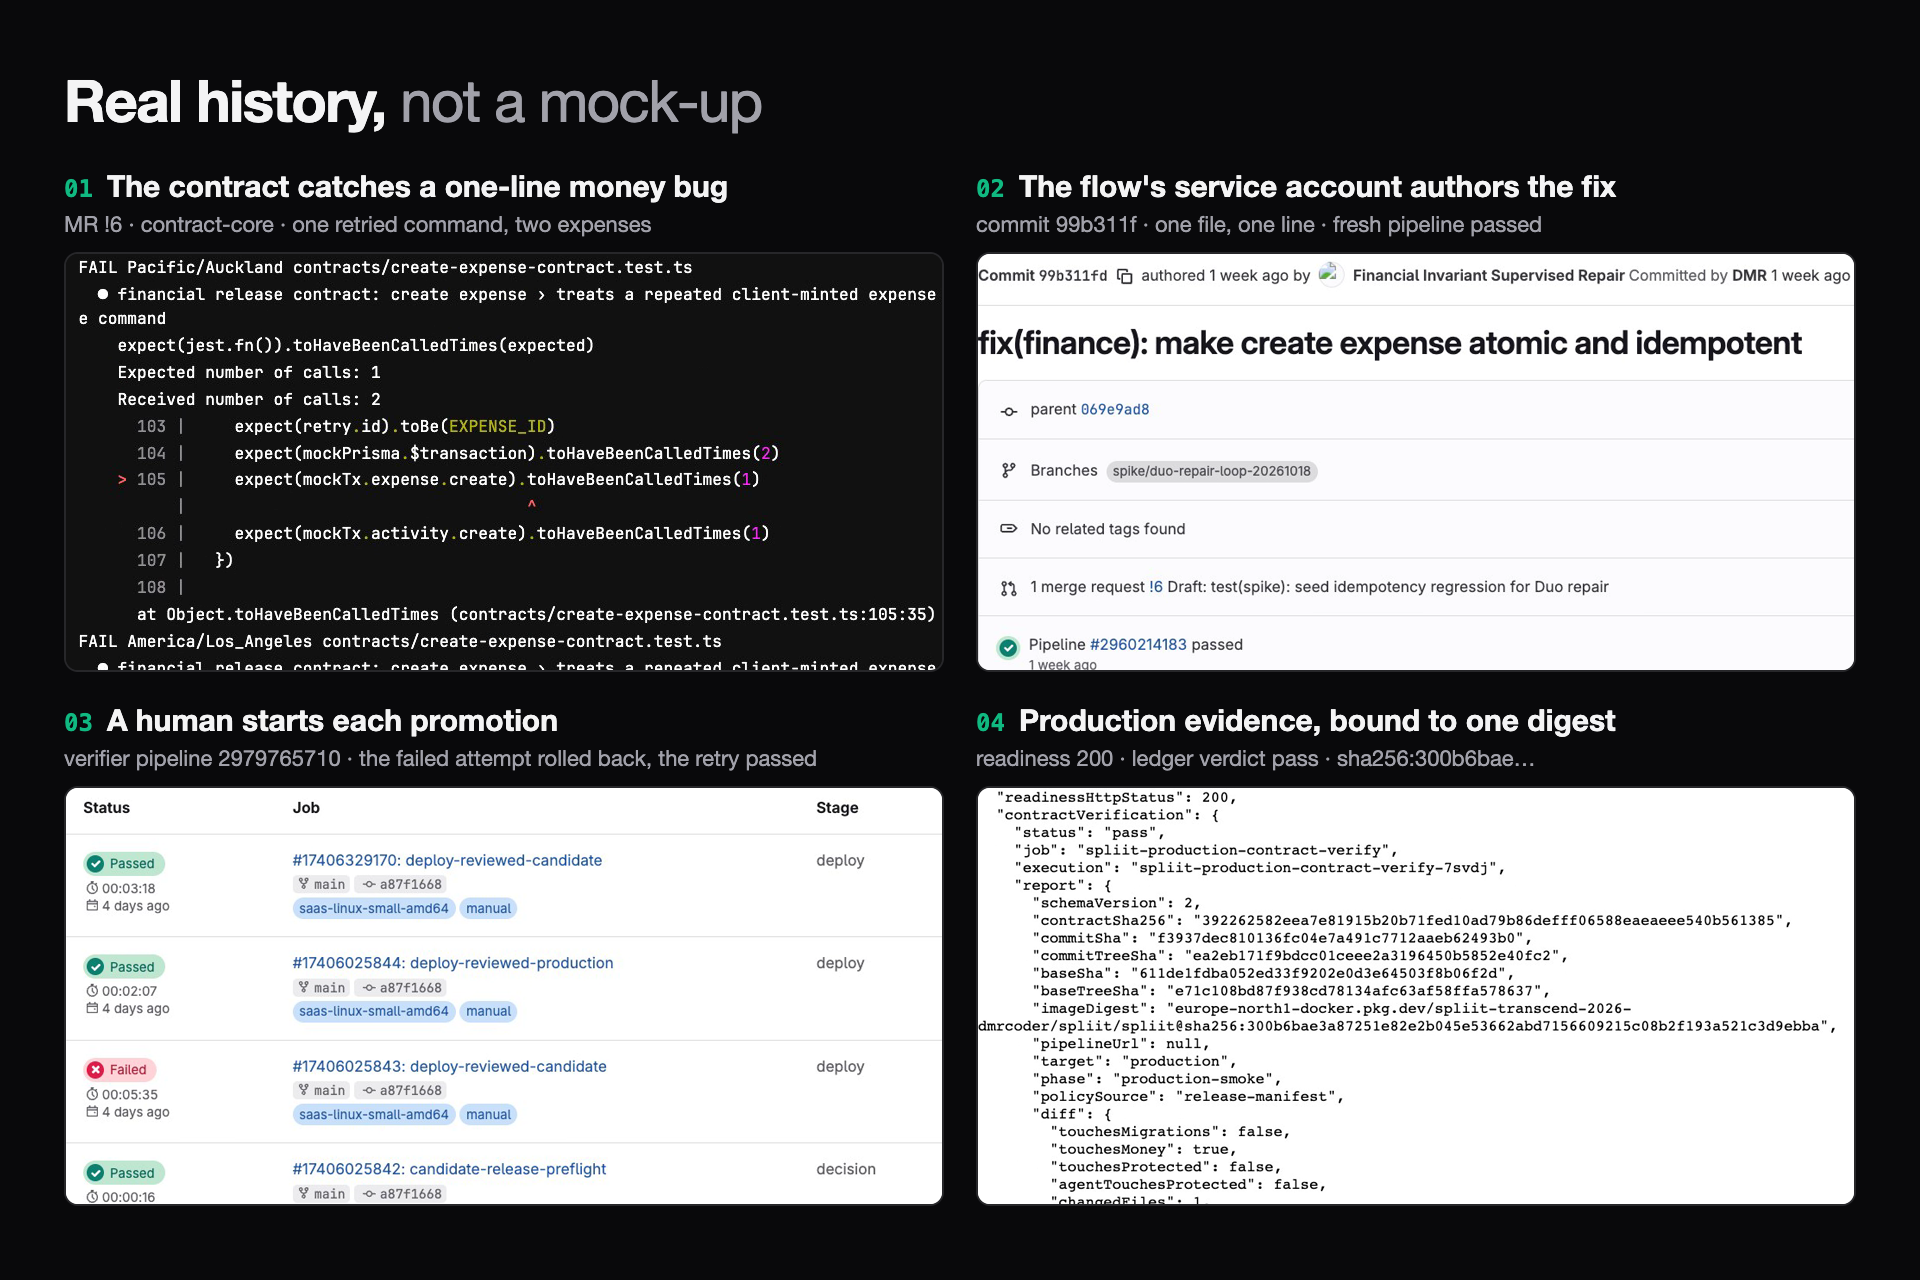
This is not a mock pipeline or a generated diagram.
- The public GitLab Duo flow defines the Financial Invariant Release Controller.
- A real Duo service account repaired the idempotency regression on MR !6.
- A fresh independent pipeline verified the repair rather than trusting the agent’s own report.
- The real verifier release pipeline promoted the reviewed candidate to production.
- Candidate and production evidence show the same immutable image digest, financial verdicts, and separate promotion decisions.
DevSecOps lifecycle coverage
| Stage | Implementation |
|---|---|
| Plan | Human-reviewed release contract and merge-request risk context |
| Create | GitLab Duo Financial Invariant Repair flow |
| Verify | Diff-derived contracts, disposable PostgreSQL regressions, migration rehearsal |
| Secure | Semgrep, Trivy, Gitleaks, CycloneDX SBOM, protected paths, WIF |
| Package | Immutable application and contract-runner digests |
| Release | Human-started candidate and production controllers |
| Configure | Terraform for Cloud Run, Cloud SQL, IAM, and budget controls |
| Monitor | Readiness, write canary, and read-only financial verifier jobs |
| Govern | Fail-closed policy, evidence artifacts, and promotion gates |
This is one connected supervised release path, not a collection of unrelated agent jobs.
Sustainability
Environmental evidence is measured rather than asserted. One supervised release is estimated at 4.7 gCO2e, using public GitLab job durations and measured Cloud Run / Cloud SQL activity. Cloud Run scale-to-zero avoids an estimated 0.43–1.6 kgCO2e over the judging period compared with minScale=1.
The model, assumptions, ranges, sources, and reproduction steps are public in the SCI report.
Built with
GitLab Duo Agent Platform, GitLab CI/CD, Google Cloud Run, Cloud SQL for PostgreSQL, Terraform, Workload Identity Federation, Next.js, Prisma, TypeScript, Semgrep, Trivy, Gitleaks, and CycloneDX.
What it does
How we built it
Challenges we ran into
Accomplishments that we're proud of
What we learned
What's next for Financial Invariant Release Controller
Built With
- ci/cd
- cloud
- duo
- federation
- gitlab
- gitleaks
- identity
- next.js
- node.js
- postgresql
- prisma
- run
- semgrep
- sql
- terraform
- trivy
- typescript
- workload

Log in or sign up for Devpost to join the conversation.