-
-
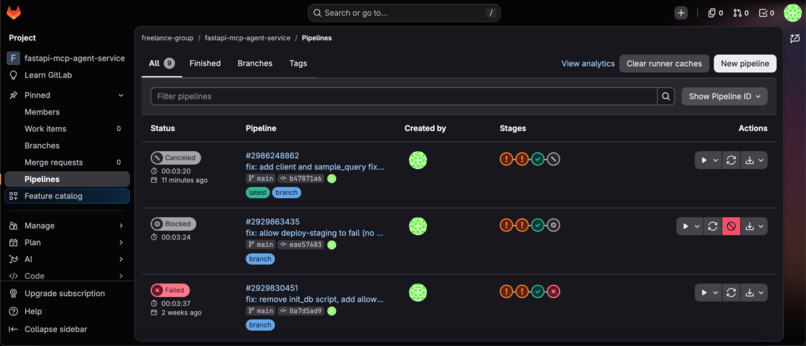
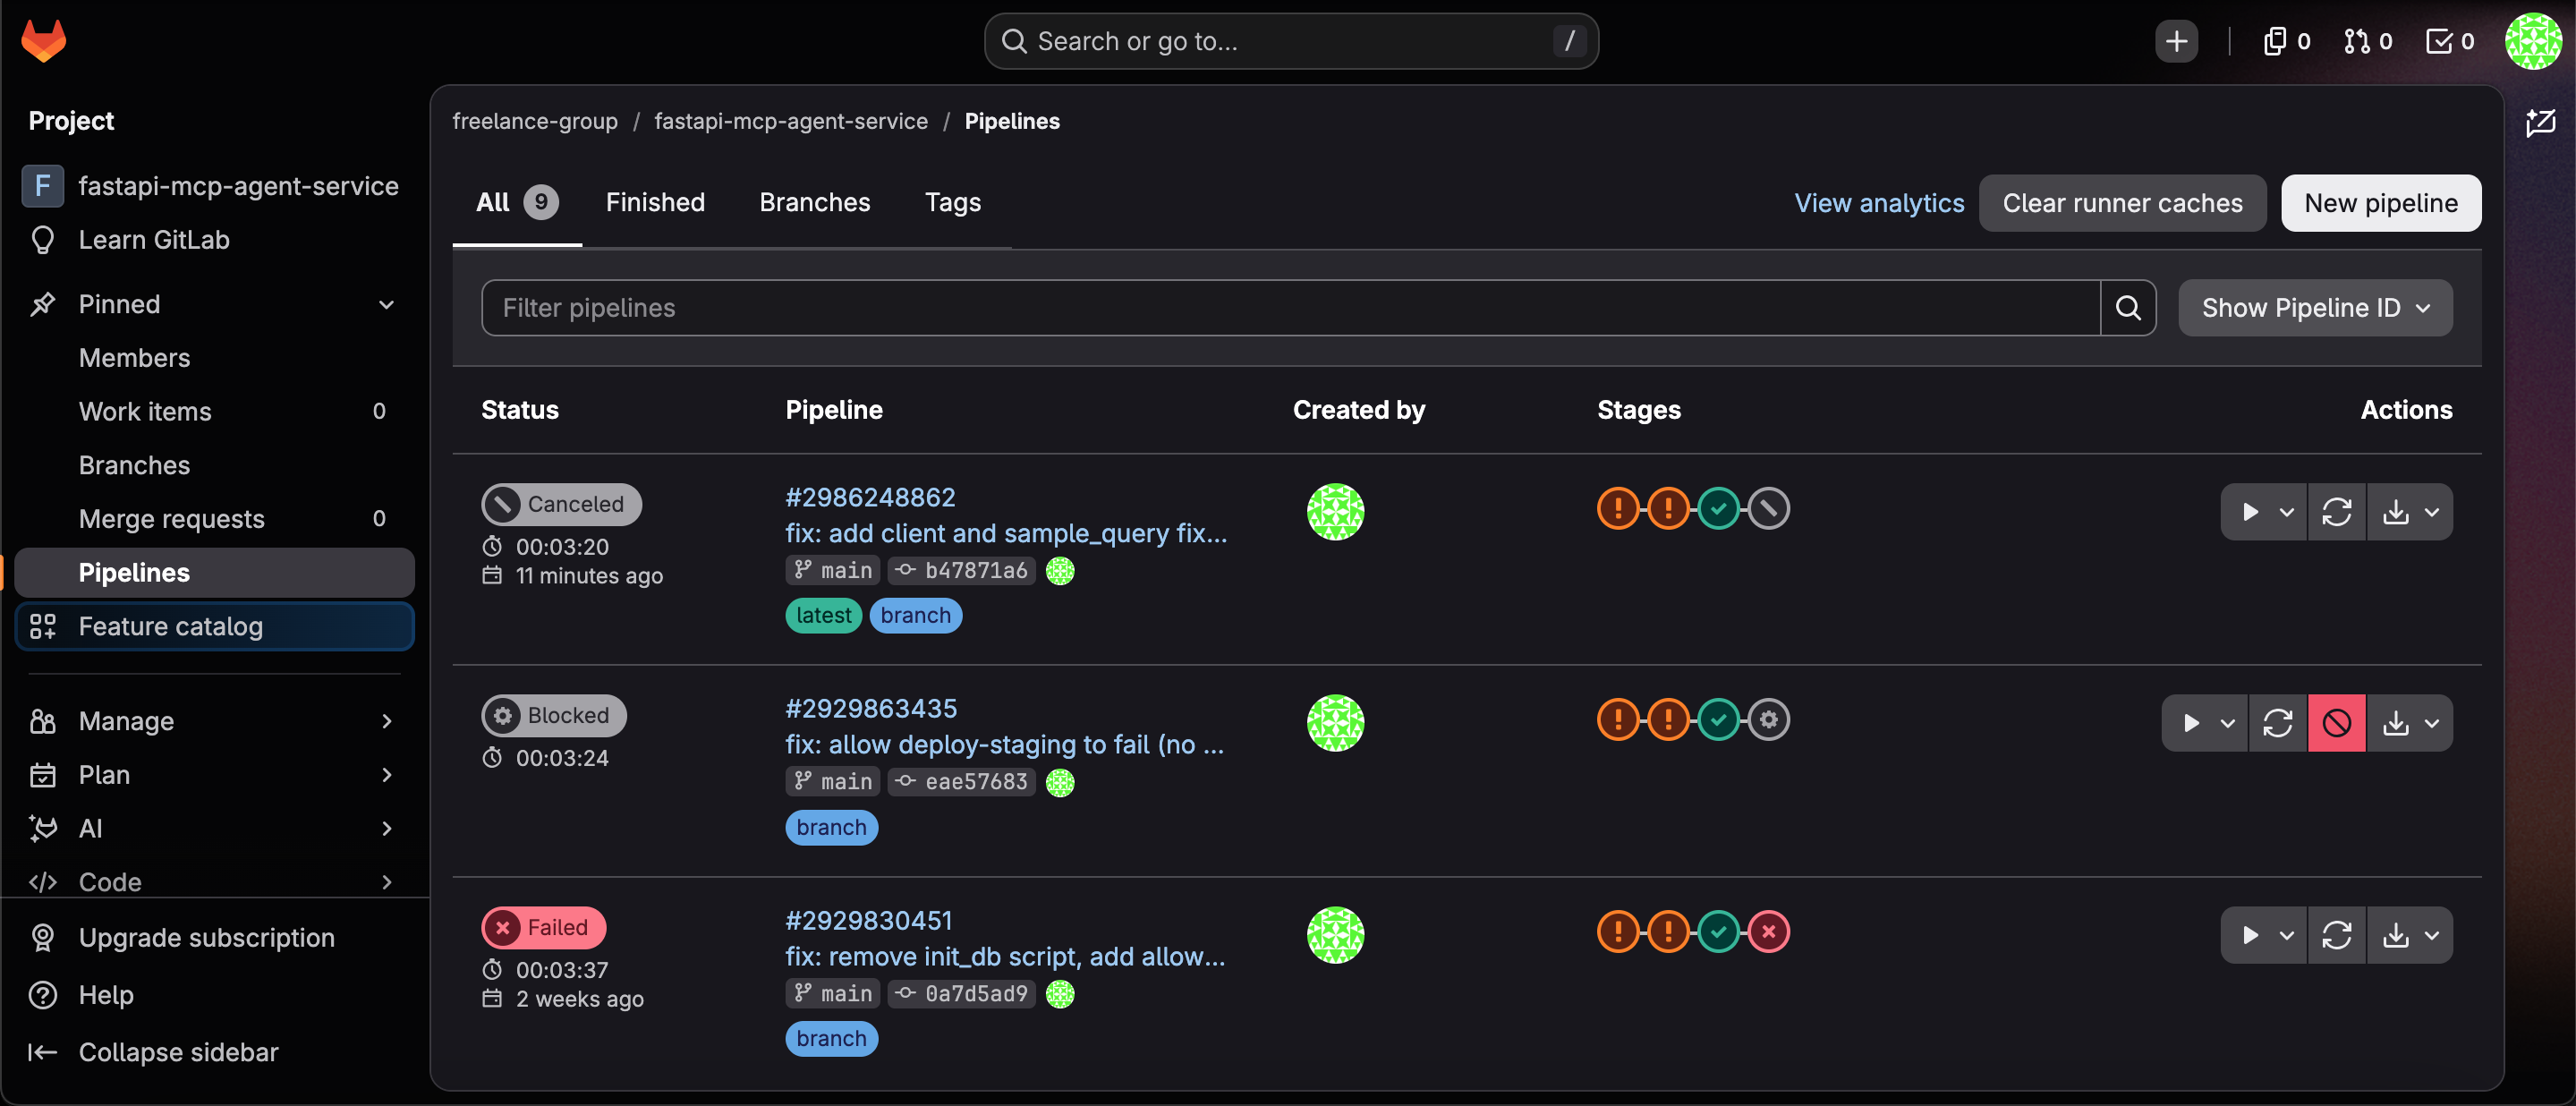
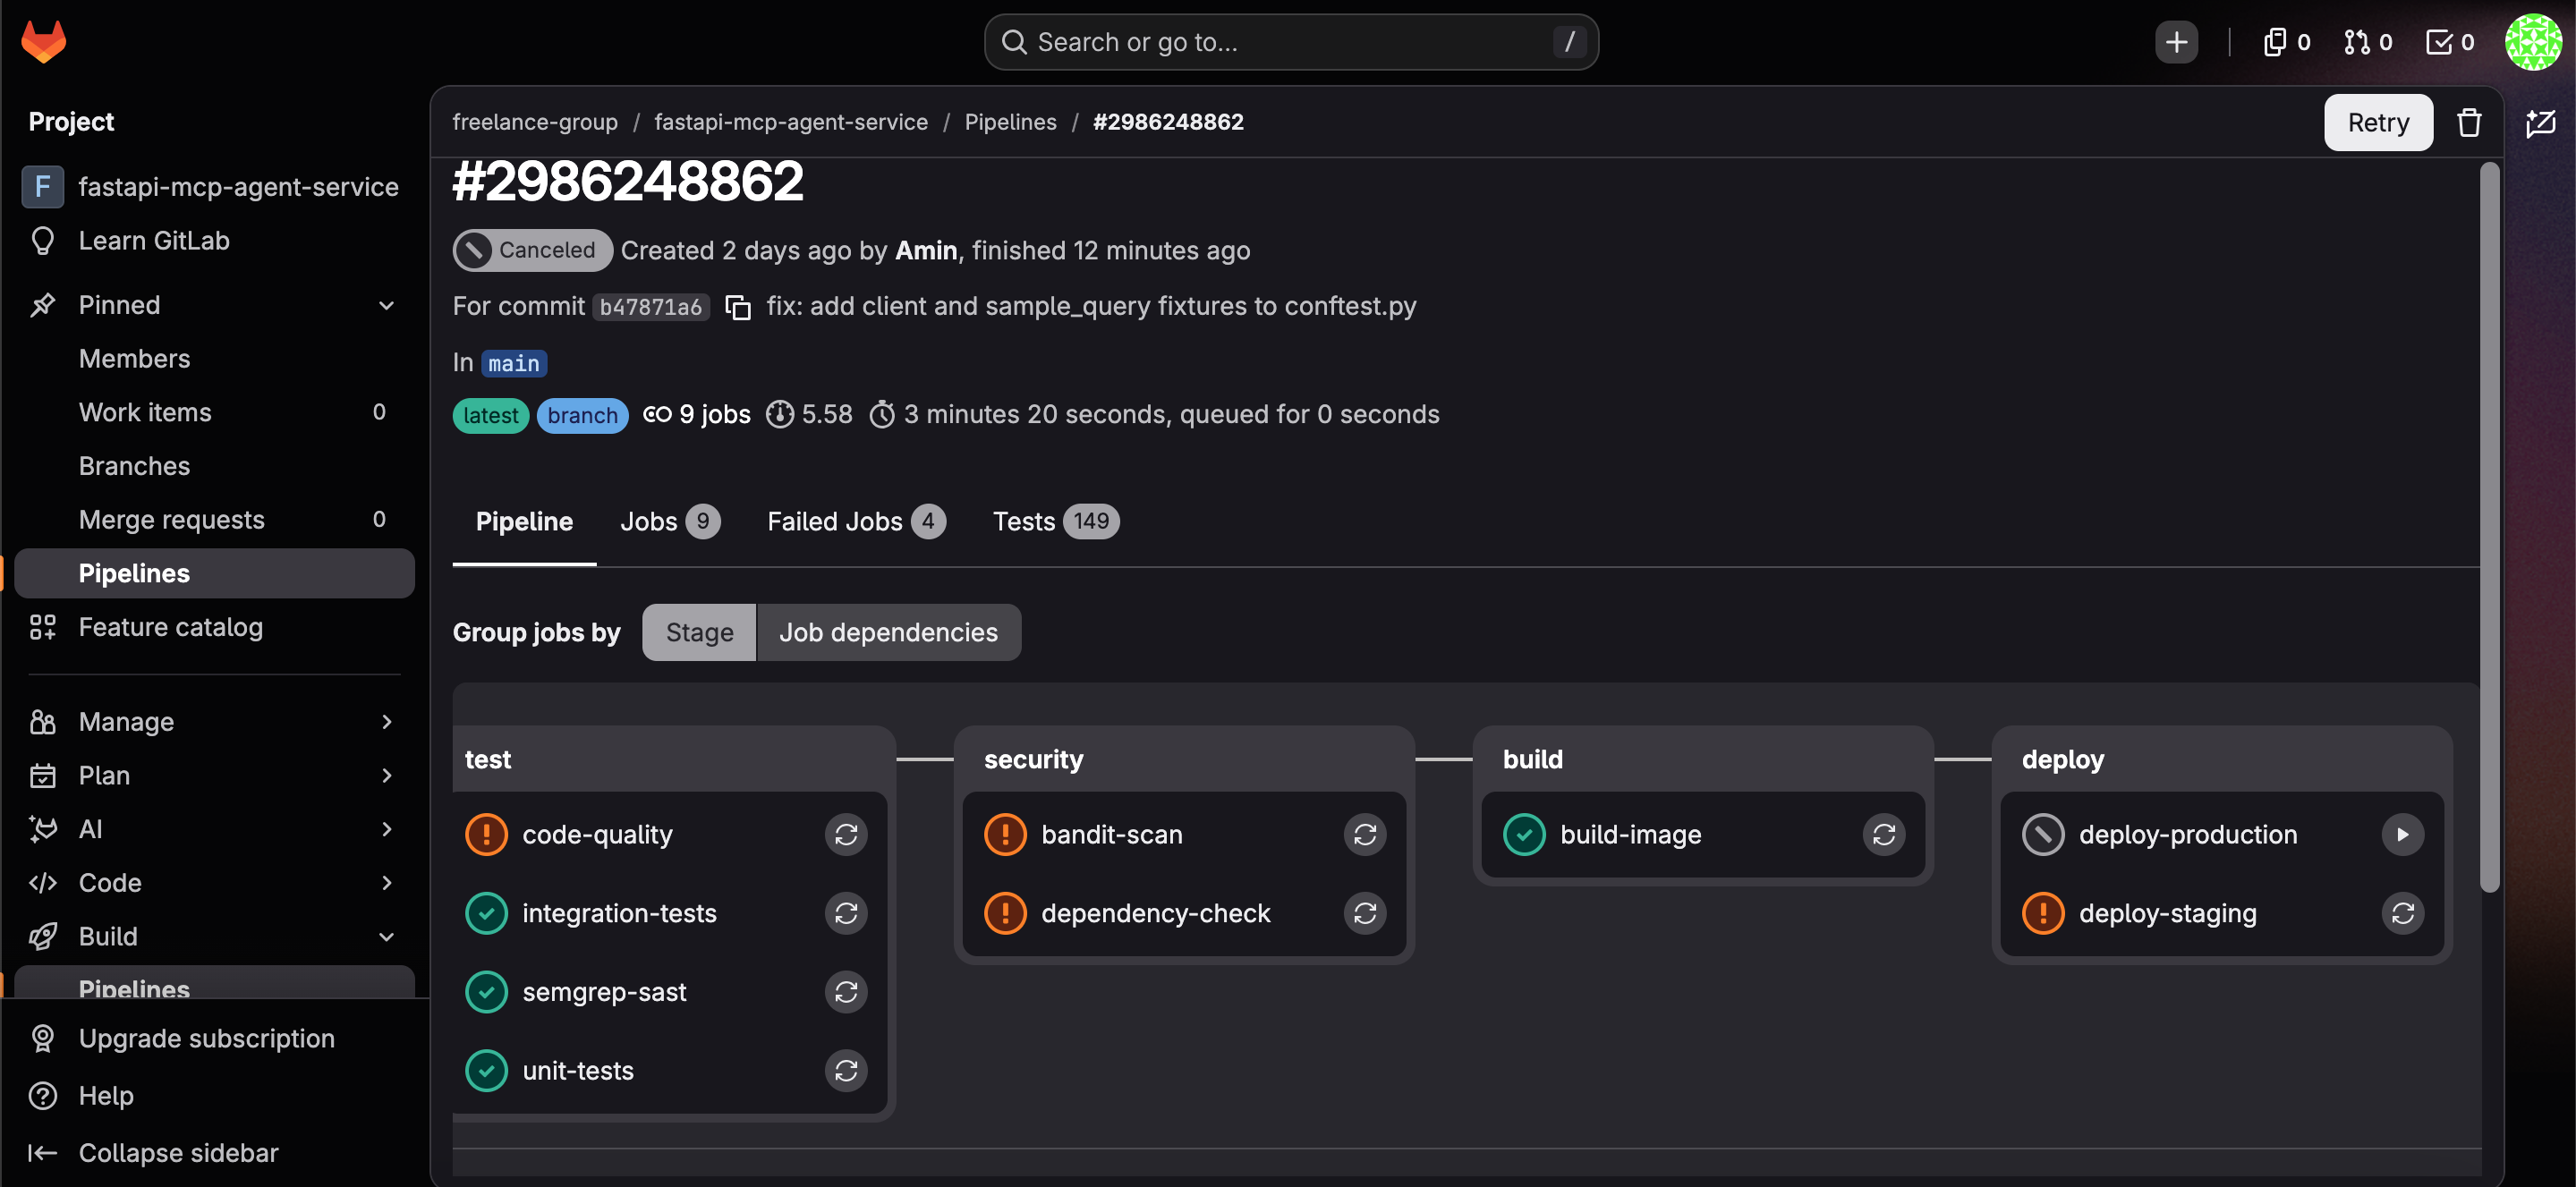
GitLab CI/CD pipeline showing automated test, security scan, build, and deploy stages triggered on each commit
-
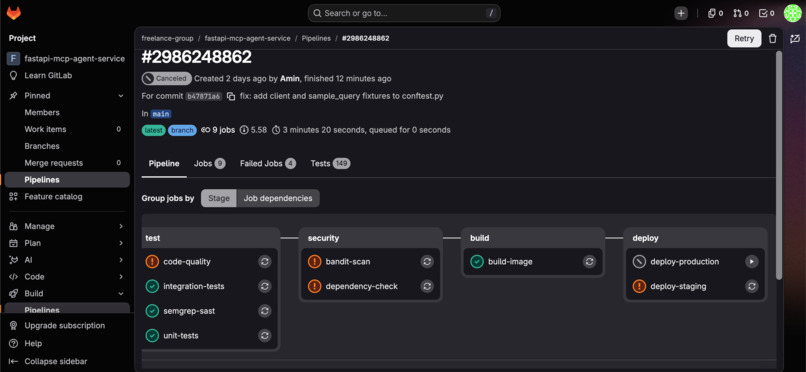
Merge request #25088 with all pipeline jobs passing – unit tests, Bandit security scan, and Docker build
-
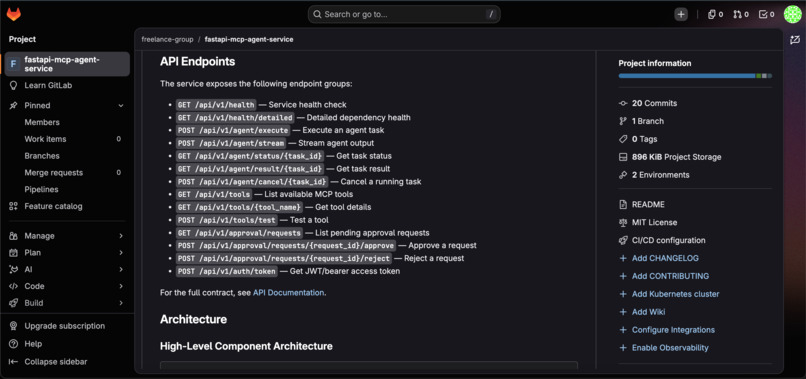
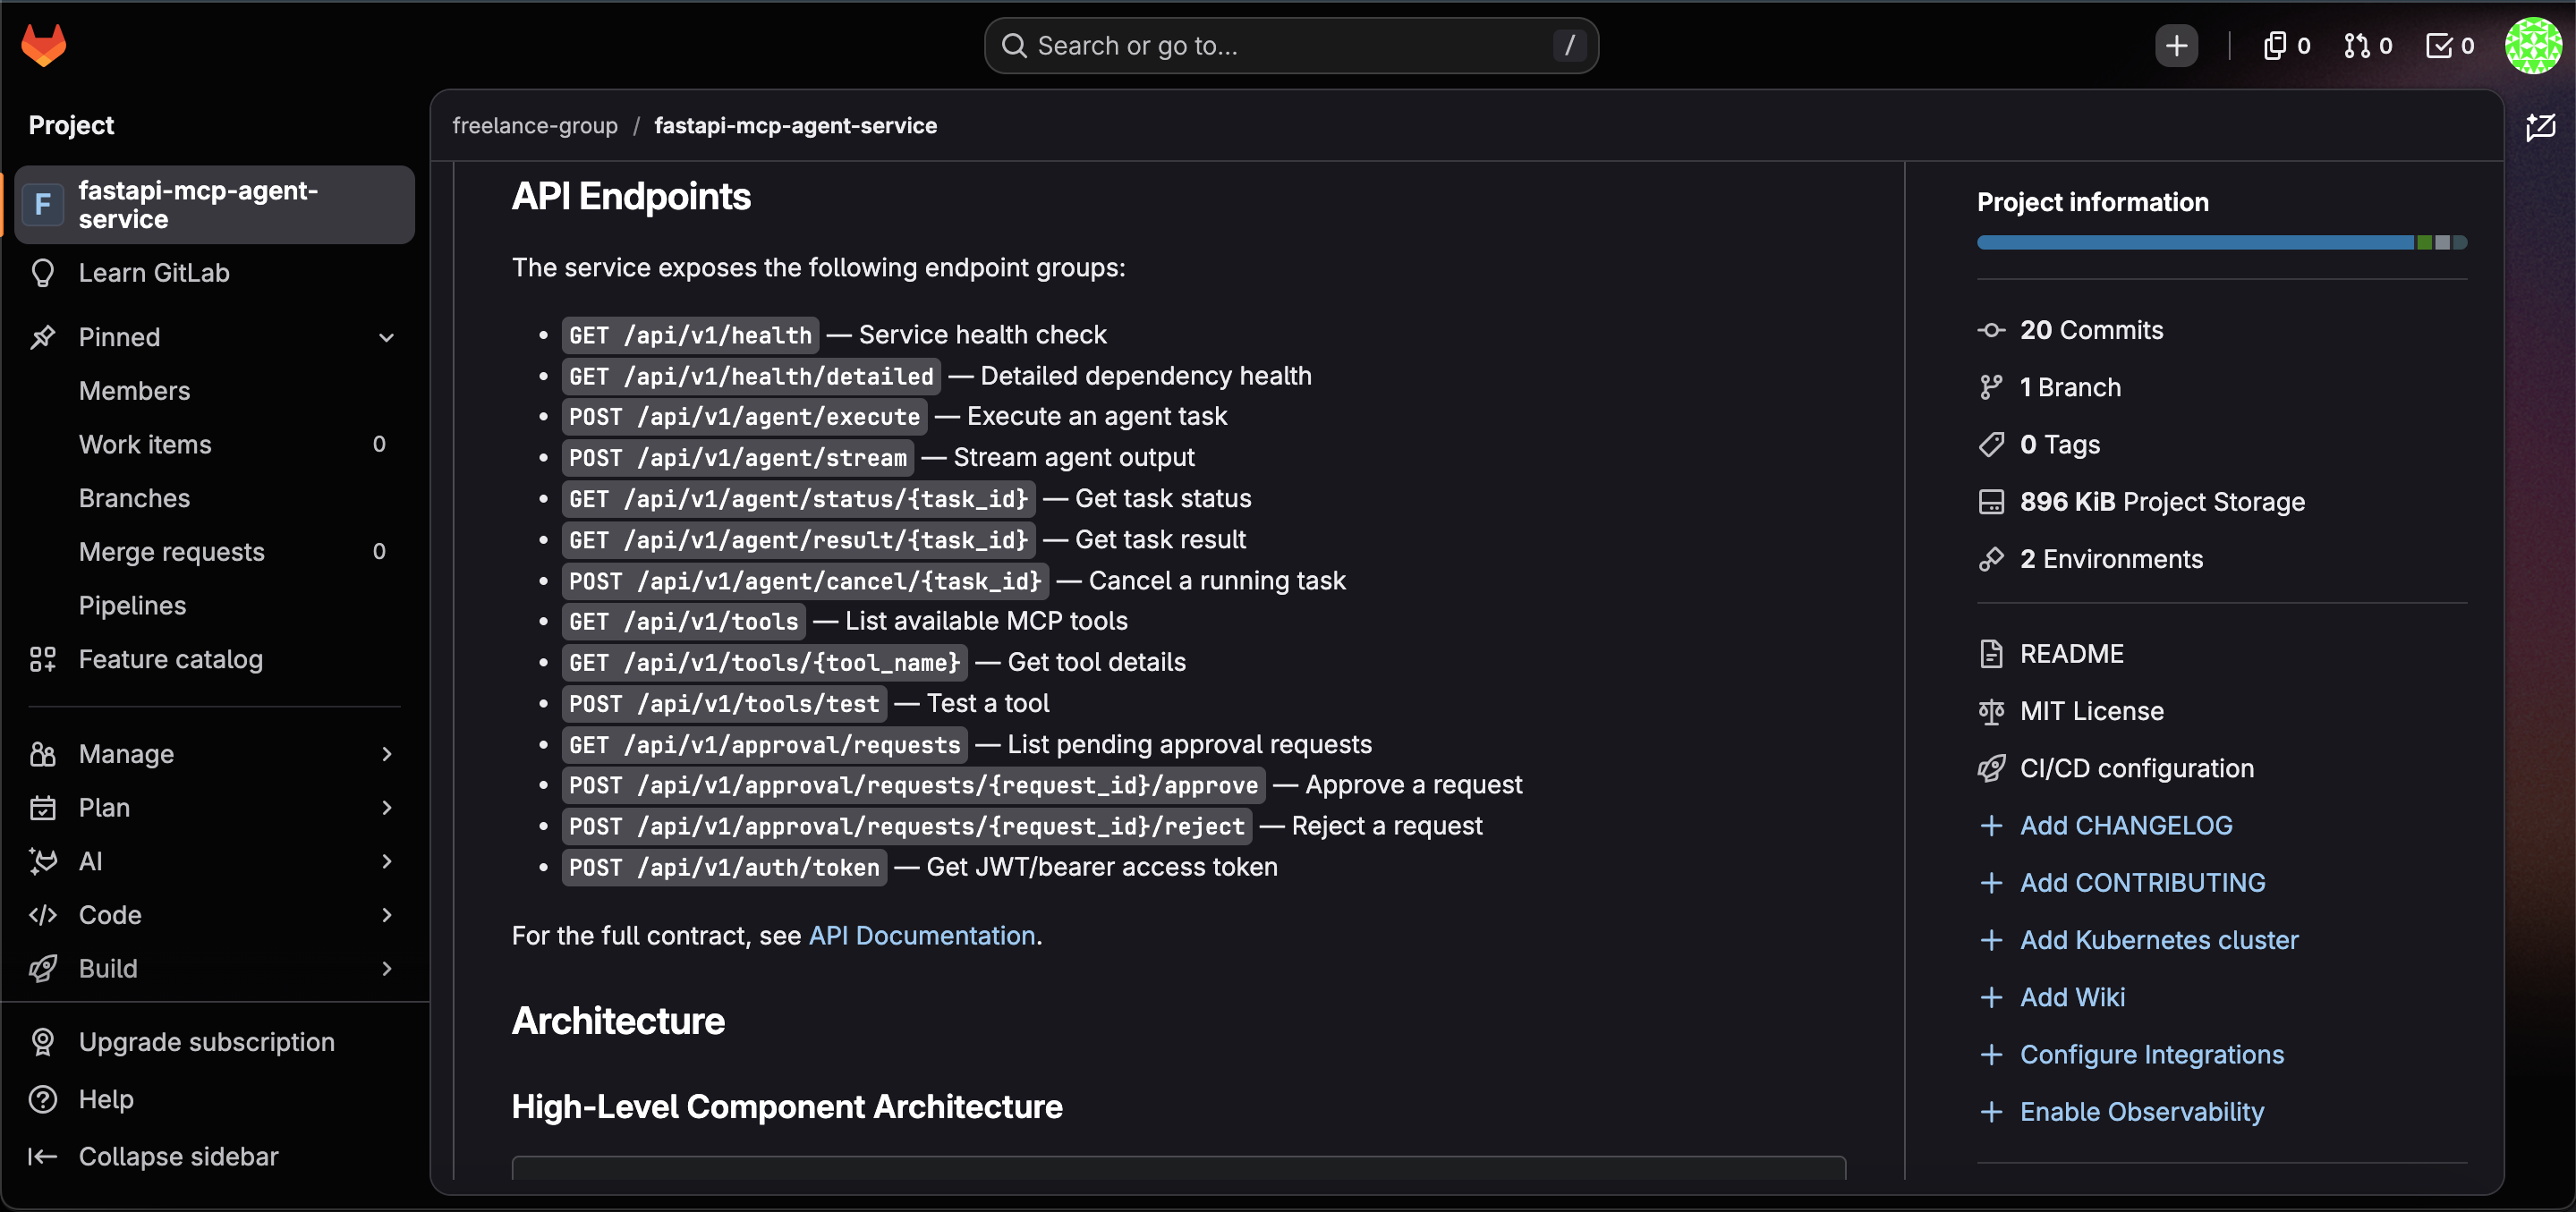
Complete list of MCP-exposed REST API endpoints available for AI agent integration and automation
-
Claude AI agent invoking MCP tools to trigger the full DevSecOps pipeline through the FastAPI service
-
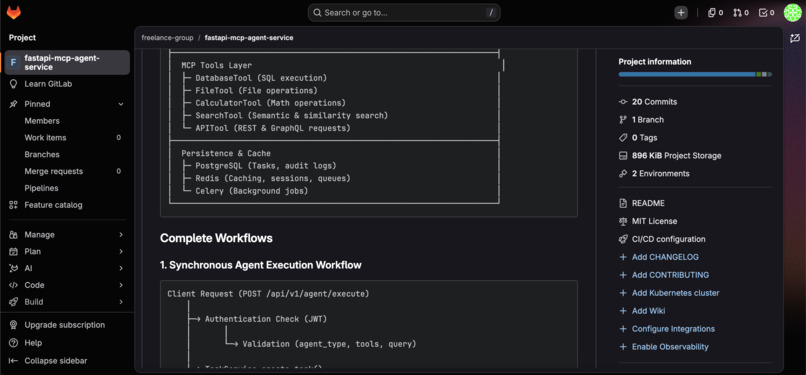
FastAPI service source code showing async endpoint handlers and MCP protocol integration layer
-
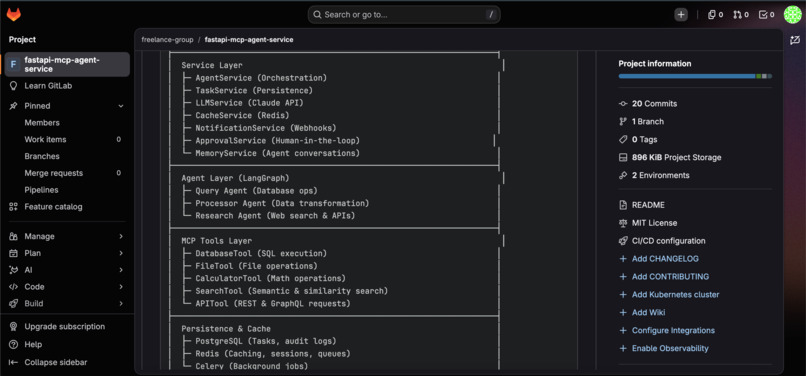
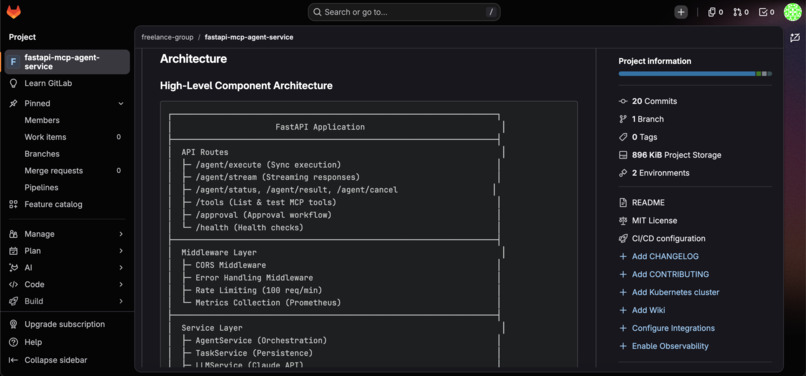
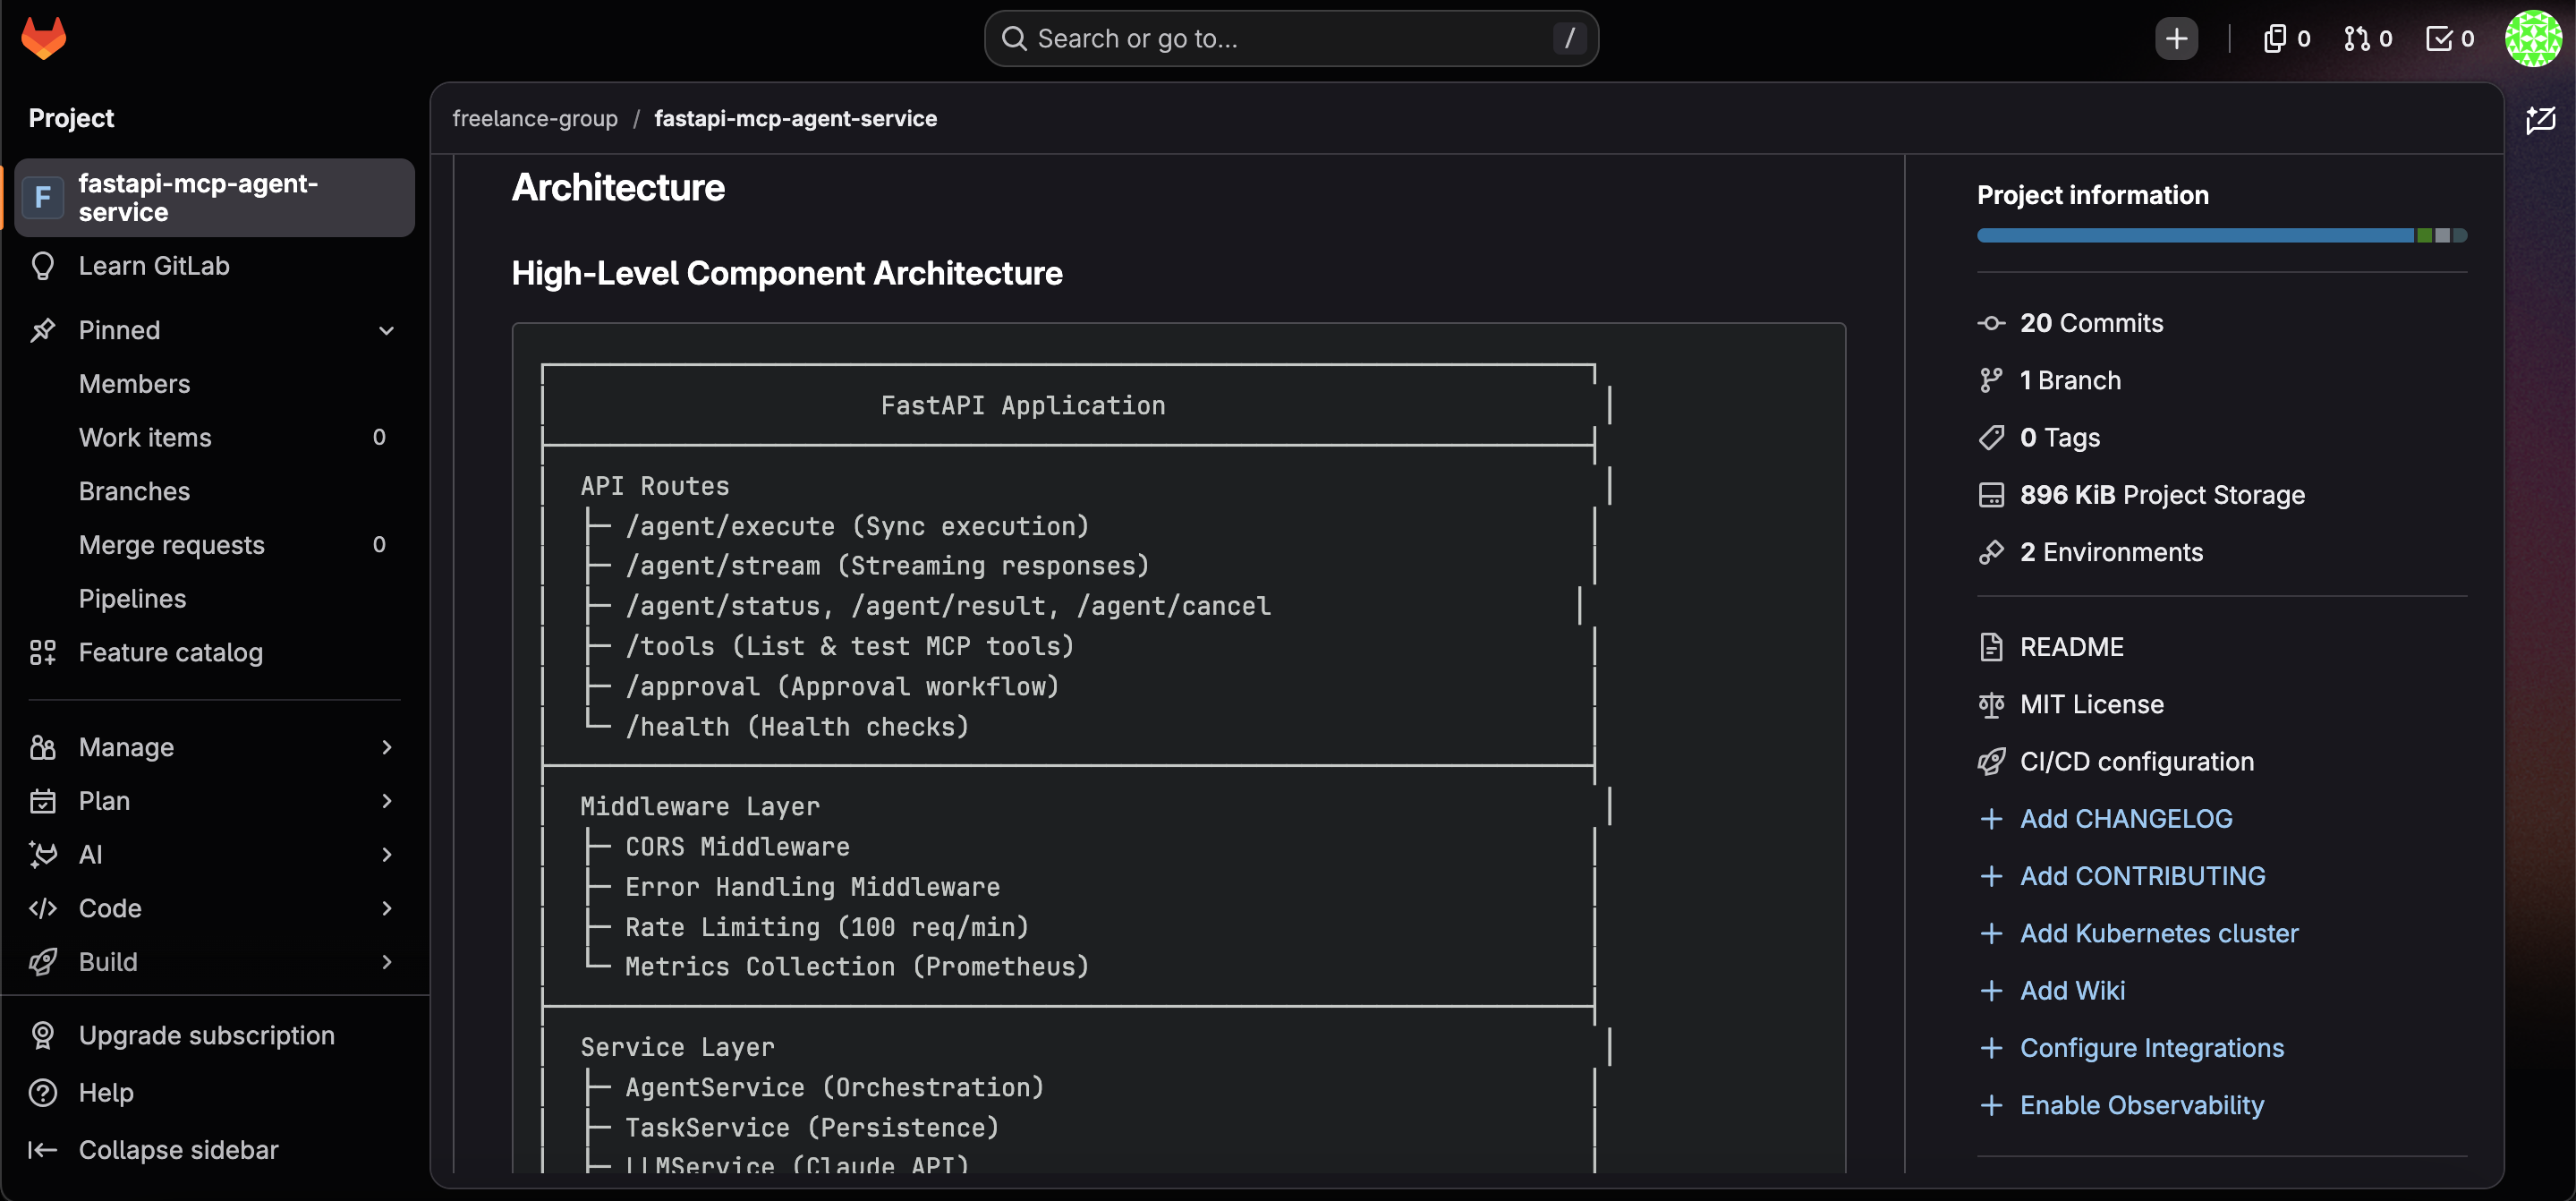
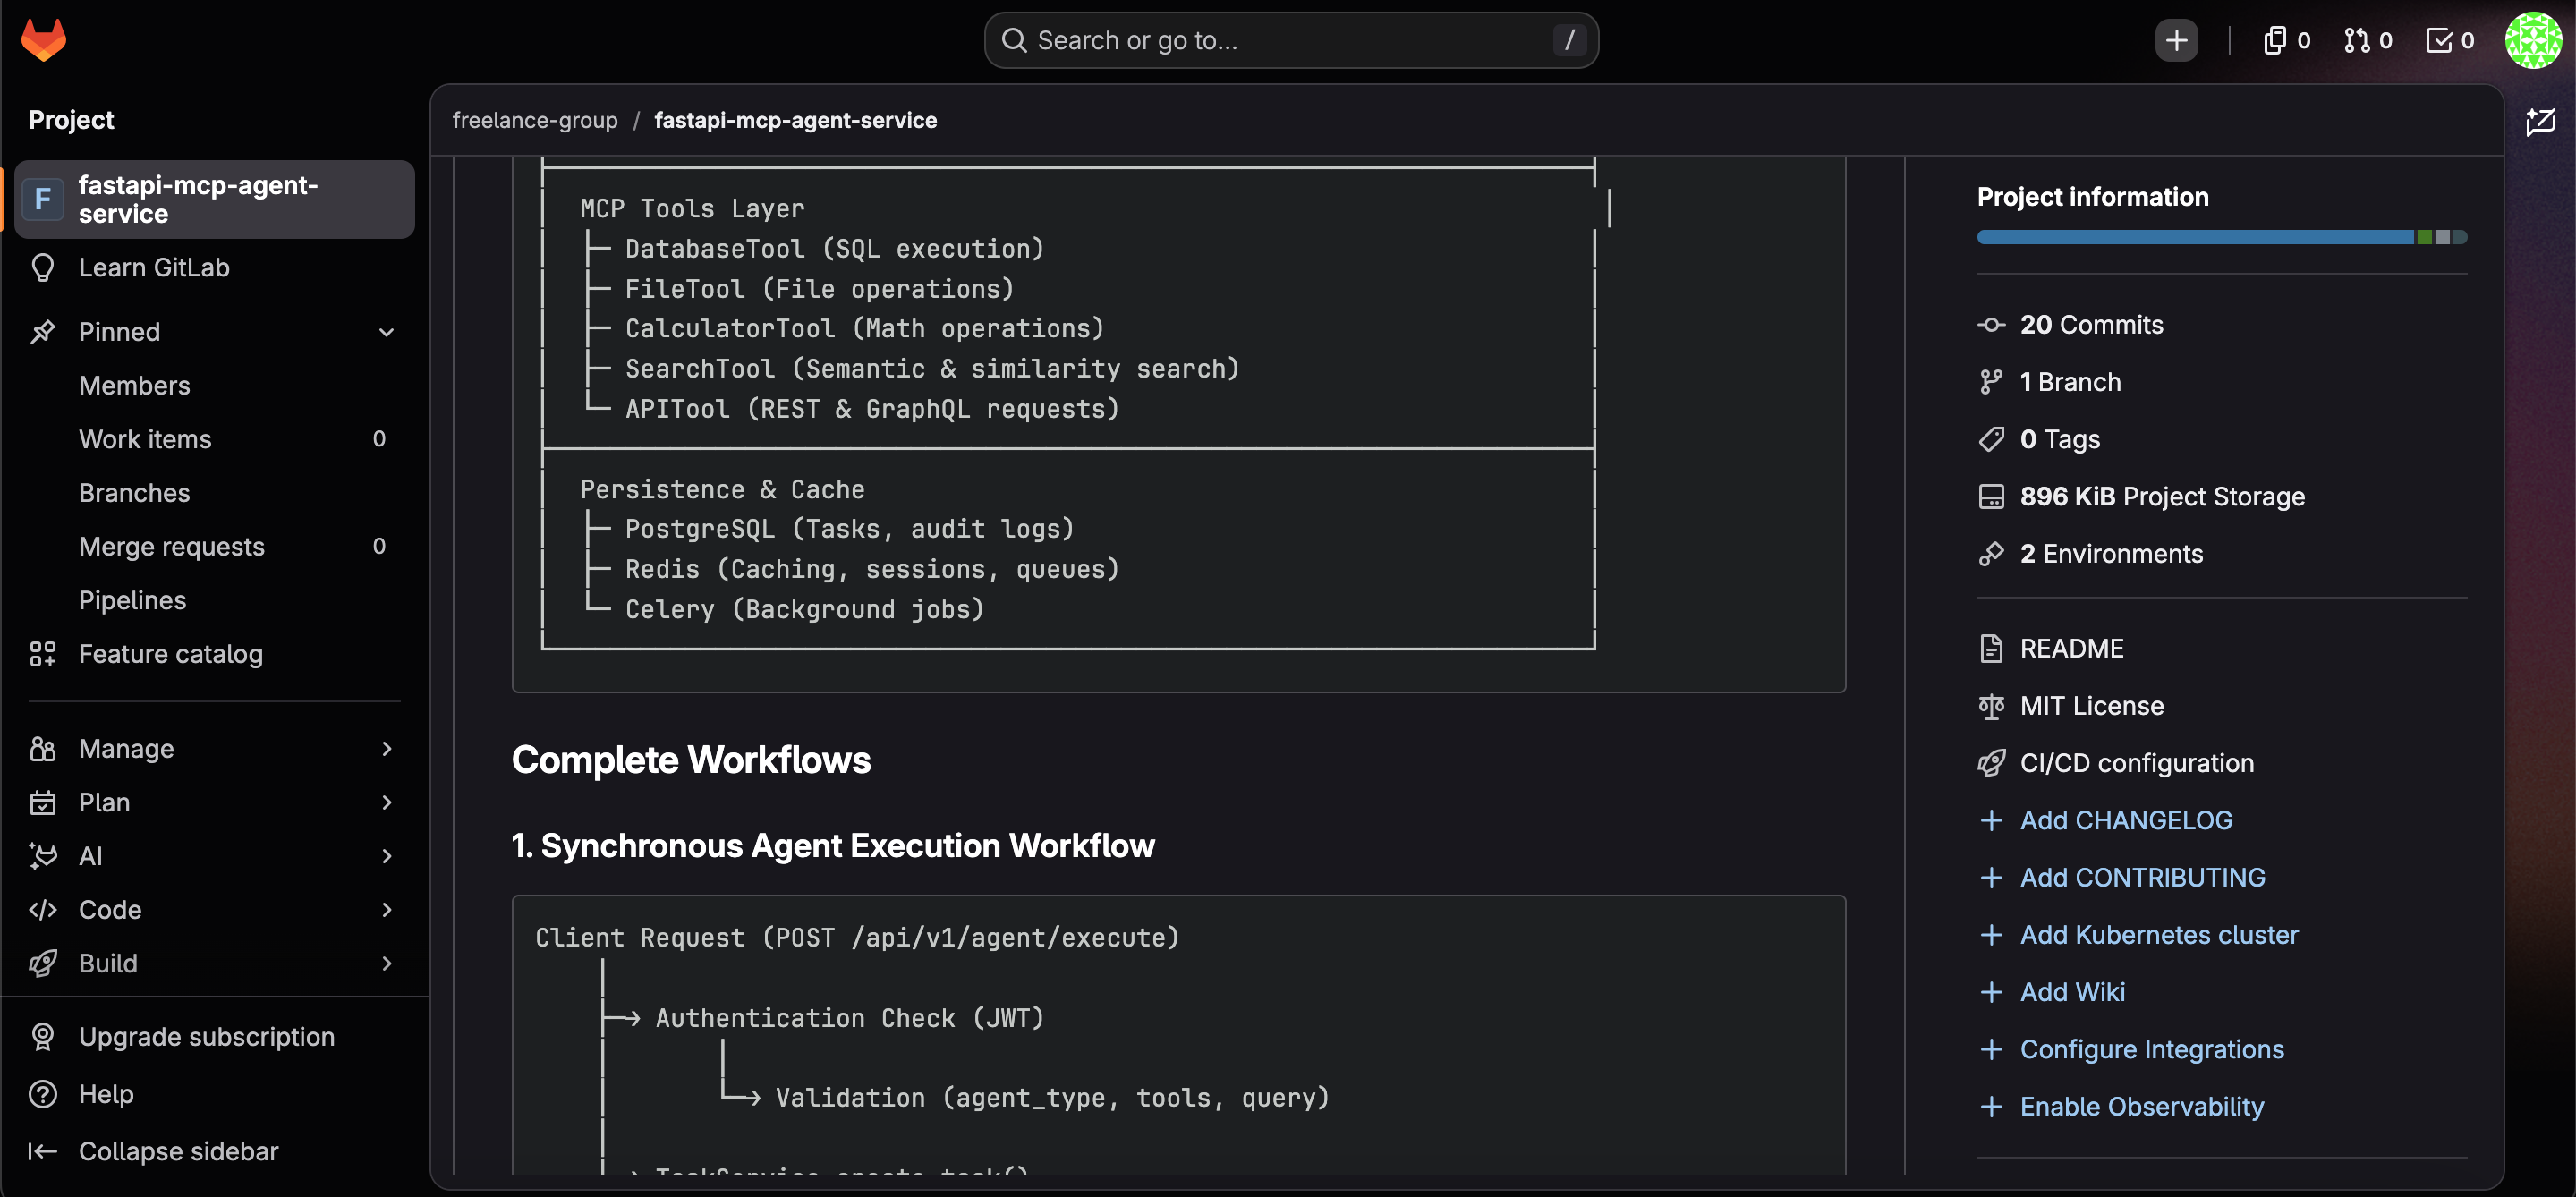
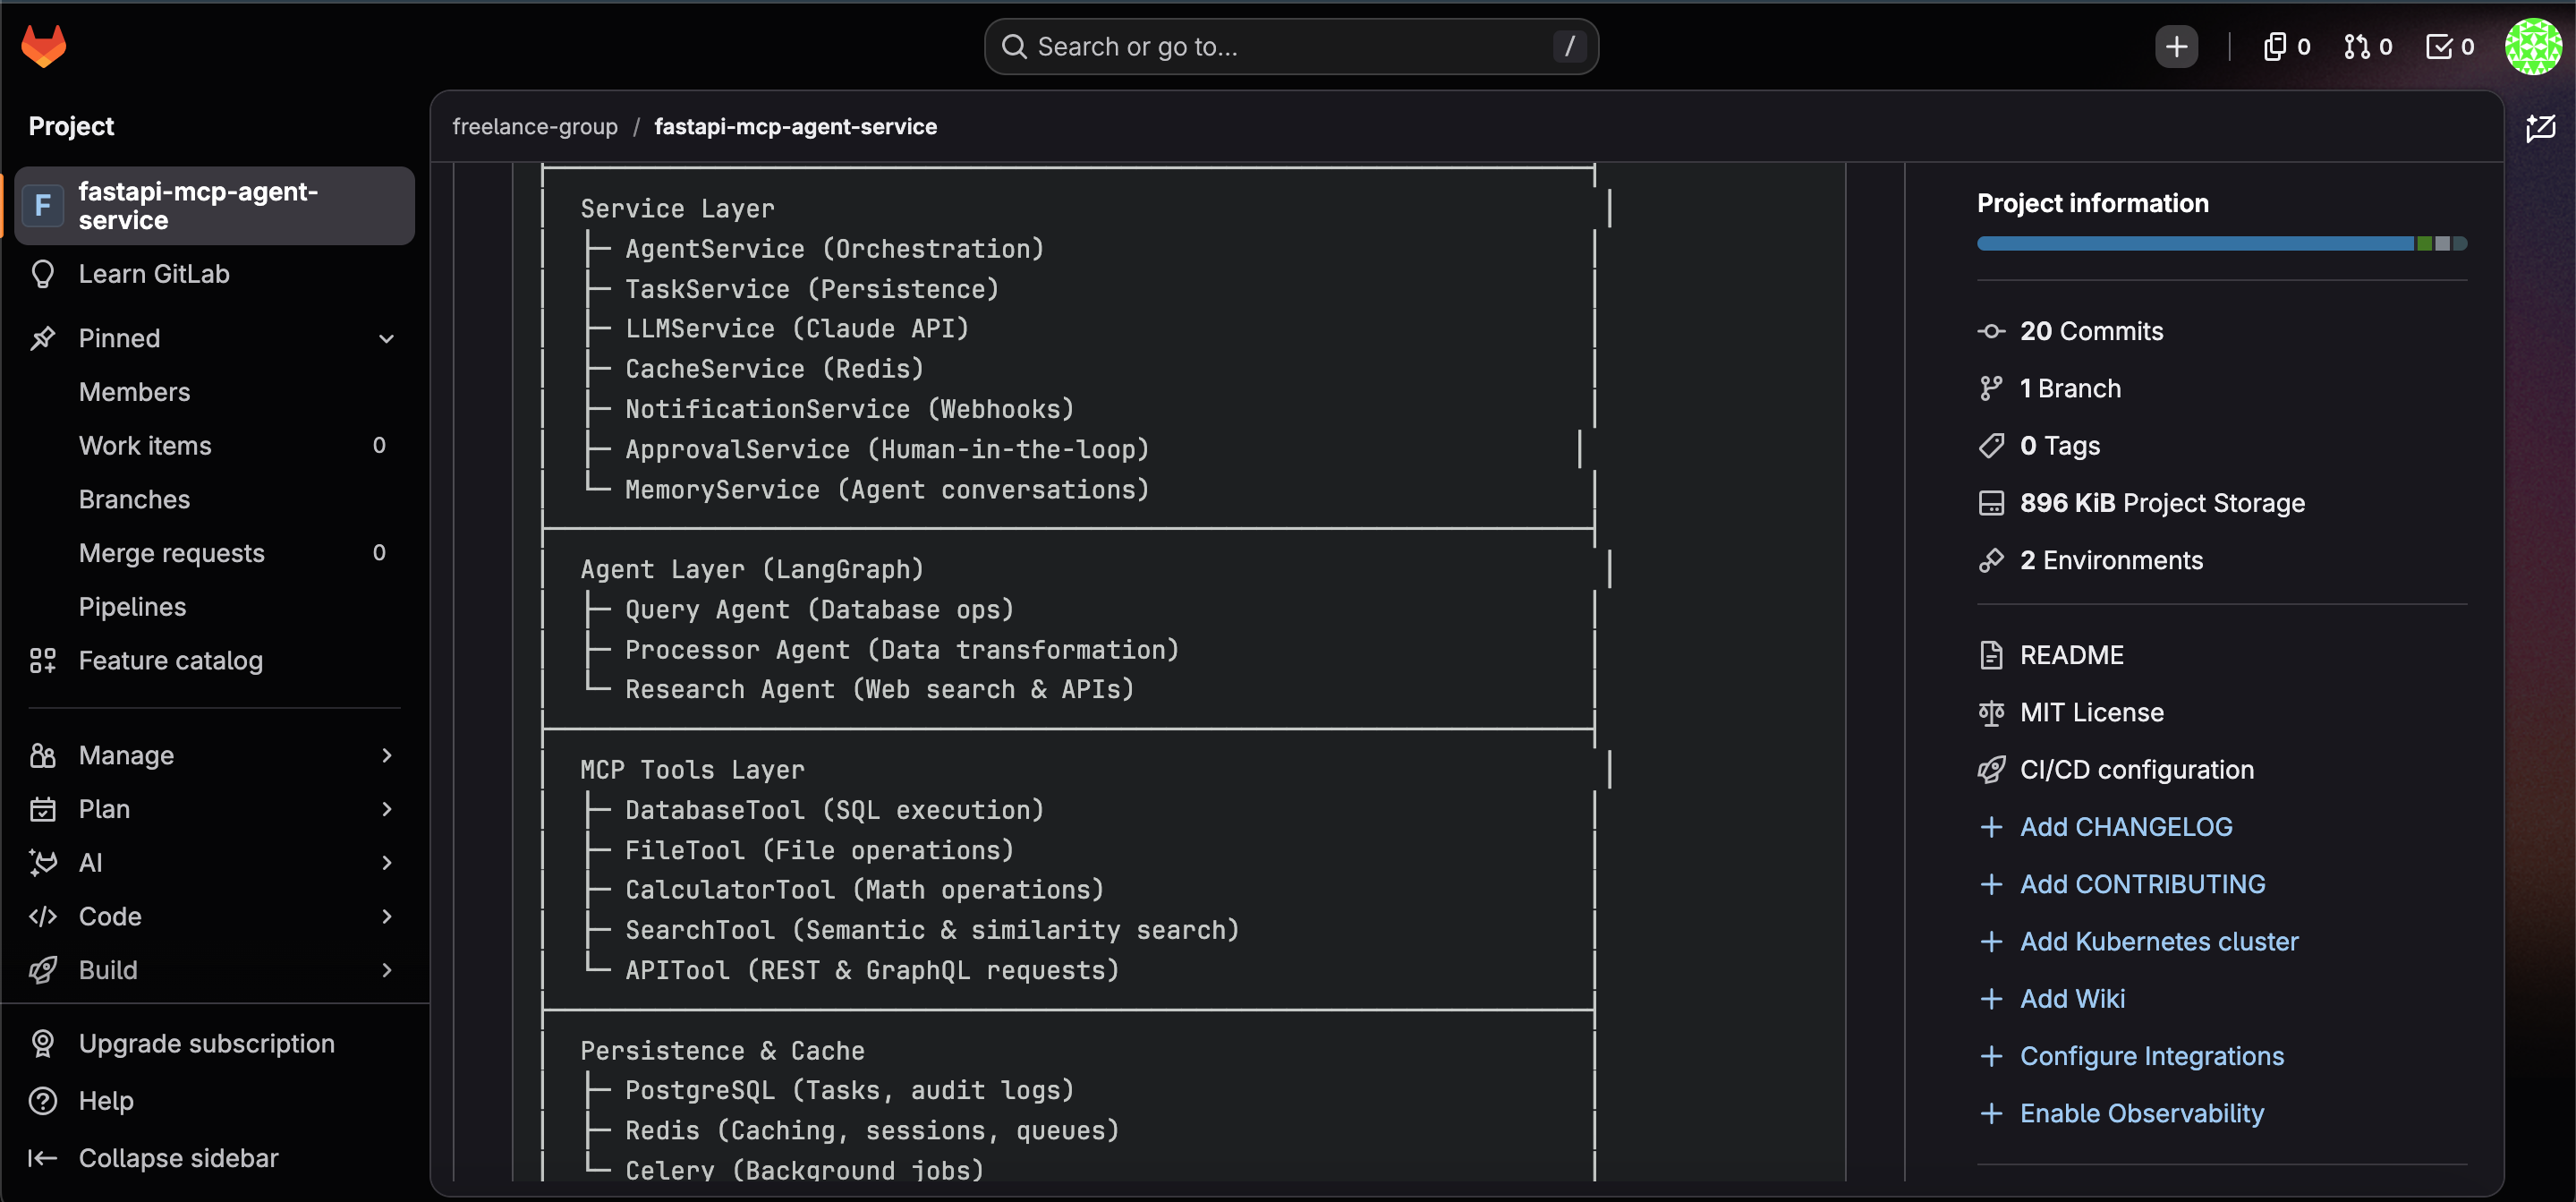
High-level component architecture: MCP layer, FastAPI service, GitLab CI/CD, and cloud infrastructure
-
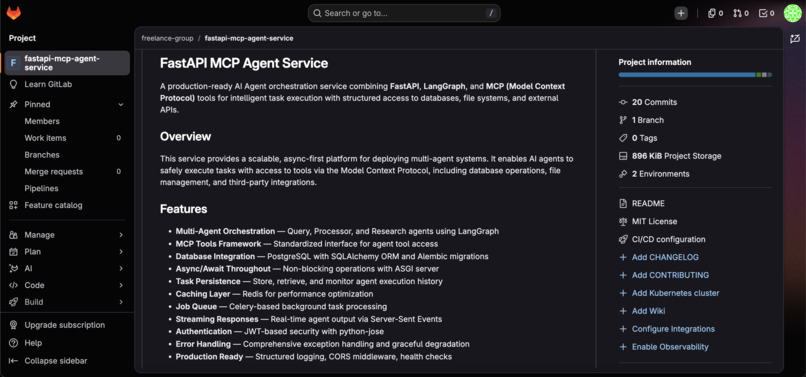
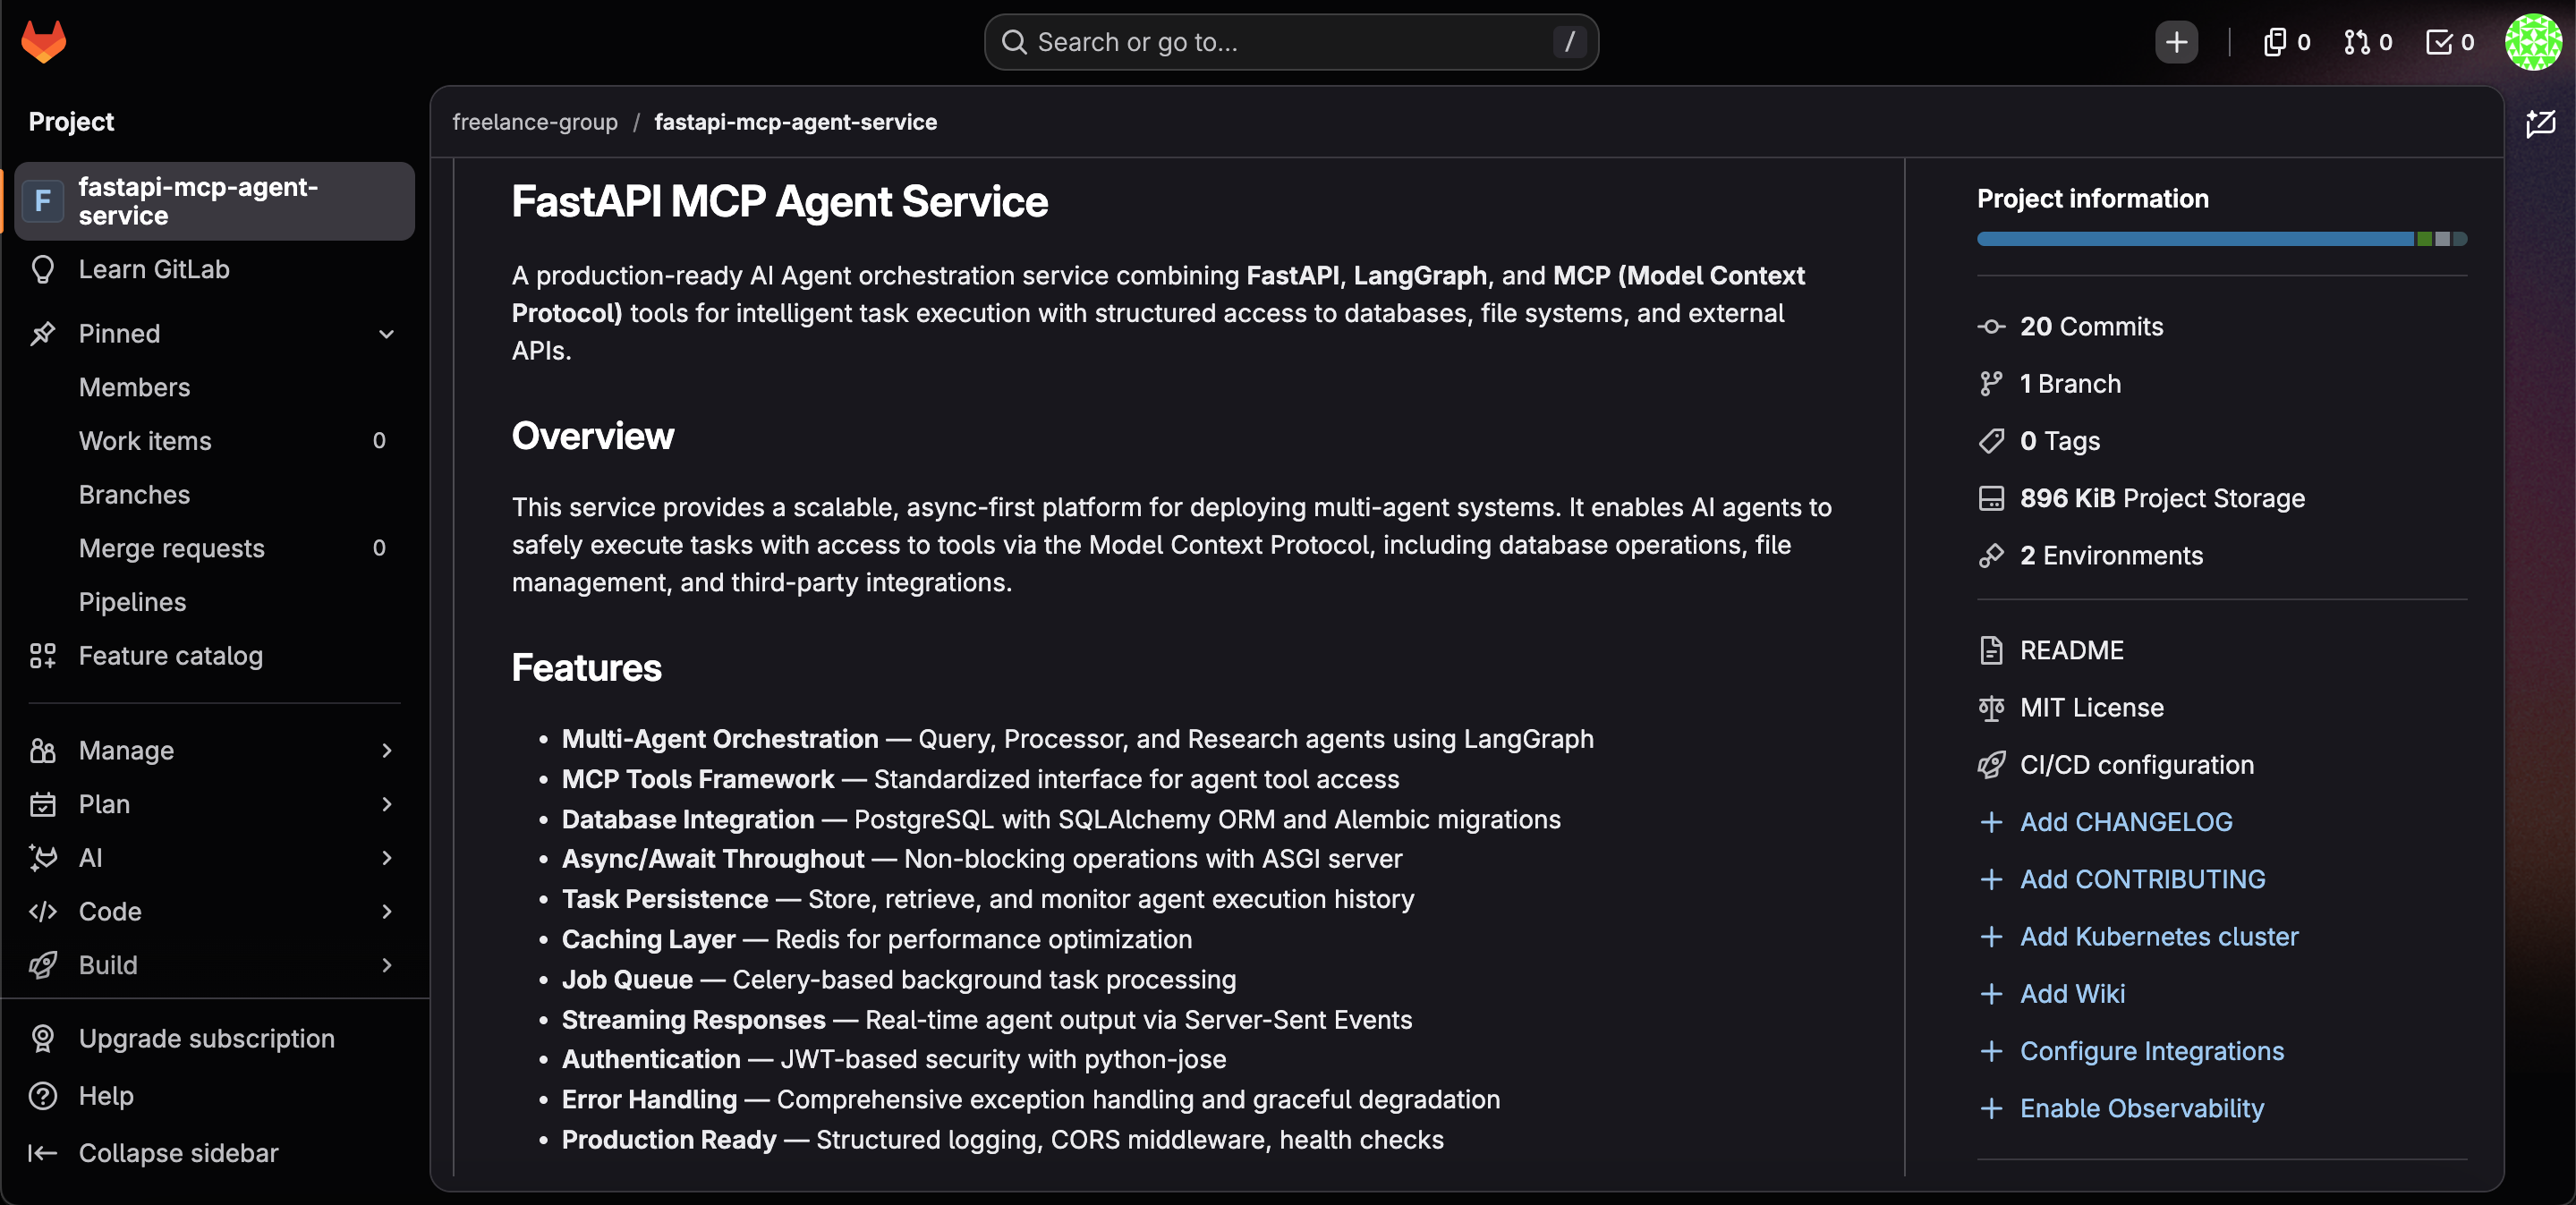
FastAPI MCP Agent Service documentation: project overview, features, and MCP tool registration details
Inspiration## Inspiration
The gap between writing code and shipping it safely to production remains one of the biggest bottlenecks in software development. I wanted to build a service that demonstrates how AI agents and MCP (Model Context Protocol) can be integrated with a complete DevSecOps pipeline — from code commit all the way to production deployment.
What it does
FastAPI MCP Agent Service is a production-ready REST API that exposes AI agent capabilities via the Model Context Protocol. It features:
- MCP Agent Integration: Connects to Claude via Anthropic API, enabling agentic workflows through a standardized protocol
- Full DevSecOps Pipeline: Automated GitLab CI/CD pipeline covering test → security → build → deploy stages
- Security Scanning: Integrated SAST (Semgrep), dependency vulnerability checks, and Bandit security analysis
- Observability: Prometheus metrics endpoint, structured logging, and health checks
- Authentication: JWT-based auth with Redis session management
- Infrastructure as Code: Dockerized service with Google Cloud Run deployment configuration
How I built it
Built on FastAPI with async PostgreSQL (asyncpg), Redis caching, and a full test suite (149 tests). The GitLab CI/CD pipeline runs 9 jobs across 4 stages:
- Test stage: Unit tests, integration tests, code quality checks, and SAST scanning
- Security stage: Bandit Python security linter and dependency vulnerability analysis
- Build stage: Docker image build and push to GitLab Container Registry
- Deploy stage: Automated staging deployment, manual production gate
Challenges
The biggest challenge was structuring the GitLab CI/CD YAML correctly — especially getting the SAST template inclusion at the right level and ensuring all jobs had proper service dependencies (PostgreSQL + Redis) for integration testing.
What I learned
Deep hands-on experience with GitLab's DevSecOps lifecycle: how to wire security scanning into the pipeline without blocking development velocity, and how MCP clients can be integrated as a service layer rather than a one-off script.
What's next
Extend the MCP agent to support multi-step agentic flows, add GitLab Duo integration for AI-assisted code review in MRs, and complete the Google Cloud Run deployment with proper secrets management via GCP Secret Manager.
What it does
How we built it
Challenges we ran into
Accomplishments that we're proud of
What we learned
What's next for FastAPI MCP Agent Service
Built With
- anthropic
- docker
- fastapi
- gitlab
- google-cloud-run
- jwt
- postgresql
- prometheus
- python
- redis

Log in or sign up for Devpost to join the conversation.