-
-
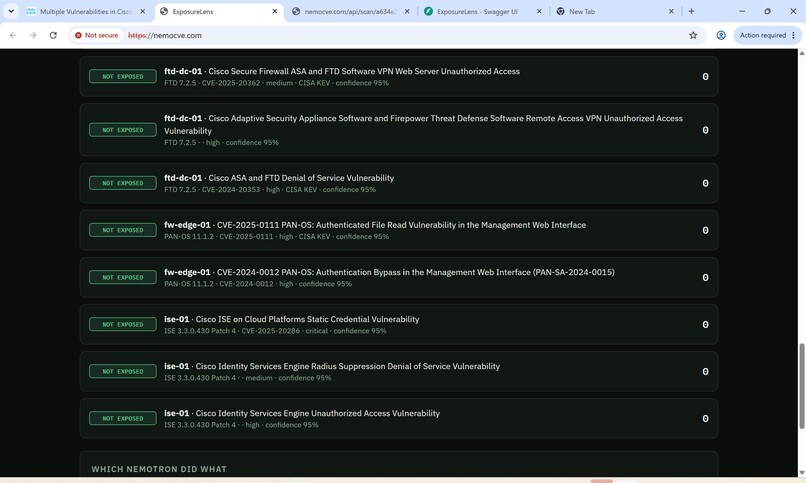
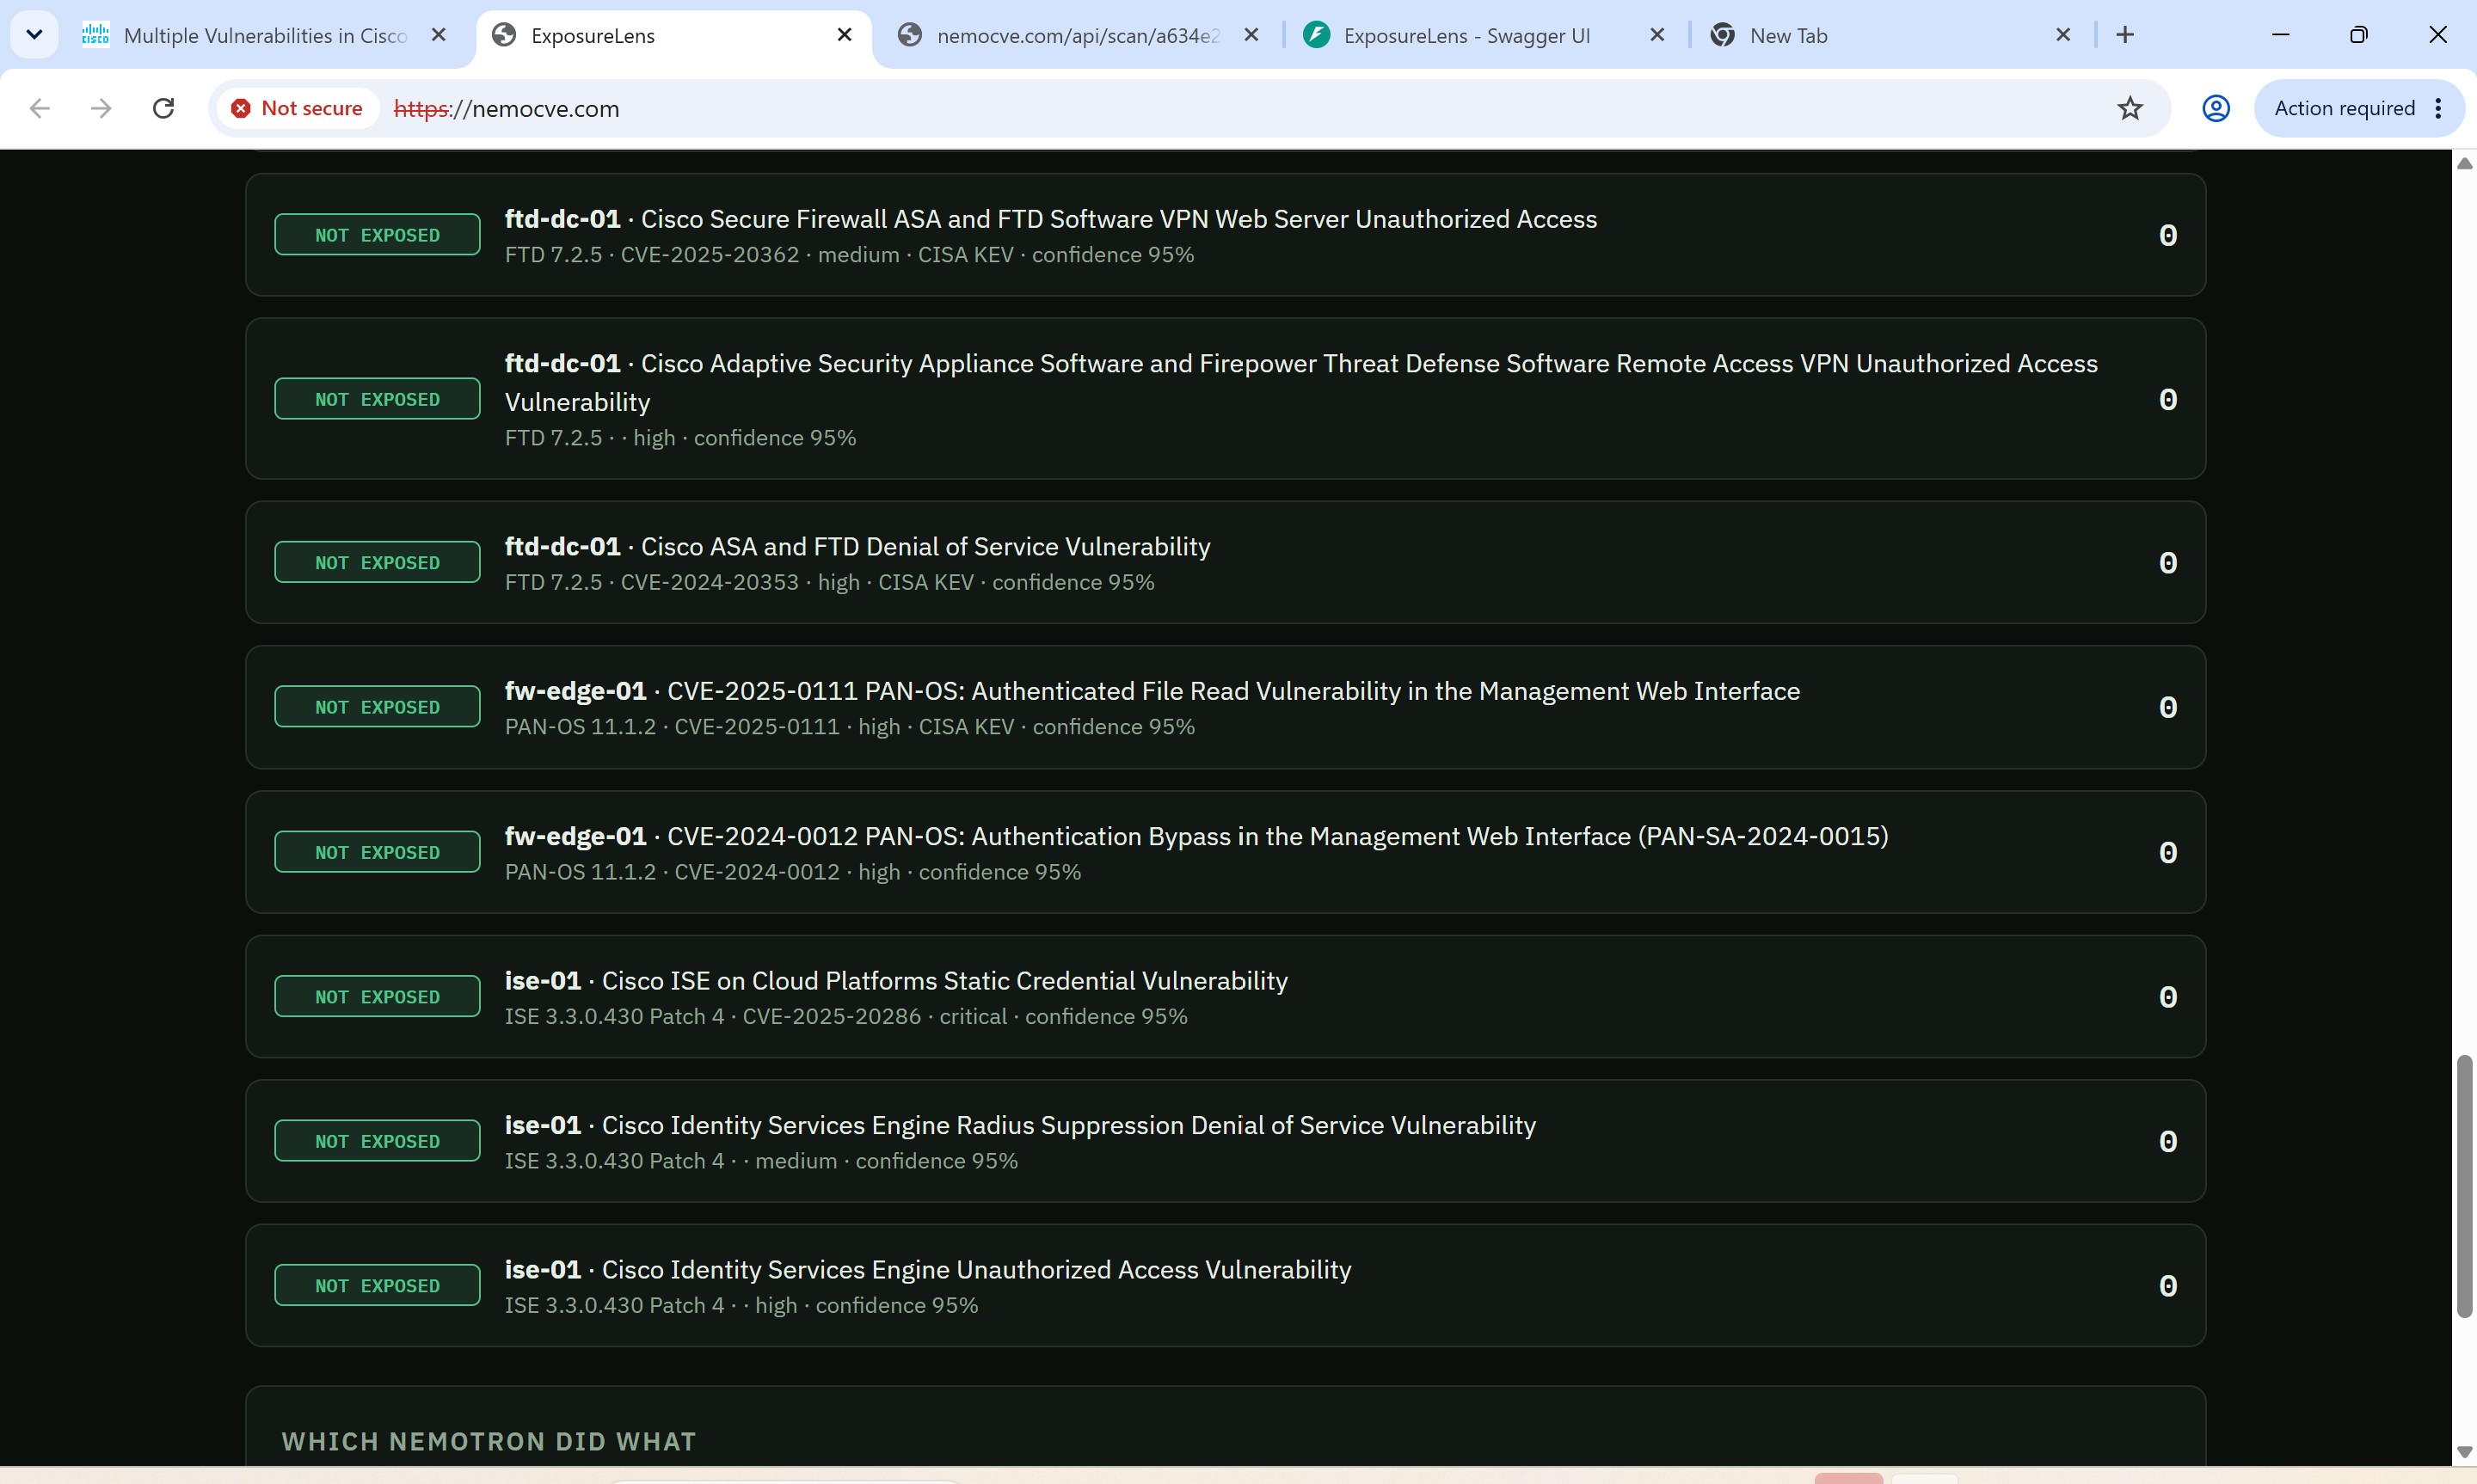
Exposed page2
-
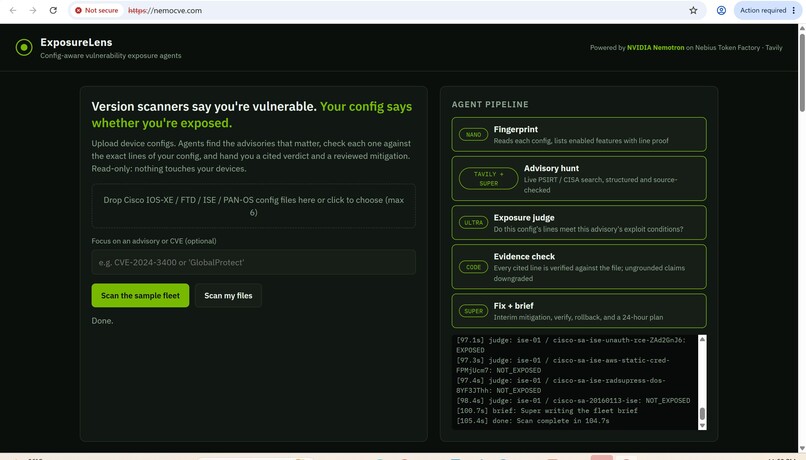
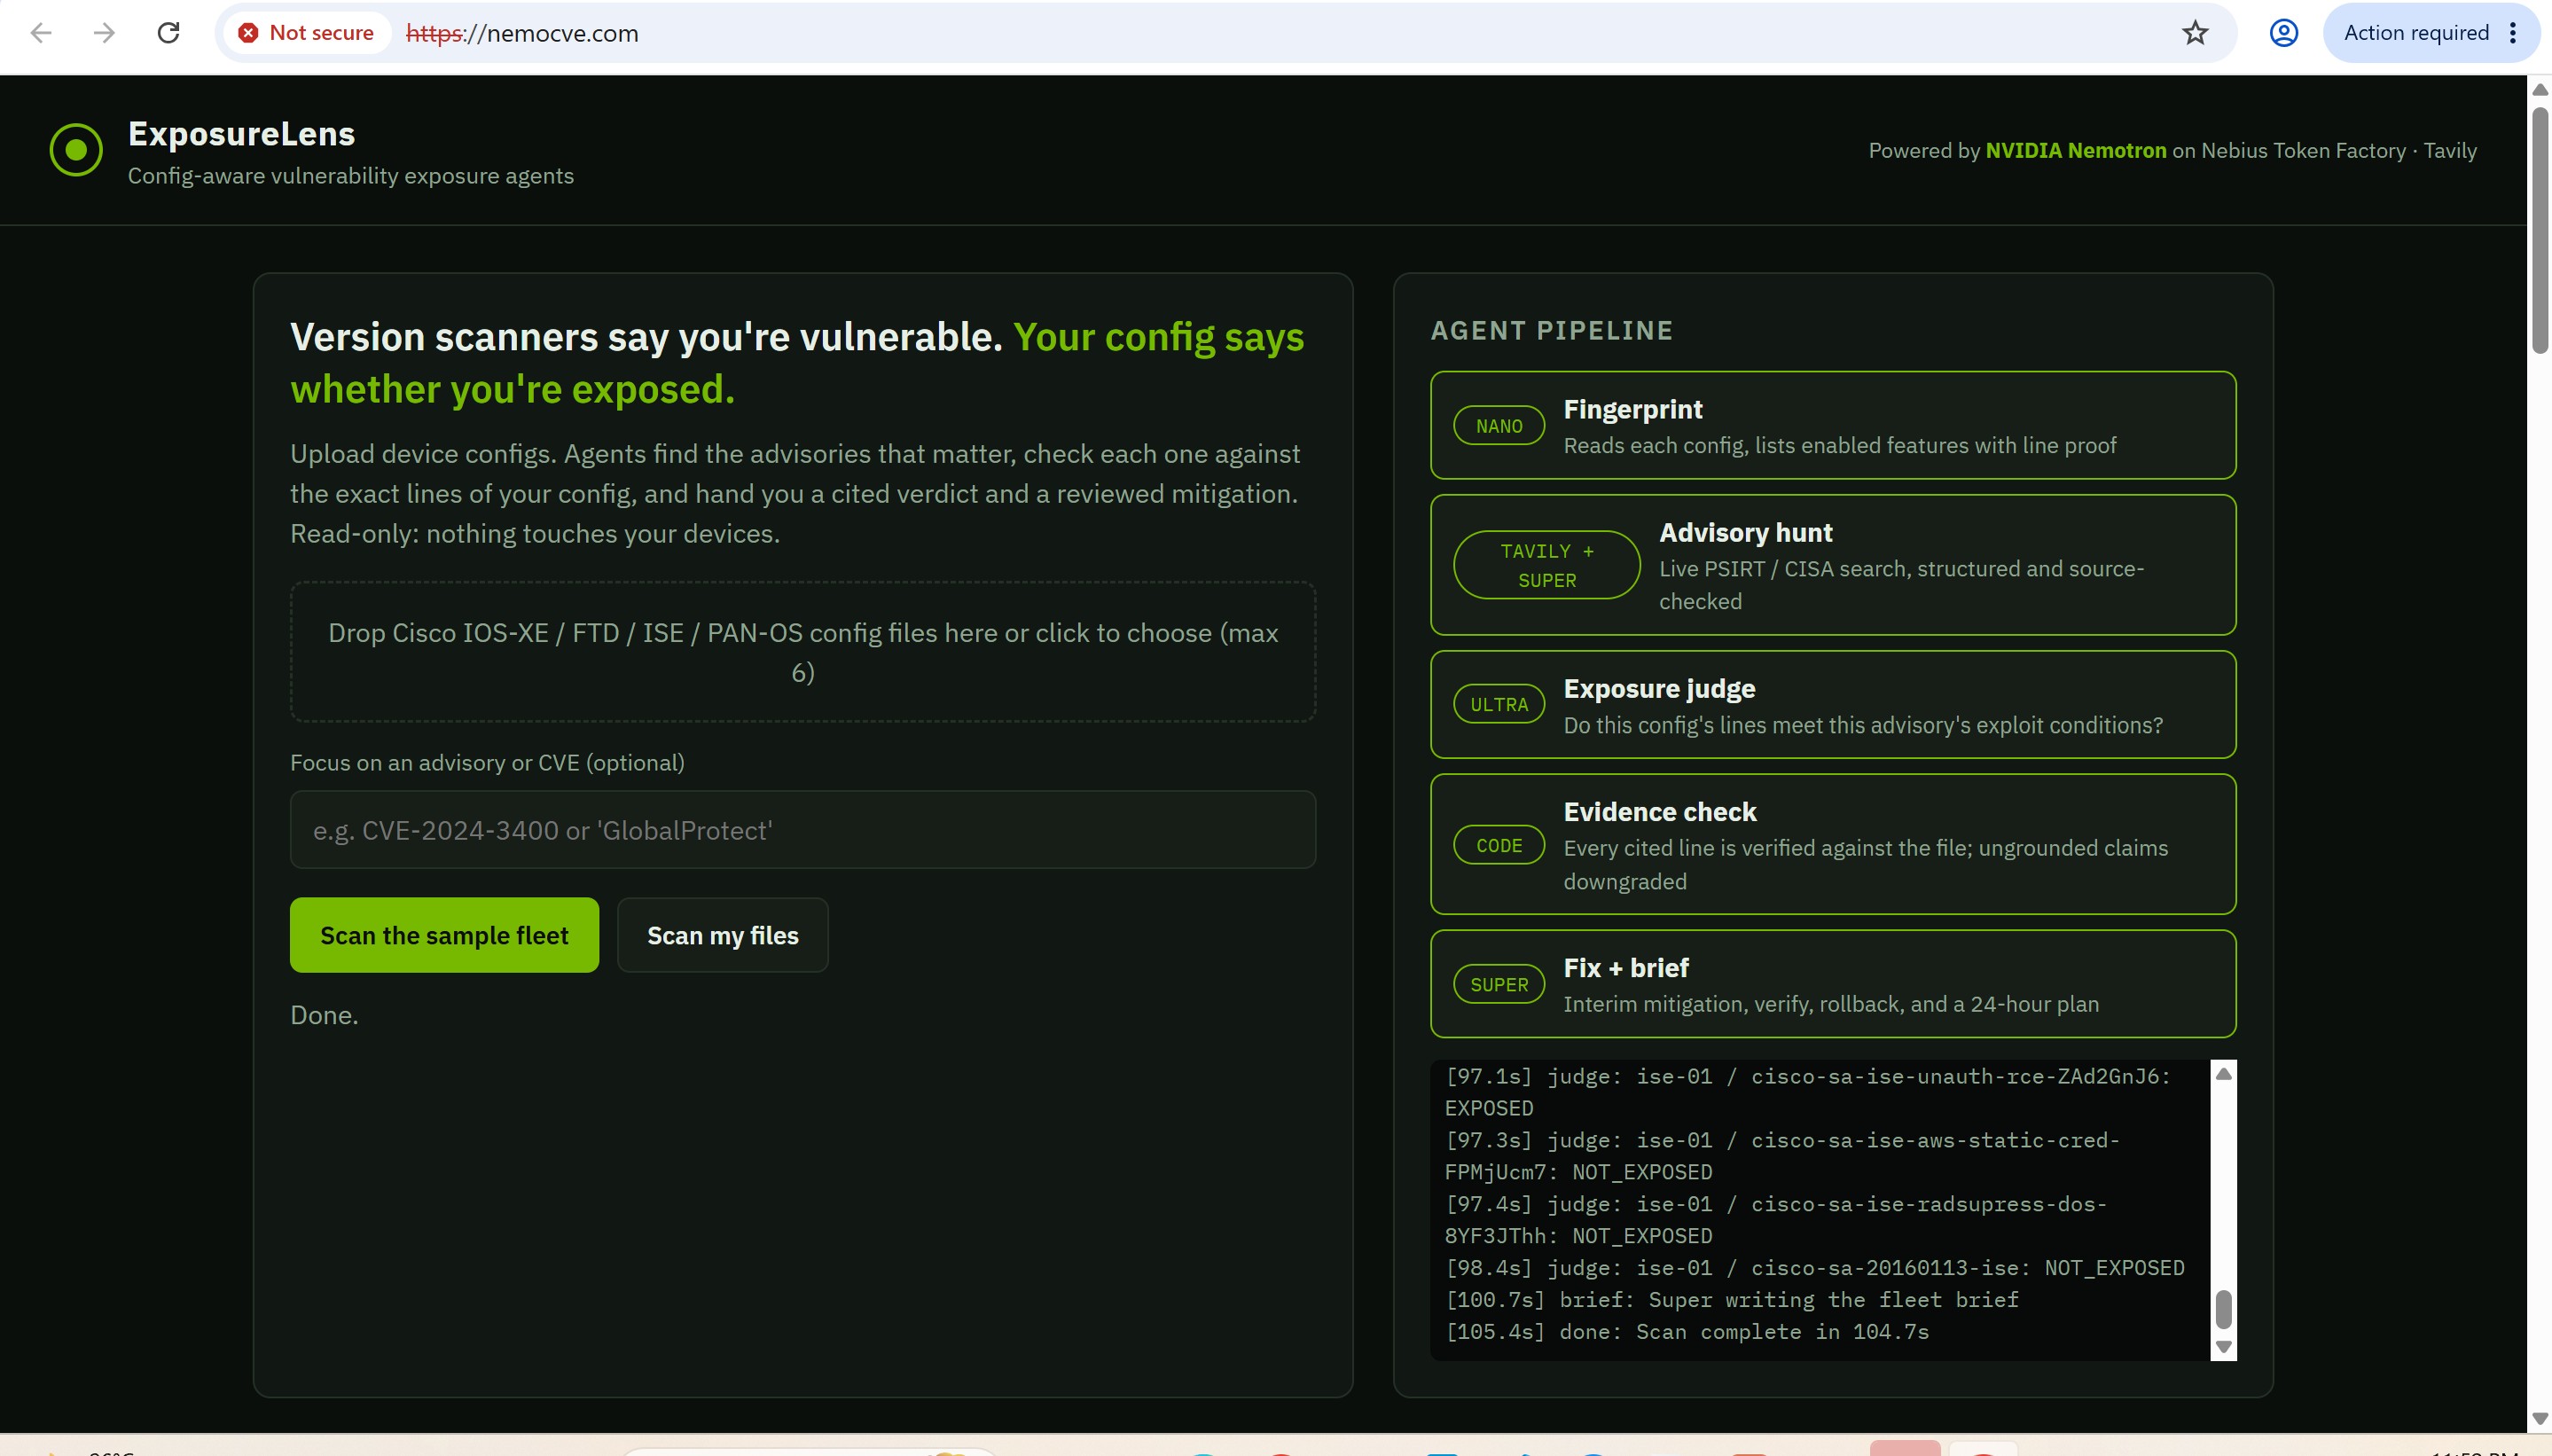
Home page
-
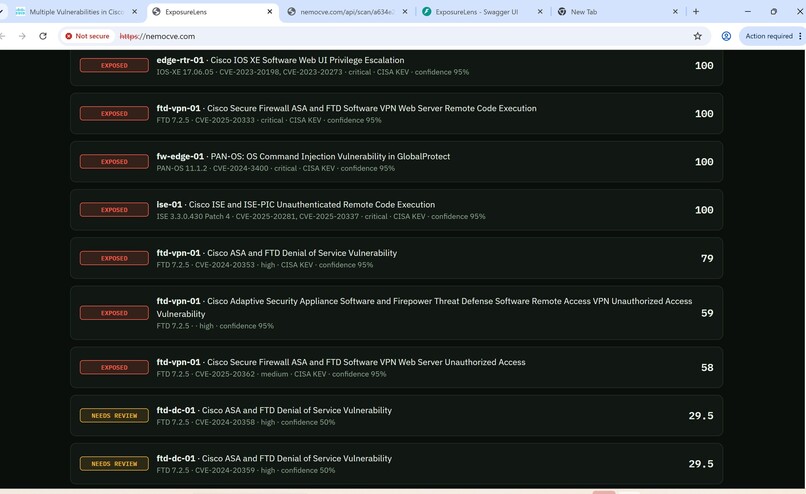
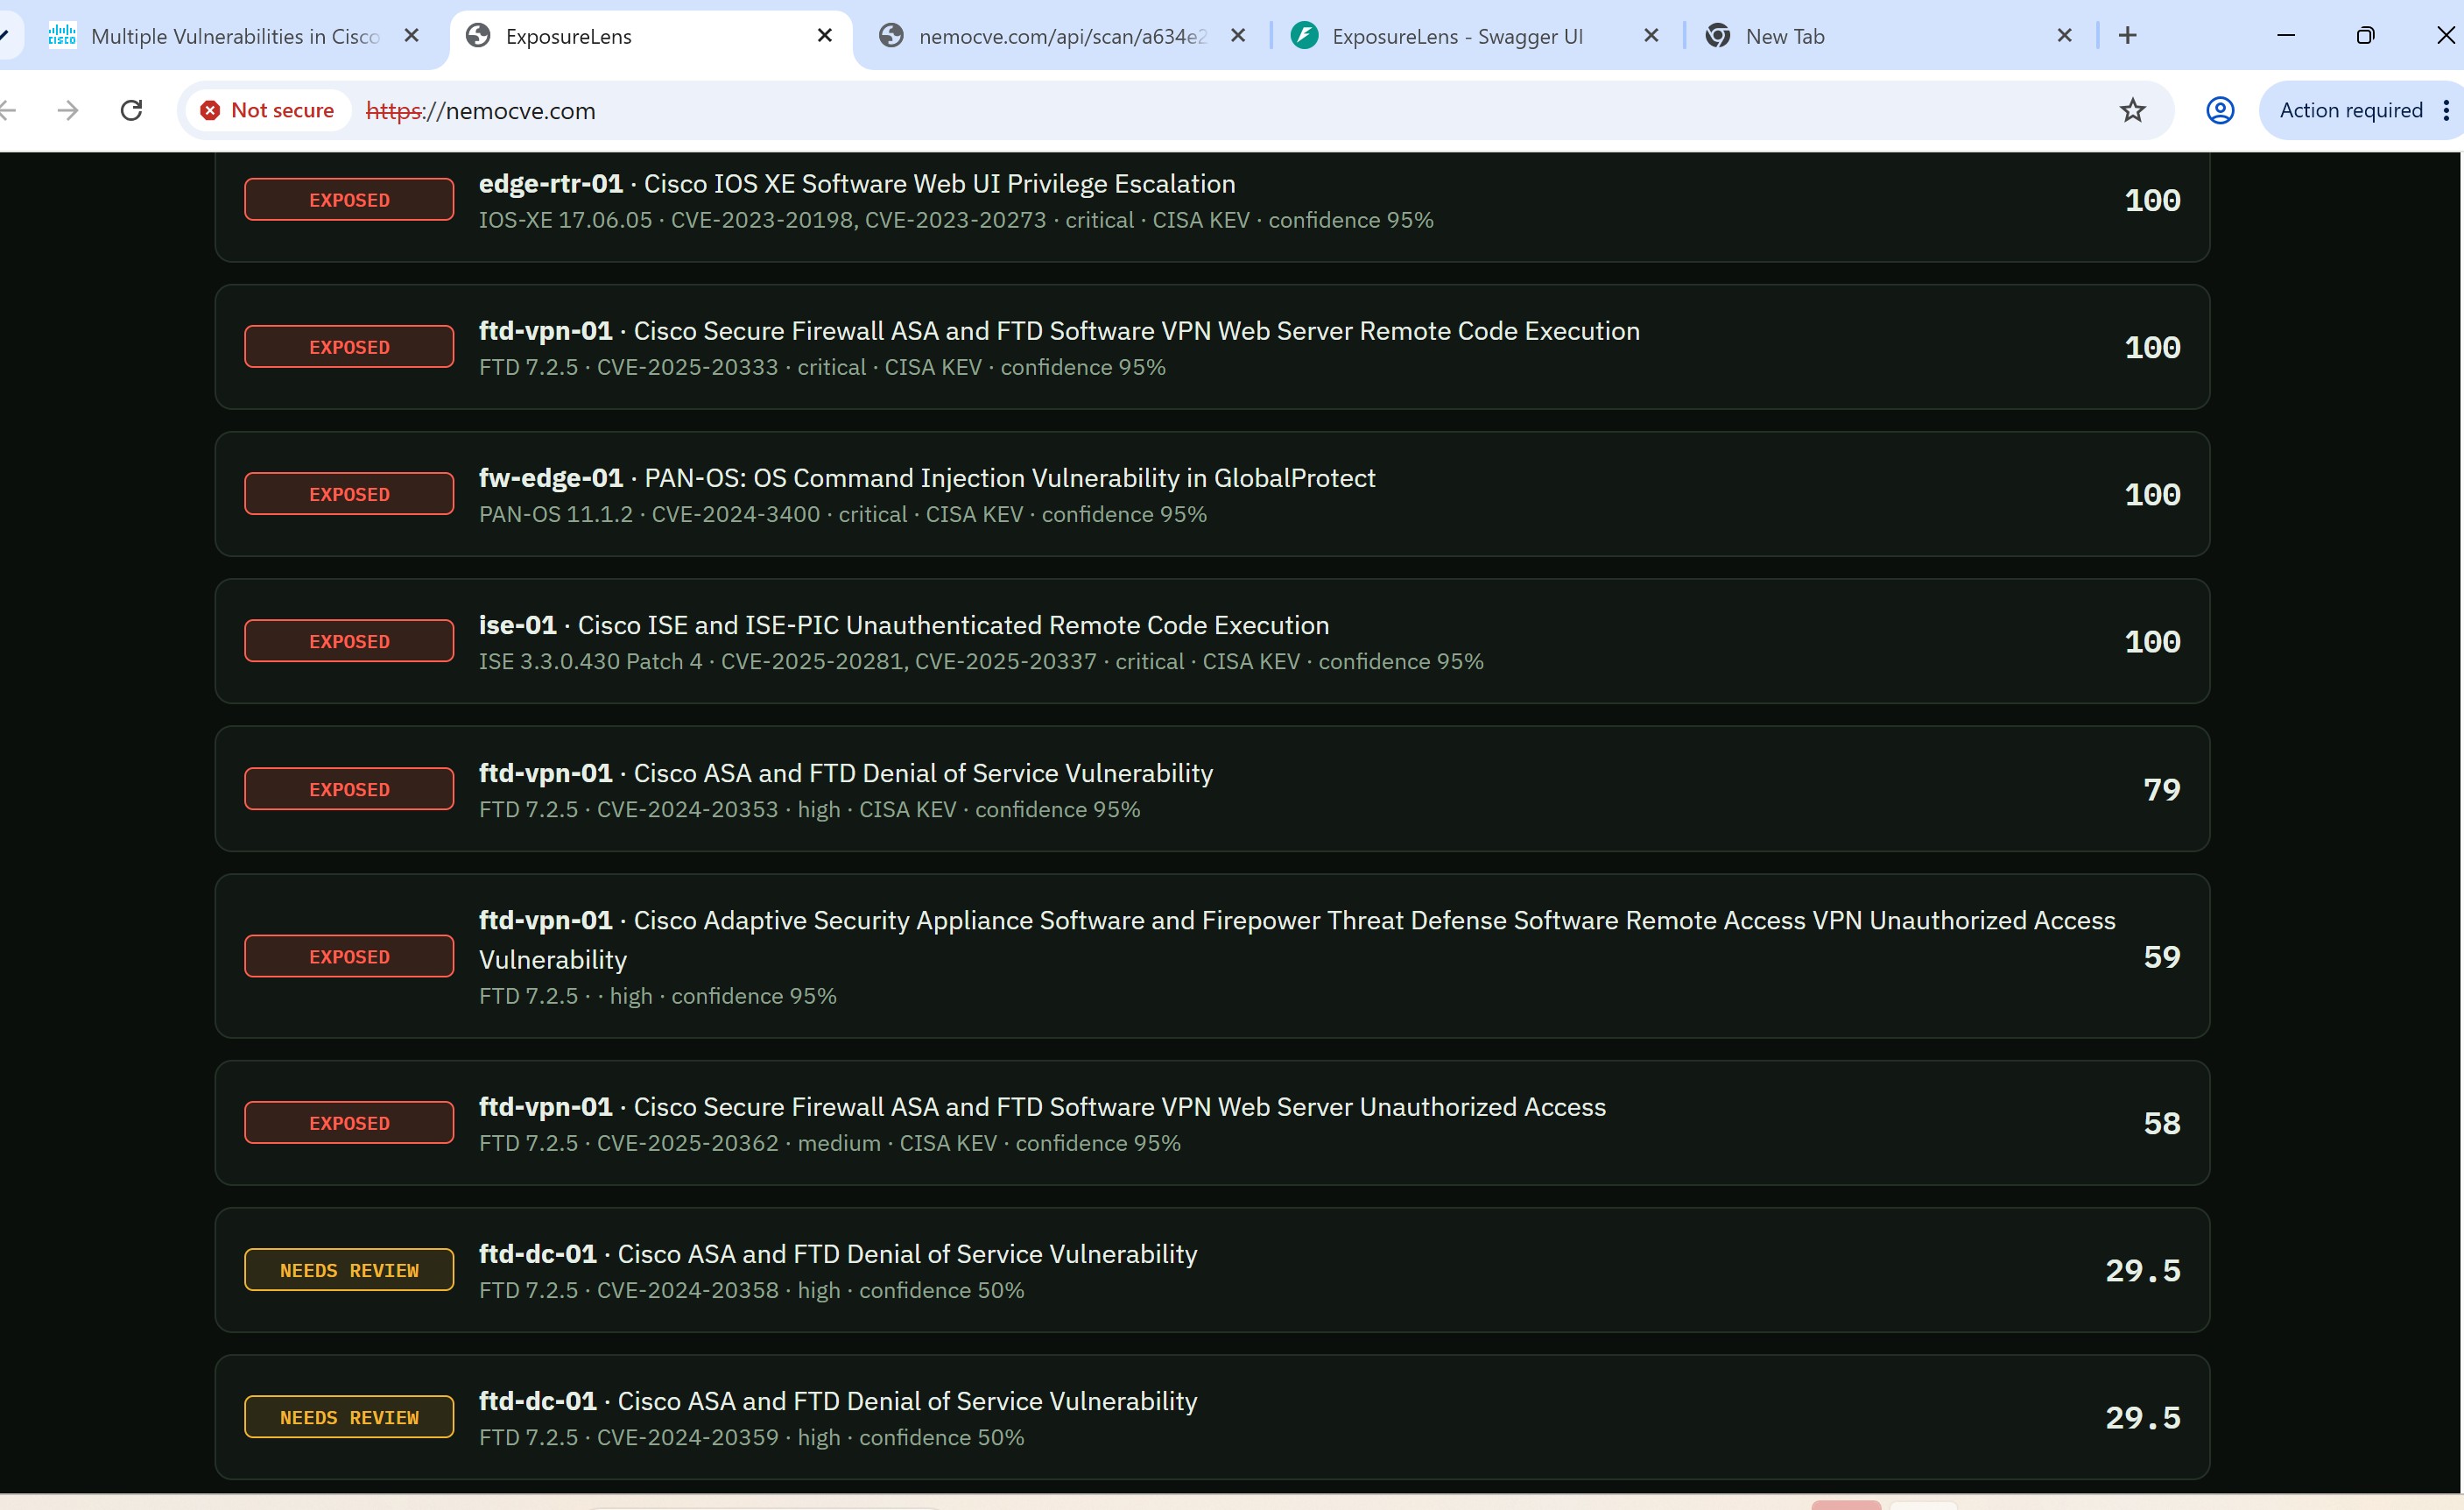
Exposed page1
-
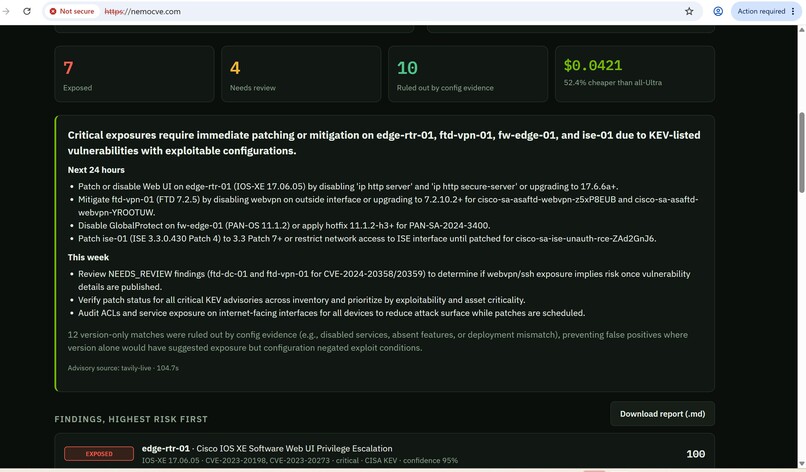
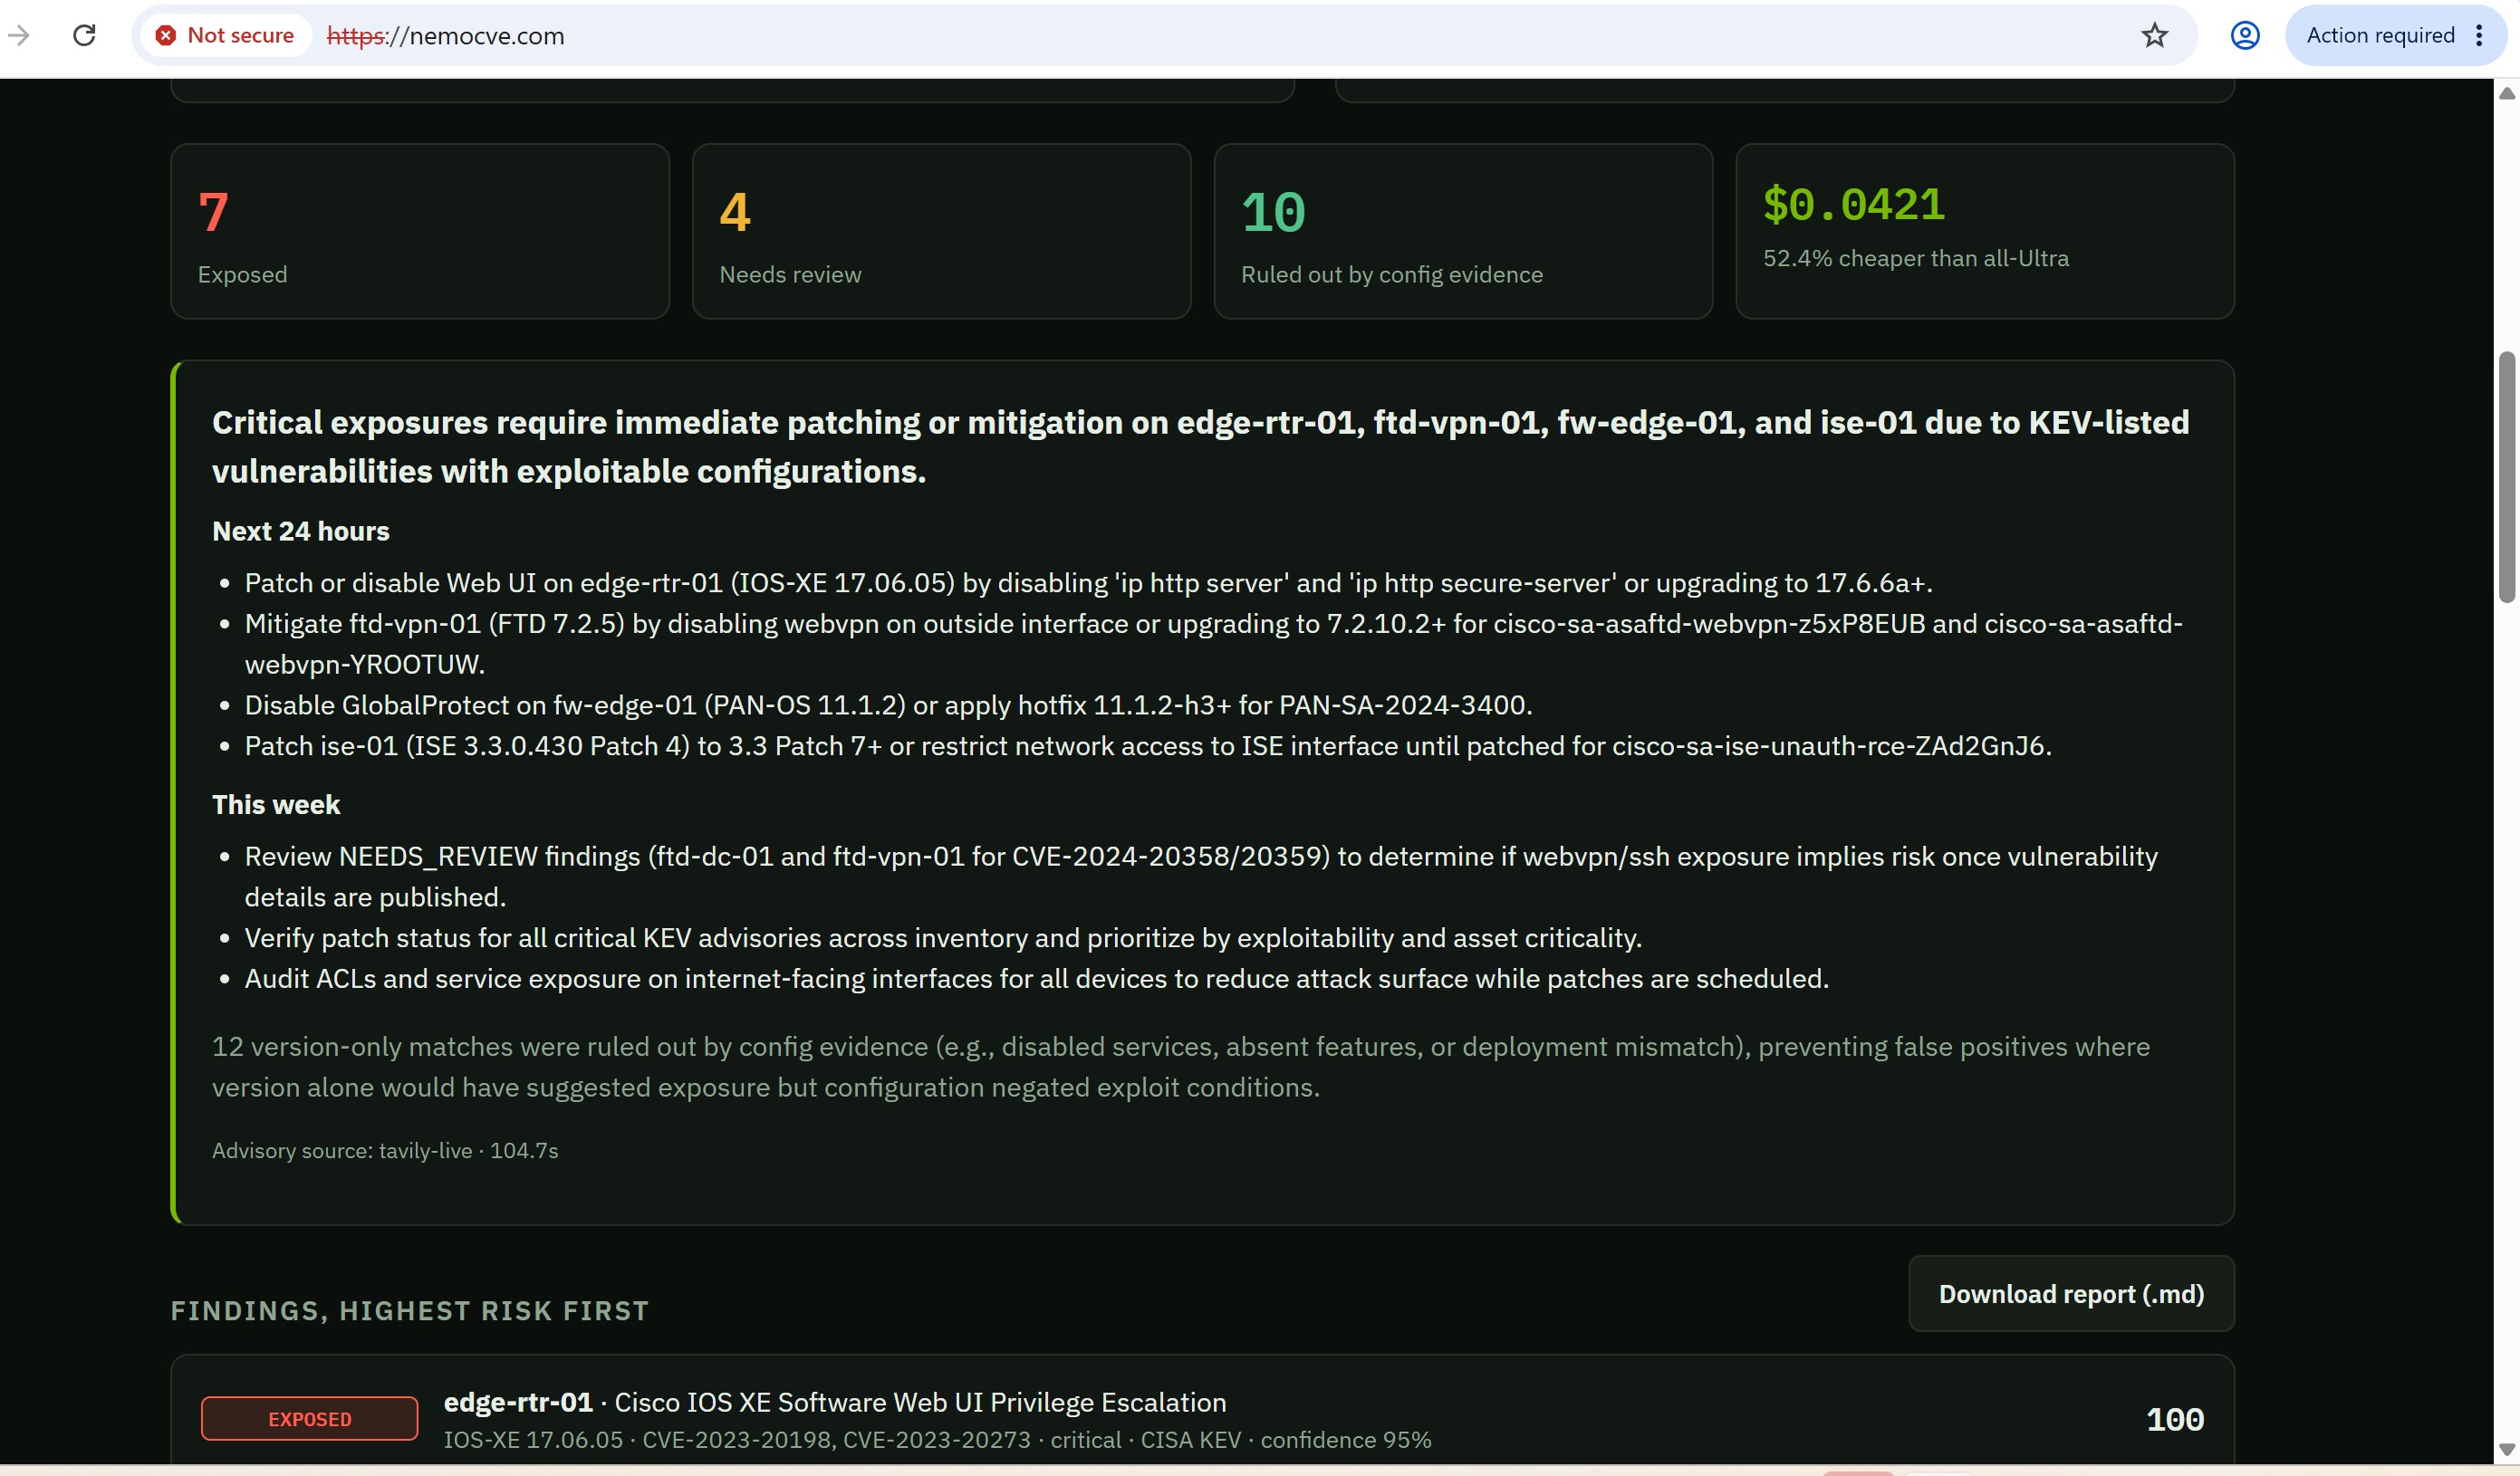
Reports
ExposureLens does that check:
Nemotron Nano reads each config. Tavily searches vendor security advisories and CISA, and Nemotron Super structures the results. Nemotron Ultra decides for each device whether it is exposed, citing the exact config lines. Plain code checks that each cited line really exists. If it doesn’t, an “exposed” verdict is downgraded to “needs review”. Super then drafts the fix commands, with verify and rollback steps.


Log in or sign up for Devpost to join the conversation.