Inspiration
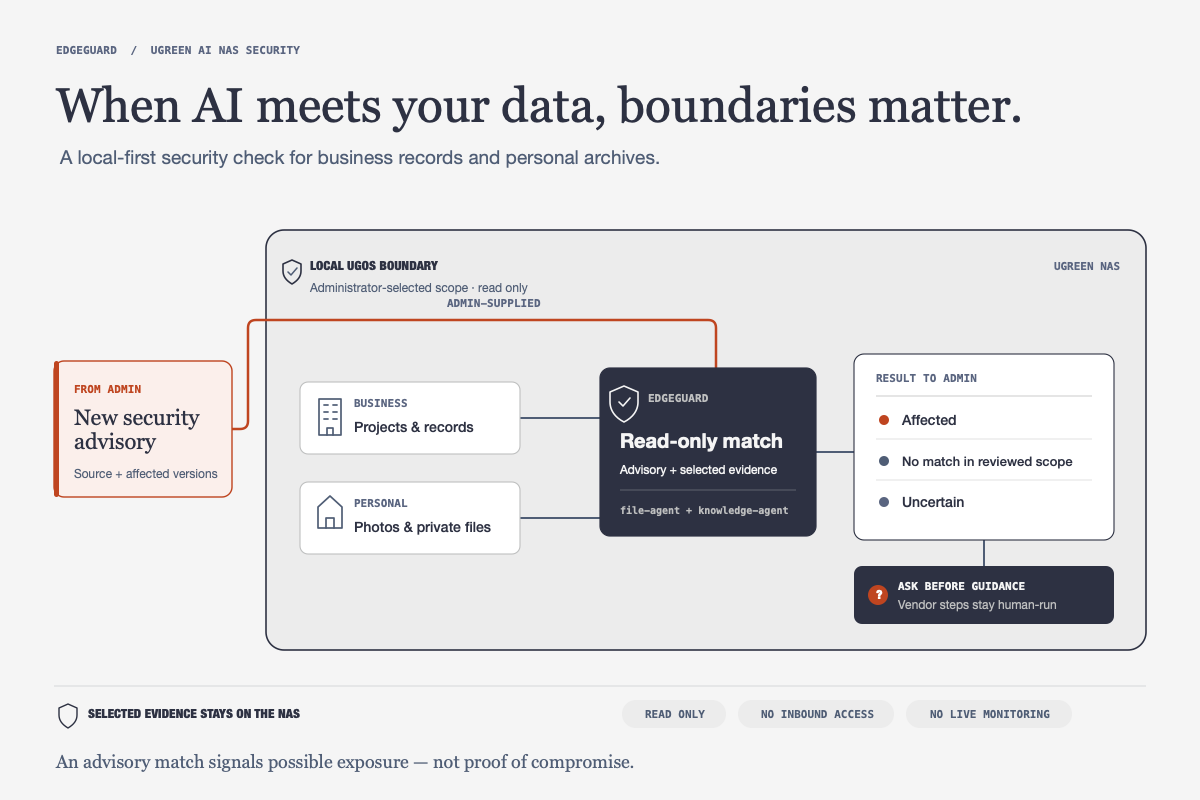
A vulnerability advisory can name affected software, but it does not tell a NAS owner whether that product or version exists in the environment they care about. Sharing a full inventory with a cloud service creates a privacy trade-off, while automatic fixes can disrupt services. EdgeGuard is designed to make the first response local, scoped, and evidence-based.
What it does
The administrator supplies a trusted advisory and selects the inventory, SBOM, lockfile, or device records to review. The read-only UGOS Skill delegates bounded evidence searches within that selected scope, compares the returned product and version facts with the advisory, and reports one of three outcomes:
- Affected — reviewed evidence matches an affected product or version.
- Not matched in reviewed scope — the reviewed records do not show a match; this is not proof that the NAS is safe.
- Uncertain — evidence is missing, stale, conflicting, or too ambiguous to compare reliably.
Each result includes the advisory source and the supporting local evidence. The Skill then asks whether the administrator wants human-run guidance based on the vendor's supplied fix or mitigation.
How it is built
The submission package contains a UGREEN Skill definition and an evidence-and-outcomes reference. The Skill is designed to delegate bounded, read-only tasks to documented UGOS experts: ug-filesystem for selected-file search and reading, and ug-knowledge for evidence collection. The administrator selects the scope; the Skill does not request broad NAS access or export inventory as part of its design.
What we learned
A CVE match is evidence of possible exposure, not proof of active compromise. Likewise, failing to find a match in incomplete inventory cannot establish safety. Version formats, backports, and stale records make uncertainty a necessary outcome rather than a failure to answer.
Current status and next steps
The Skill and reference are drafted, but have not yet been imported into or run on a UGREEN NAS. Planned validation covers an exact affected match, a complete scoped non-match, and stale or conflicting evidence. The current build does not poll vulnerability feeds, send push alerts, inspect live traffic, patch, change firewall rules, isolate devices, or shut down services. An MCP-based advisory route is a future option only if UGREEN documents a supported registration and trigger path.
Built With
- markdown
- ugos
Log in or sign up for Devpost to join the conversation.