-
-
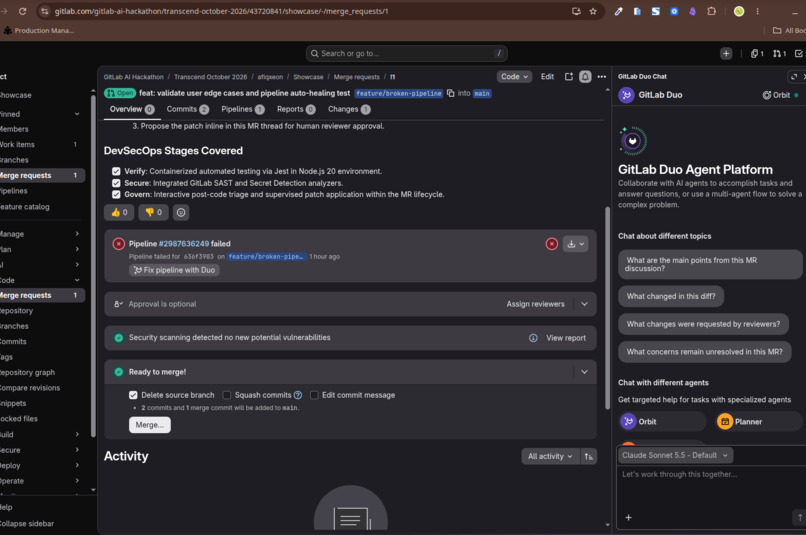
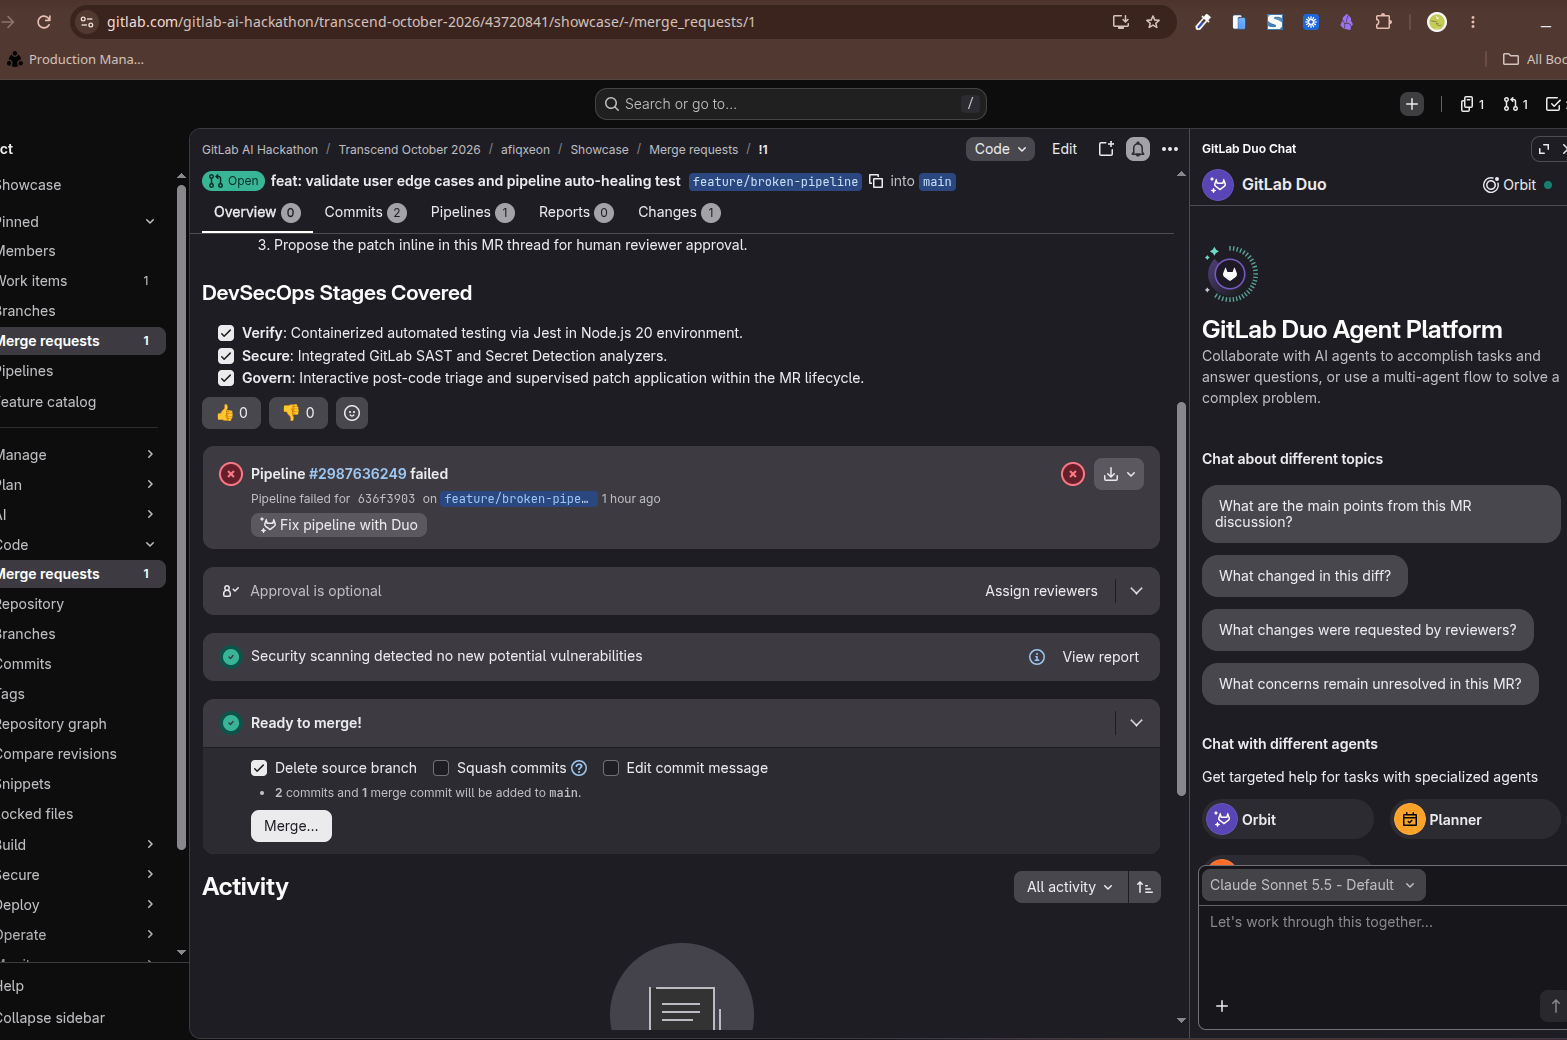
Initial CI/CD Failure: Merge Request encountering an intentional unit test failure in app.test.js, triggering automated root-cause detection
-
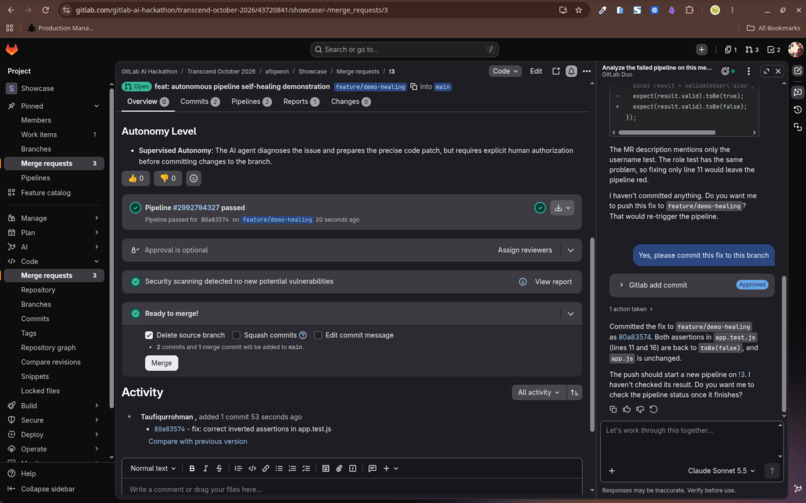
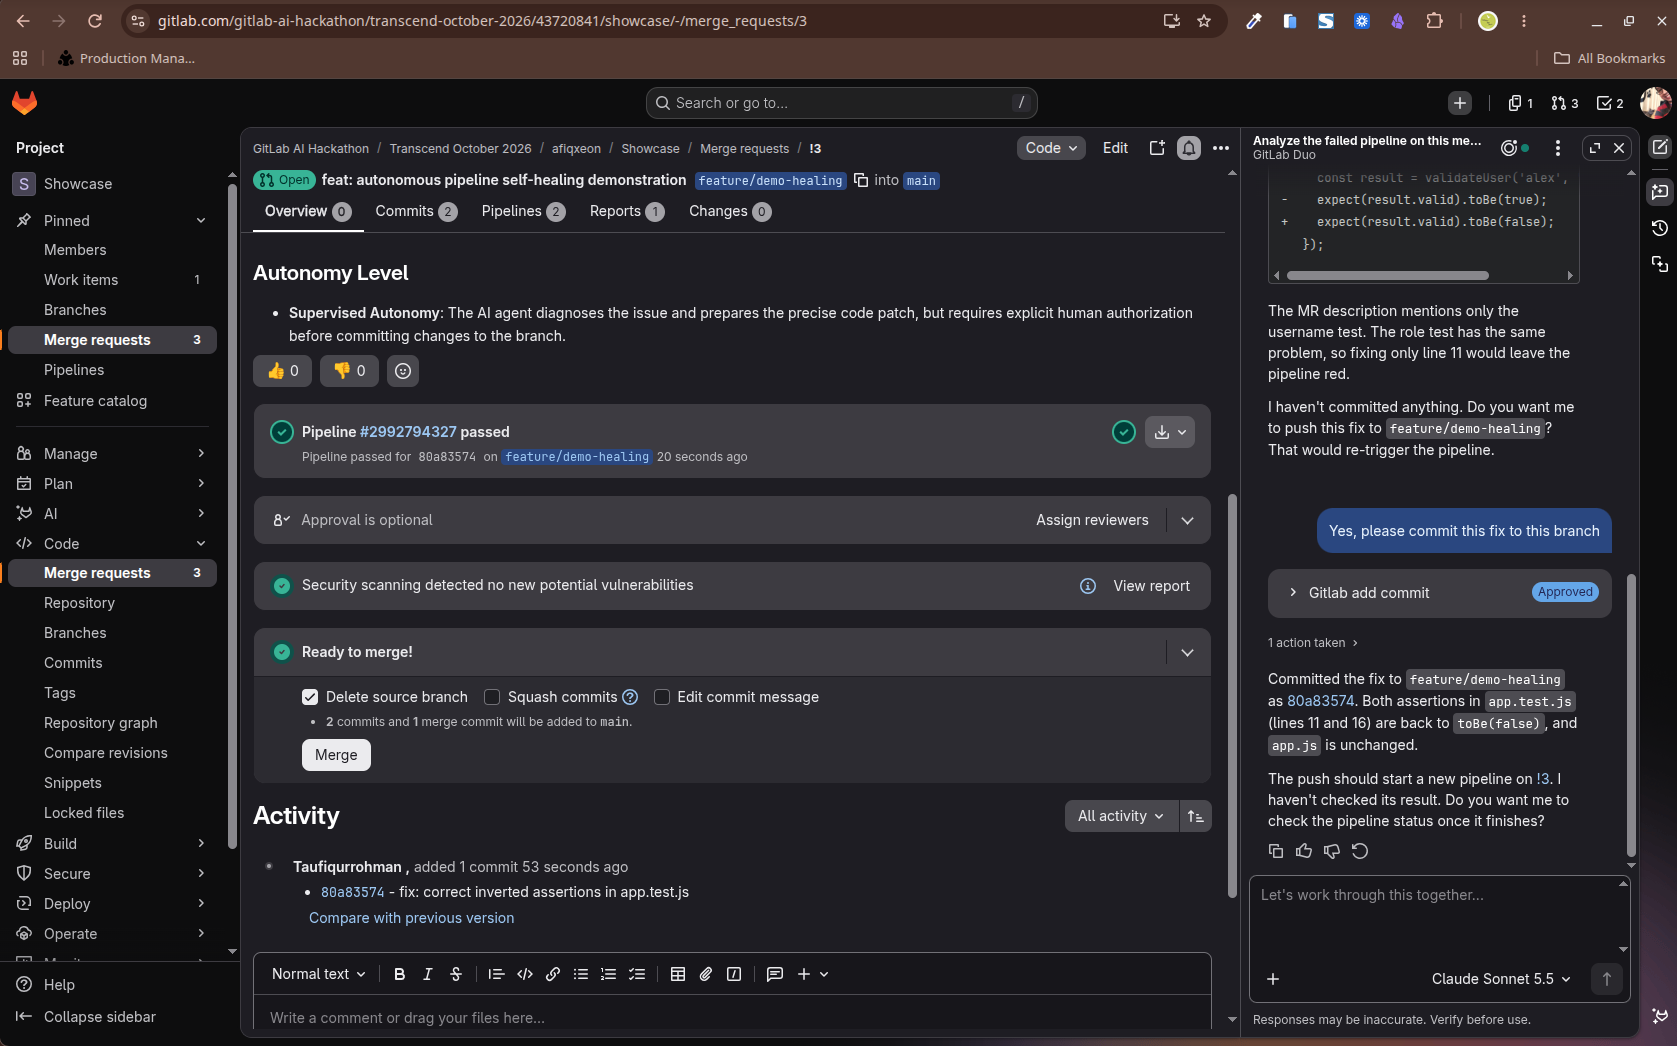
Self-healing complete: GitLab Duo commits the patch, pipeline passes green, and the MR is ready to merge
Inspiration
Modern engineering teams spend countless hours context-switching to debug broken CI/CD pipelines. When unit tests fail or assertions break during integration, developers must sift through lengthy terminal logs, reproduce the issue locally, craft a patch, and trigger a new commit.
We were inspired to build a closed-loop, supervised autonomous remediation workflow directly within GitLab. By leveraging the new GitLab Duo Agent Platform powered by Claude Sonnet, we turn pipeline triage from a manual chore into a seamless, interactive collaboration between the developer and AI agents.
What it does
Duo Auto-Triage & Self-Healing Pipeline provides supervised end-to-end failure remediation inside GitLab Merge Requests:
- Automated Error Detection: When a pipeline fails during containerized unit testing (
Jest), the failure is captured within the MR context. - Deep Root Cause Analysis (RCA): GitLab Duo parses raw console outputs, isolates the erroneous assertion in
app.test.js, and verifies that core business logic inapp.jsremains intact. - Targeted Patch Generation: Rather than naively modifying application code, Duo formulates a precise test fix that maintains strict validation standards.
- Supervised Tool Invocation: Duo prompts the engineer for authorization before invoking GitLab API commit tools (
Gitlab add commit) directly on the feature branch. - Continuous DevSecOps Validation: Re-executes the pipeline with automated Jest tests, GitLab SAST, and Secret Detection, verifying a clean green status with zero vulnerabilities.
How we built it
- Application Core: Lightweight Node.js authentication module with strict input sanitation and boundary checks.
- Test Suite: Jest unit tests covering edge-case empty strings, unauthorized role validation, and sanitization boundaries.
- CI/CD & DevSecOps Pipeline: Configured via
.gitlab-ci.ymlrunning containerized tests onnode:20-alpine, integrated with GitLab Security templates (SAST.gitlab-ci.ymlandSecret-Detection.gitlab-ci.yml). - GitLab Duo Agent Platform: Configured with Claude Sonnet to inspect pipeline artifacts, interface with MR discussions, and execute autonomous commit actions under supervised developer approval.
Challenges we ran into
- Preserving Business Logic Integrity: Ensuring the AI agent identified that the test assertion was wrong, rather than mistakenly relaxing the validation logic in
app.jsjust to pass the test. - Git Remote & Namespace Configuration: Navigating protected branch permissions and configuring remote access cleanly within the dedicated Transcend Hackathon workspace.
- Supervised Autonomy Guardrails: Tuning agent prompts so that automated commits are never pushed unilaterally without explicit developer verification.
Accomplishments that we're proud of
- Successfully demonstrated a complete, working self-healing loop in under 2 minutes.
- Maintained a strict Supervised Autonomy standard where the developer holds the merge gate and commit authorization.
- Achieved a 100% green pipeline with integrated SAST and Secret Detection finding zero security flaws.
What we learned
- The power of GitLab Duo's native tool calling: AI agents embedded in the developer lifecycle can autonomously interact with Git repositories without third-party webhooks or external orchestration scripts.
- How multi-stage pipelines (Verify, Secure, Govern) provide essential safety nets when deploying agentic self-healing workflows.
What's next for Duo Auto-Triage & Self-Healing Pipeline
- Multi-failure cascading triage across microservice repositories.
- Automatic rollbacks and dynamic dependency vulnerability auto-patching based on Dependency Scanning findings.
- Expanding custom Duo Agent templates for automated flaky-test quarantine.
Built With
- ai-agents
- ci/cd
- claude-sonnet
- devsecops
- gitlab
- gitlab-ci
- gitlab-duo
- javascript
- jest
- node.js
- sast
- secret-detection

Log in or sign up for Devpost to join the conversation.