Inspiration
The problem I wanted to solve was not meeting transcription. It was what happens after the meeting, when the summary is already forgotten and the original promise has been reduced to a vague task. Teams can see commits, comments, and status updates, but still struggle to answer whether the promised outcome was actually delivered.
What it does
Dost is a stateful commitment operations desk for teams:
- Cited extraction: Gemini 3.5 Flash proposes commitments with exact transcript citations.
- Human review gate: Unresolved or consequential fields must be resolved before activation.
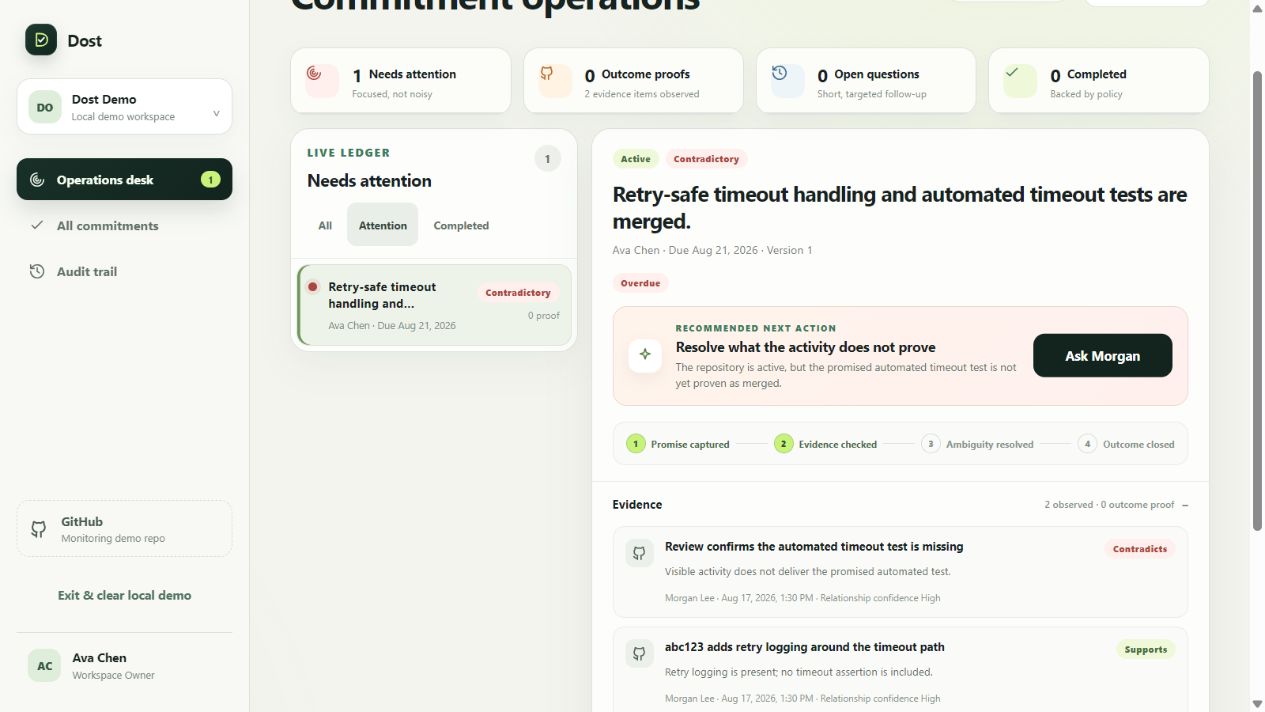
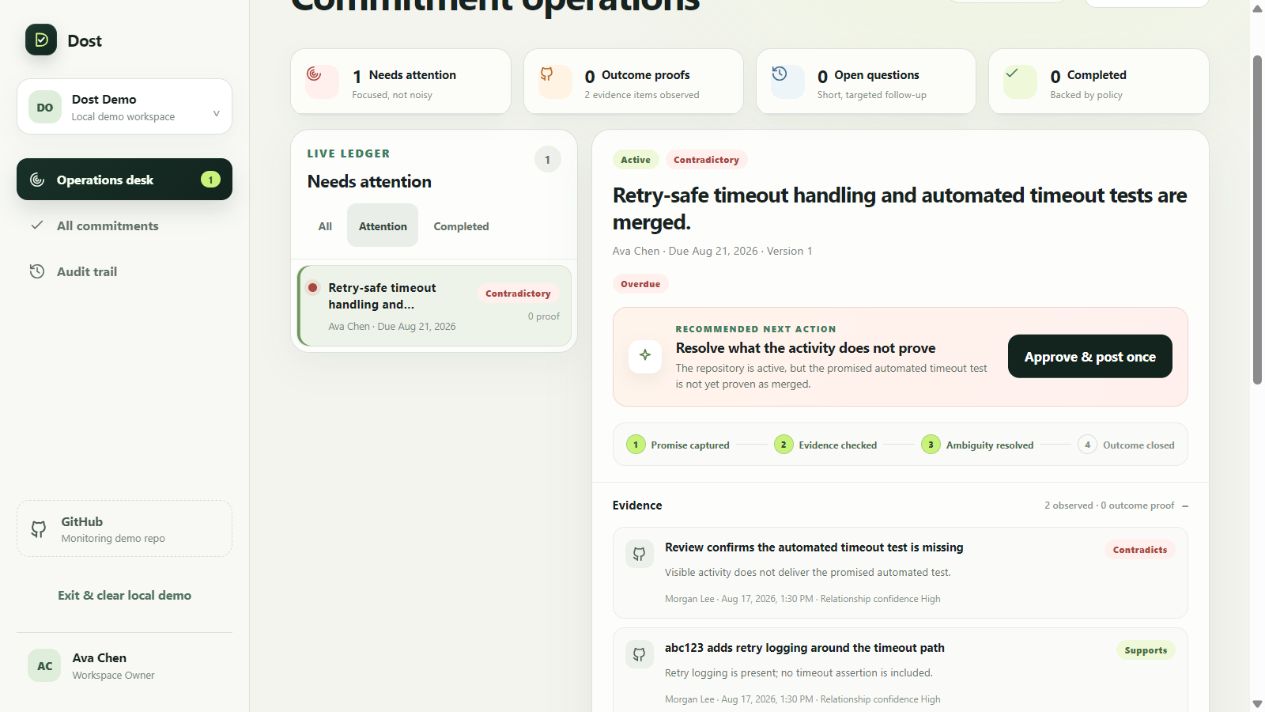
- Outcome vs. Activity: It compares live GitHub evidence against the promised outcome. Commits and comments do not count as proof of completion until the policy is satisfied.
- Targeted questions: Asks precise, non-generic follow-ups when evidence is missing or contradictory.
- Authorized actions: Executes bounded GitHub comments only through a deterministic ActionExecutor after version-bound approval.
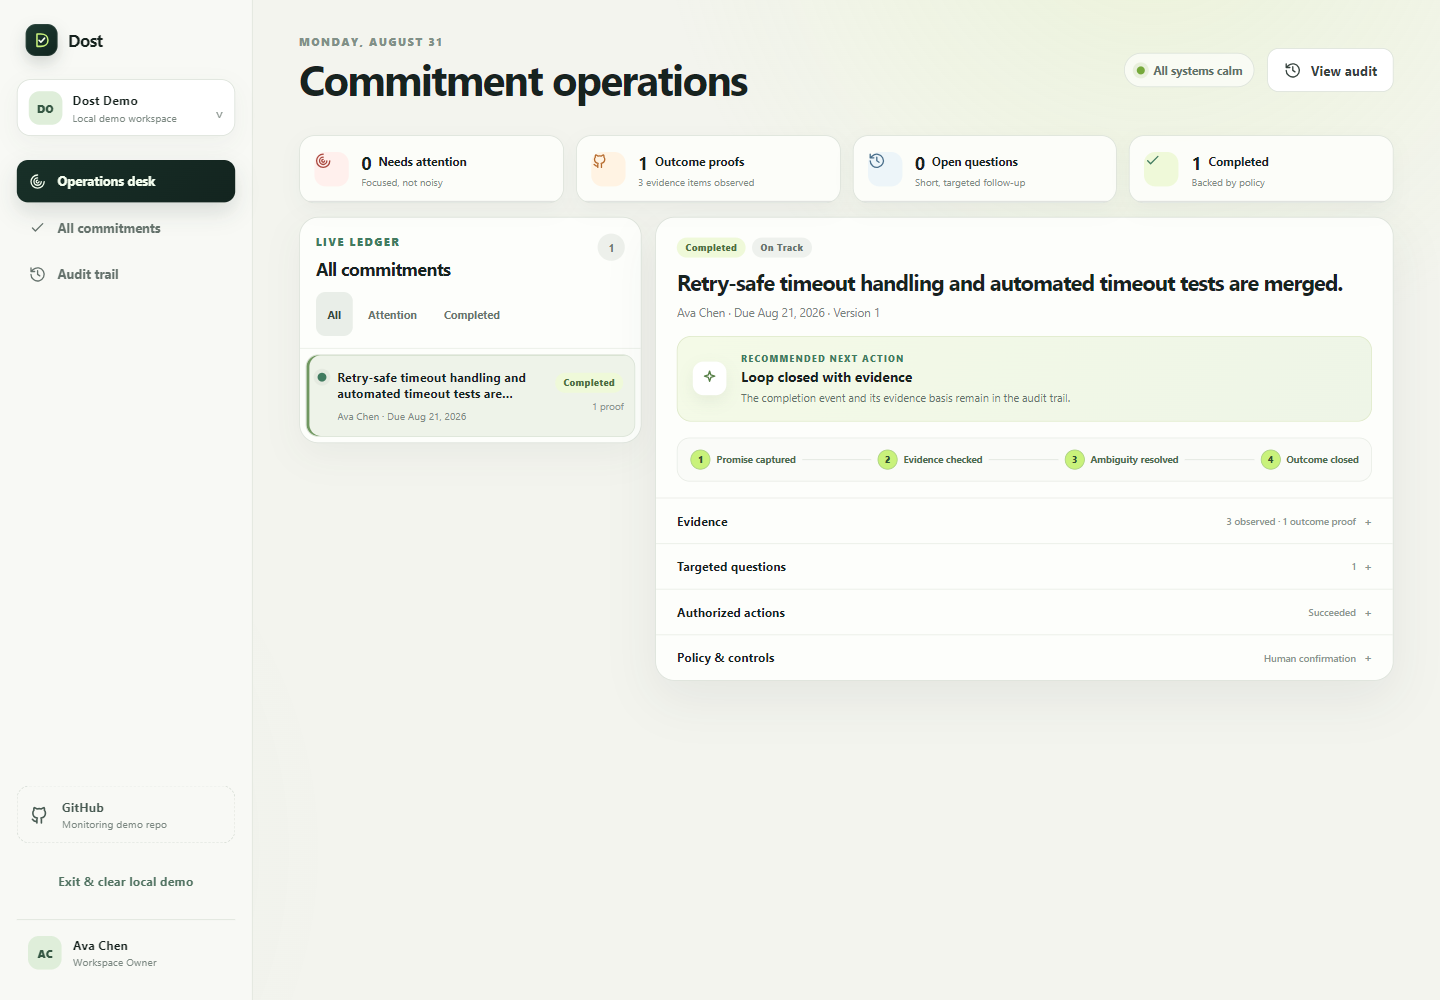
- Verified completion: Closes commitments only when merged PR evidence and human confirmation pass.
How I built it
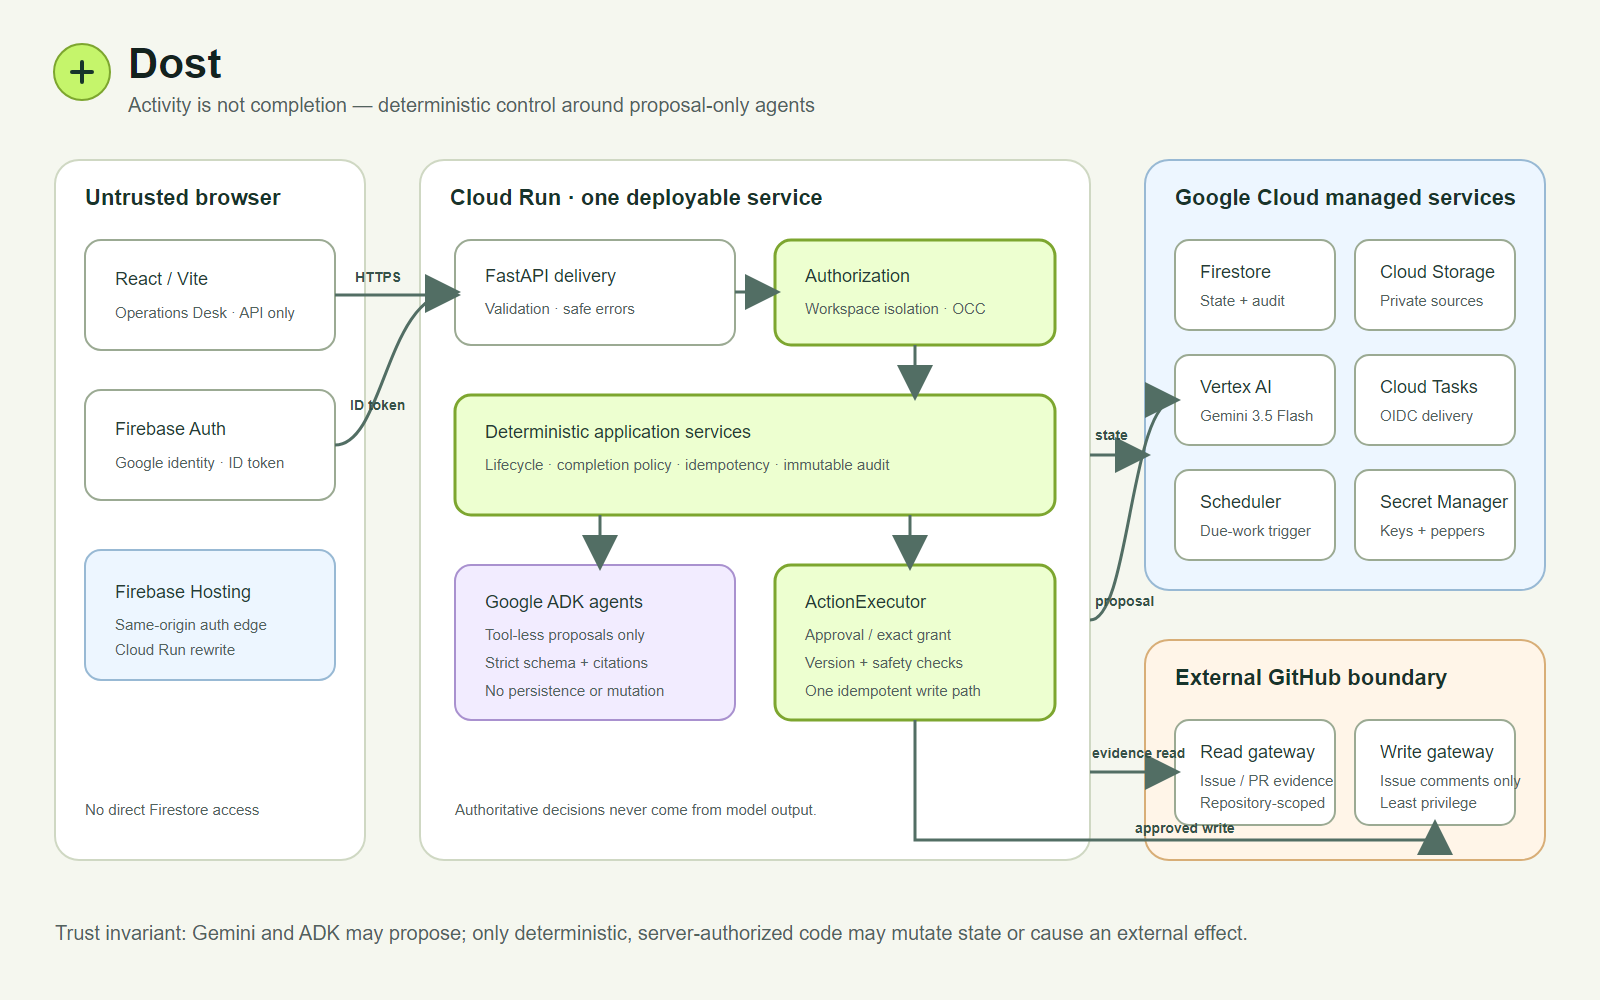
The React/Vite interface and FastAPI API run together as a single container on Google Cloud Run. Firebase provides same-origin Google authentication while workspace decisions remain server-authorized.
- State & Audit: Firestore stores authoritative product state, versioned commitments, and immutable audit history.
- AI & Reasoning: Vertex AI runs Gemini 3.5 Flash through tool-less Google Agent Development Kit (ADK) agents.
- Async Reliability: Cloud Tasks and Cloud Scheduler handle bounded asynchronous monitoring.
- Security: Secret Manager protects the GitHub App private keys.
ADK agents are deliberately tool-less proposals: deterministic application code owns authorization, idempotency, retries, reconciliation, and all GitHub writes.
Challenges
The hardest part was preserving the boundary between model suggestions and authoritative state. An agent needs judgment, but a plausible model response must never silently mutate commitments or trigger unverified external actions. We solved this with exact citation binding, immutable versioning, optimistic concurrency, and a deterministic ActionExecutor.
Accomplishments
The deployed application closes a complete, verifiable loop: cited transcript extraction, human review, activation, contradiction detection against live GitHub activity, targeted Q&A, authorized GitHub issue commenting, merged PR evidence reconciliation, human confirmation, and an immutable audit trail—running live on Google Cloud Run.
What I learned
Agentic AI becomes significantly more trustworthy when authority is narrow and transparent. Models excel at proposing interpretations and asking good questions, but consequential state transitions must remain deterministic.
What's next
- Expanding to Jira and Slack evidence connectors while keeping the same strict authorization boundaries.
- Scaling the bounded workspace ledger to support distributed multi-team operations.
Built With
- cloud-run
- cloud-scheduler
- cloud-storage
- cloud-tasks
- fastapi
- firebase-authentication
- firebase-hosting
- firestore
- gemini-3.5-flash
- github-app
- google-adk
- react
- secret-manager
- typescript
- vertex-ai
- vite

Log in or sign up for Devpost to join the conversation.