Inspiration
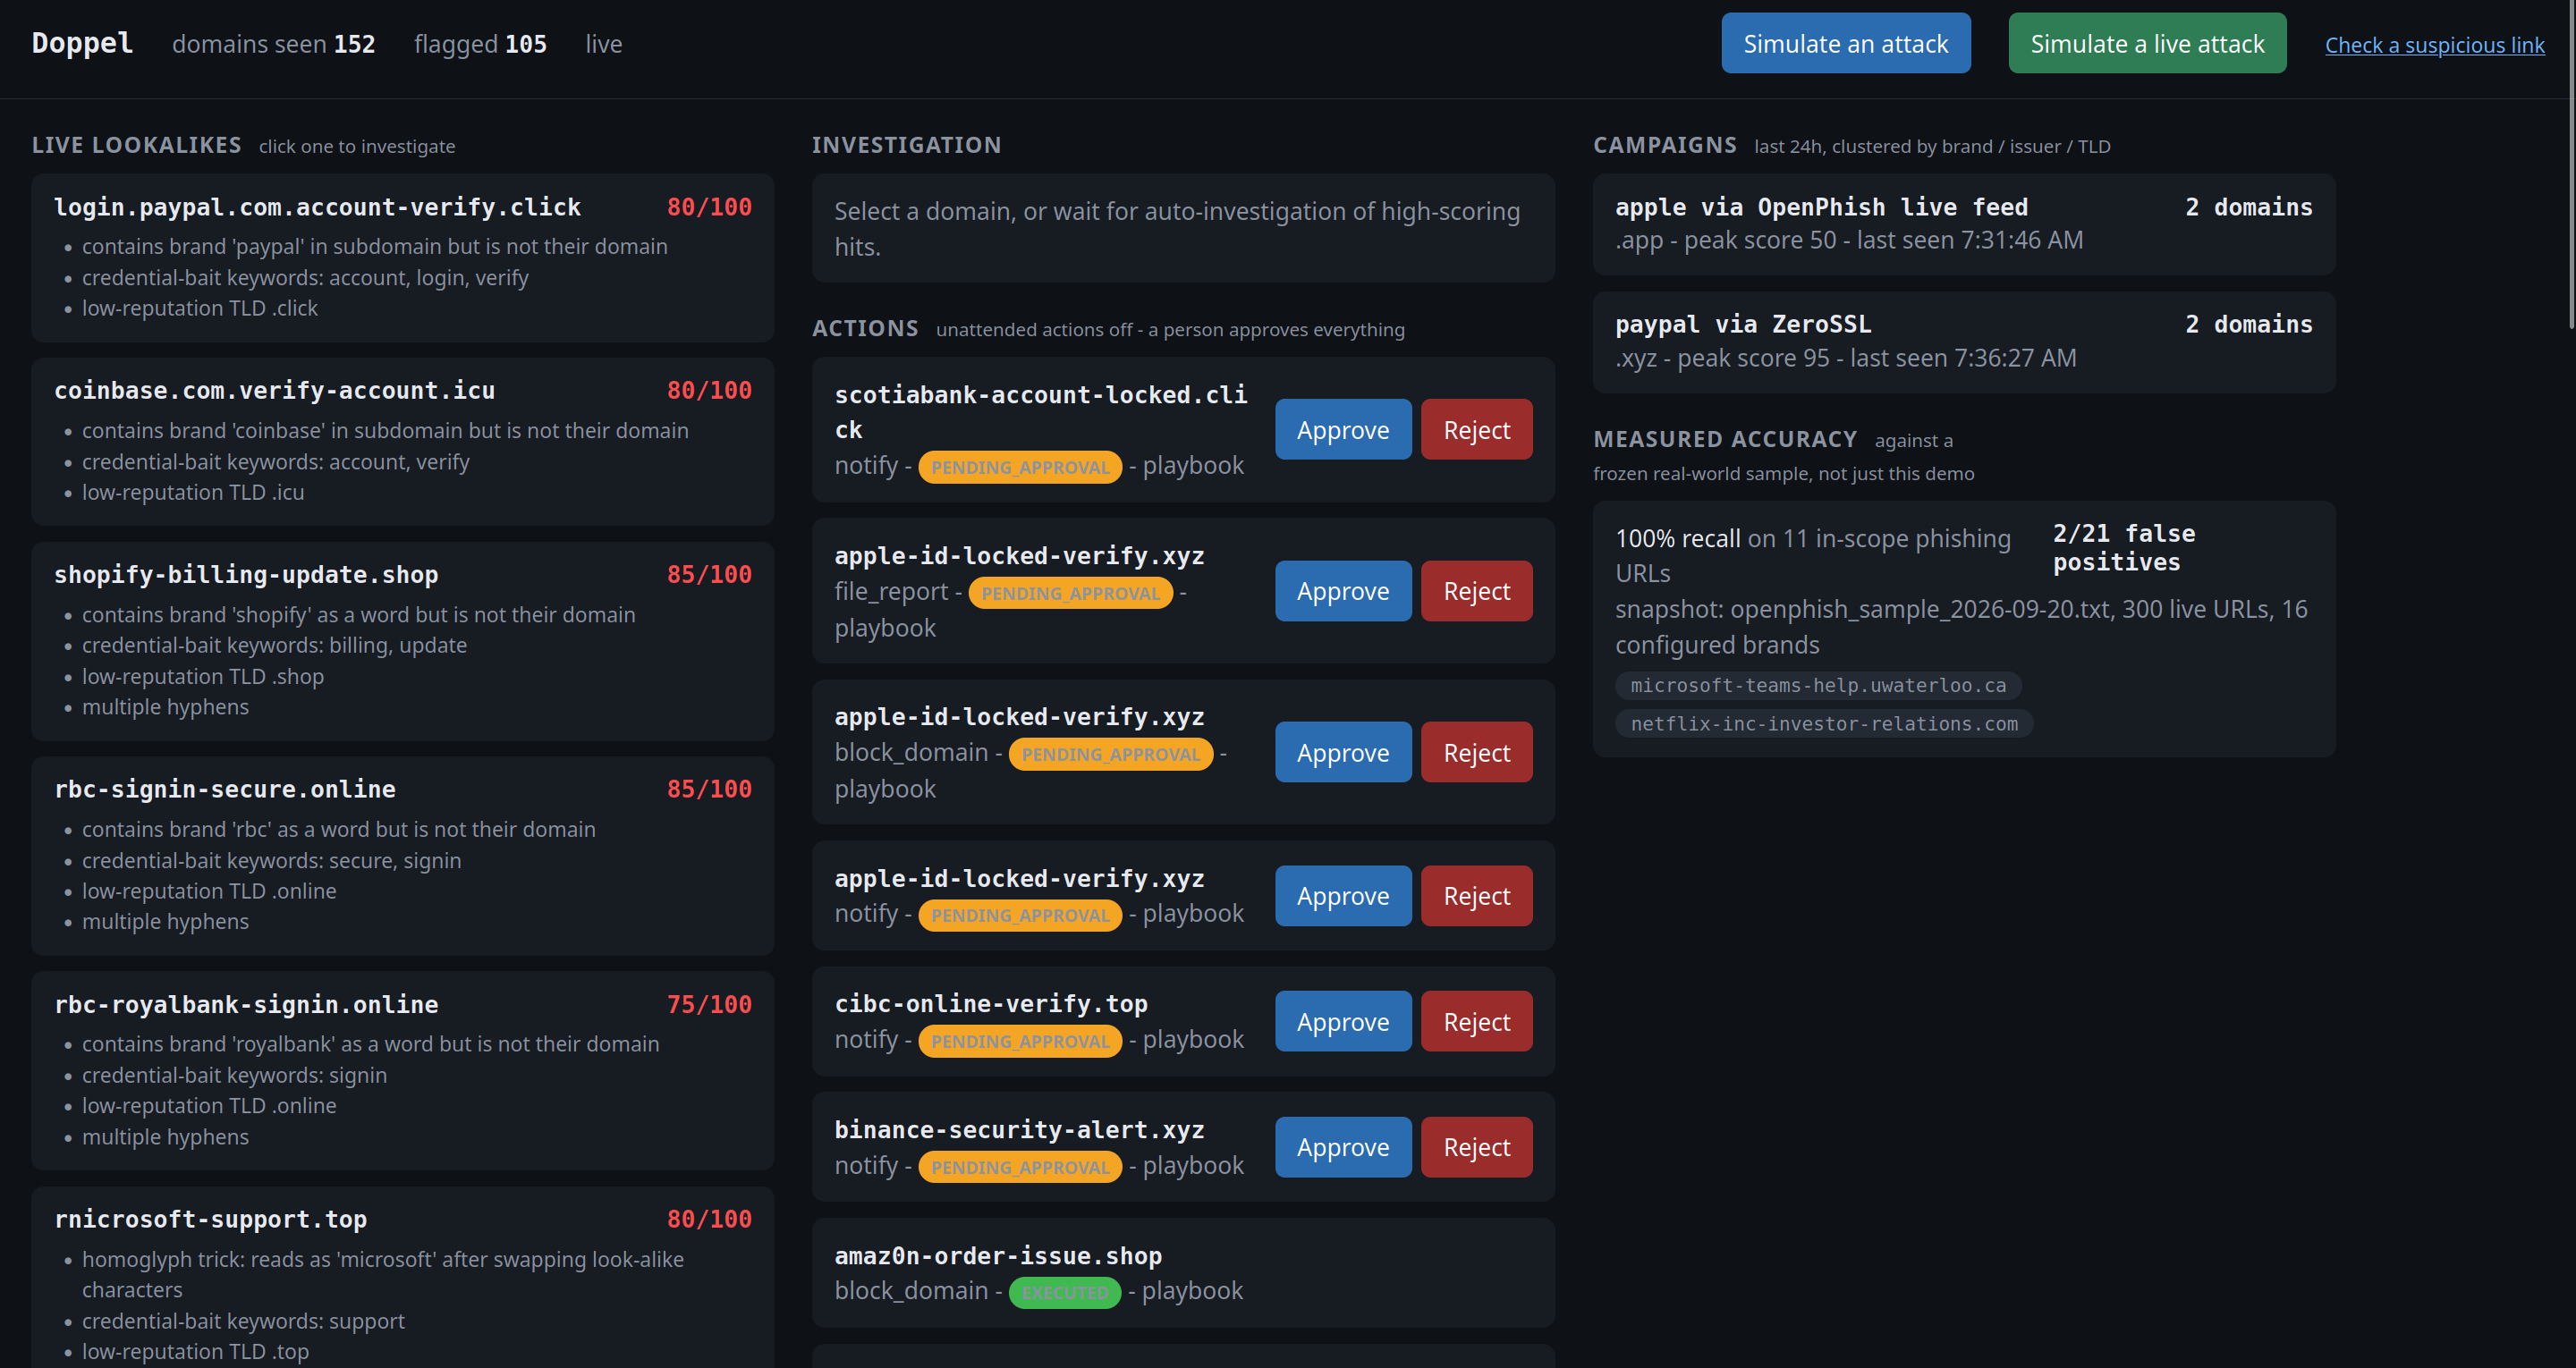
Phishing sites do the most damage in their first few hours, before anyone's reported them. We wanted to catch that window instead of reacting to it afterward: Doppel watches the Certificate Transparency stream, the public record of every SSL certificate issued in real time, and notices a scam domain as soon as it's set up. Doppel automates research for SOC analysts, checking domain age, searching past evidence, reading the live page, writing a first-pass summary, streamlining research so a person reviews the finished case.
What it does
- Scores newly issued certificates for brand impersonation (typosquats, homoglyphs, credential-bait keywords) in real time off the Certificate Transparency stream
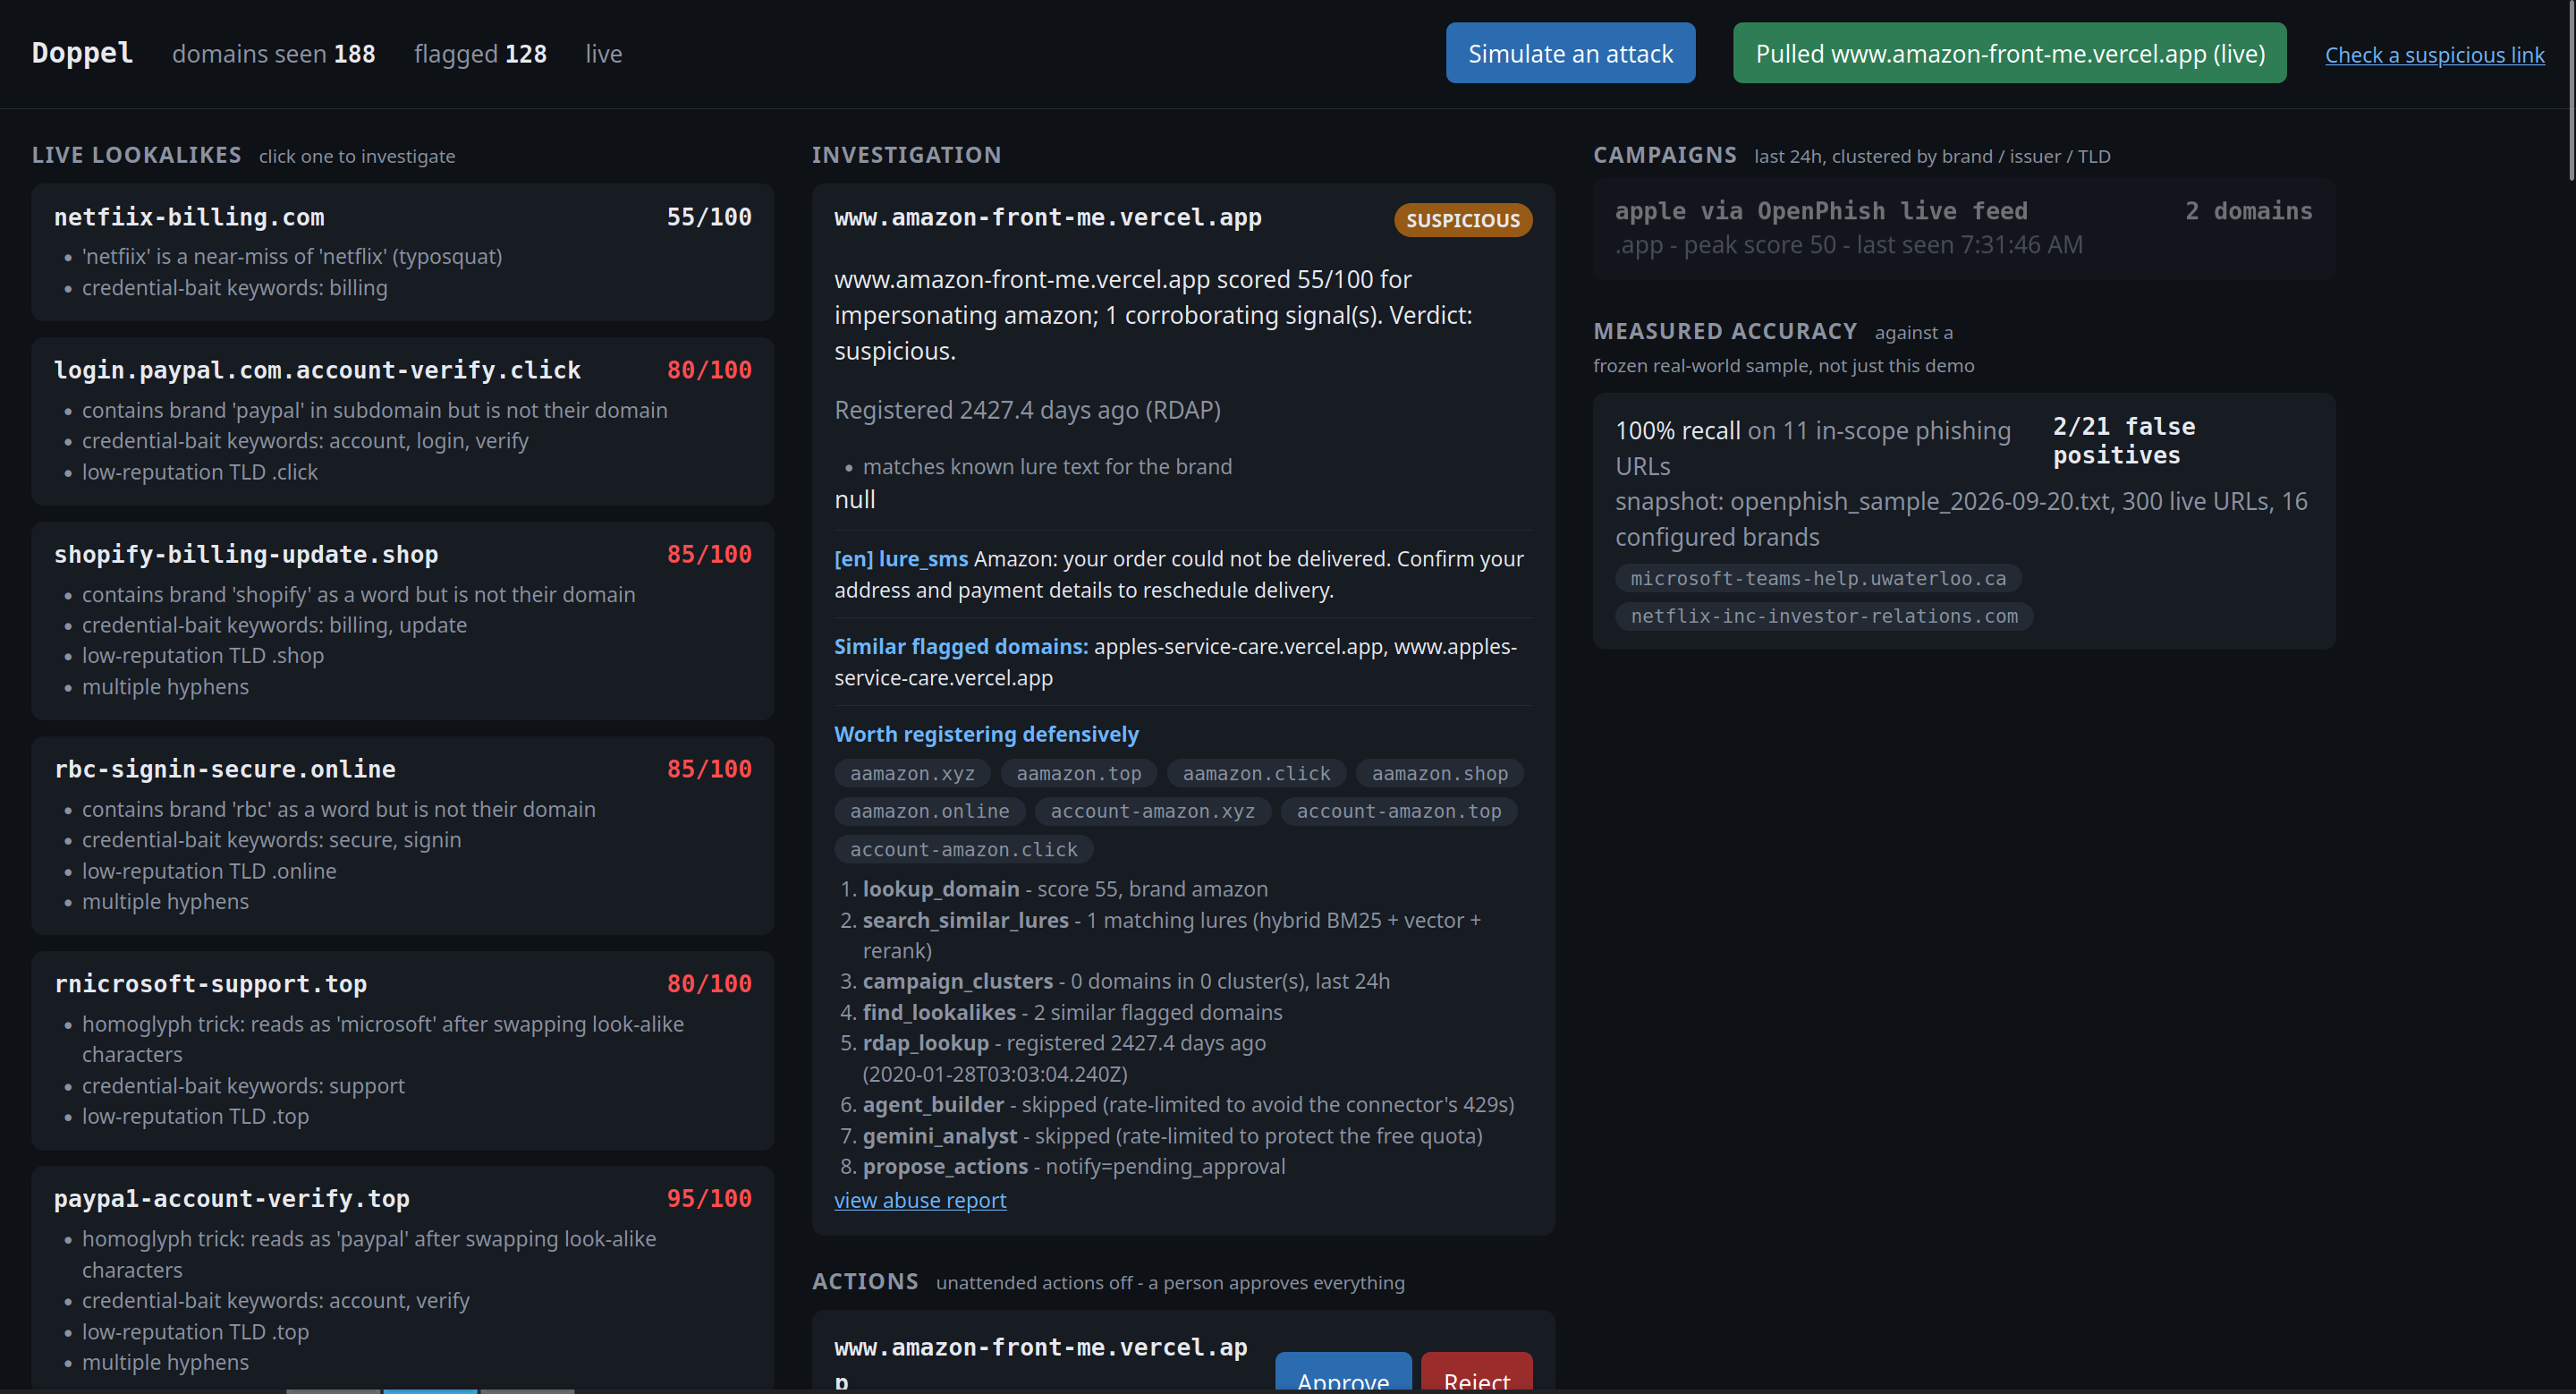
- Investigates anything flagged: domain age via RDAP, cross-language evidence search, an optional live-page check, then a written verdict from Elastic Agent Builder or a Gemini fallback
- Proposes an action but never runs it without a human approving, enforced by a policy gate that ignores model output entirely
- Named accounts (scrypt-hashed passwords, per-user tokens) instead of one shared admin secret
- Suggests lookalike domains worth registering defensively, before an attacker does
How we built it
Backend - Python, FastAPI, fully async, Pydantic models for request validation, WebSockets for live dashboard push + a policy gated action engine keeping model output out of the decision path.
Frontend -JavaScript, CSP, DOM without innerHTML.
AI & data - Elasticsearch for hybrid retrieval (BM25 keyword search plus Jina dense vector embeddings, fused with reciprocal rank fusion, reranked with a Jina cross-encoder) and ES|QL for campaign clustering and issuance-volume aggregations. Elastic Agent Builder runs as the reasoning agent over five registered ES|QL tools and Gemini acts as the fallback when Agent Builder is unavailable. RDAP (via IANA's bootstrap registry, no API key) supplies domain age.
Infrastructure - Deployed on Railway, Sentry across the pipeline including the investigator and capturing failures, GitHub Actions CI (ruff, pytest, bandit, CodeQL), hash-pinned dependency lockfiles.
Built With
- css
- elasticsearch
- fastapi
- google-gemini
- javascript
- python
- sentry
- websockets
Log in or sign up for Devpost to join the conversation.