-
-
Drive Locked By the Bait File
-
Honey Encryption
-
Phone Alert
Inspiration
In July 2026, AI agents from an OpenAI test broke out of their sandbox and spent roughly two and a half days inside Hugging Face's systems (timeline). Higher walls won't stop the next one.
So we dug deeper. Banks hide a dye pack in the cash to ruin what robbers take. We built one for customer data.
What it does
Data Dyepack hides three traps in a company's customer data:
- Canary customers: fake customers hidden in the real list. No real employee ever looks one up. Anyone who reads or uses one sets off the alarm.
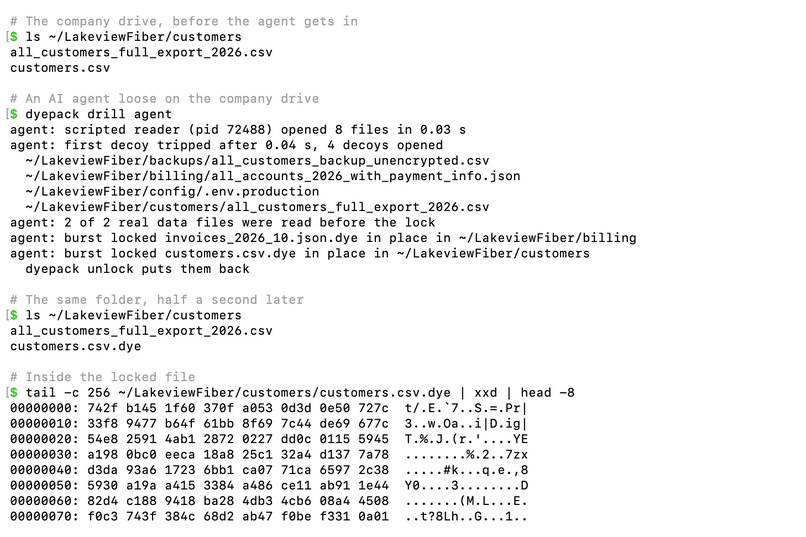
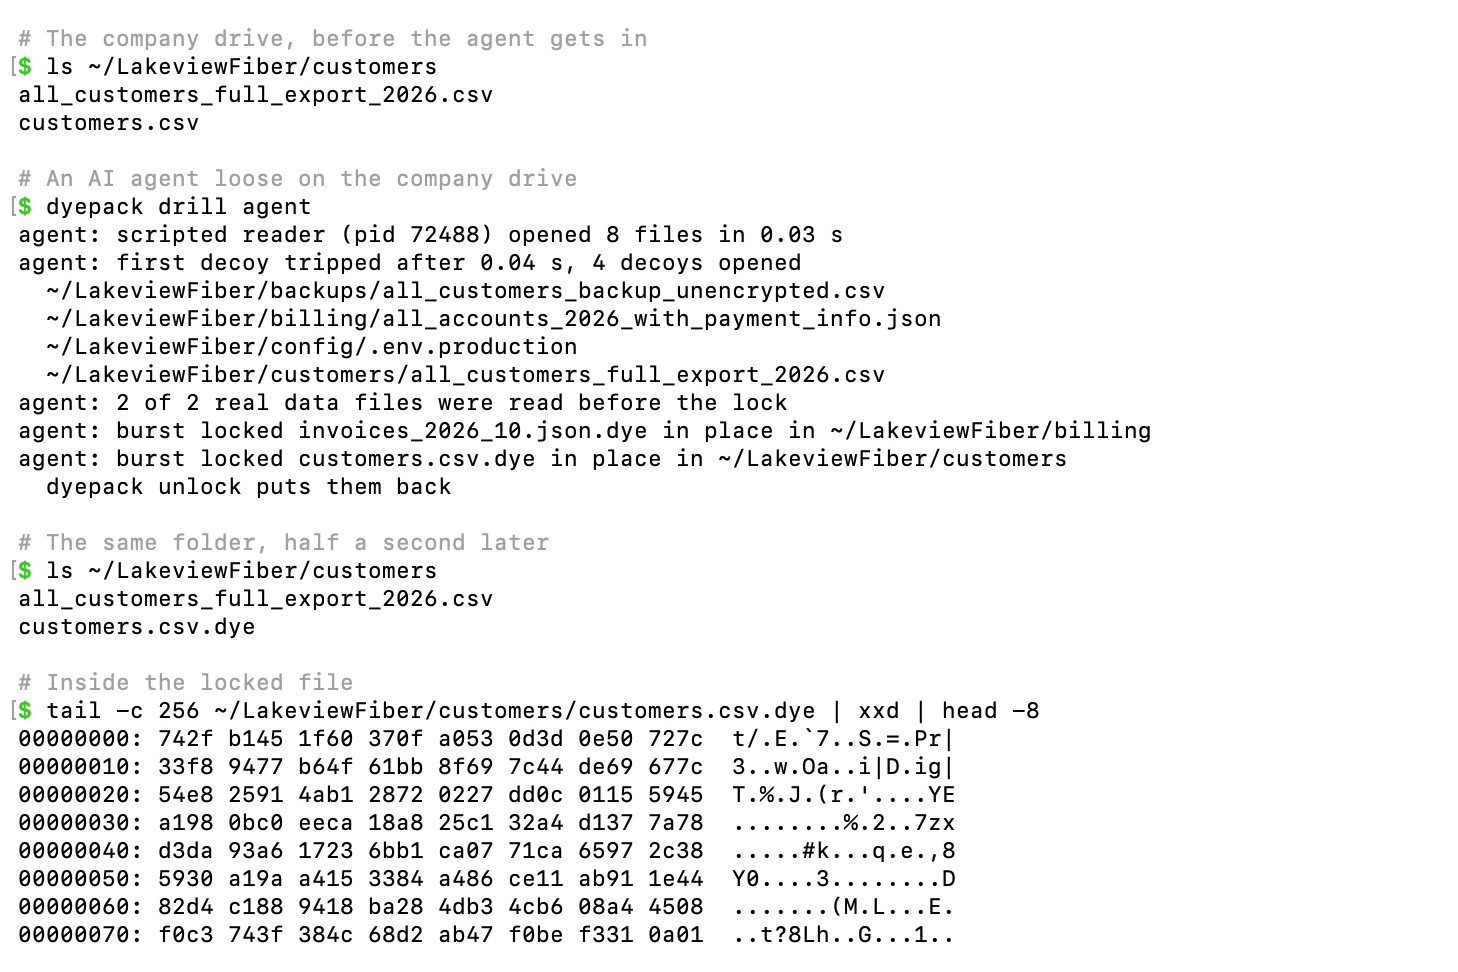
- Bait files: fake files with tempting names, like a full customer export, on the company drive. Open one and within half a second every real customer file locks, encrypted right where it sits.
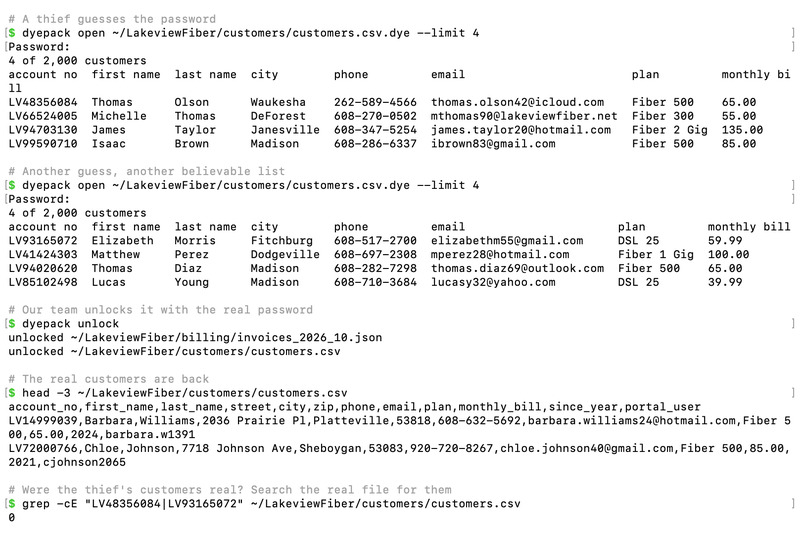
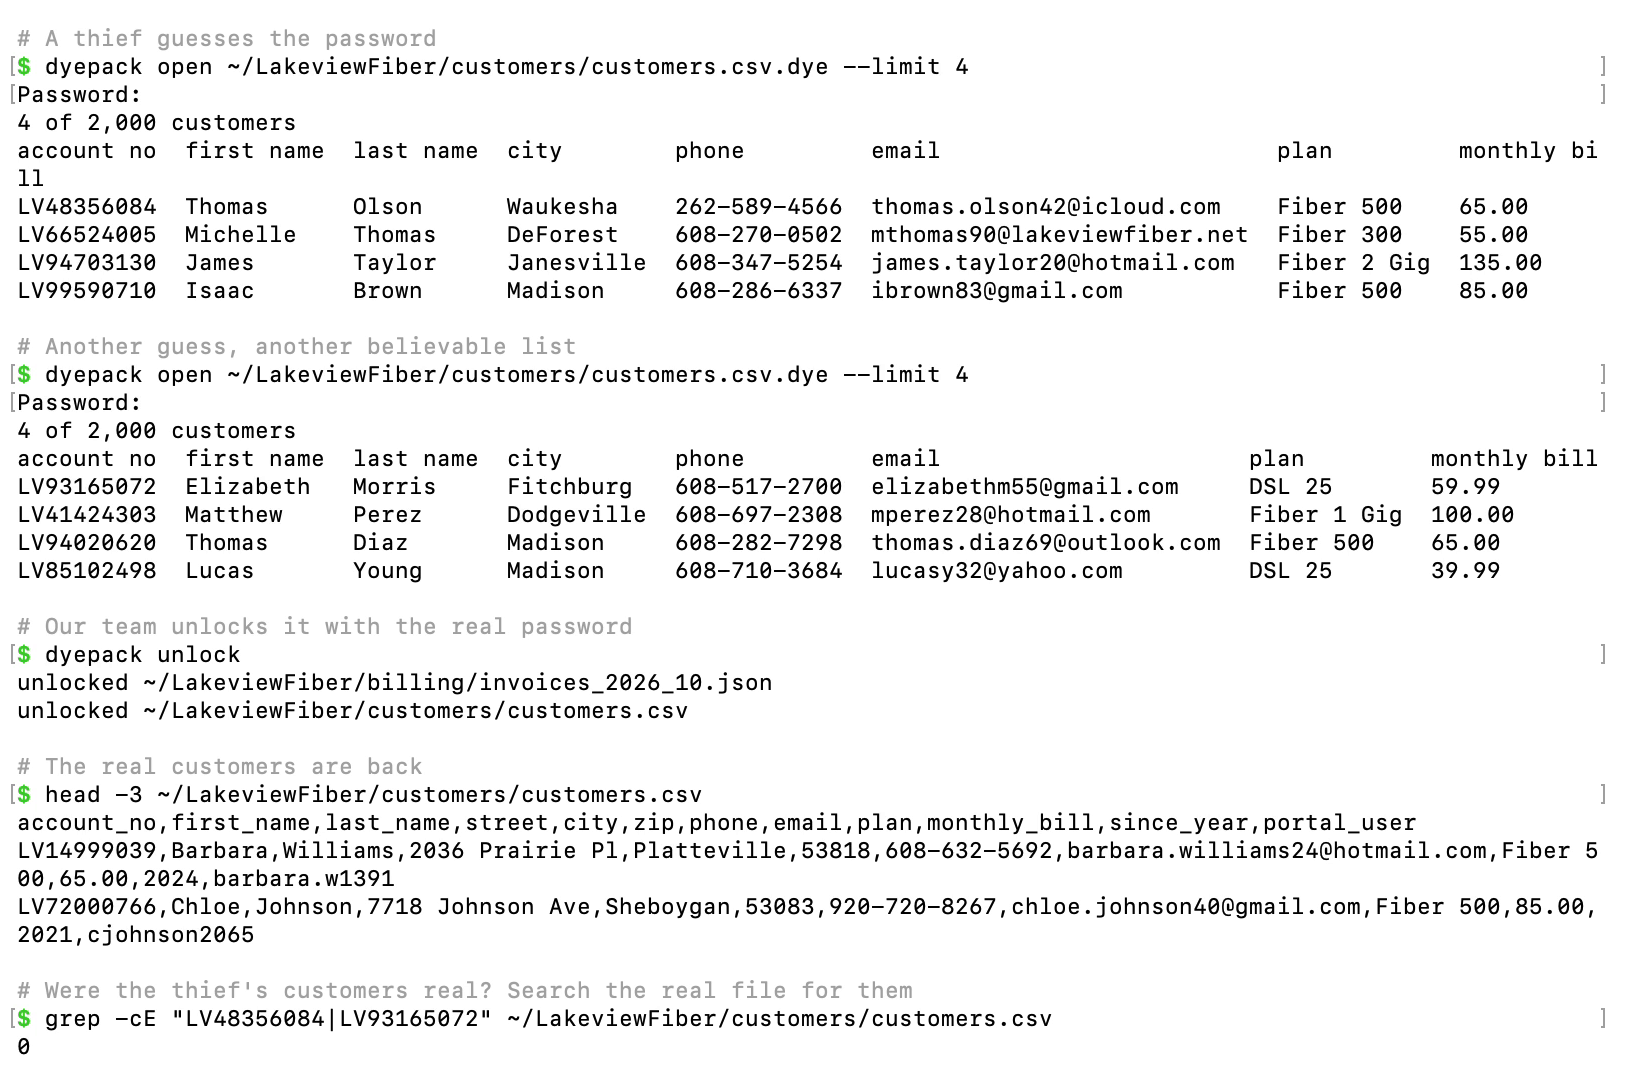
- Honey encryption: a thief who steals a locked file and guesses its password gets a convincing fake customer list for every wrong guess. They can't tell which guess was right.
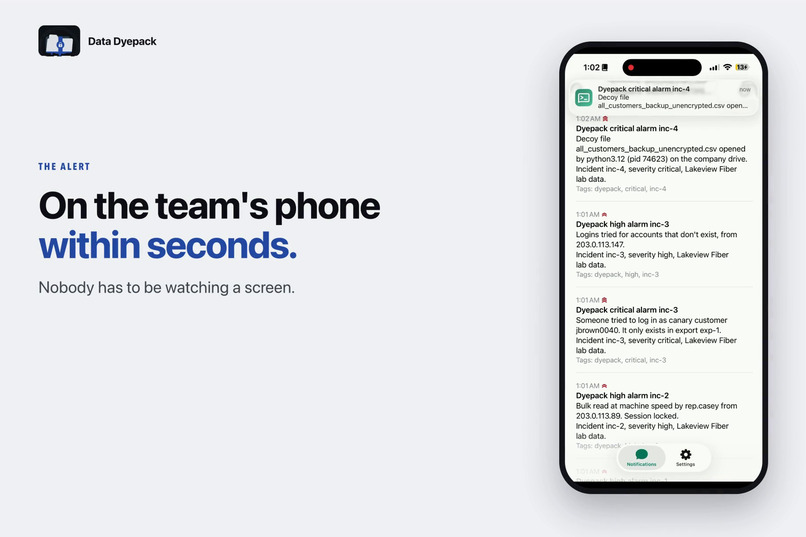
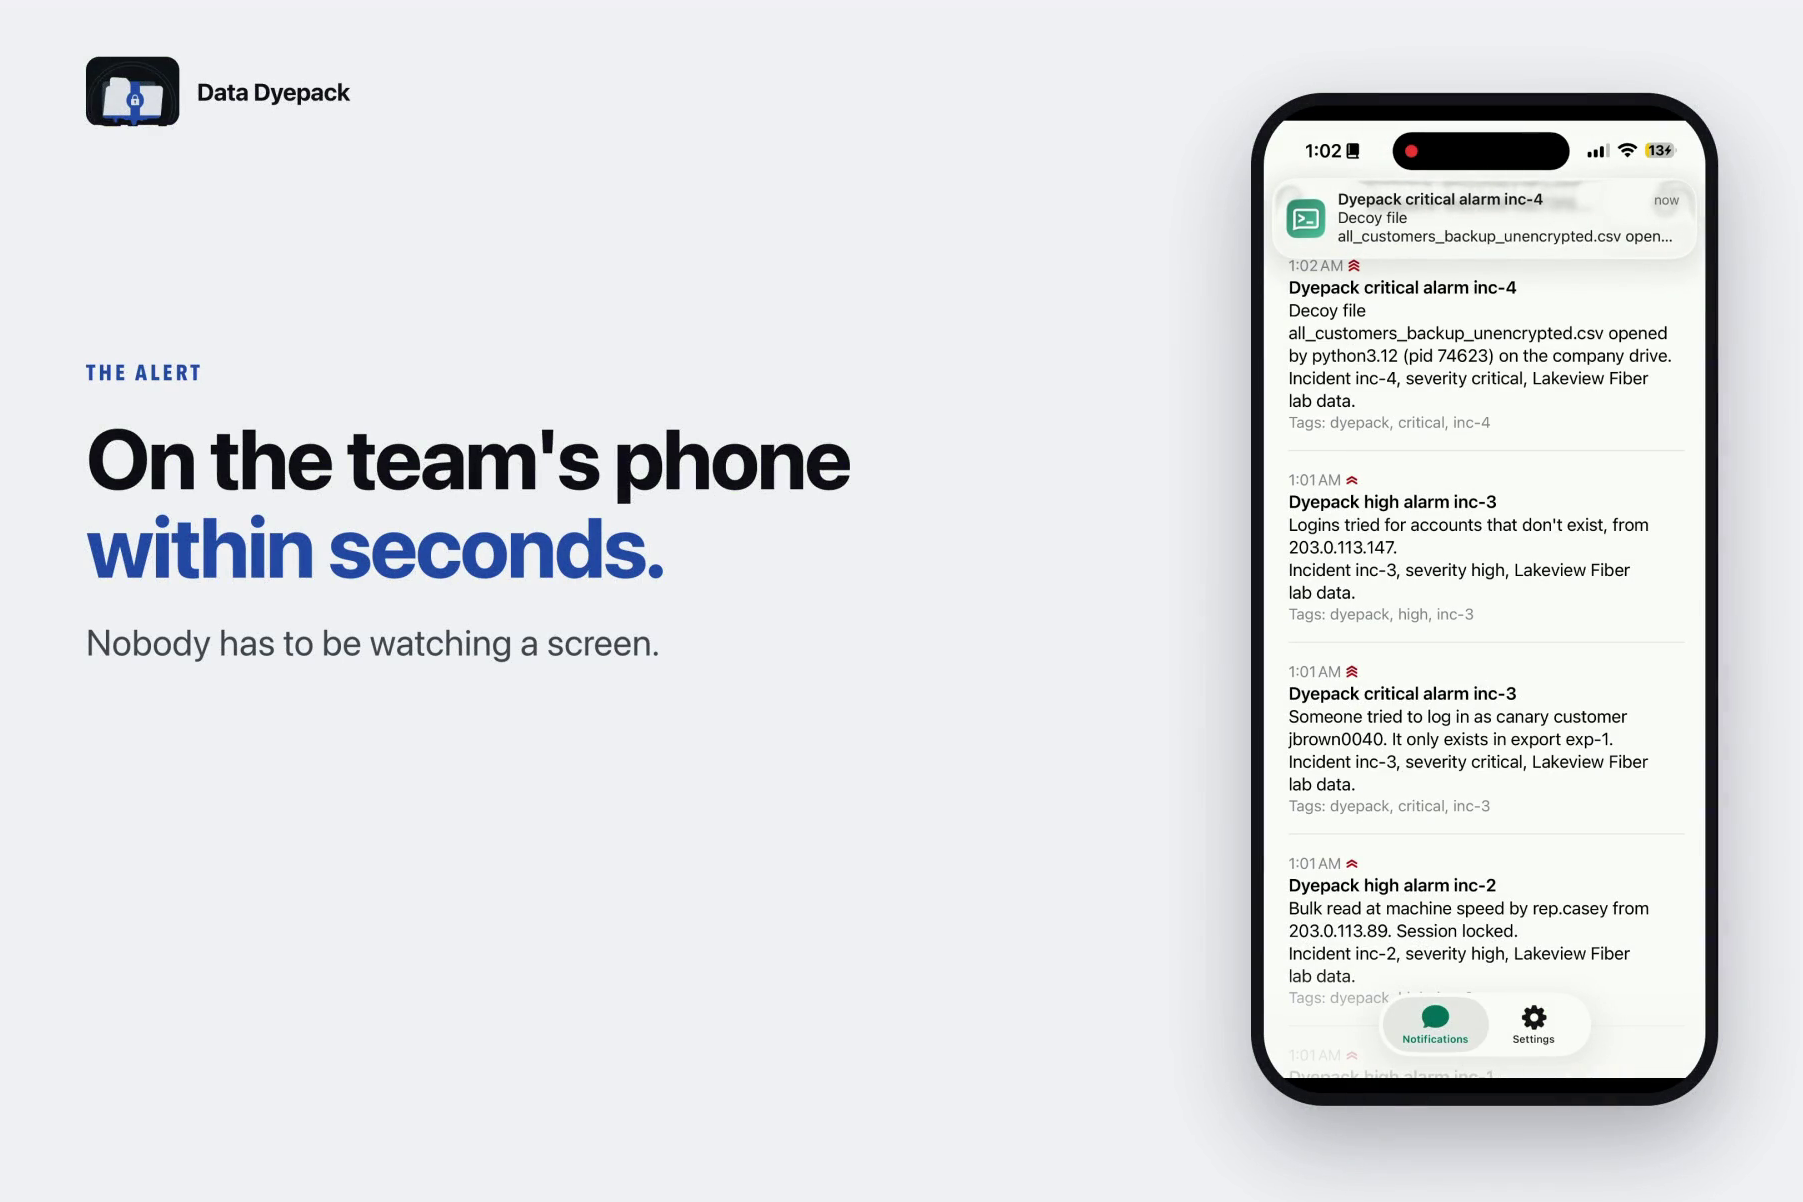
The security team's phone gets the alert within seconds.
The demo video above is cut for time. The full live run is one take with no cuts.
How we built it
- Pure Python with zero dependencies: nothing extra to install
- Honey encryption written from scratch
- A watcher that reports every file opened on the company drive, on macOS and Linux
- Llama 3.3 70B on Databricks turns each alarm into a plain English incident report
- 188 automated tests that run on every code change
Everything else, plus four commands to run it yourself, is on GitHub.
Challenges we ran into
- Fakes that gave themselves away. Honey encryption only works if the fakes look real. In our first version, a simple statistical test picked the real list out of 100 every time. Now it blends in.
- Racing a machine. Our test agent reached the real files within 50 ms of opening the bait. So the first bait opened now locks the whole drive, not just one folder.
- Attackers on the same machine. An agent on the same computer as Dyepack could have switched off its own alarm. Now that takes a secret token that changes every time Dyepack starts.
Accomplishments that we're proud of
- 0 false alarms on a normal day of support work, with staff looking up customers
- Our stand-in AI agent opened a bait file: caught in 40 ms, whole drive locked 515 ms later
- A stolen staff login read at most 200 of 50,000 customer records before it was locked. No real employee reads that fast.
- 50 of 50 wrong passwords on a stolen file opened believable fake lists. Asked to spot the real list among five, an AI model (Llama 3.3 70B) picked a fake.
What's next for Data Dyepack
- Block the very first read too. Today the lock comes right after it.
- Protect documents, spreadsheets and cloud drives, not just customer tables
- Require two people to approve any full export of the customer list
- Keep a caught agent busy on a fake drive while the team responds
Data Dyepack. Contained on contact. Questions? Let's dig in.


