-
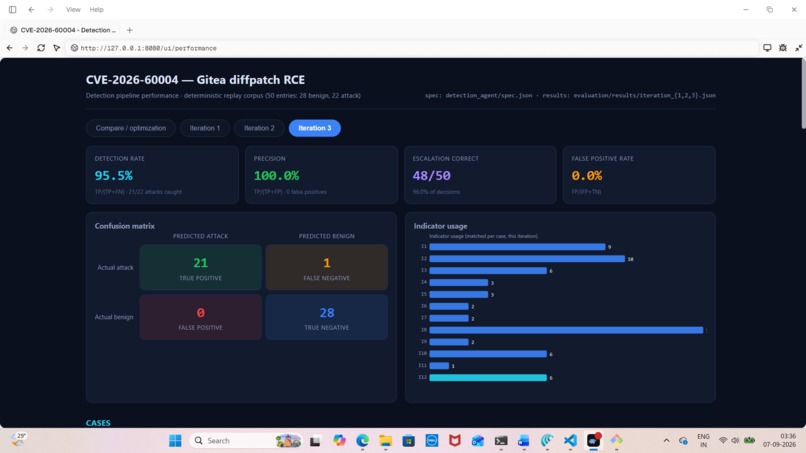
Dashboard Metrics
Inspiration
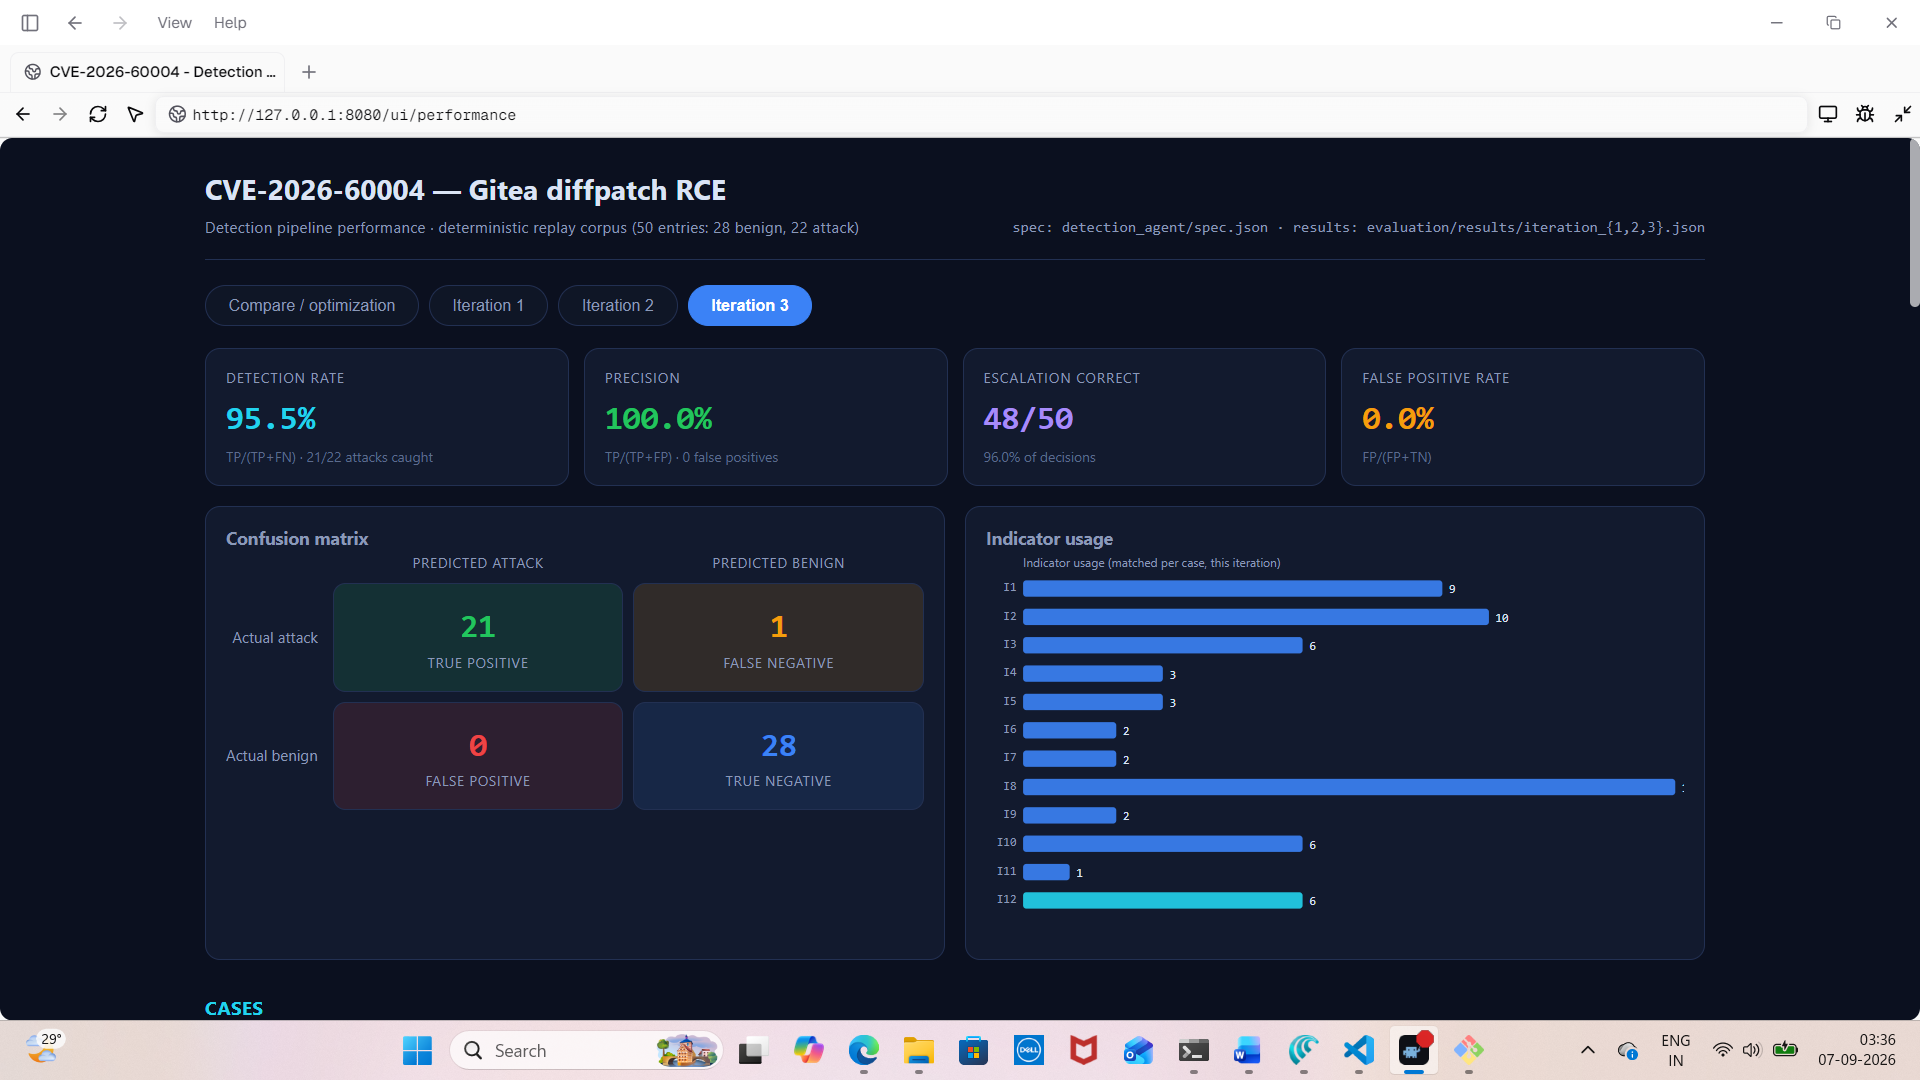
CVE Sentinel takes a CVE and writes its own detector for it — then tests that detector against real attack traffic, catches its own mistakes, and rewrites itself to fix them. No human tuning the rules by hand. On CVE-2026-60004, a critical Gitea RCE, it went from 82% detection with 5 false positives on its first try, to 91% detection with zero false positives after one self-critique cycle. Every decision is traced end-to-end, so a security analyst can audit exactly why it flagged — or cleared — an event.
What it does
How we built it
Challenges we ran into
Accomplishments that we're proud of
What we learned
What's next for CVE Sentinel
DEmo video:https://drive.google.com/file/d/1UJq-IfBNv82qvgZ6popnoEeVamYF3W4F/view?usp=sharing
Built With
- ao
- neatlogs
- tensormux


Log in or sign up for Devpost to join the conversation.