Inspiration
Compliance teams often review invoices, identity documents, and contracts manually. The risk is not only missing data; it is releasing a record whose uncertainty was never reviewed. Compliance Copilot makes uncertainty visible and every decision traceable.
What it does
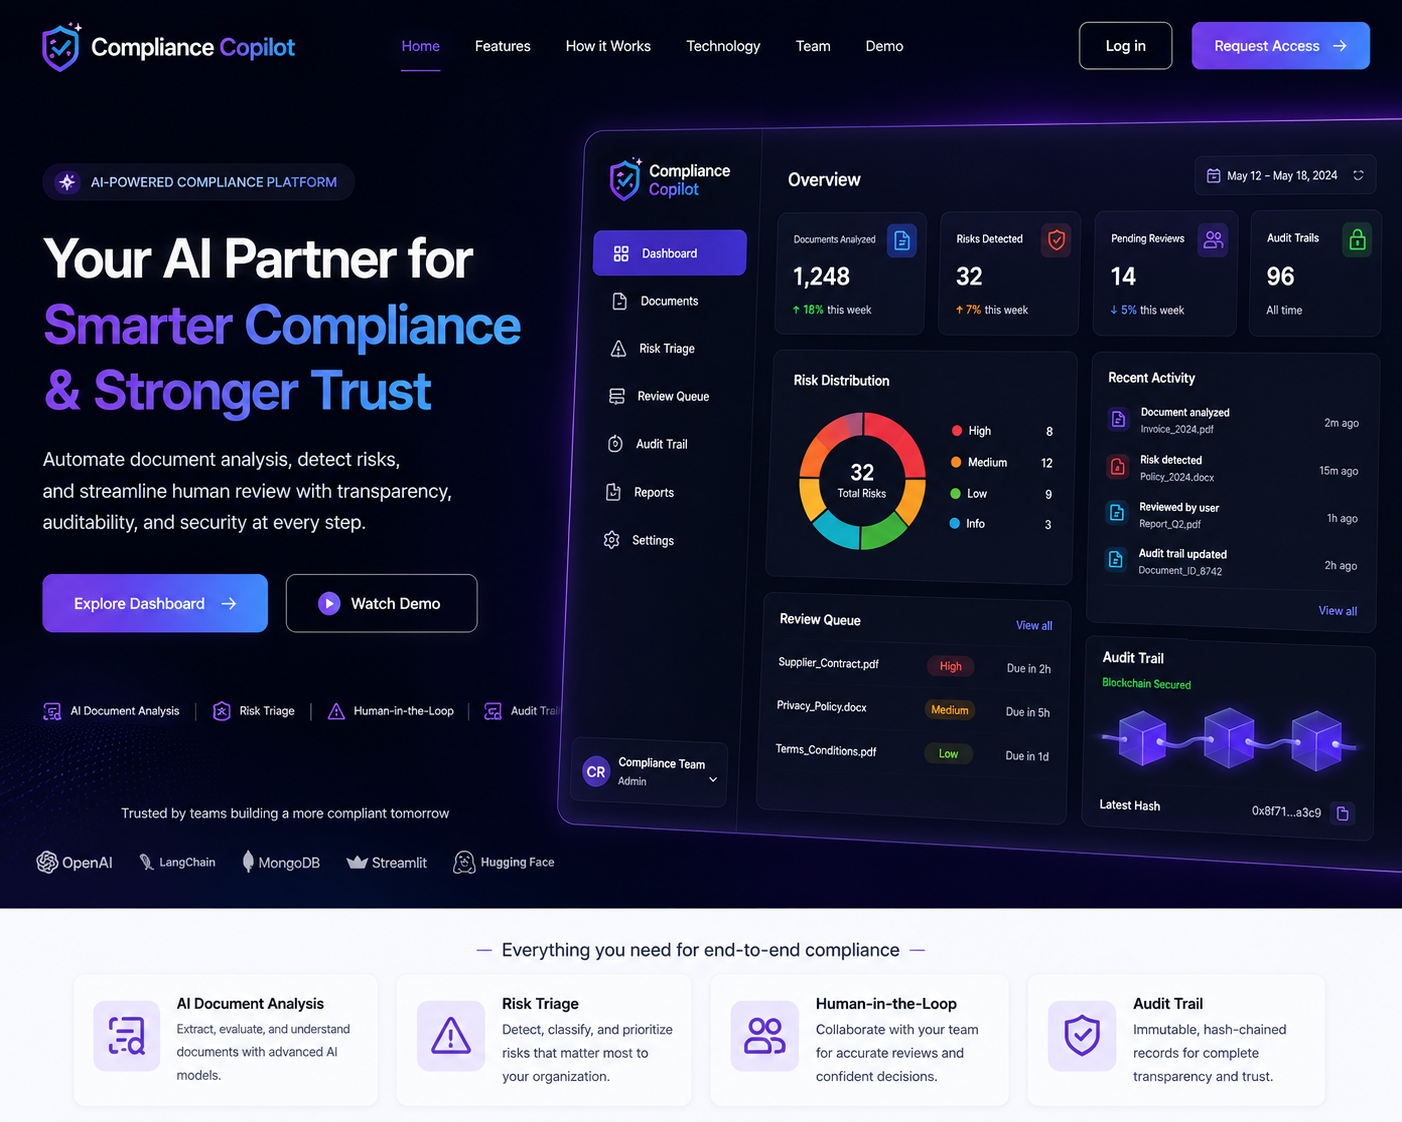
Compliance Copilot is an evidence-first document compliance workflow. Users upload an invoice, KYC/AML identity document, or contract. Nutrient OCR/PDF processing extracts structured fields and confidence scores. Deterministic policy checks identify missing required values. Anthropic-powered AI triage prioritises risk and routes uncertain cases to a human reviewer. Reviewers see source quality, confidence, failed rules, and release risk. Each decision is recorded in a hash-chained audit ledger. Doctavian handles the final compliant document generation and signing workflow.
How we built it
The application is built with Next.js and React, deployed on Vercel, and backed by Prisma and SQLite. It integrates Anthropic for triage, Nutrient for PDF/OCR processing, and Doctavian for document generation and signing. A transparent deterministic demo fallback keeps the walkthrough functional without paid AI credits and is clearly represented in the interface.
What we learned
Model confidence is not the same as compliance permission. High-confidence extraction still requires policy validation and human review when the consequence of an error is high. Audit evidence should be designed into the workflow from the beginning.
Challenges
We wanted a useful hackathon demo without making paid API credits a prerequisite. We therefore kept provider integrations optional, used deliberately planted demo defects, and made the review queue and audit evidence visible end to end.
Why it matters
Compliance Copilot helps teams move from “the model said so” to a reviewer-approved, evidence-backed, verifiable compliance record.
Built With
- next.js
- react
- vercel


Log in or sign up for Devpost to join the conversation.