-
-
-
-
-
-
-
codepulse homepage
-

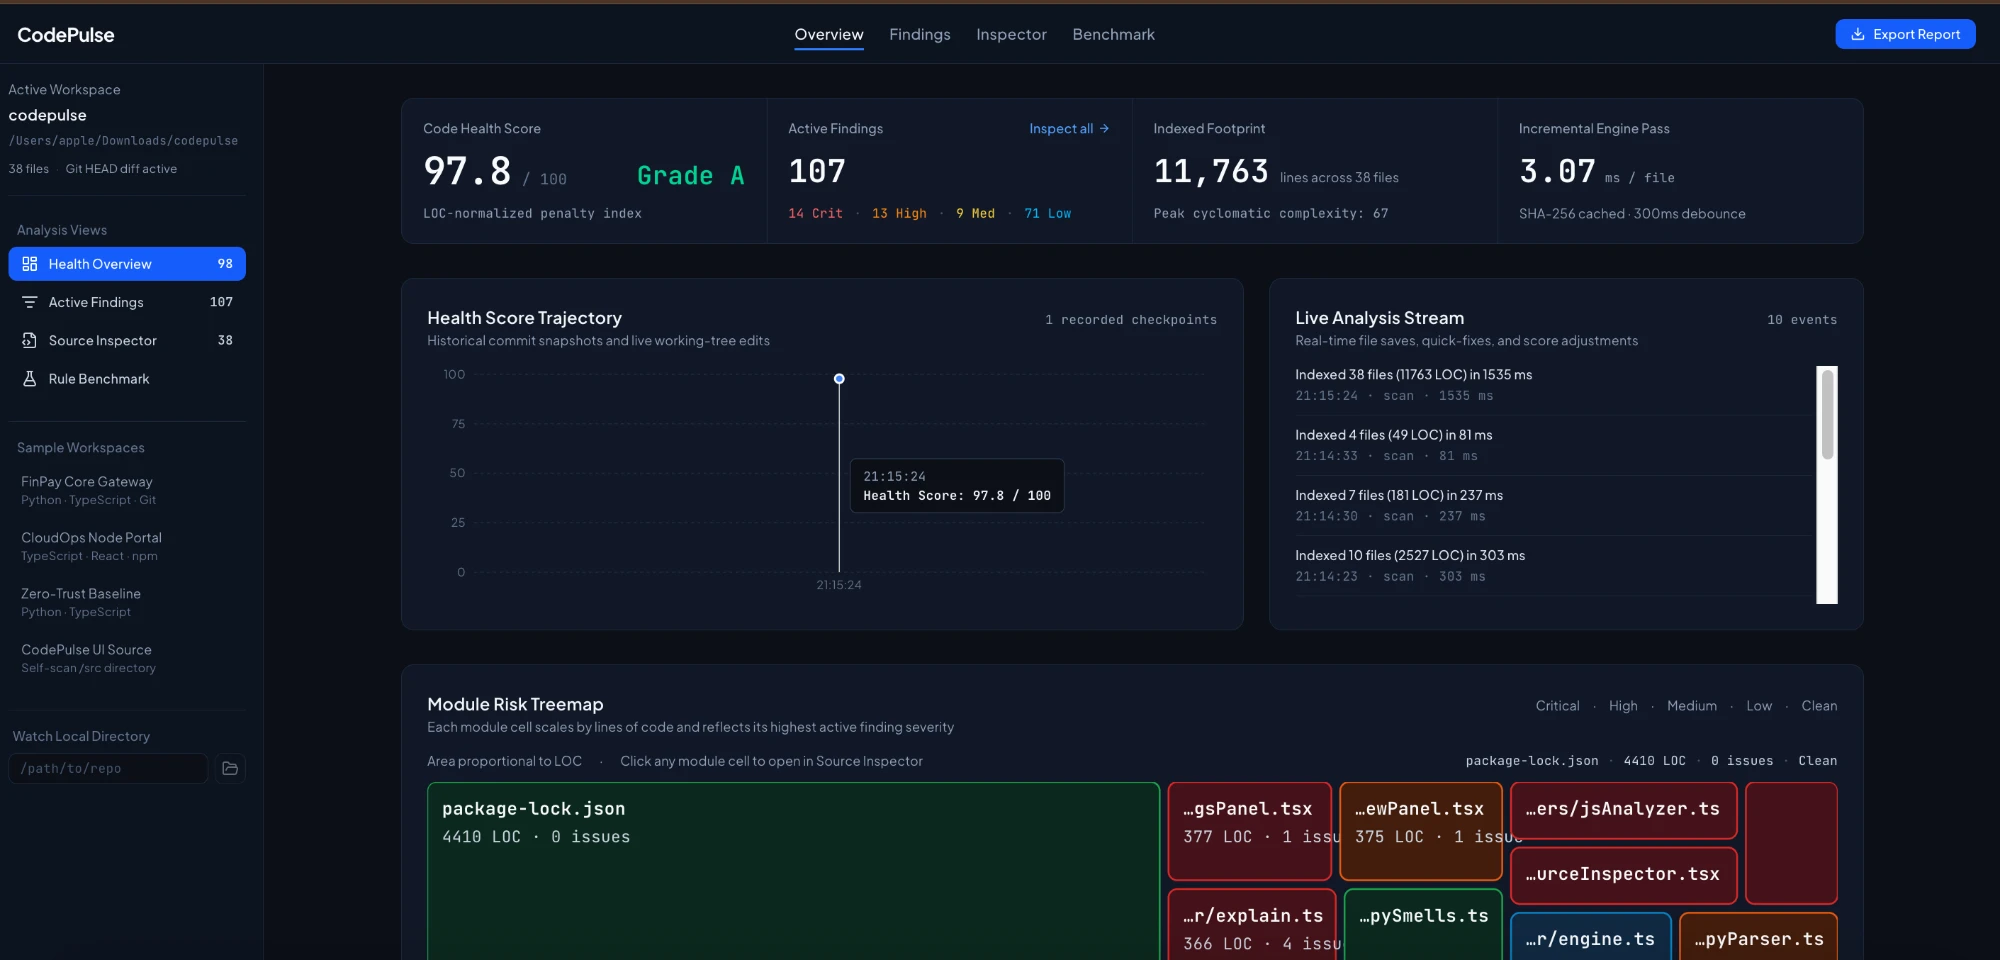
Inspiration### What is CodePulse?
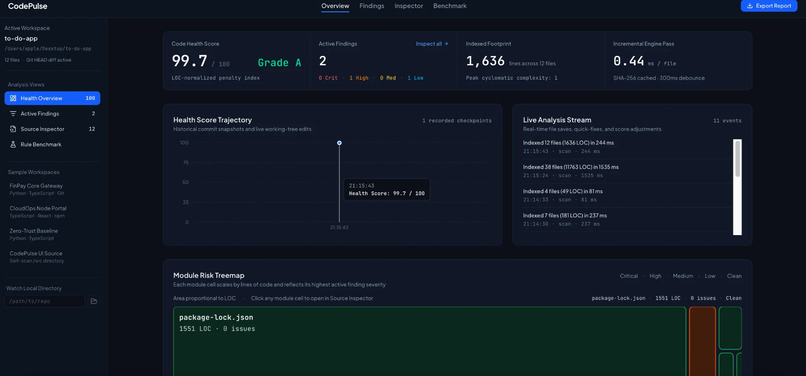
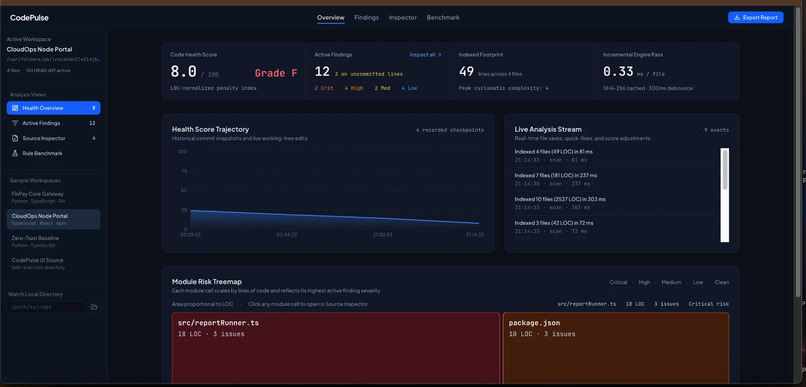
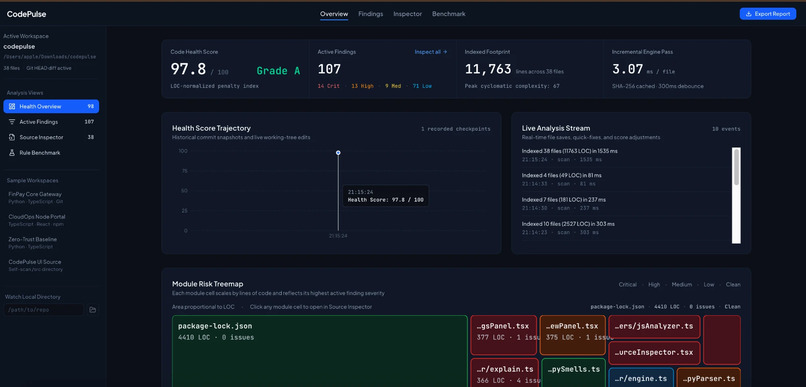
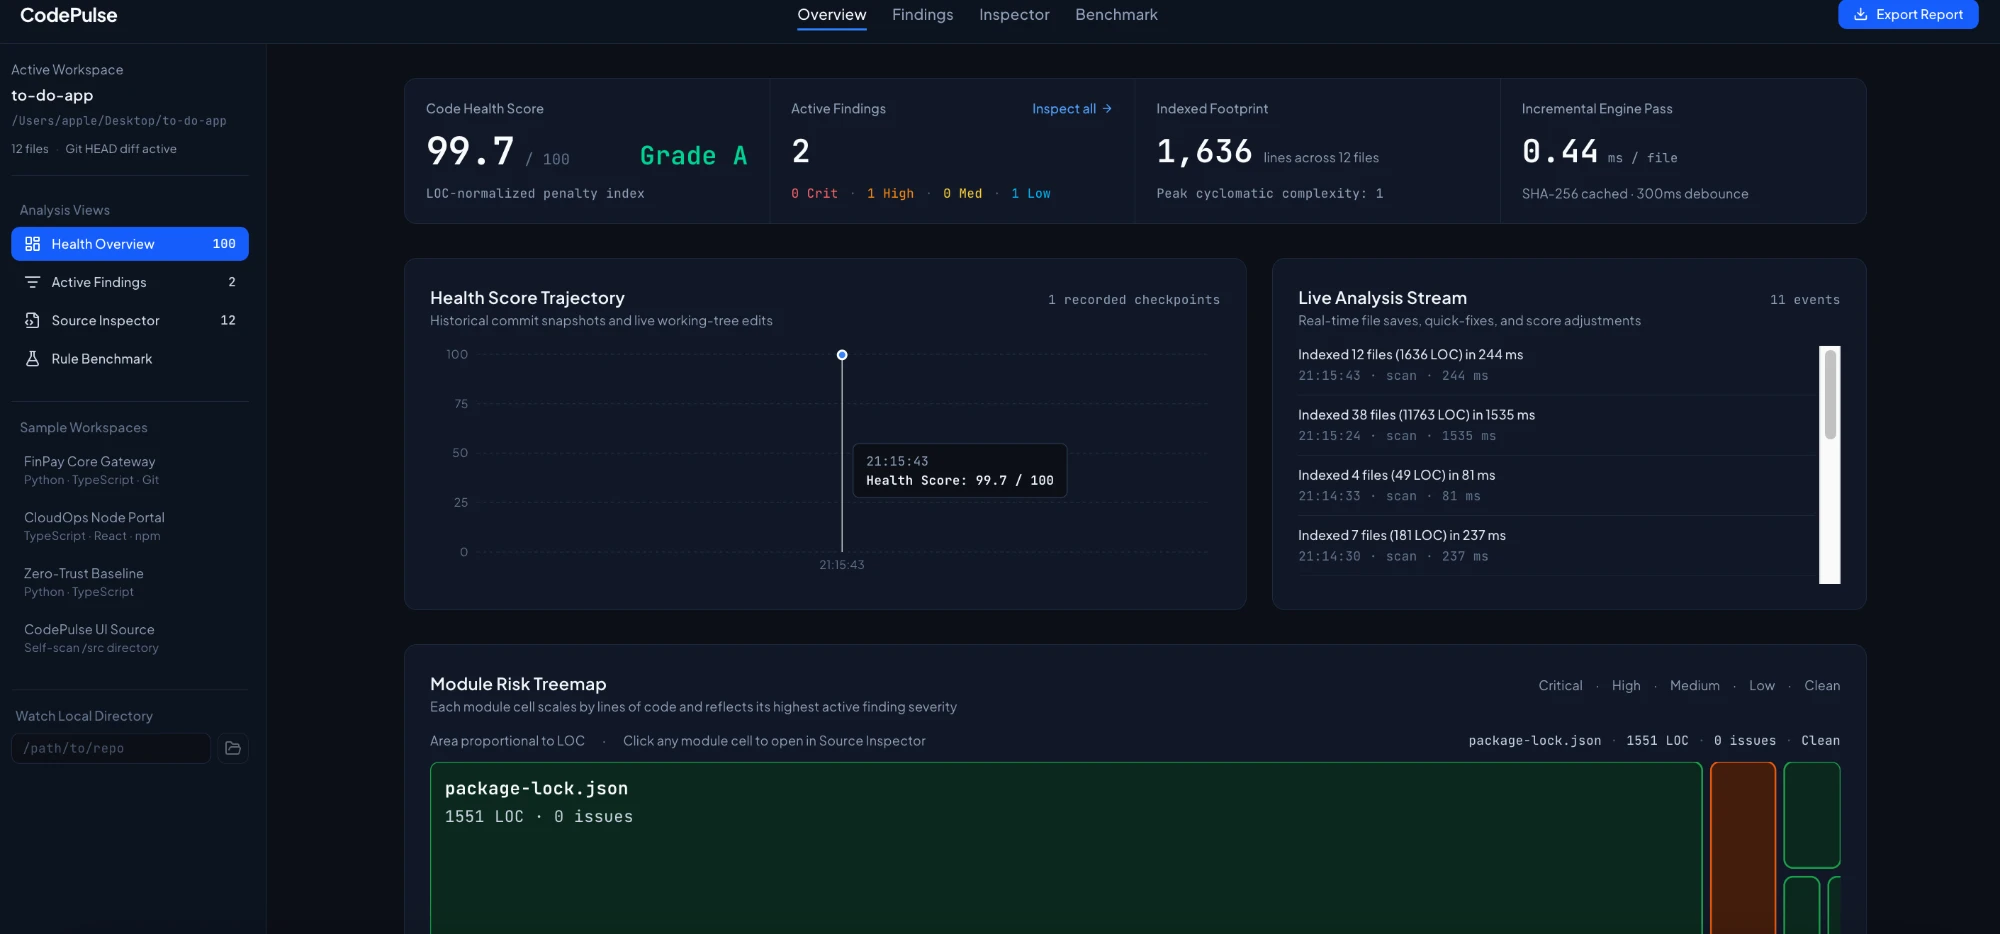
CodePulse is a real-time code quality monitoring platform that transforms static analysis from a slow, batch-oriented CI step into an instant, interactive development experience. It watches your codebase continuously, analyzes every file change in milliseconds, and provides immediate visual feedback on security vulnerabilities, code complexity, duplicate code, and technical debt.
Core Innovation
Traditional Approach:
Write code → Commit → Push → Wait for CI → Get feedback 10 minutes later → Context switch cost
CodePulse Approach:
Write code → Auto-save → Instant analysis (<50ms) → Live dashboard updates → Fix immediately
Key Differentiators
| Feature | CodePulse | Traditional Tools |
|---|---|---|
| Feedback Speed. | <50ms (real-time) | 5-30 minutes (CI). |
| Privacy | 100% local, zero telemetry | Often cloud-based. |
| Visualization | Live dashboard with health score | Text reports. |
| Git Integration | Highlights uncommitted changes | Post-commit only. |
| State Persistence. | Dismissals survive refactors. | Lost on file changes |
| Developer Experience | Interactive, visual, continuous. | Batch, text-based, delayed |
Target Users
- Individual Developers: Want instant feedback without CI setup
- Security-Conscious Teams: Need local-only analysis (compliance, proprietary code)
- Tech Leads: Monitor team code quality trends in real-time
- Code Reviewers: Visual quality metrics before reviewing PRs
Problem Statement
The Code Quality Feedback Gap
Modern development suffers from a temporal disconnect between writing code and discovering quality issues:
Problem 1: Slow Feedback Loops
- CI/CD takes 10-30 minutes: Developer has moved to next task
- Context switching cost: Need to reload mental model to fix issues
- Productivity loss: 23 minutes average to regain focus after interruption
Problem 2: Privacy & Security Concerns
- Cloud-based tools: Source code uploaded to third-party servers
- Compliance issues: HIPAA, SOC 2, GDPR restrictions on data movement
- Trade secrets: Proprietary algorithms exposed to SaaS providers
Problem 3: Poor Developer Experience
- Text-only output: Thousands of lines of logs to parse
- No visualization: Hard to prioritize which issues matter
- State loss: Dismissing false positives doesn't persist across runs
Problem 4: Incomplete Coverage
- Post-commit only: Issues found after code is already committed
- No incremental analysis: Full repo scan every time
- Expensive compute: CI minutes cost money and burn energy
Real-World Impact
Scenario: Security Vulnerability Introduction
Without CodePulse:
- Developer copies code snippet with hardcoded AWS key (Monday 2pm)
- Commits and pushes to feature branch
- CI runs 15 minutes later, flags secret
- Developer is now debugging different issue
- Context switch to fix security issue
- New commit, another CI run
- Total time to fix: 45 minutes + 2 CI runs
With CodePulse:
- Developer pastes code with AWS key (Monday 2pm)
- Auto-save triggers analysis (50ms later)
- Red critical badge appears instantly on line
- Developer sees issue before even committing
- Replaces with environment variable immediately
- Total time to fix: 30 seconds, zero CI runs
Built With
- express.js
- genai
- motion
- node.js
- python
- react
- sqlite
- typescript
- vite
- websockets

Log in or sign up for Devpost to join the conversation.