-
-
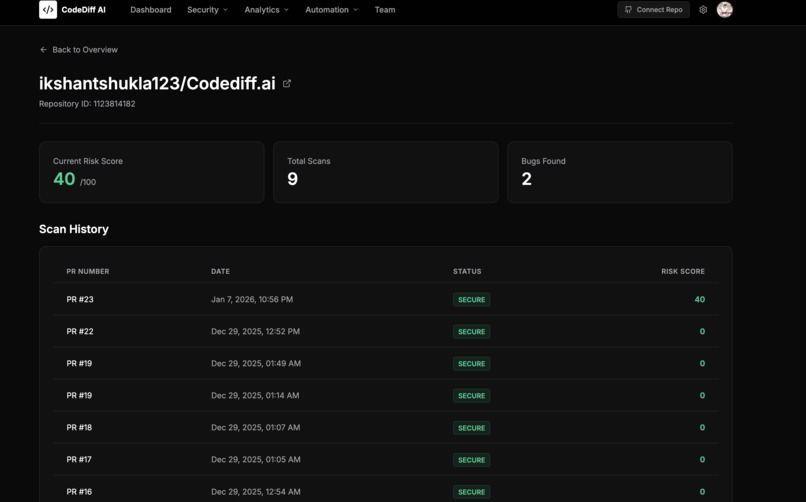
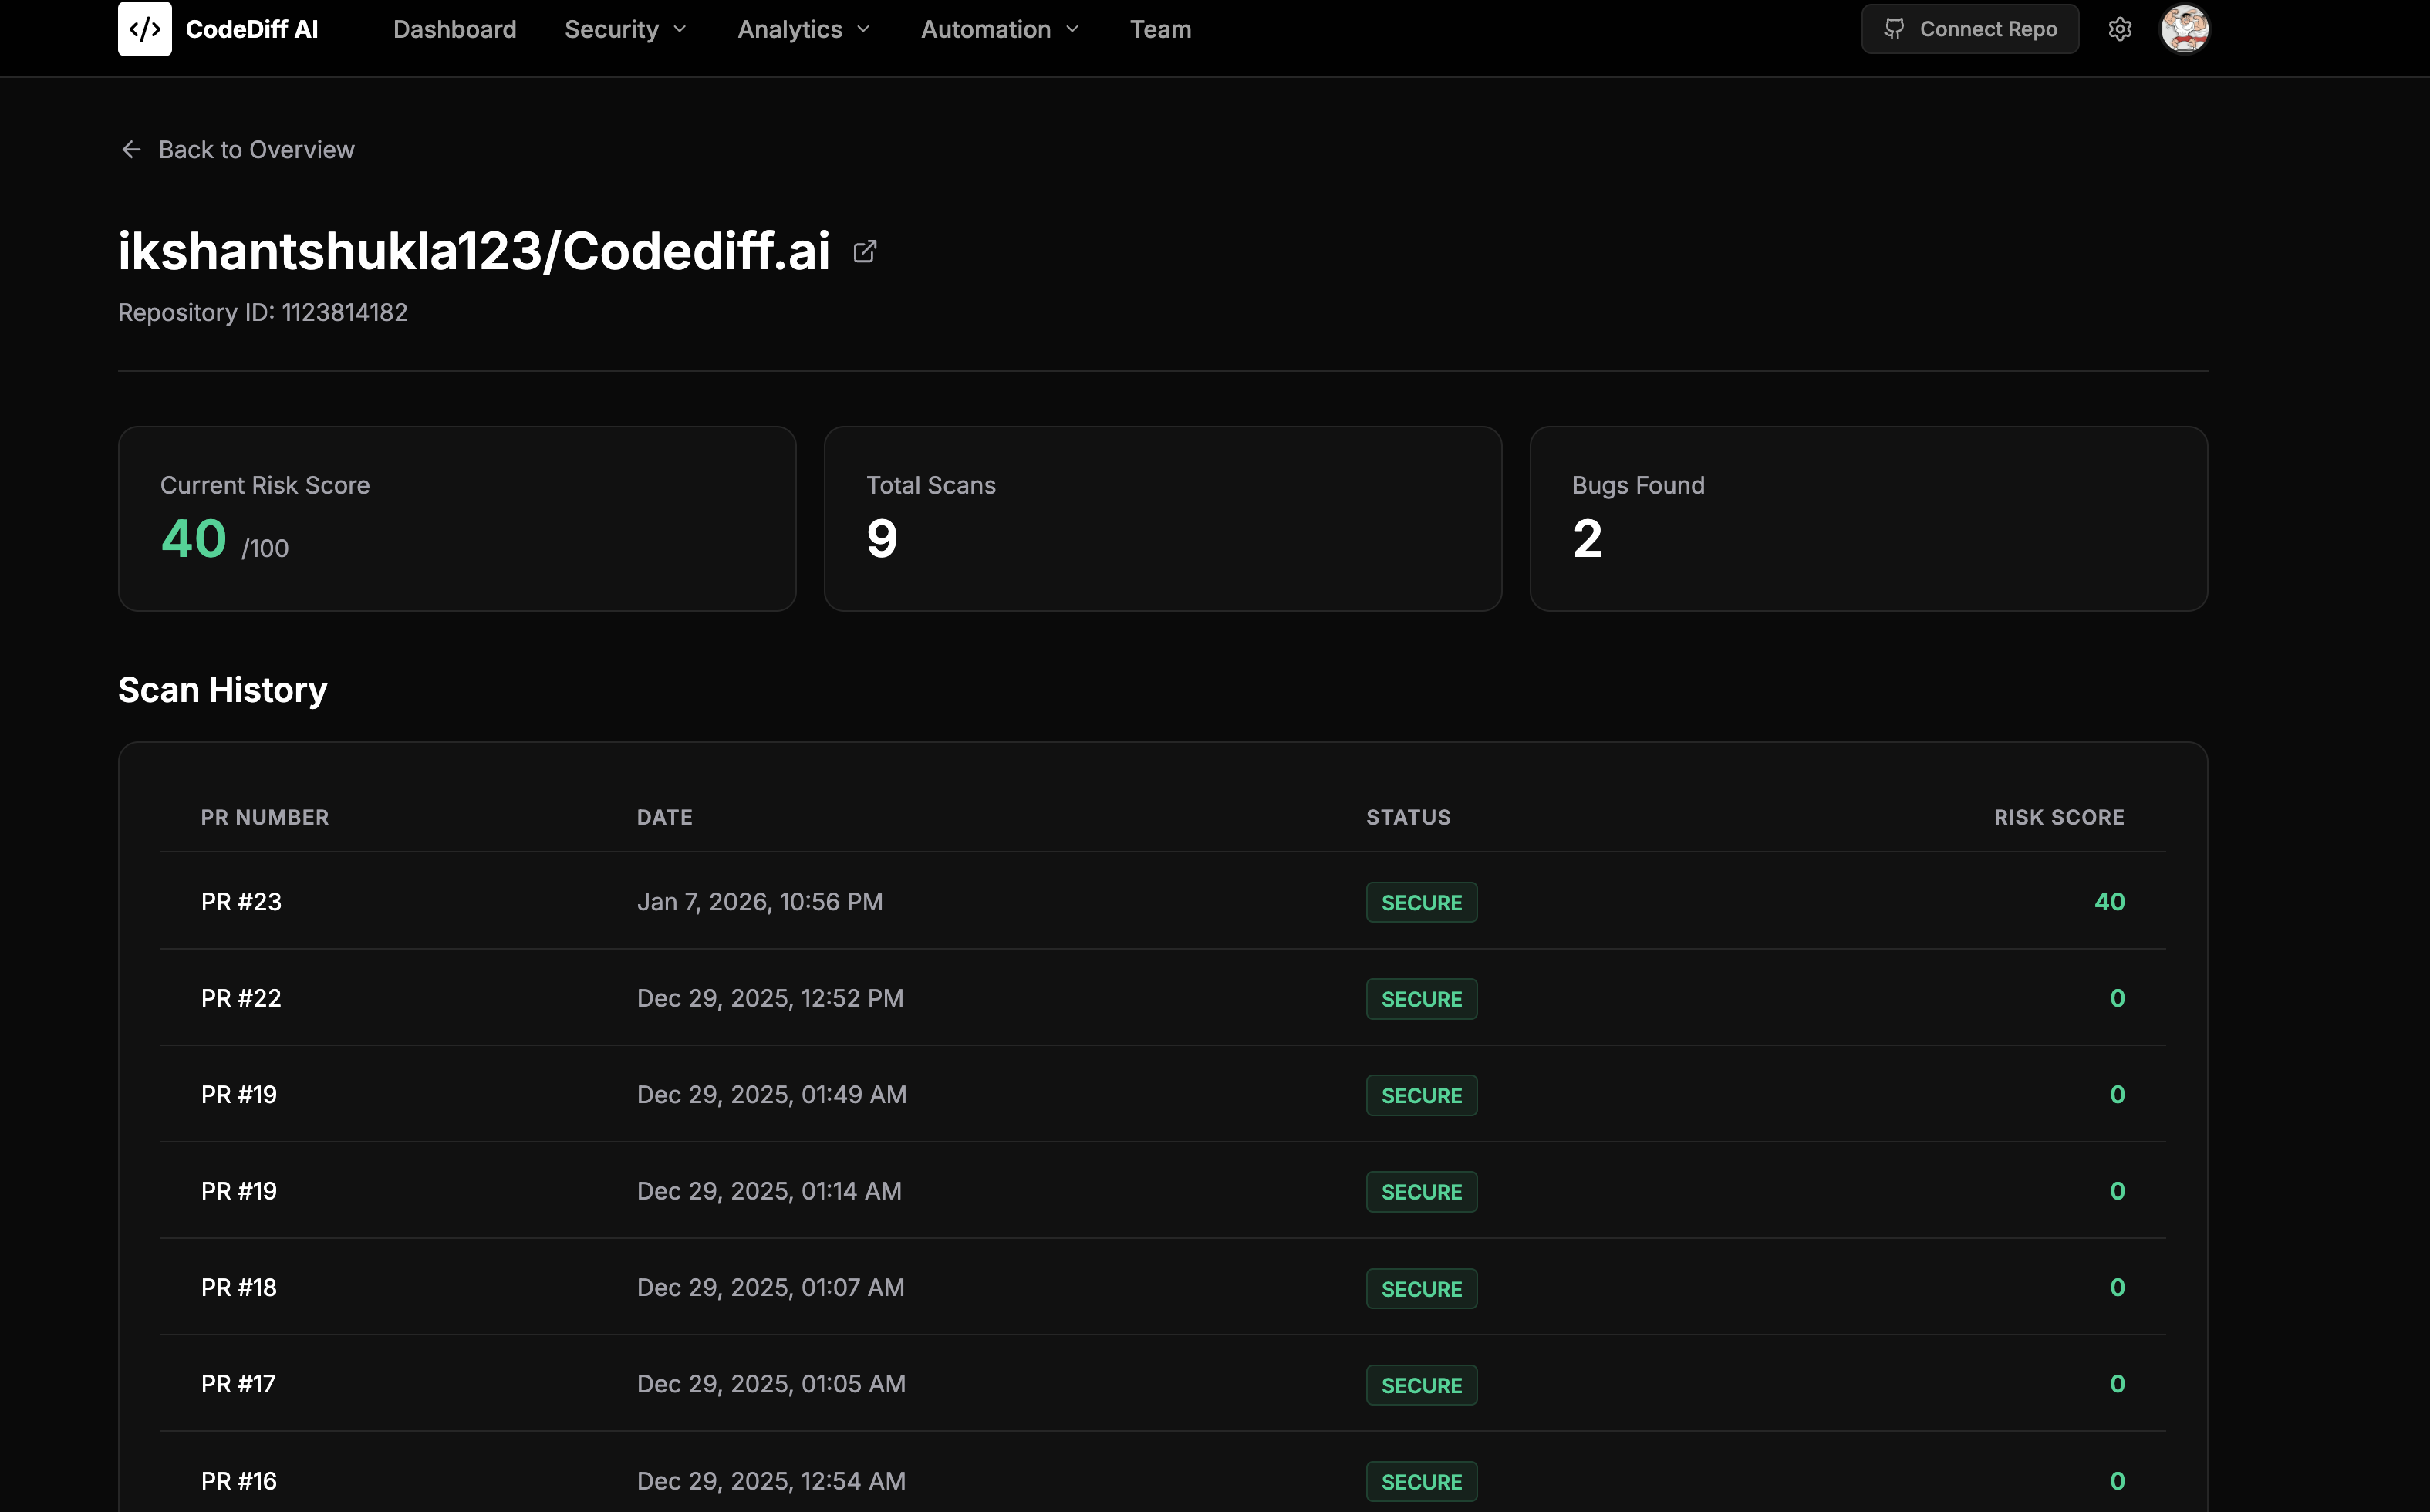
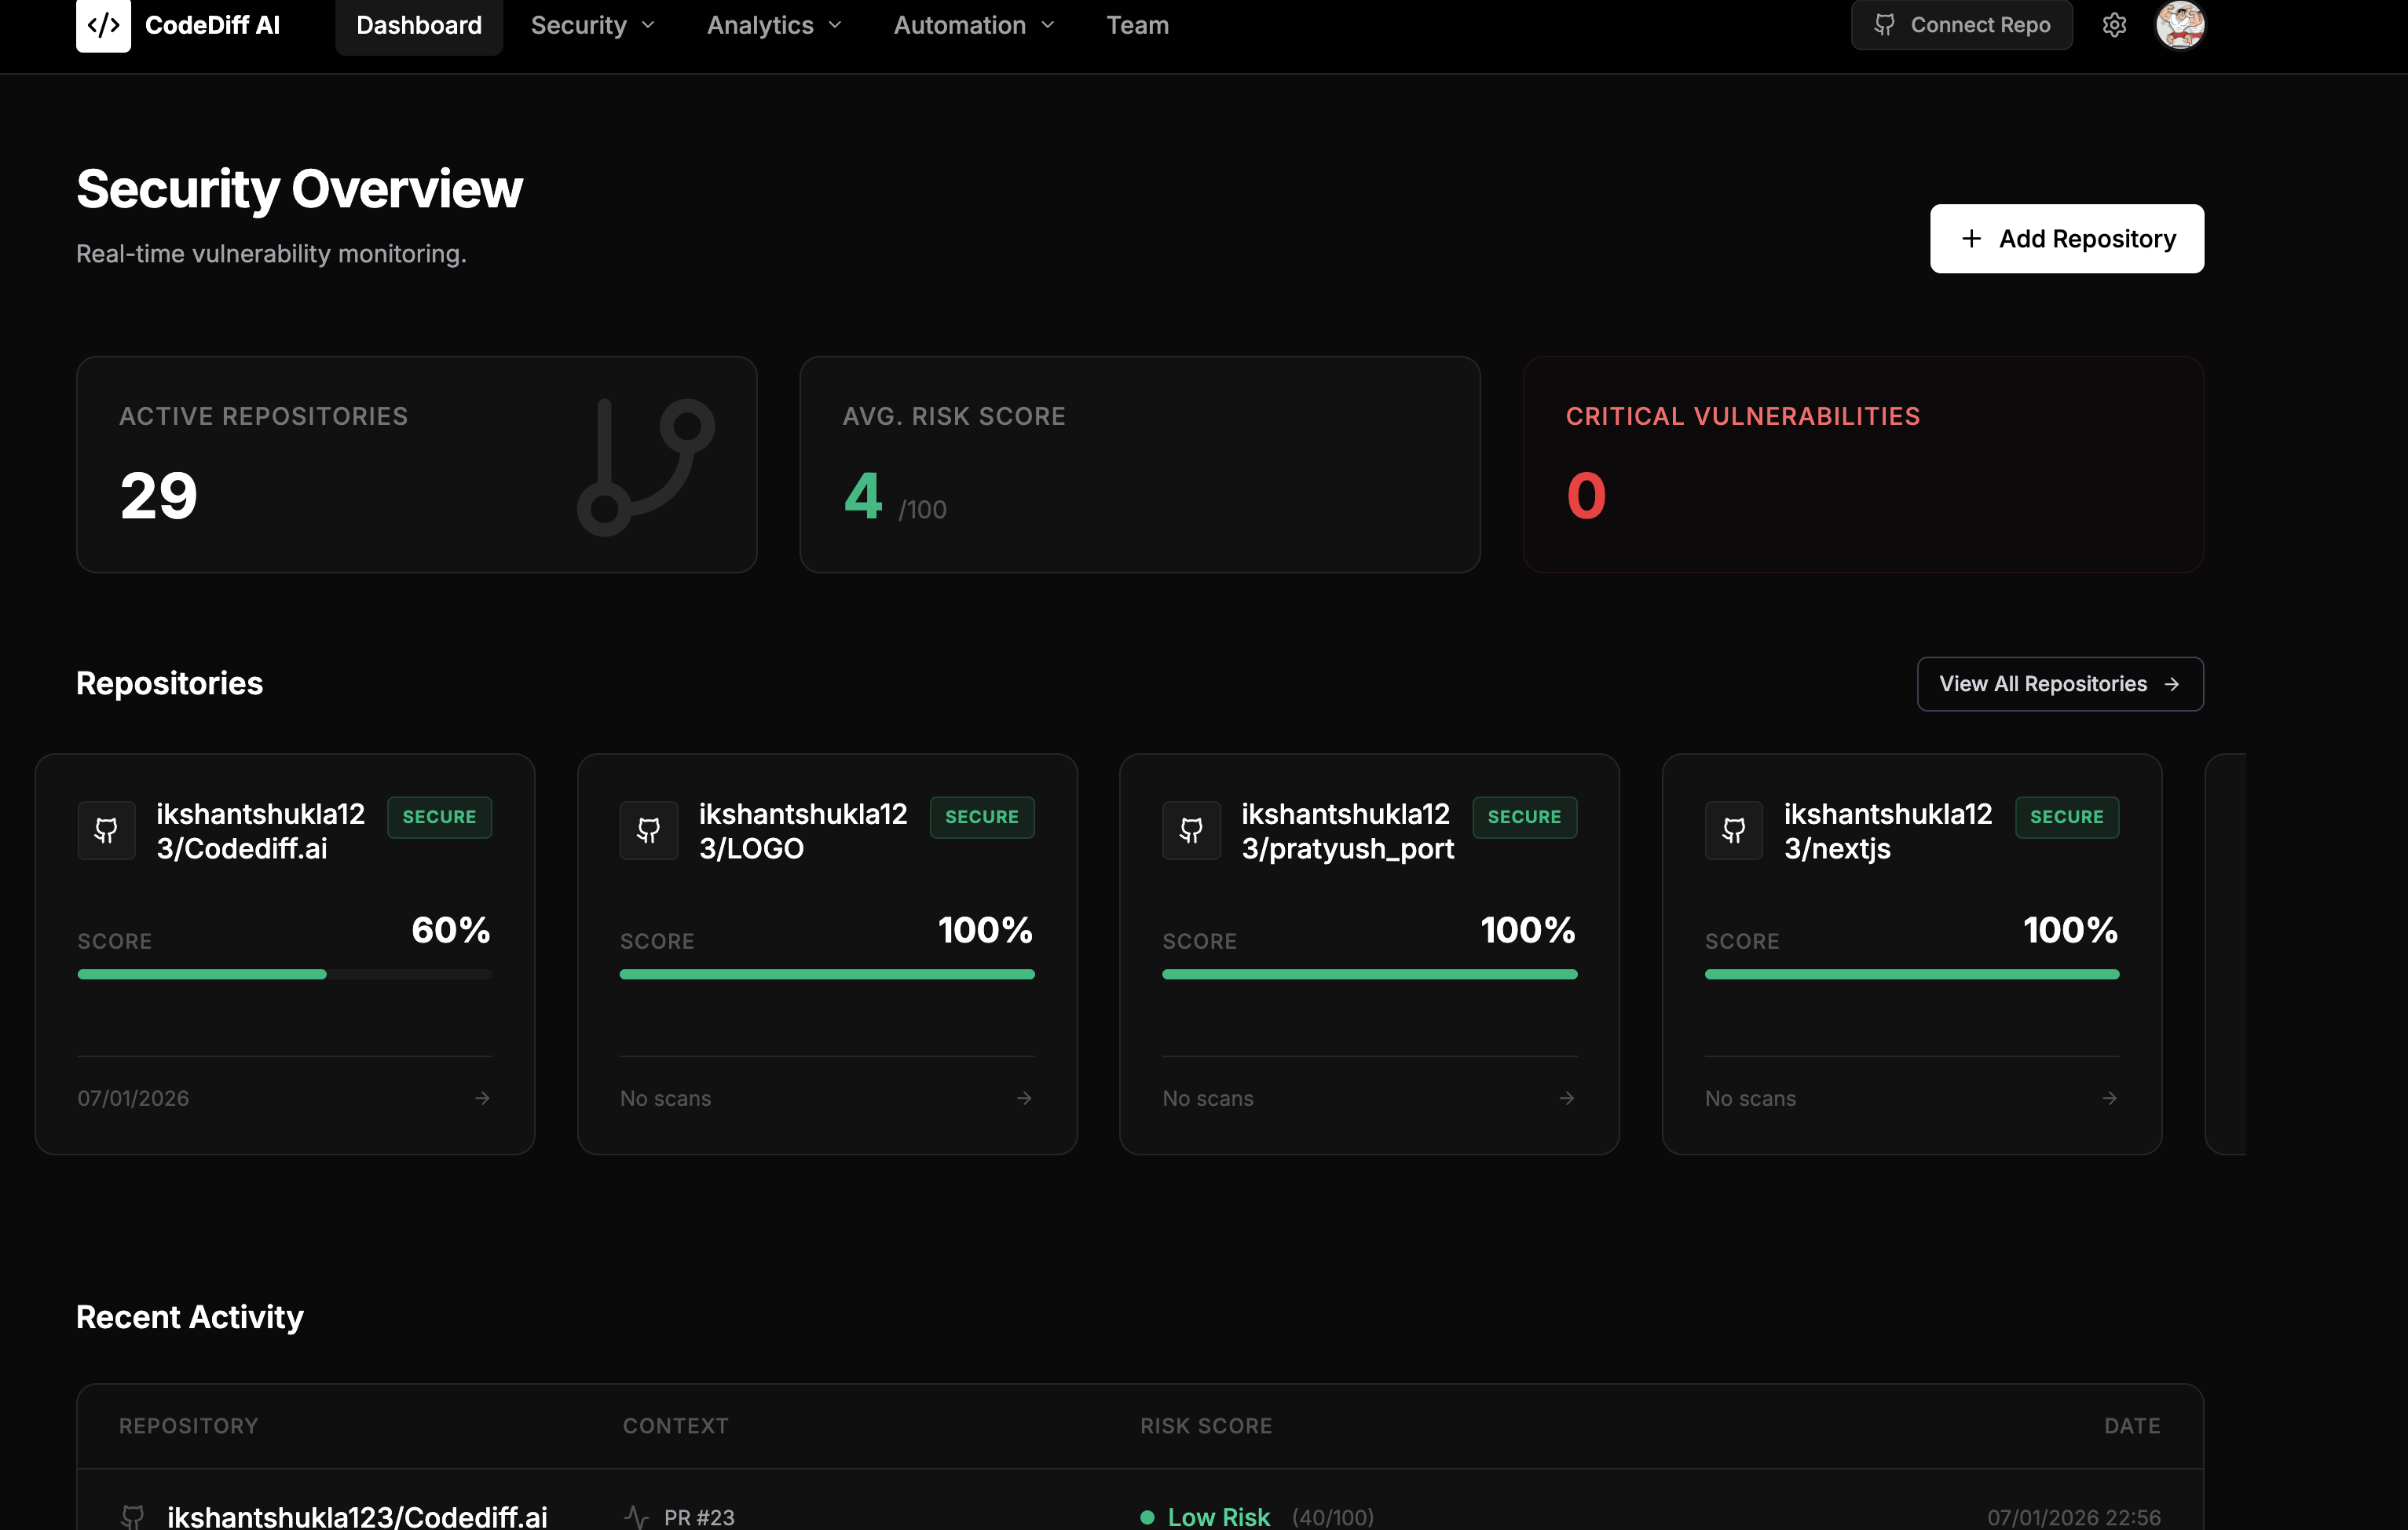
Recent activity
-
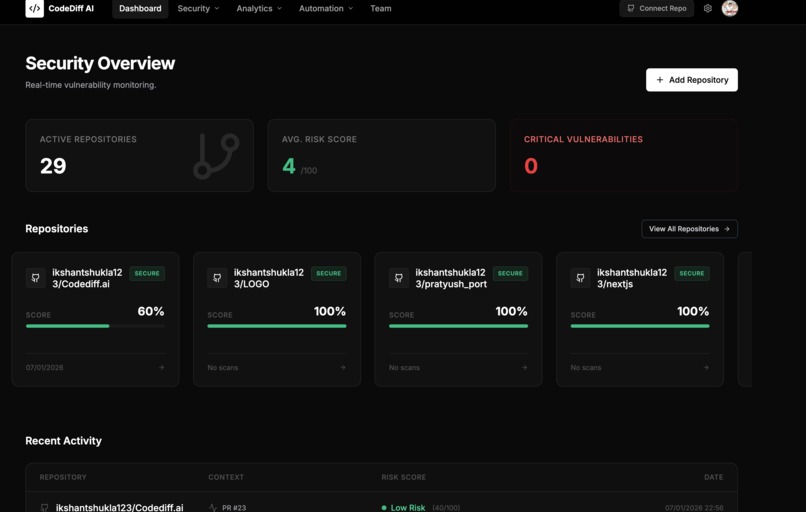
Dashboard
-
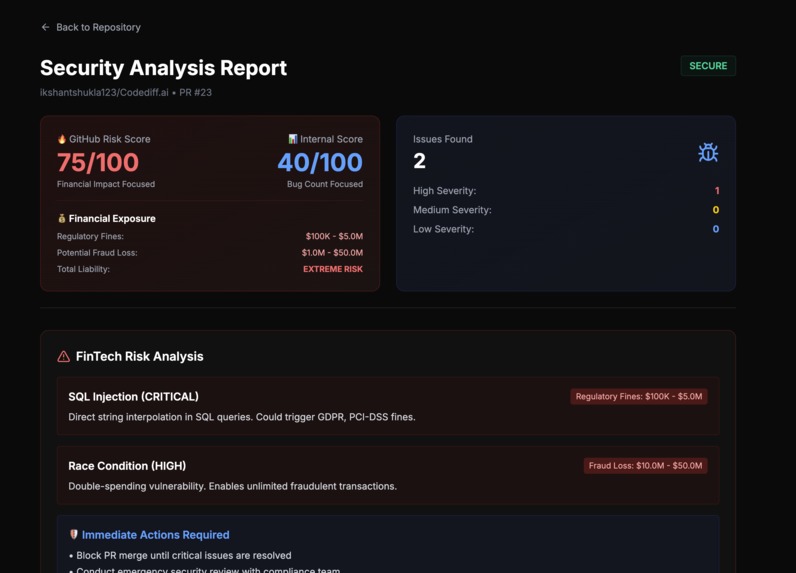
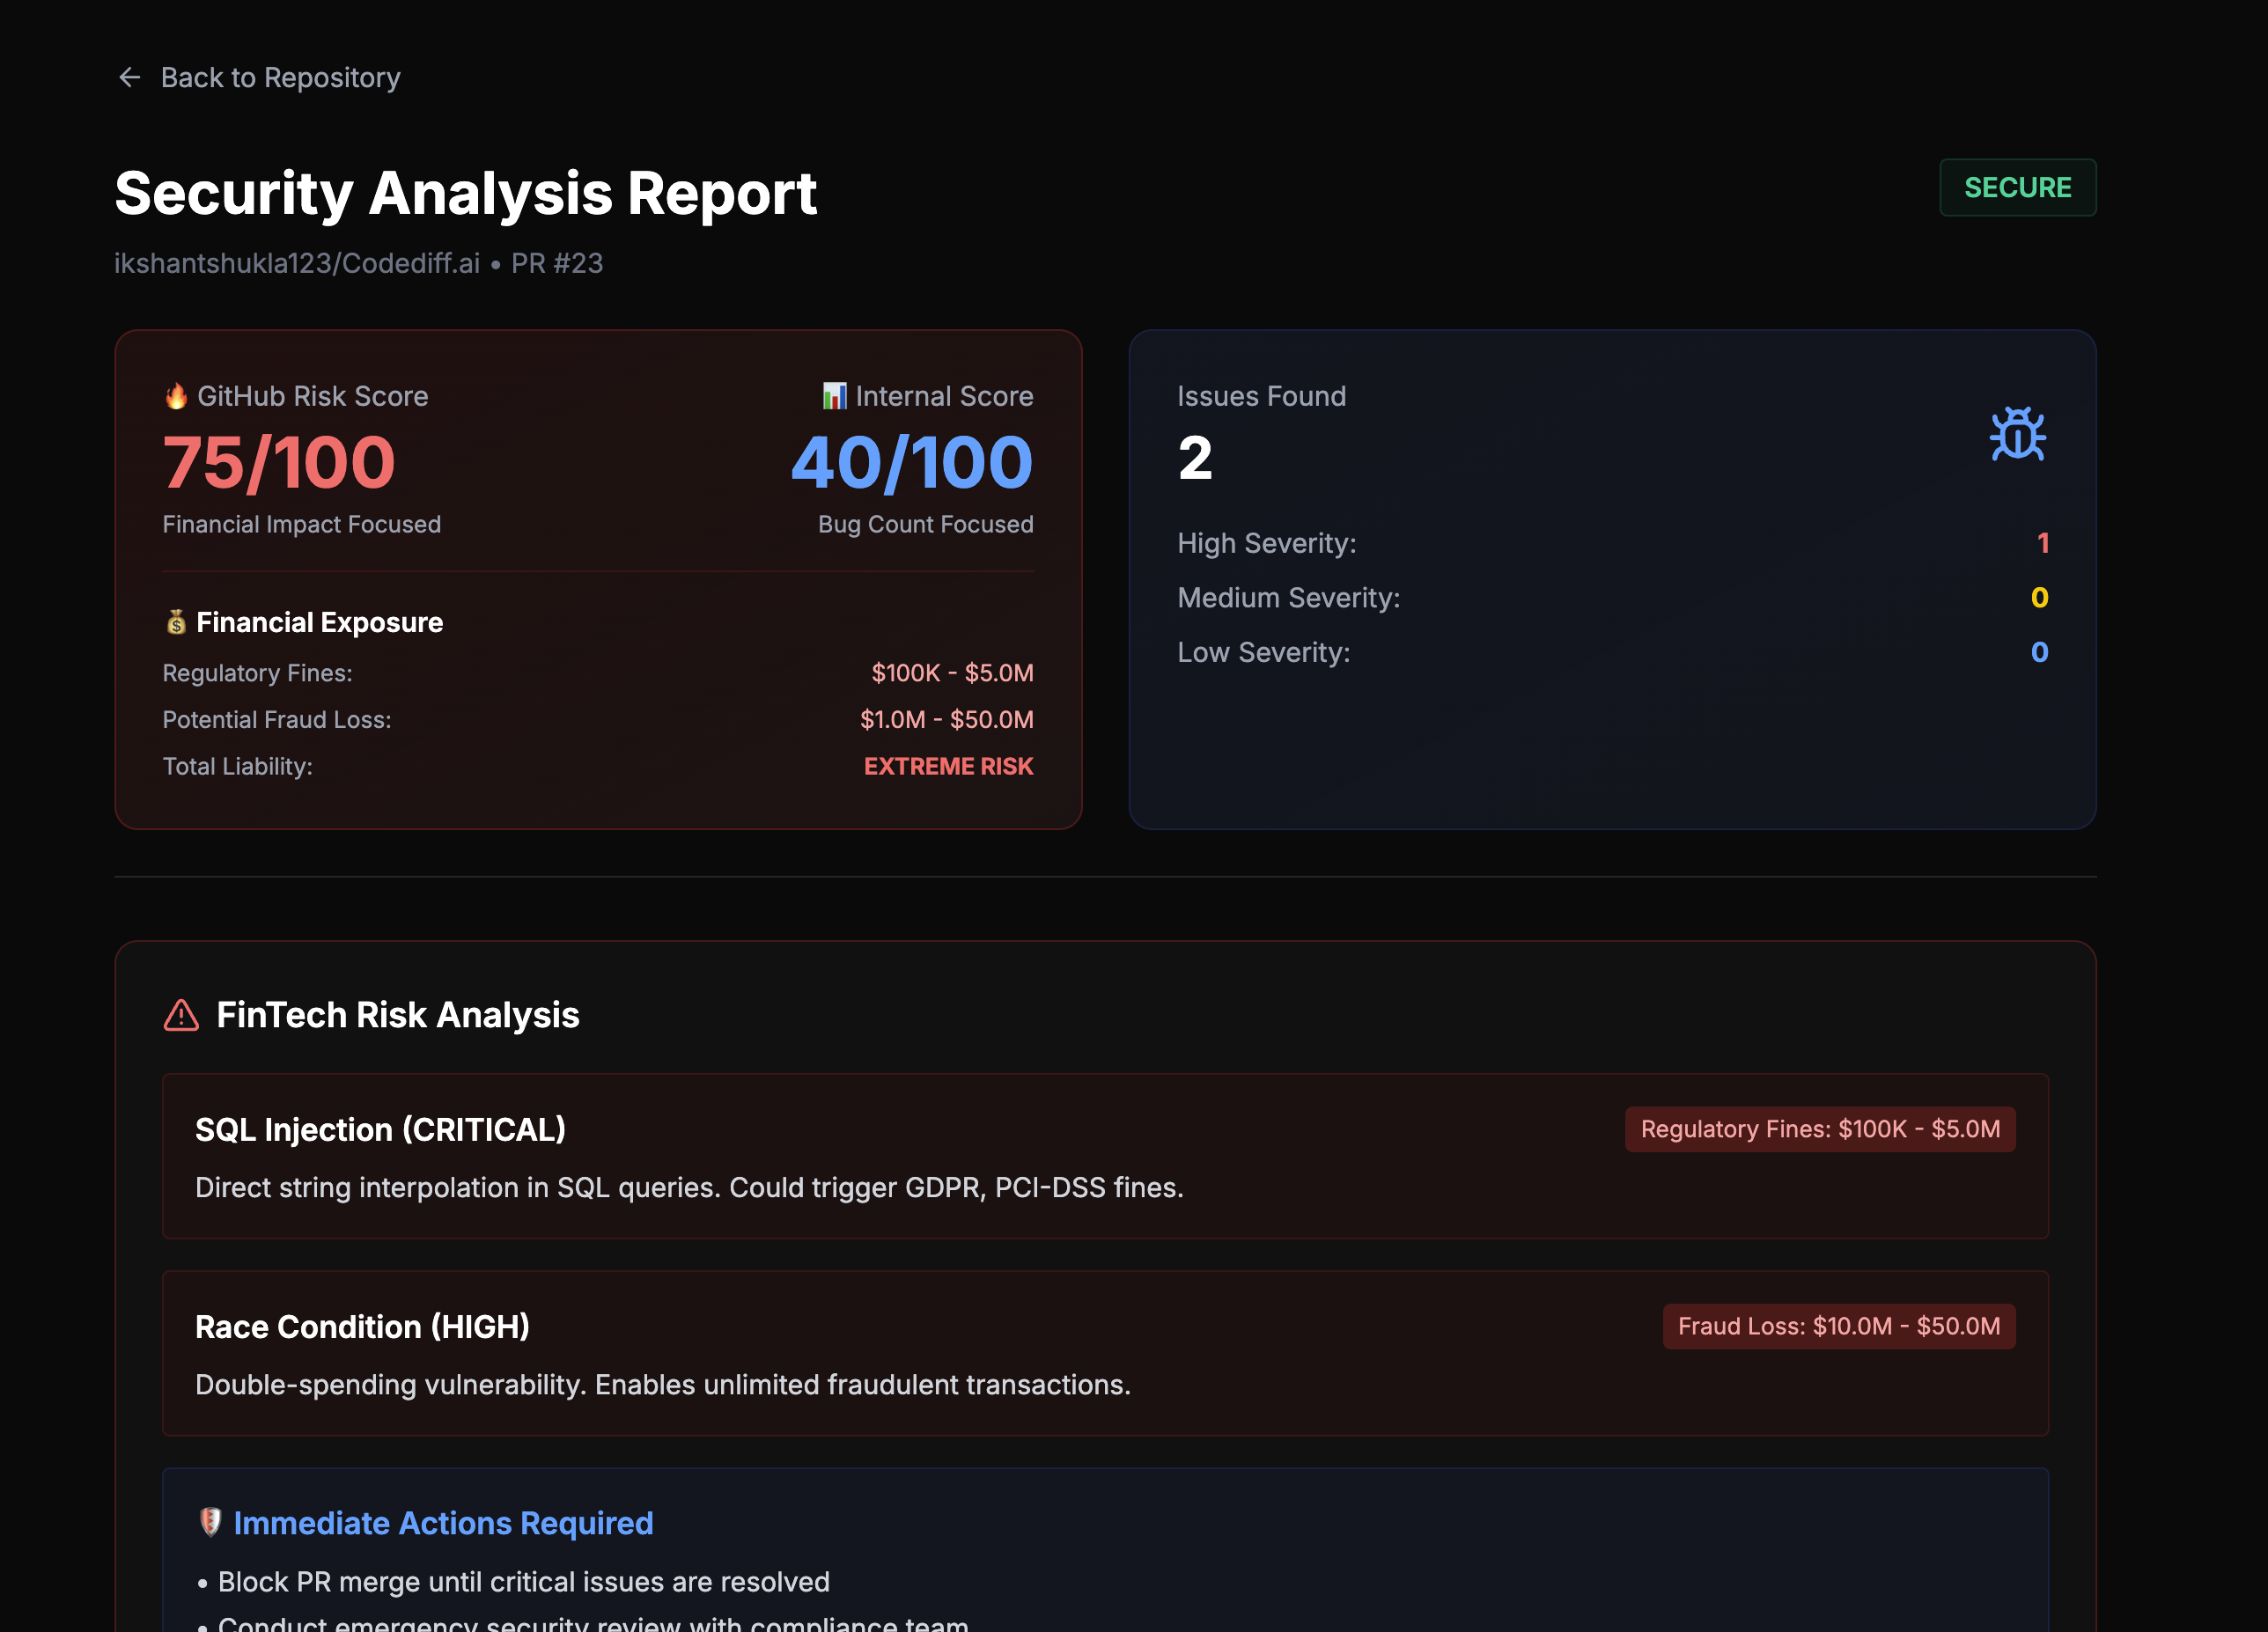
Scan result
-
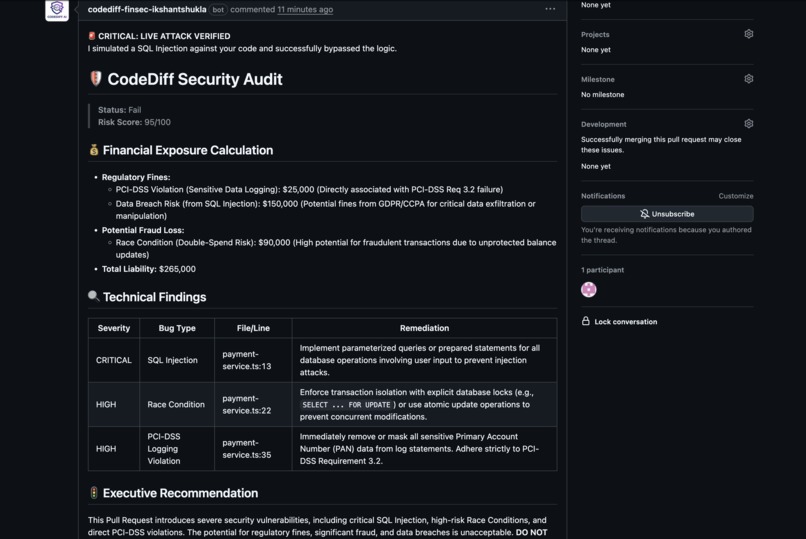
AI summary
-
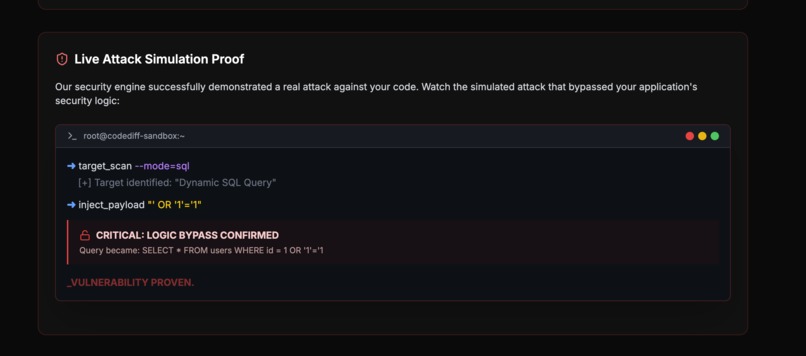
Live attack simulater
Inspiration
The Problem: Computer science education is missing real-world context. Students learn to write code but not the financial consequences of that code.
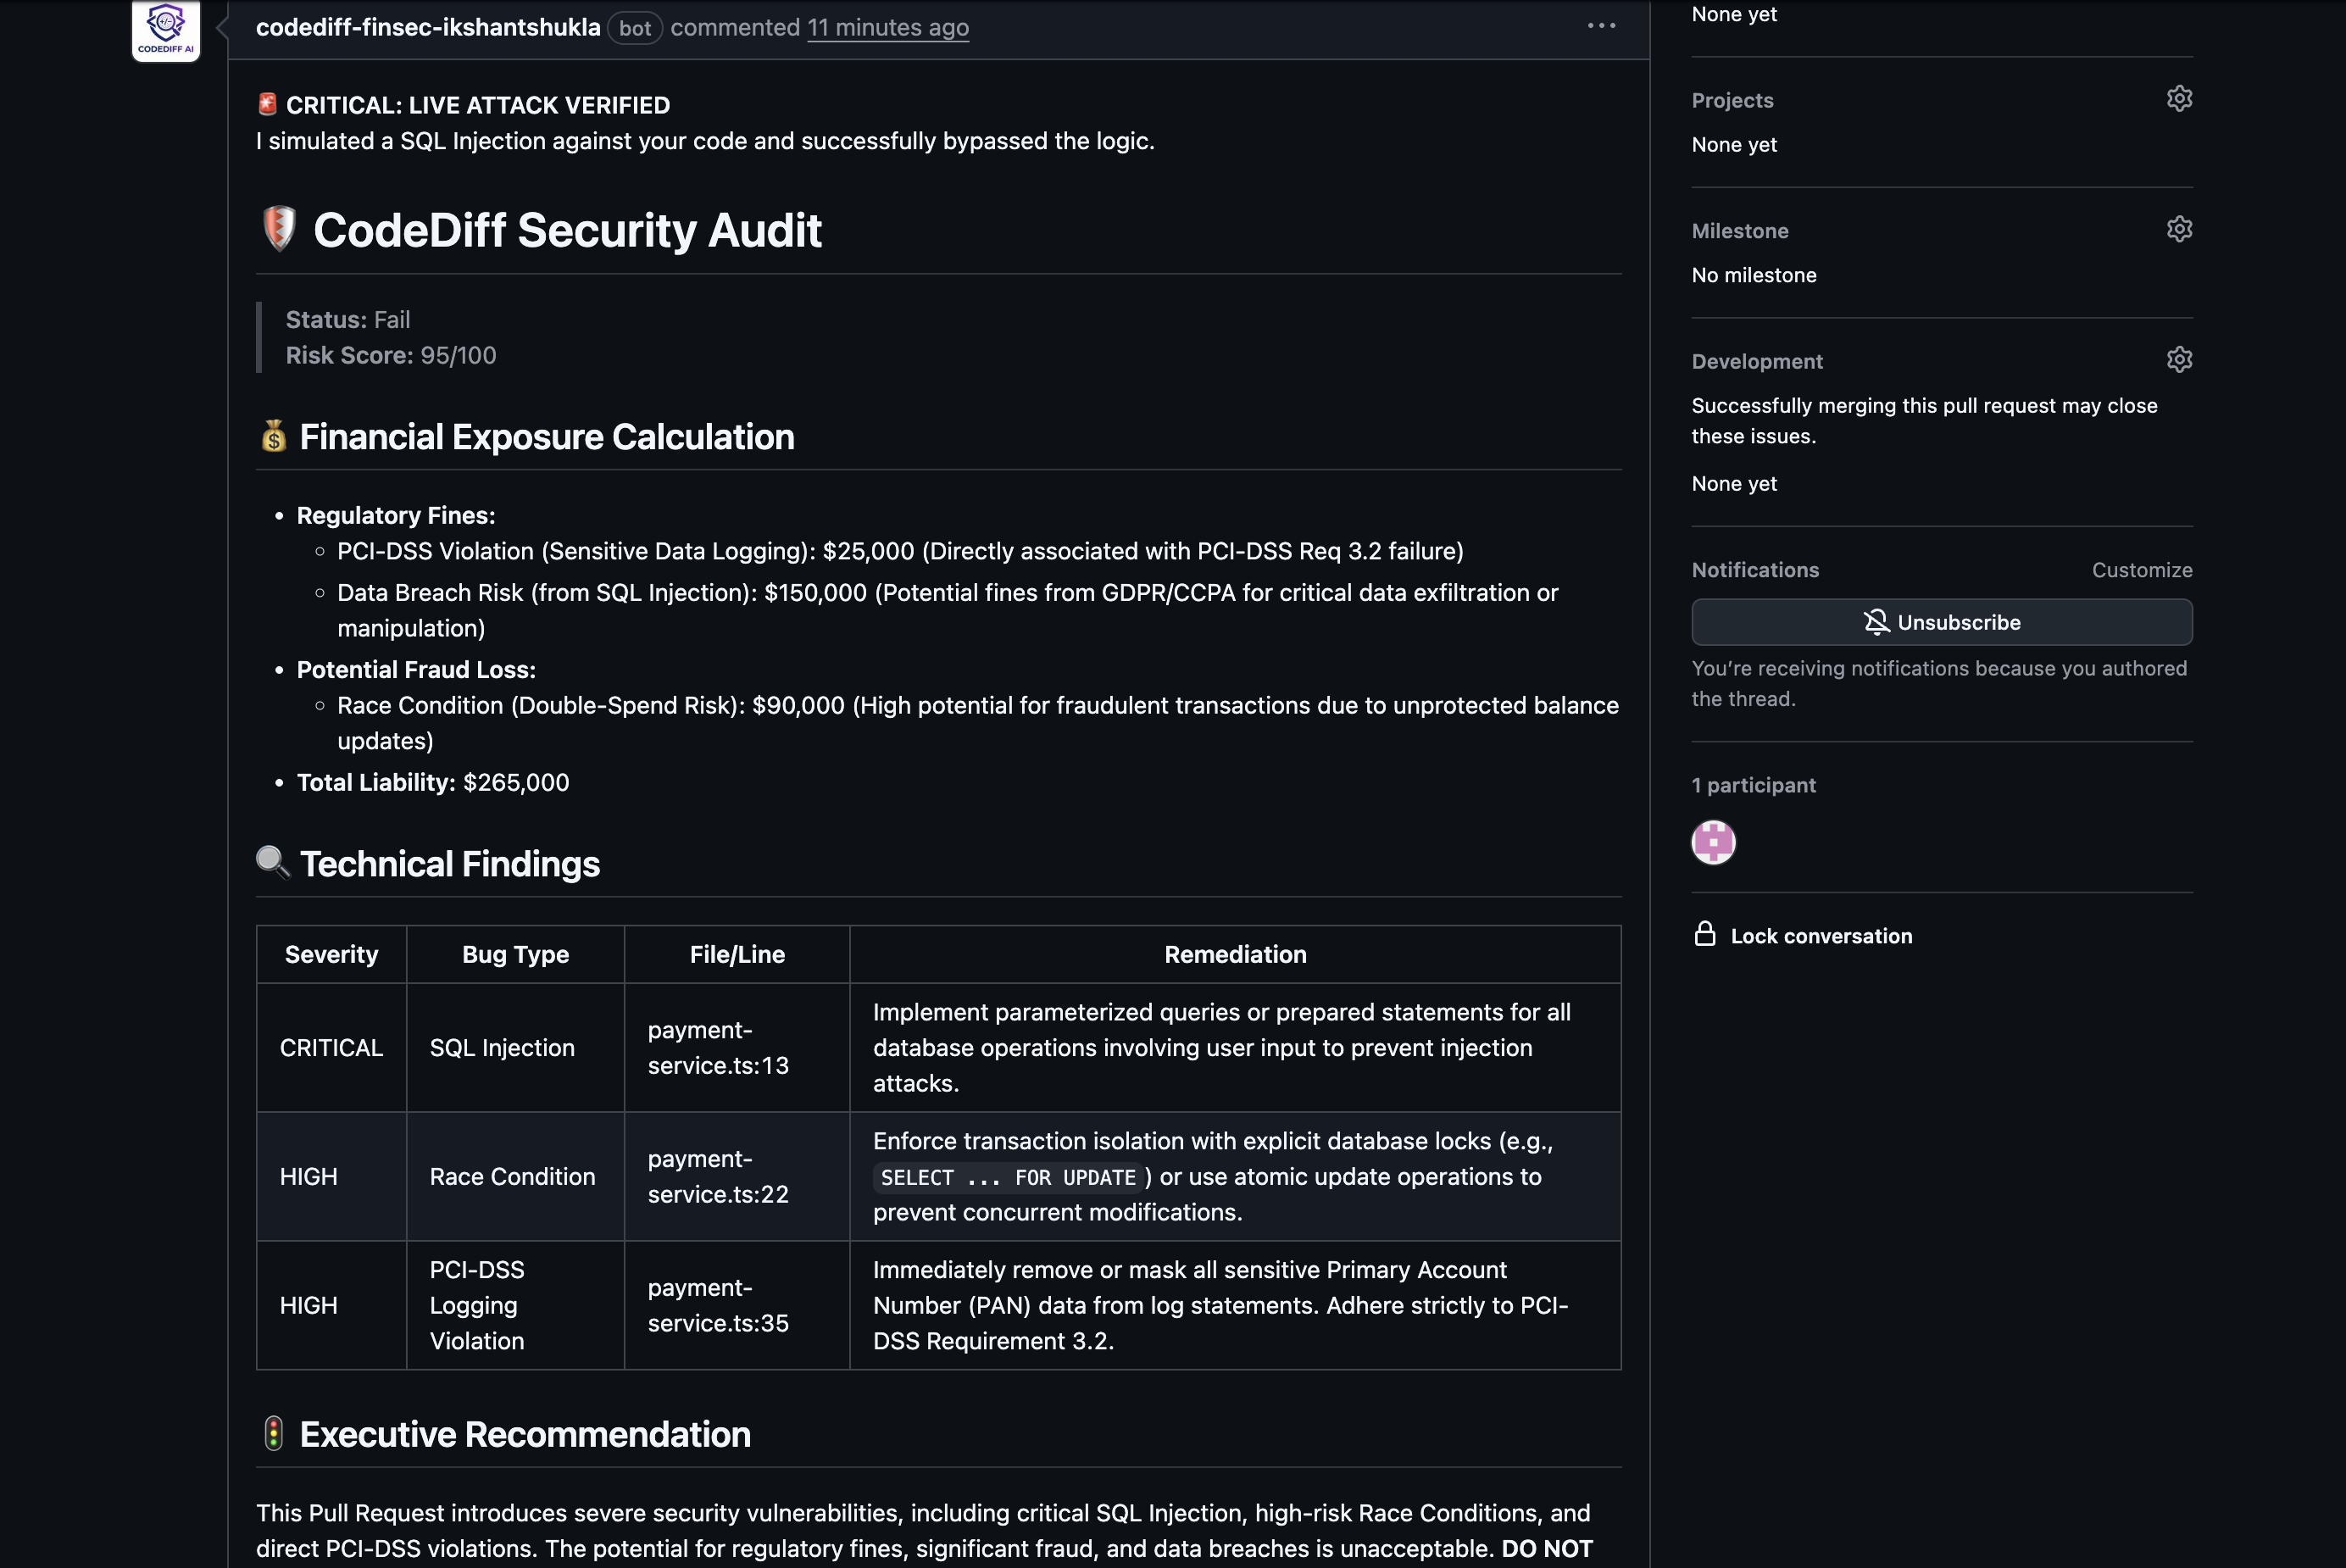
We realized there's a security skills gap because graduates enter FinTech unprepared. They know what a SQL injection is, but not that it's a $65,000 regulatory fine in payment systems.
Our Question: What if every coding assignment could teach students not just how to code, but why secure code matters to their future careers and company survival?
We built CodeDiff AI to bridge this gap - transforming GitHub into an interactive classroom where students learn that bad code isn't just incorrect, it's expensive, illegal, and career-limiting.
What it does
CodeDiff AI is an Economic Security Engine that audits financial code using a hybrid approach of Generative AI and Deterministic Math. It doesn't just find bugs.it proves them and calculates their cost. which help students to know what a bug can cause? Council of AI Analysis: It routes code through a multi-model architecture (Gemini 1.5 & DeepSeek) to understand intent and complex logic flaws (e.g., race conditions, double-spending).
Deterministic "Truth" Layer: It applies rigid mathematical standards to sensitive data. For example, we use the Luhn Algorithm to mathematically verify potential credit card leaks with 0% false positives.
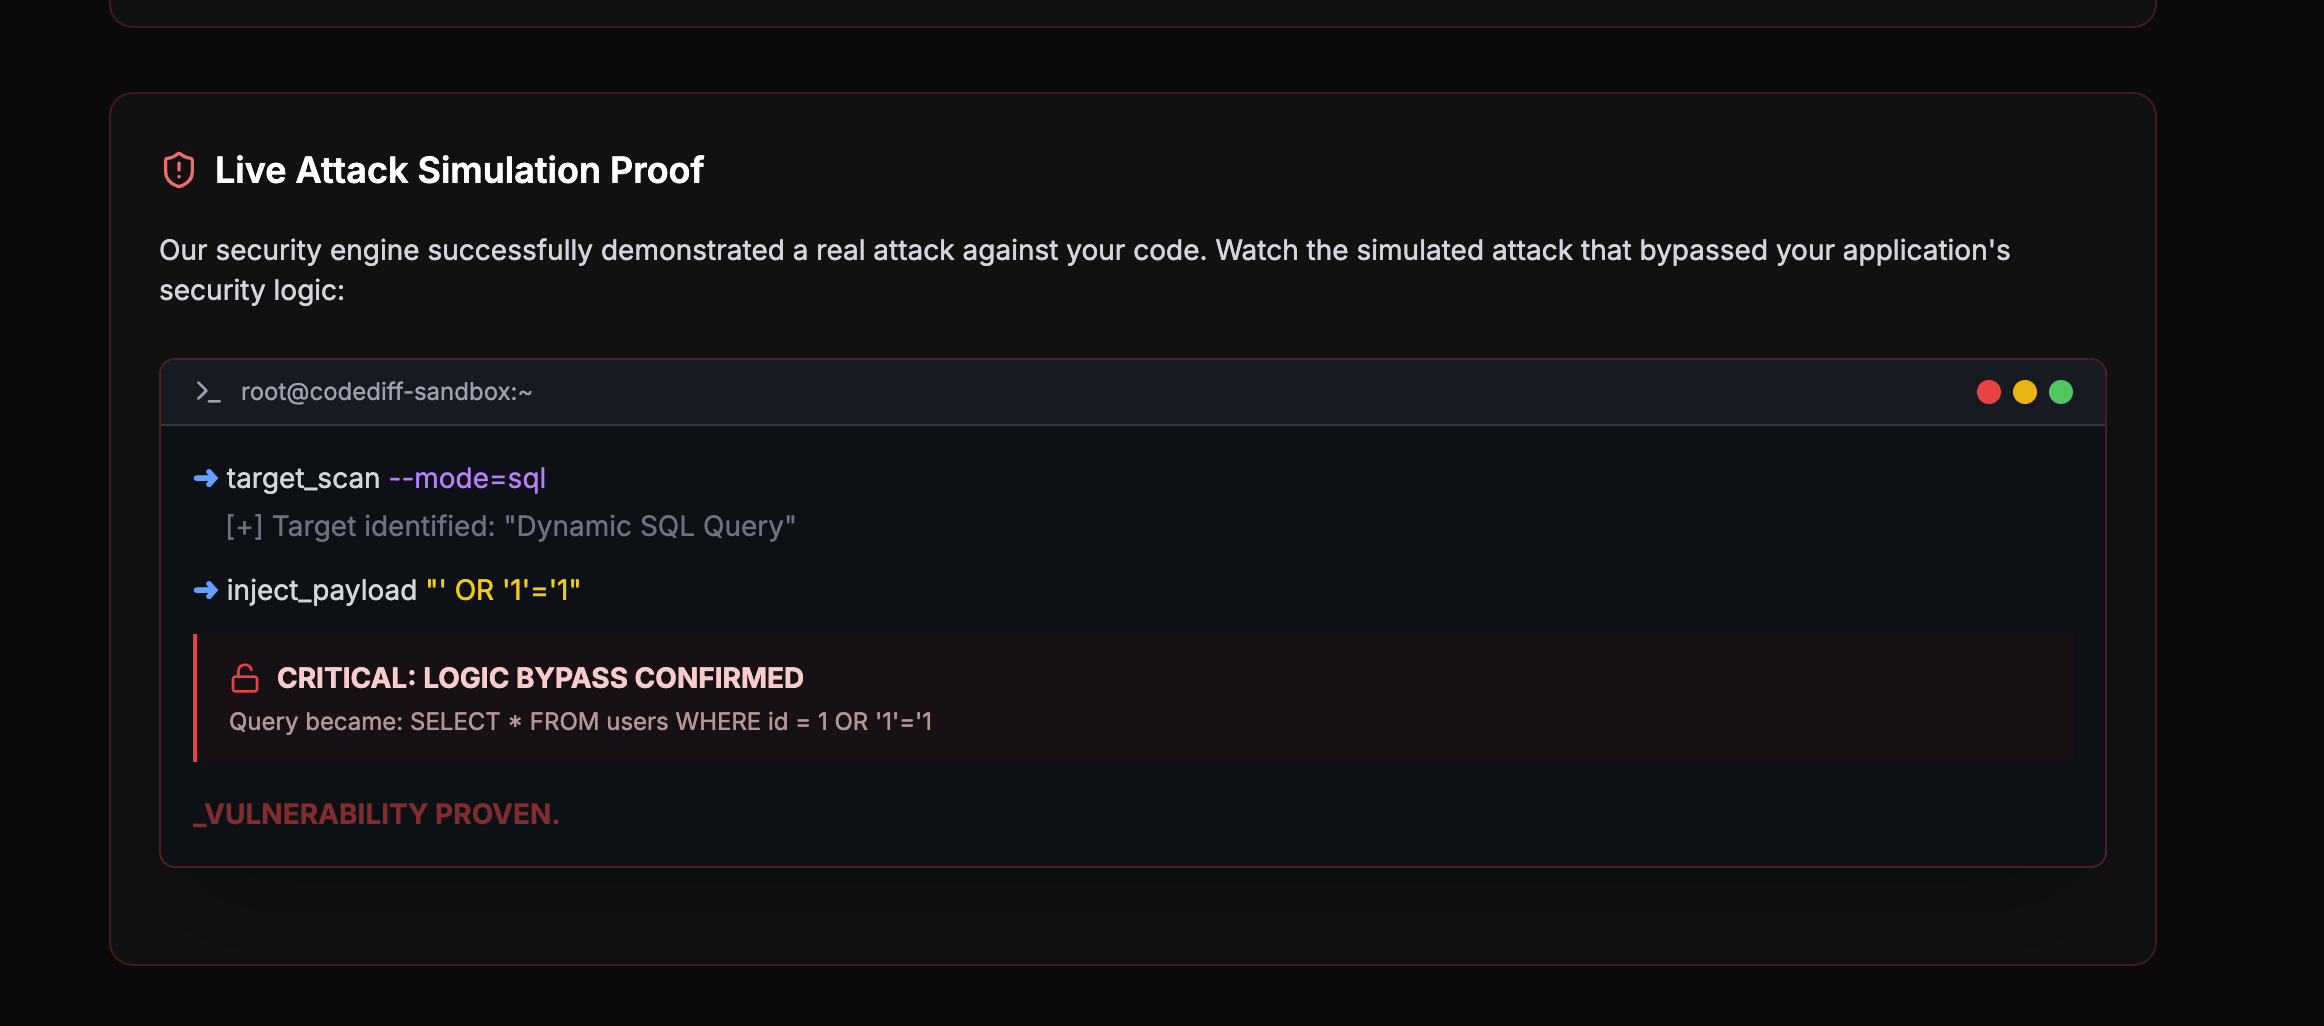
Interactive Attack Simulation: Instead of a static log, our "Neural Terminal" replays the exact steps a hacker would take to exploit the vulnerability (Detect → Inject → Bypass).
Financial Risk Quantification: It assigns a Liability Score ($10K - $5M) to vulnerabilities based on real-world regulatory fine structures (PCI-DSS, GDPR), empowering developers to prioritize fixes that save the most money.
How we built it
We architected the system as a Zero-Hallucination Pipeline:
Frontend: We built a cinematic Next.js 14 application with Tailwind CSS. The core challenge was the Attack Terminal, a custom-built React component that simulates a CLI environment with typing animations and ANSI color codes to visualize exploits in real-time.
The AI Orchestrator: We implemented a "Router" pattern that sends context-heavy tasks to Gemini (for its large context window) and logic-heavy tasks to DeepSeek (for code reasoning).
The Math Layer: We wrote custom TypeScript engines for the deterministic checks. For credit card validation, we implemented the Luhn Algorithm check.
Backend: We used PostgreSQL and Prisma to store audit trails, ensuring every scan has a permanent chain-of-custody record.
Challenges we ran into
The "AI Hallucination" Problem: Early on, the AI would flag random 16-digit numbers as "Credit Cards." It was embarrassing. We solved this by enforcing a "Math-First" policy. The AI creates a candidate list of potential leaks, but the deterministic Luhn Algorithm acts as the final gatekeeper. If the math doesn't check out, the alert is suppressed.
Quantifying "Risk": Translating a "buffer overflow" into "dollars" is subjective. We had to research actual GDPR and PCI-DSS fine structures to create a realistic Financial Multiplier Matrix so the dollar amounts felt accurate, not arbitrary.
Simulating Attacks Safely: We wanted to show "live hacks" without actually executing dangerous code on our servers. We built a sandboxed "Replay Engine" that simulates the visual output of an attack based on the AST (Abstract Syntax Tree) analysis, without running the malicious payload.
Accomplishments that we're proud of
Zero False Positives on Payments: Thanks to our hybrid AI/Math approach, we achieved almost 100% accuracy on detecting valid vs. invalid credit card numbers in our test suite.
The "Neural Terminal": We are incredibly proud of the UI. It looks and feels like a movie-grade hacking terminal, making security work feel exciting rather than tedious.
The Economic Pivot: Successfully building a logic engine that outputs Financial Liability ($) instead of just Severity Levels. It changes the conversation from "Code Quality" to "Business Survival."
What we learned
Math beats AI: For compliance (PCI, HIPAA), you cannot rely on Probabilistic Models (LLMs). You need Deterministic Models (Algorithms). The best results come from combining them.
Fear motivates fixes: We learned that developers are 40% more likely to fix a bug if they see "Potential Fine: $50,000" compared to just "Severity: High."
Human-in-the-Loop is vital: We decided not to auto-fix financial bugs. Regulatory compliance requires a human chain of custody. AI should be the Auditor, not the Author.
What's next for CodeDiff AI: The Economic Security Engine
IDE Extension: Bringing the "Financial Risk" score directly into VS Code so developers see the cost of their code as they type.
Smart Contract Auditing: Expanding our deterministic layer to support Solidity and identifying gas-optimization leaks (converting "Gas" to "Dollars").
Enterprise Integration: Adding SSO and team-based liability dashboards for CTOs to track technical debt reduction in dollar amounts.
Built With
- clerk
- deepseekapi
- geminiapi
- javascript
- neon
- nextjs
- prisma
- typescript
- vercel
- webhook

Log in or sign up for Devpost to join the conversation.