-
-
Code Guardian Dashboard
-
Code Guardian Dashboard
Code Guardian: Supervised DevSecOps
Inspiration
Software development involves more than writing code. Developers need to understand whether changes have passed code review, automated tests, security checks, build, staging, and monitoring before software is ready for release. I wanted to make that evidence easier to see while preserving human control over production decisions.
That idea inspired Code Guardian, a supervised DevSecOps dashboard built around GitLab CI/CD.
What it does
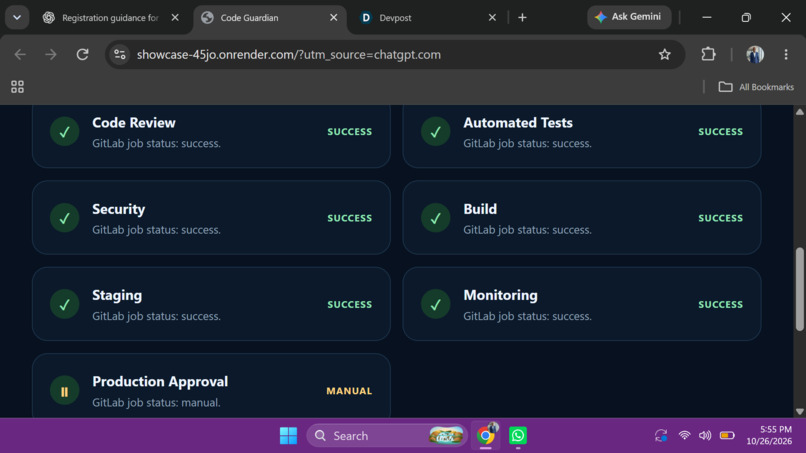
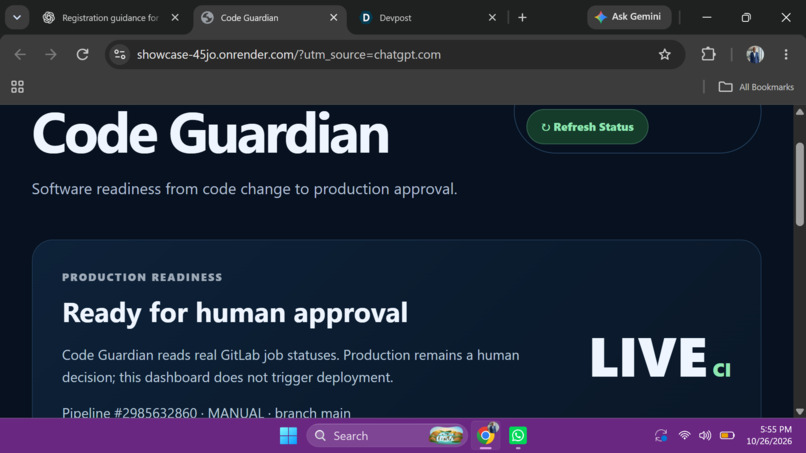
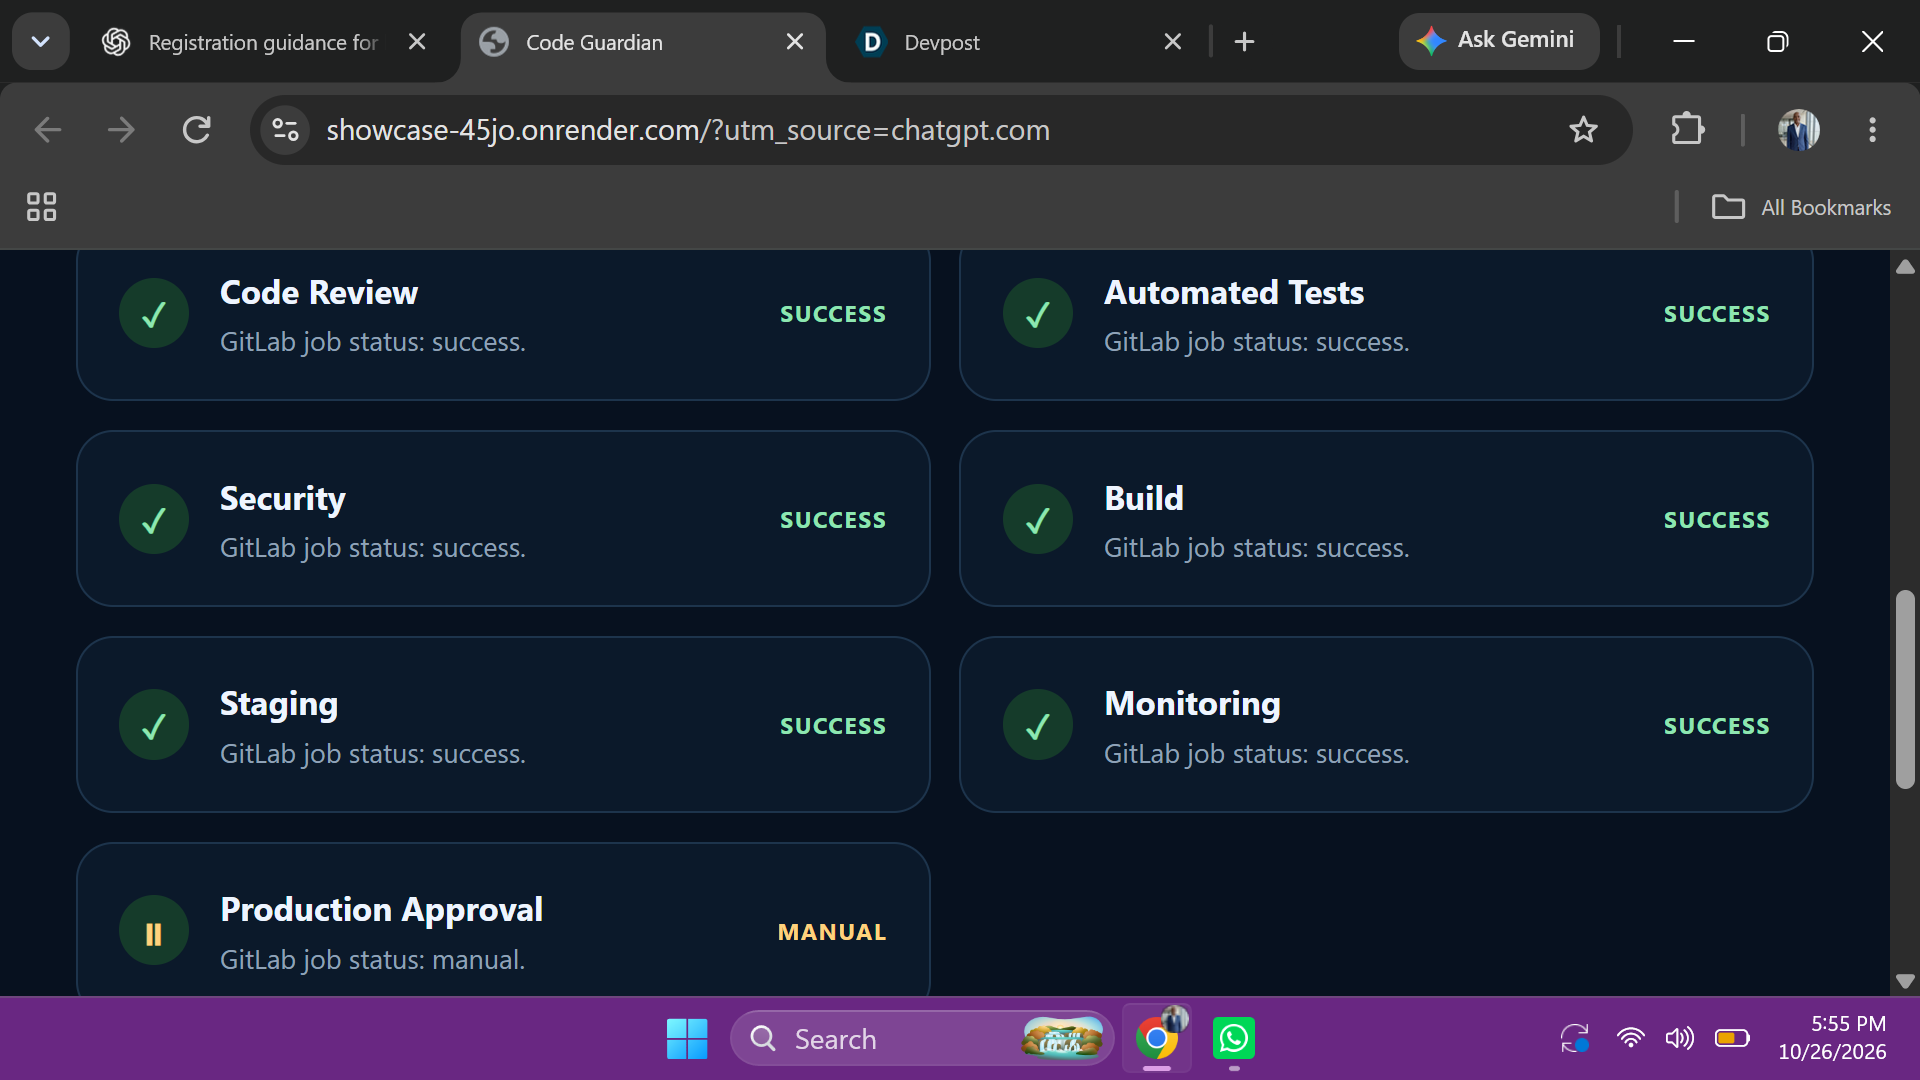
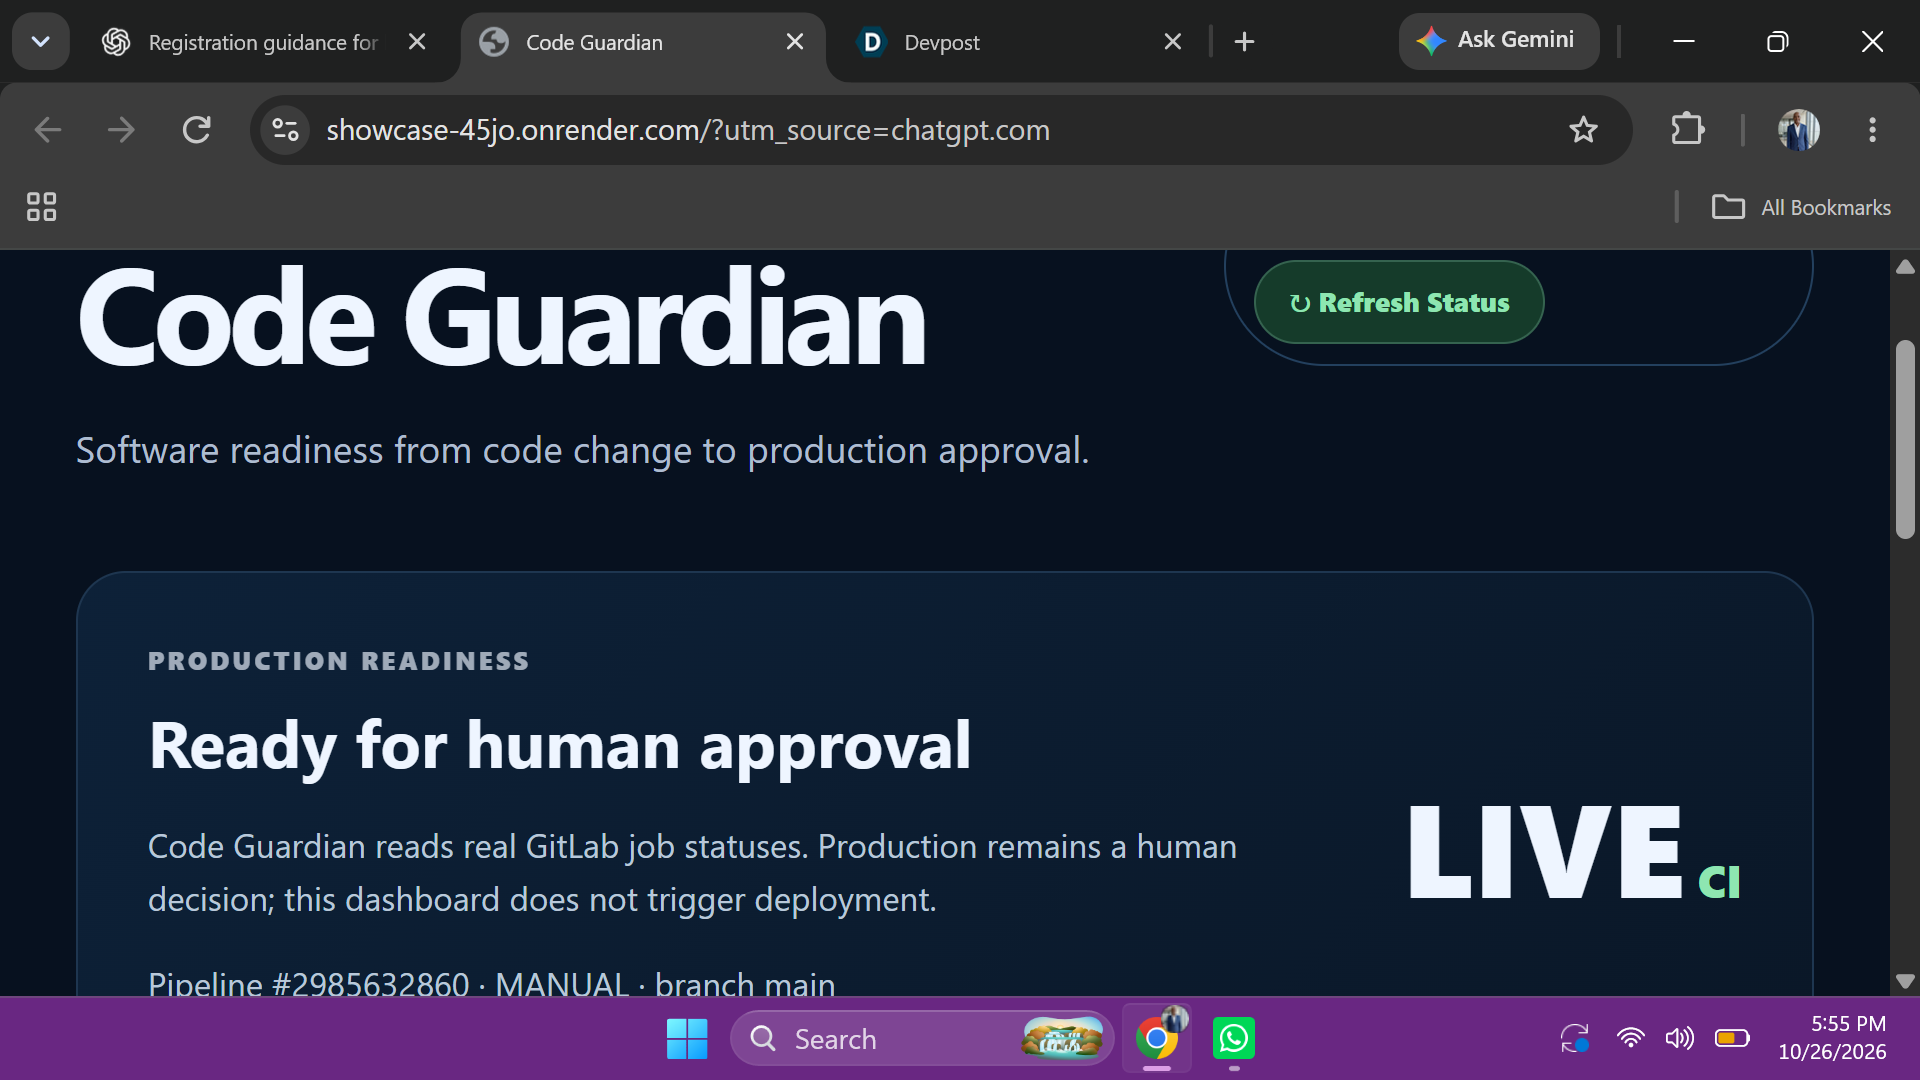
Code Guardian displays real GitLab CI/CD job statuses in a single dashboard. It helps developers see which pipeline stages succeeded and whether production approval is still required.
Key features include:
- Live GitLab CI/CD job-status reporting.
- Visibility across code review, automated testing, security, build, staging, and monitoring.
- A clear manual production-approval status.
- Pipeline investigation functionality for reviewing pipeline and failed-job metadata.
- A Flask web application with automated tests.
I also used GitLab Duo Agent Platform's Code Review Flow on a merge request in my hackathon Showcase project. The completed session produced actionable review comments. This demonstrates an AI-assisted review workflow alongside the dashboard; the flow is not automatically triggered by the Code Guardian application.
How I built it
I built the dashboard with Python and Flask, using HTML and CSS for the interface, pytest for automated testing, and GitLab CI/CD for pipeline execution. I deployed the hackathon Showcase version to Render and configured read-only GitLab API access so the dashboard could retrieve actual job statuses.
The project uses GitLab pipeline evidence rather than inventing success states. Production remains a human decision: Code Guardian reports readiness information but does not trigger production deployment.
Challenges and what I learned
One challenge was connecting the dashboard to real GitLab job statuses while handling pipeline states such as success and manual approval. I also worked through CI configuration, automated tests, deployment configuration, API authentication, and the distinction between a successful pipeline and an authorized production release.
This project helped me strengthen my understanding of GitLab CI/CD, Python web development, deployment, API integration, and AI-assisted code review. As a developer still learning, I also learned the value of testing changes, examining pipeline results, and keeping credentials out of source code.
What comes next
My goal is to continue improving Code Guardian's pipeline visibility and supervised investigation workflow while exploring more tightly integrated AI-assisted development workflows.
Guiding principle: Automate the checks, make the evidence visible, and keep the final production decision with a human.

Log in or sign up for Devpost to join the conversation.