Files used in handoffs, audits, and disputes are easy to rename or replace. Screenshots and timestamps do not prove that the bytes being reviewed are the original bytes.
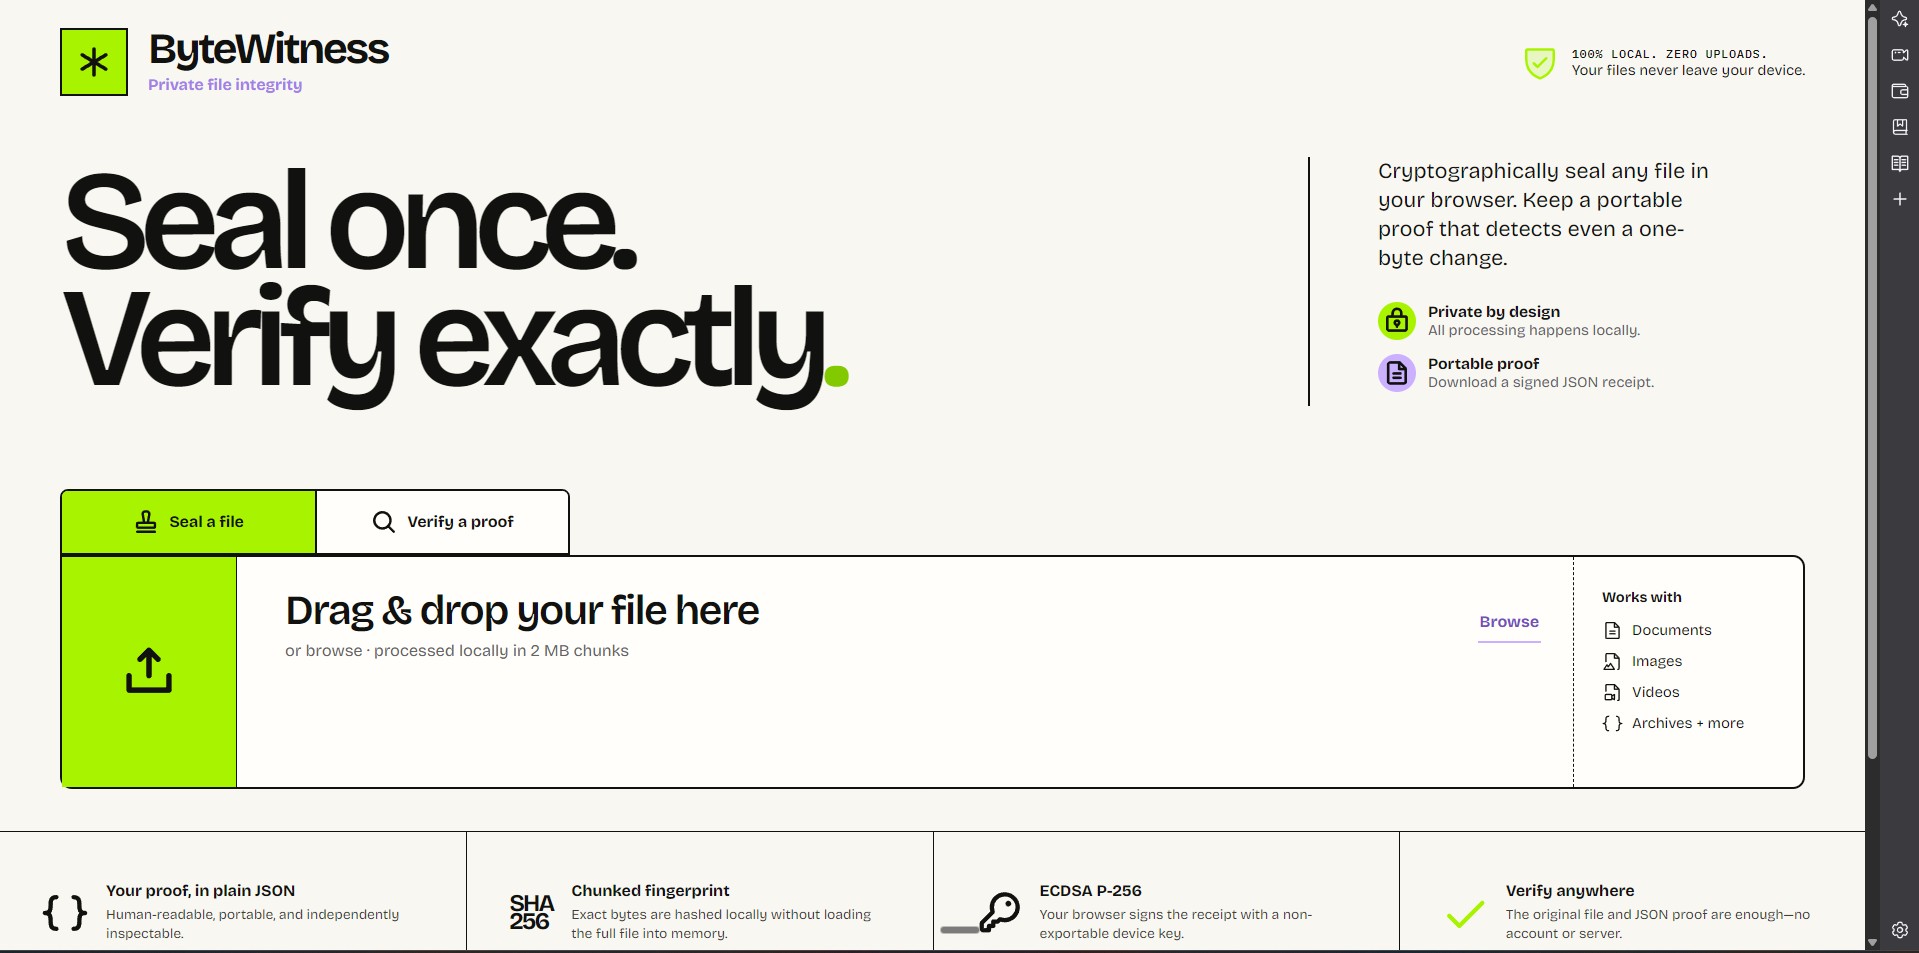
ByteWitness creates a portable integrity proof entirely in the browser. It hashes the selected file in chunks with SHA-256, hashes the selected file in chunks and signs the digest with a non-exportable ECDSA P-256 key, then exports a .bytewitness.json receipt. Later, the same browser can verify the receipt signature and compare the current file byte-for-byte against that proof.
There is no backend, account, or file upload. Private key material stays non-exportable in browser storage, while strict Zod validation rejects malformed or unsupported receipts.
Usage:
- Seal: choose a source file and create a receipt.
- Verify: select the matching file and receipt to check integrity.
- Results show unchanged, changed-file, invalid signature, malformed receipt, or missing signer context states.
ByteWitness is intentionally narrow: it proves byte identity and continuity of a local signing key. It does not prove legal identity, ownership, authorship, or trusted creation time.
Built With
- ecdsa
- react
- typescript
- vite
- web-crypto-api
- zod


Log in or sign up for Devpost to join the conversation.