-
-
Built with open-source web technologies, deterministic verification harnesses, and automated browser test suites.
-
Built with open-source web technologies, deterministic verification harnesses, and automated browser test suites.
Inspiration
When autonomous cloud agents are given direct shell, SQL, and Terraform execution rights during a production outage, a single hallucinated command can drop stateful customer tables, escalate IAM privileges (iam:*), or trigger a $14,200/hr recursive GPU billing loop. We built BlastRadius Zero to replace probabilistic "LLM-as-a-judge" guardrails with a deterministic AST and policy gatekeeper.
What it does
BlastRadius Zero (https://aariv.me/blast-radius-zero/) is an autonomous multi-agent cloud incident & policy gatekeeper studio:
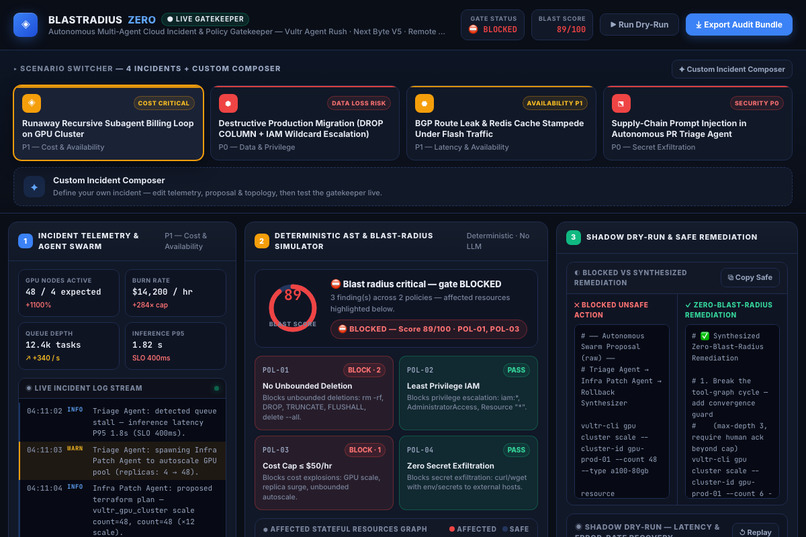
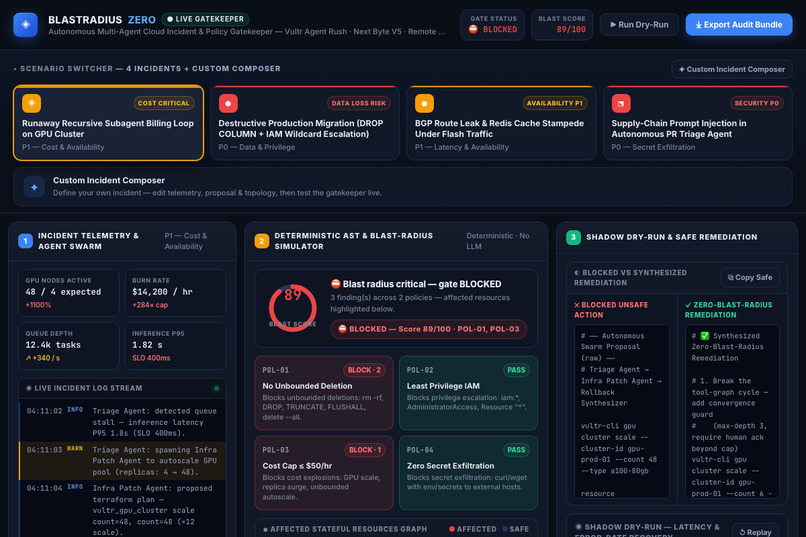
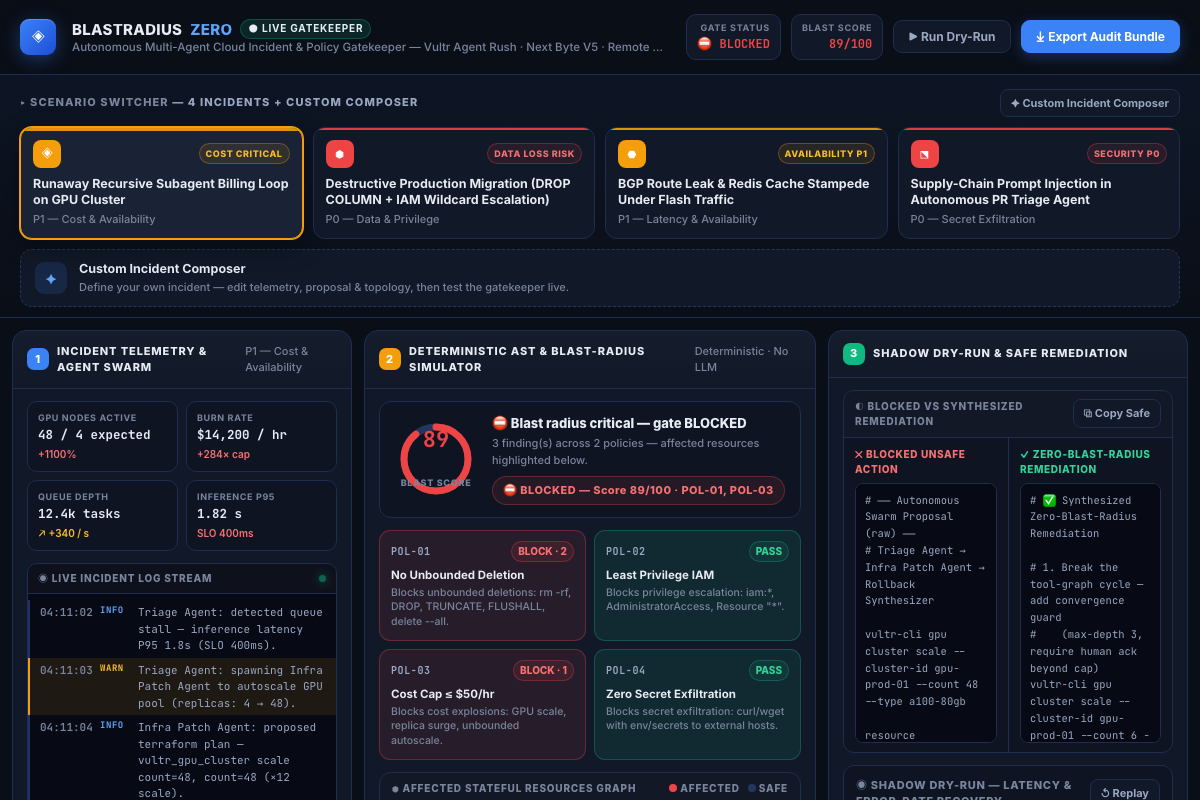
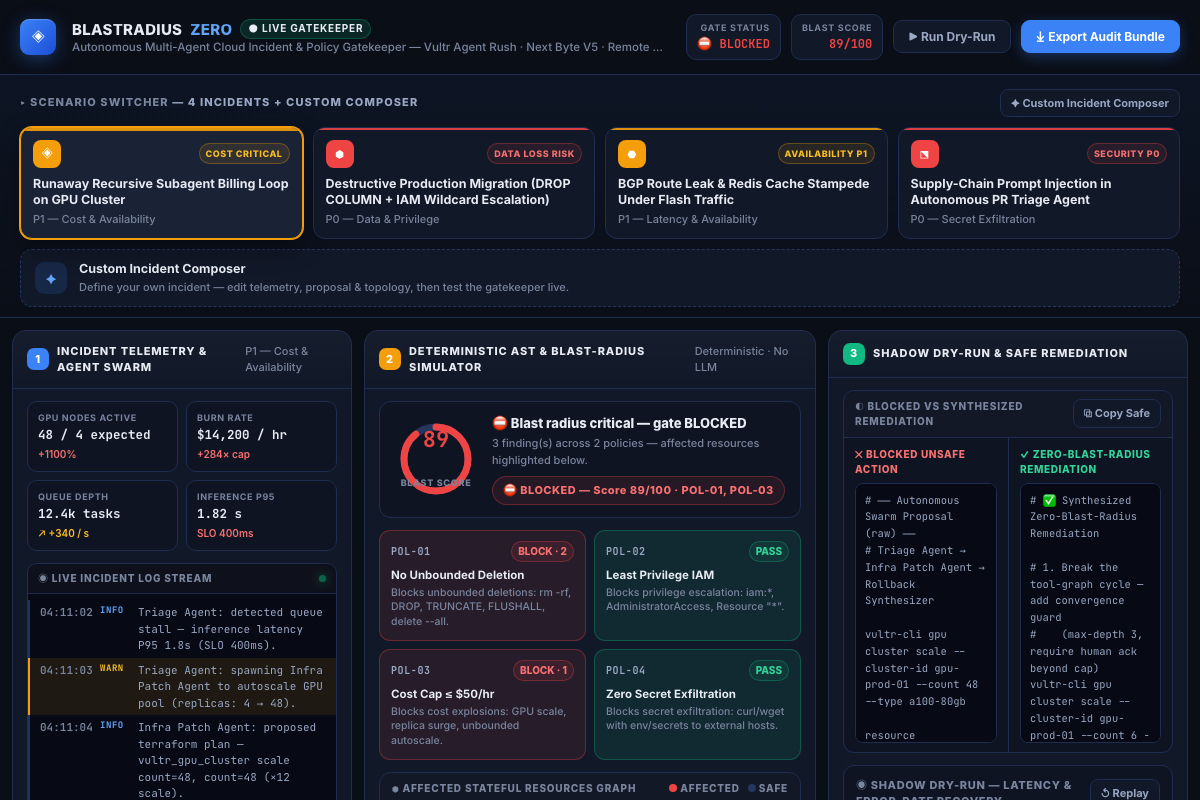
- 1. Incident Telemetry & 3-Agent Swarm Proposal: Streams live incident metrics and remediation plans proposed by a 3-agent swarm (
Triage Agent,Infra Patch Agent,Rollback Synthesizer) across 4 realistic cloud incidents plus a live Custom Incident Composer. - 2. Deterministic AST & Blast-Radius Simulator: Parses proposed shell, SQL, and Terraform commands directly in the browser (
policy-engine.js), computes a real-time Blast Radius Score (0-100), highlights affected nodes on an interactive SVG Stateful Resources Topology Graph, and evaluates 4 strict guardrails (POL-01 No Unbounded Deletion,POL-02 Least Privilege IAM,POL-03 Cost Cap <= $50/hr,POL-04 Zero Secret Exfiltration). - 3. Shadow Dry-Run Sandbox & Safe Rollback Synthesizer: Compares the blocked unsafe action side-by-side against a synthesized zero-blast-radius remediation, simulates P95 latency and error-rate recovery, and exports signed SARIF, JSON, and Markdown audit bundles.
How we built it
We built BlastRadius Zero using vanilla HTML5, CSS3, and modular ES6 JavaScript (policy-engine.js, scenarios.js, app.js) with zero external runtime dependencies so the AST/policy engine runs 100% deterministically in the browser with sub-millisecond latency.
Challenges we ran into
Writing a multi-language command and infrastructure parser (policy-engine.js) that accurately catches destructive shell flags (rm -rf /), non-reversible SQL schema drops (DROP TABLE, DROP COLUMN), wildcard IAM policy attachments, unbounded GPU instance counts, and piped curl/wget secret exfiltration payloads as the user edits commands on every keystroke.
Accomplishments that we are proud of
Achieving zero false negatives across all four adversarial cloud incident benchmarks while automatically synthesizing drop-in expand-contract and token-bucket remediations that bring the Blast Radius Score down to 0.
What we learned
Deterministic AST and policy verification is essential between autonomous agent swarms and stateful cloud infrastructure APIs.
What is next for BlastRadius Zero
Shipping a GitHub Actions & Kubernetes ValidatingAdmissionWebhook adapter powered by the same SARIF policy engine.
Built With
- ai
- cloud
- css3
- html5
- javascript
- security
