-
4
-
3
-
2
-
1
Inspiration
What it does## What it does
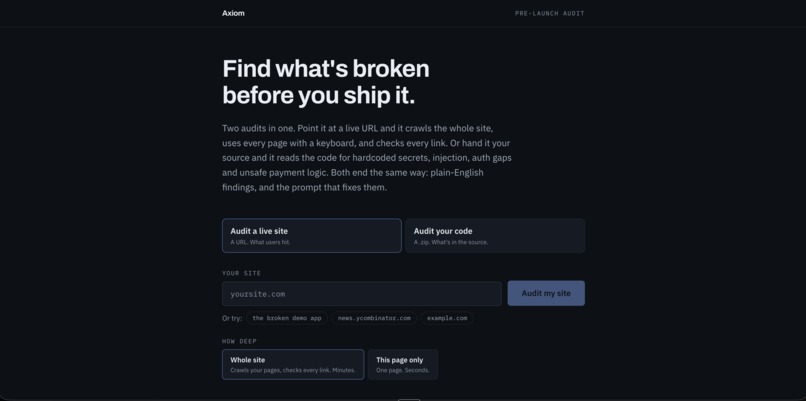
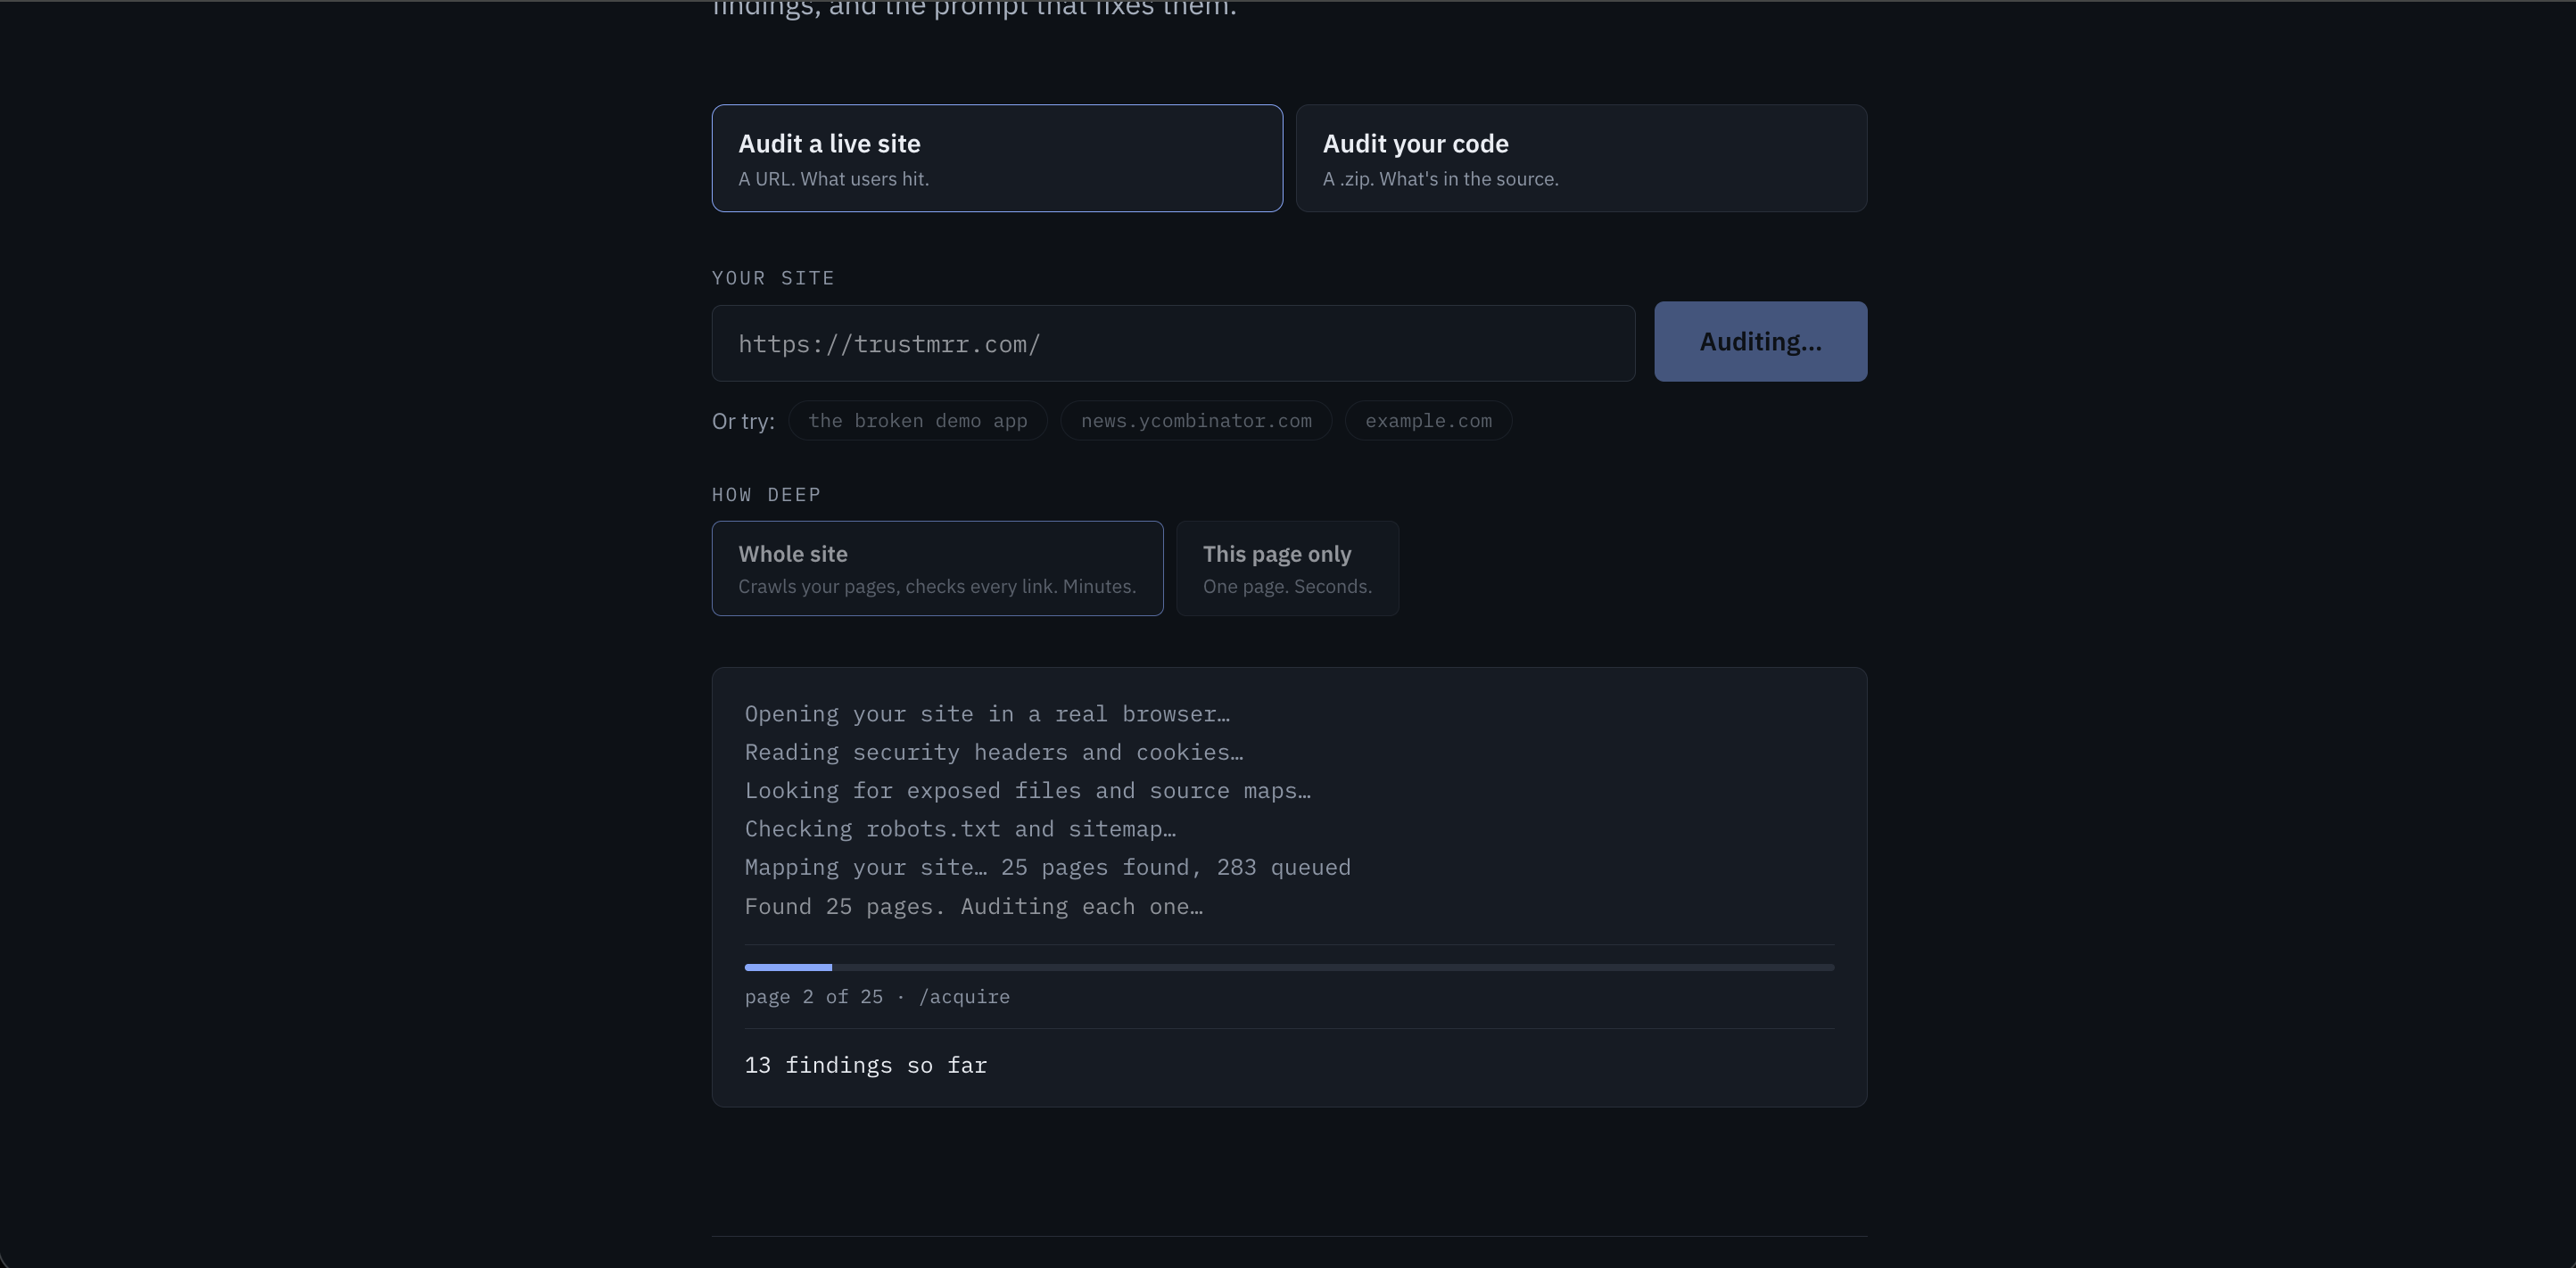
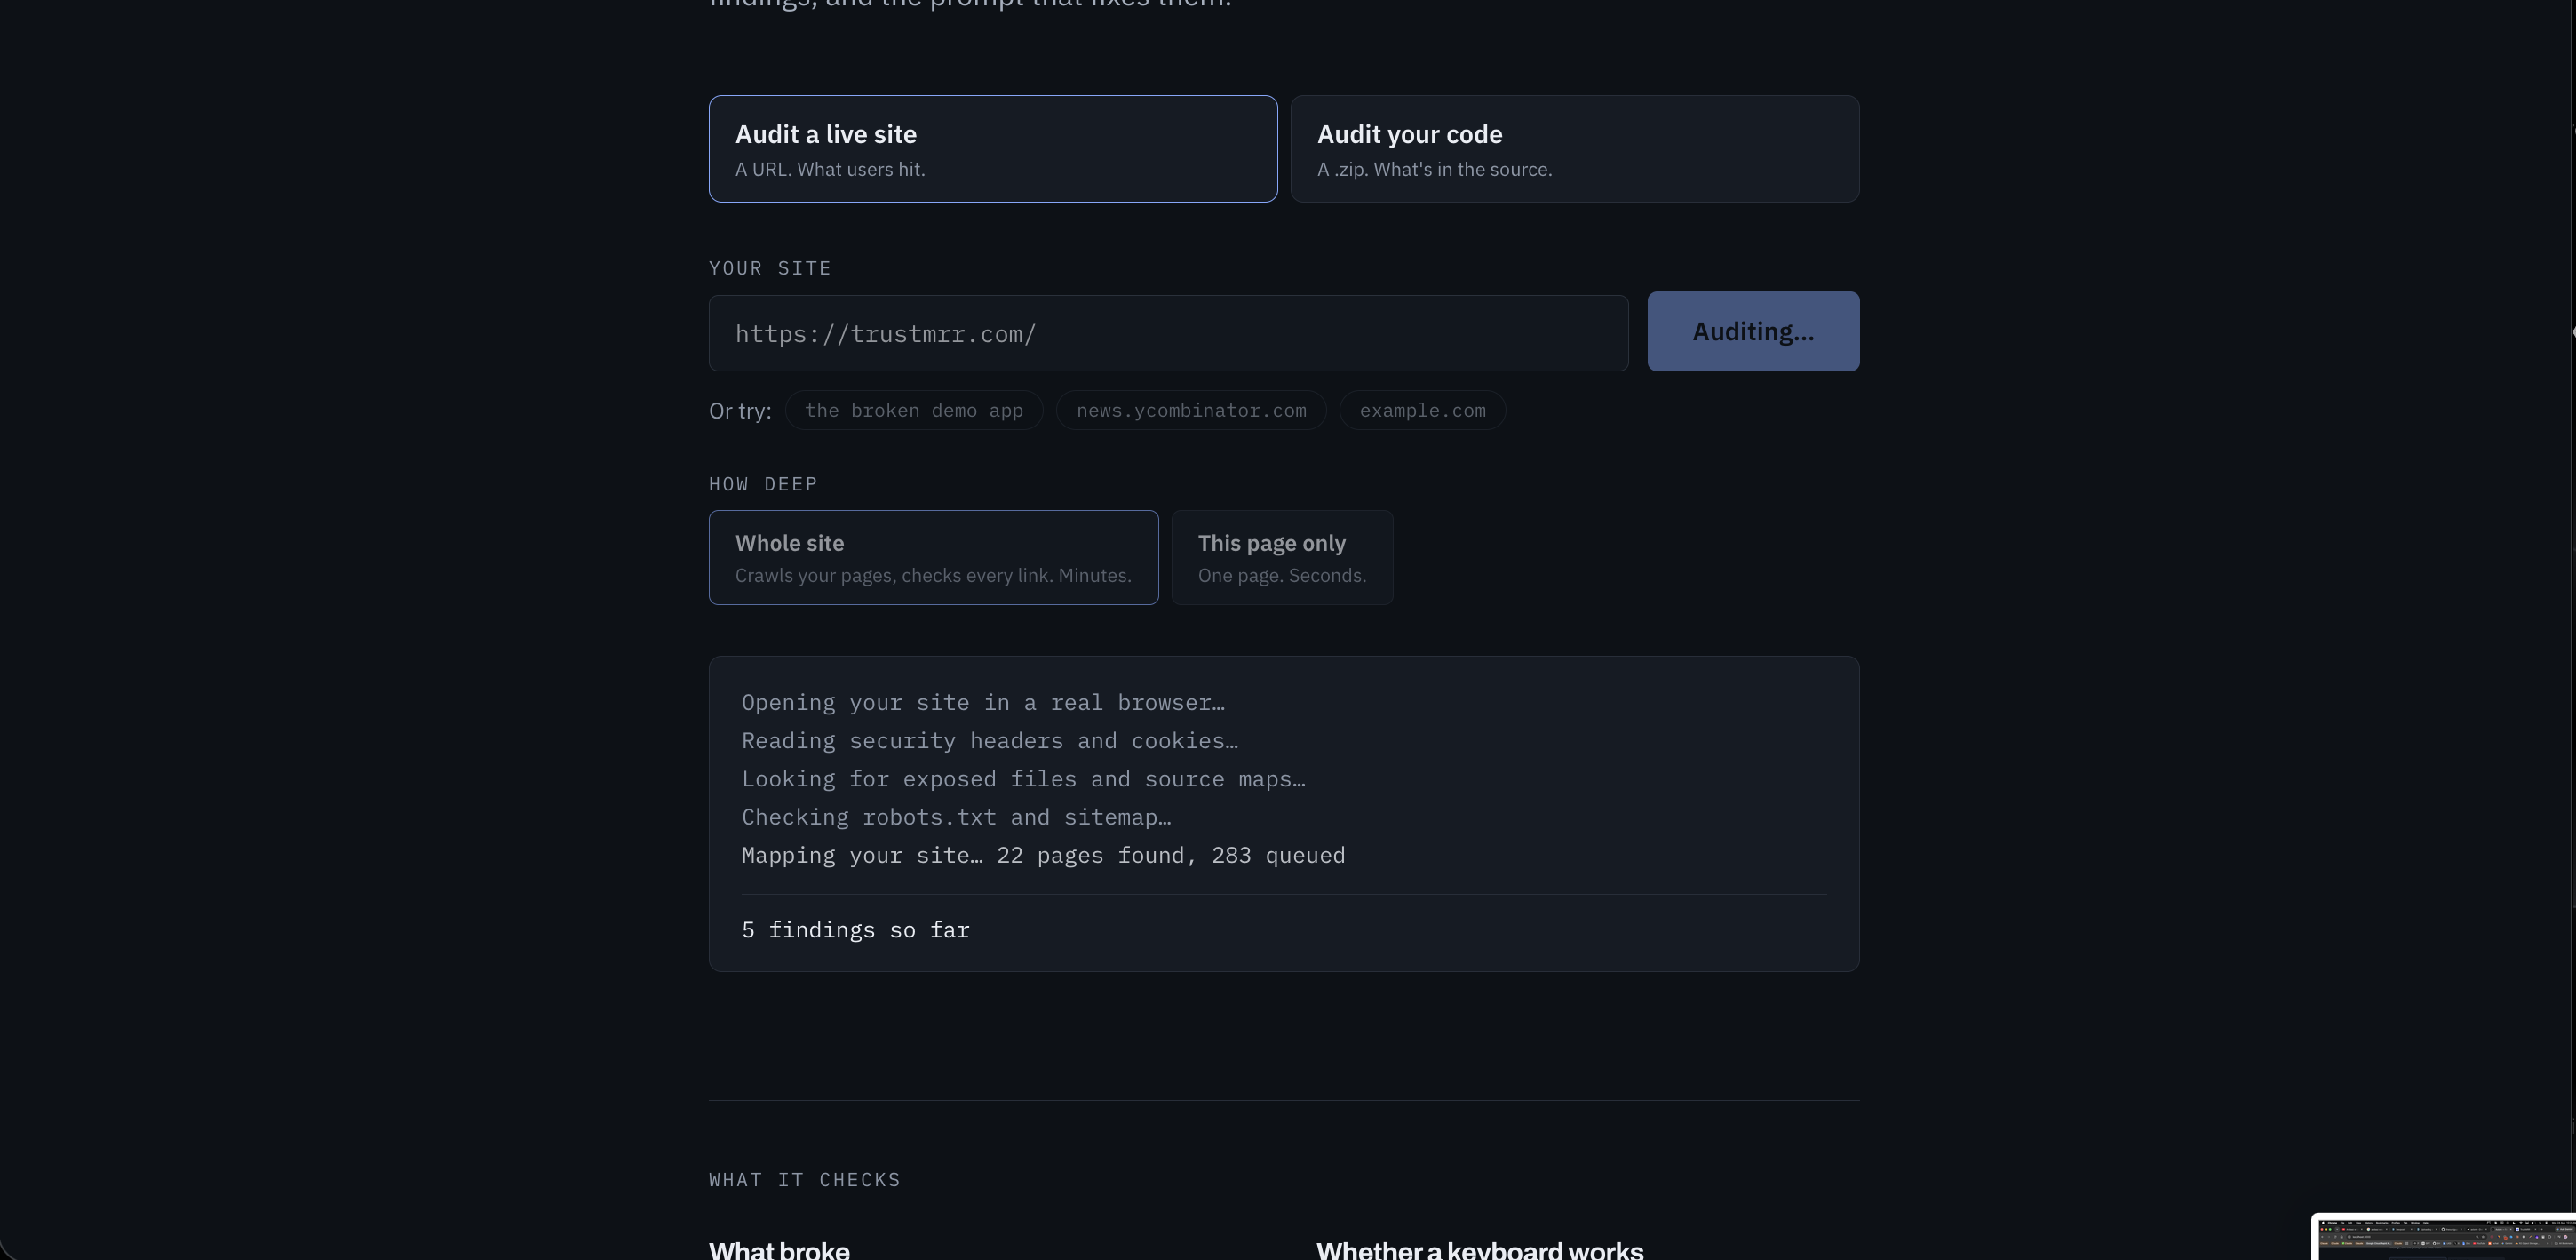
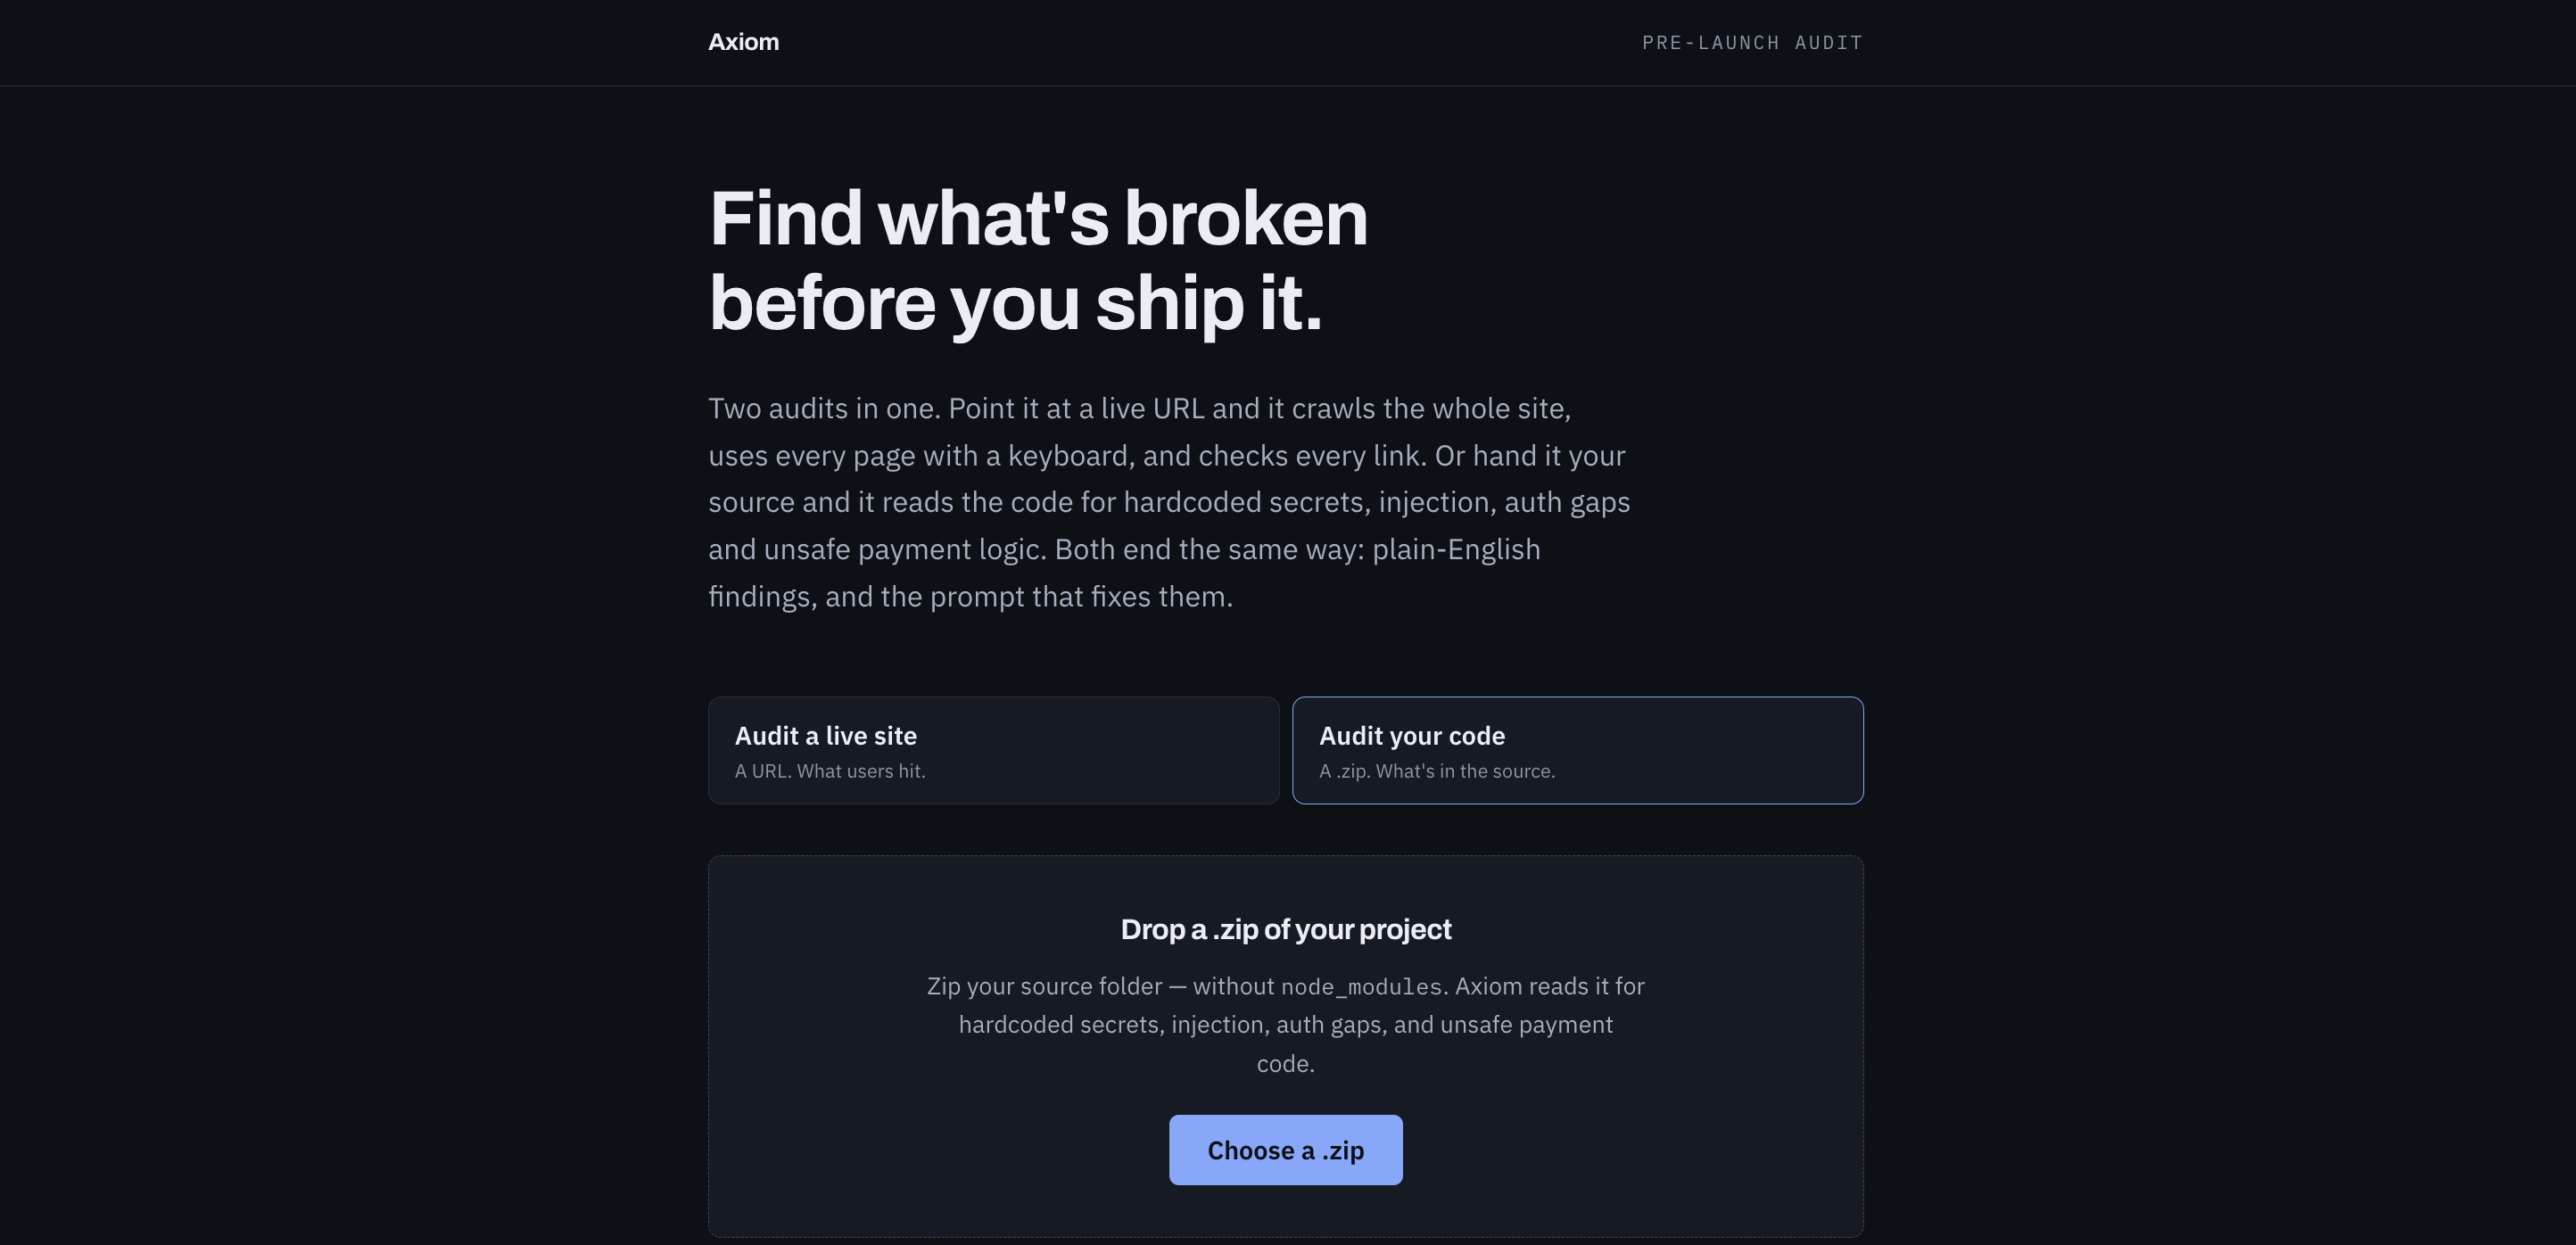
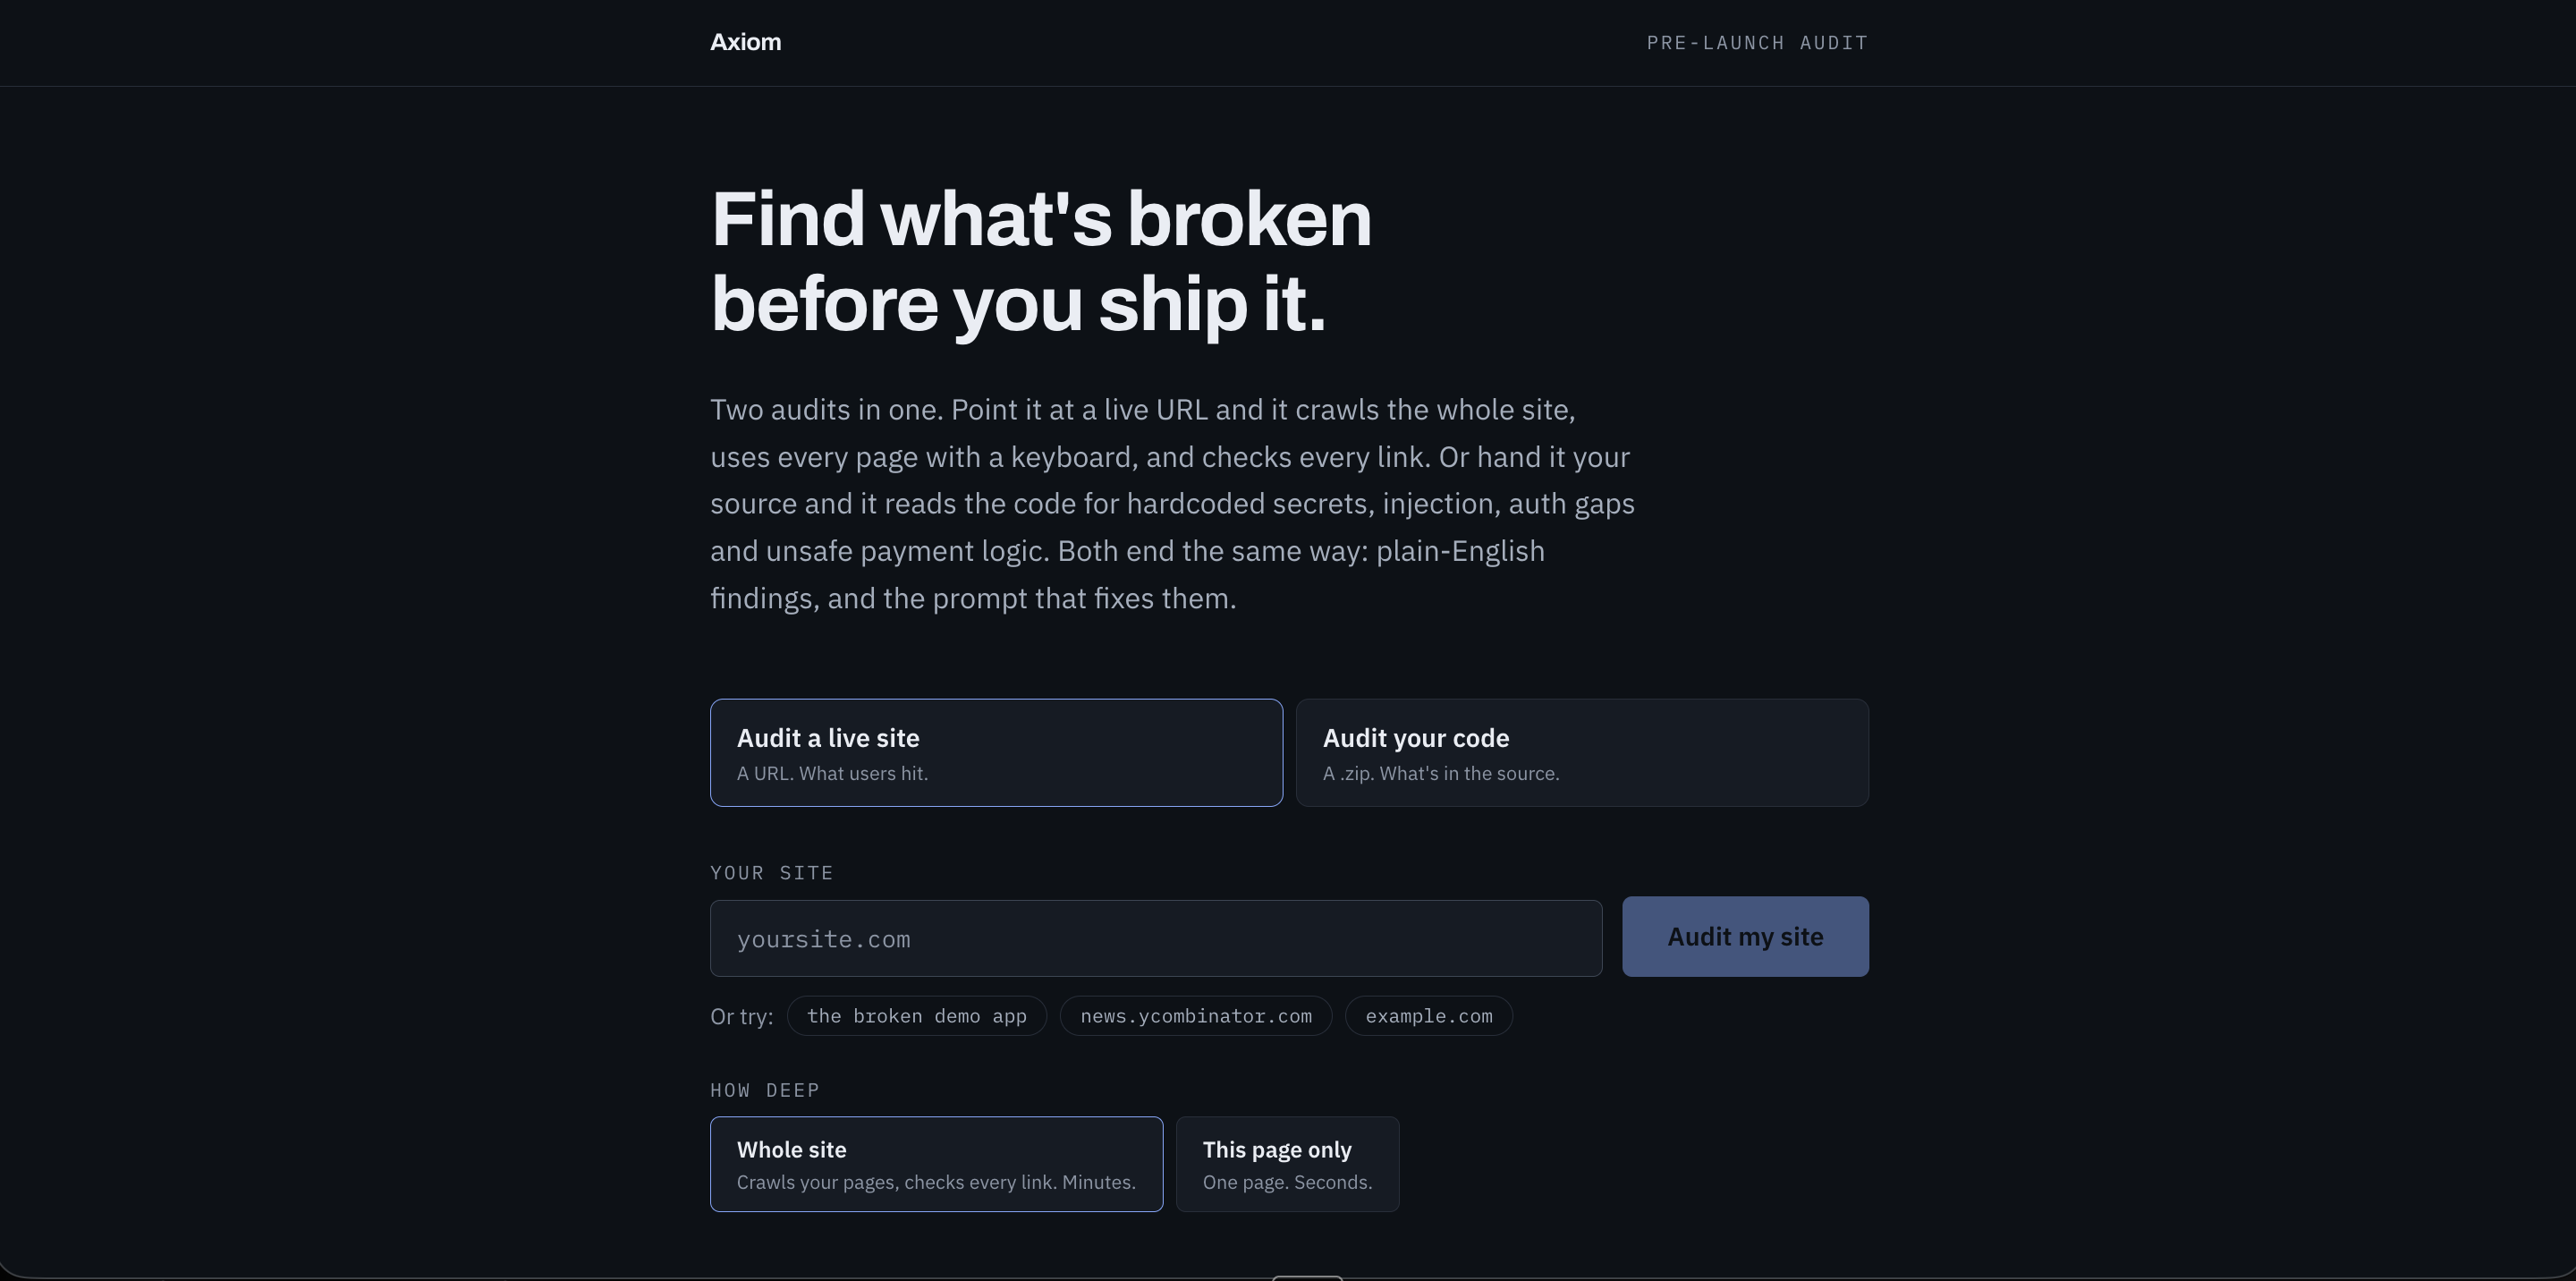
Axiom is two audits in one.
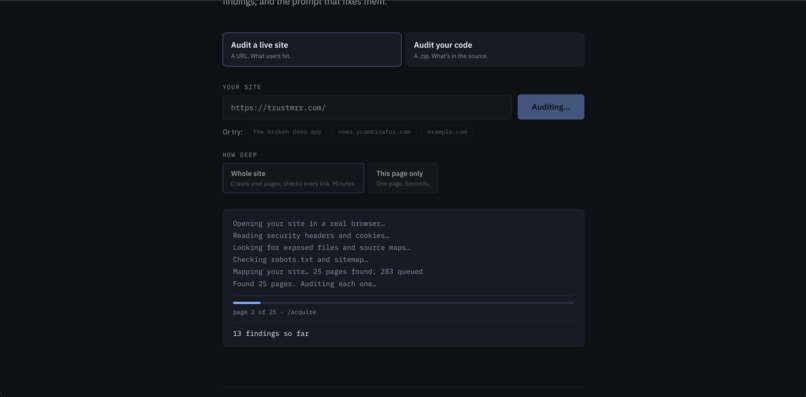
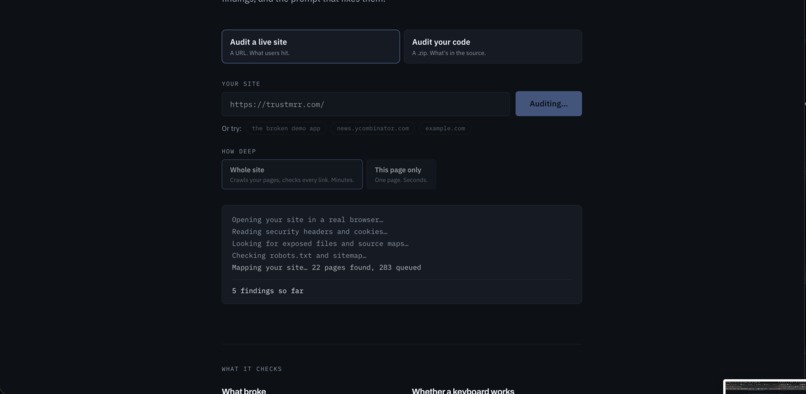
Point it at a URL and it crawls your whole site, opens every page in a real browser, and actually uses it — pressing Tab through each screen like a keyboard-only user, checking every link, rendering each page on a phone, and reading the security headers, cookies and exposed files.
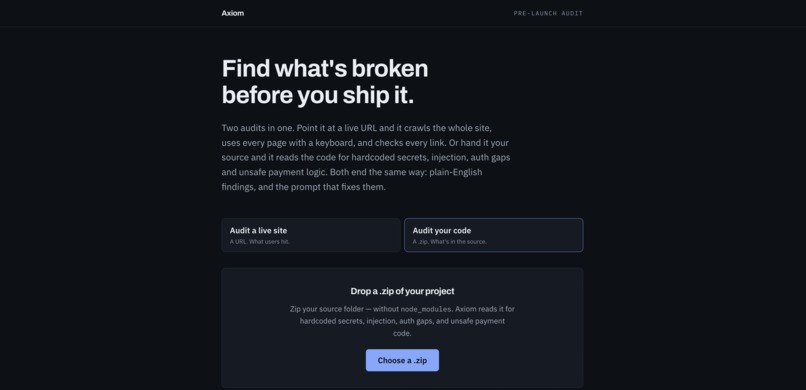
Or hand it your source code and it reads it for the security bugs AI coding assistants ship constantly: hardcoded API keys, SQL built by string concatenation, login routes with no rate limiting, payment amounts trusted from the client.
Both audits end the same way — plain-English findings ranked by severity, and a ready-to-paste prompt that makes Claude Code (or any agent) fix them.
Inspiration
95.9% of the top million homepages fail WCAG, and 5,000+ web-accessibility lawsuits were filed in 2025. Meanwhile people ship AI-built apps in an afternoon with no security headers, exposed .env files, and buttons keyboard users can never reach. The bugs that matter most aren't visible from reading source — you find them by using the app.
How we built it
Next.js 16, TypeScript, Playwright and axe-core. The live audit runs two browser passes — one under the site's real Content Security Policy to catch genuine runtime errors, one instrumented to inject the auditor — because bypassing CSP to inject a harness also hides the failures CSP itself causes. The code audit is static analysis: secret scanning with masking, plus pattern rules for injection, auth and payment bugs. It runs 100% locally or unzips in memory on upload — your code is never stored or sent to any model. Found secrets are always masked (sk_live_••••••7a4).
What makes it different
Every other tool stops at "here's a list." Axiom uses the site — no scanner finds an unreachable button by reading HTML; you find it by pressing Tab and watching where focus never lands. And it's honest: it refuses to invent alt text it can't verify, and marks findings "detected," not "proven."
Challenges we ran into
Getting zero false positives on careful sites (w3.org came back with 2 we had to fix), and the CSP two-pass insight — which we only found by running Axiom on Axiom. It found 8 real bugs in itself, and we fixed all 8.
What's next
Authenticated crawls, a hosted CI check, and a deeper dependency-CVE pass.
How we built it
Challenges we ran into
Accomplishments that we're proud of
What we learned
What's next for Axiom
Built With
- axe-core
- fflate
- next.js
- node.js
- playwright
- tailwindcss
- typescript


Log in or sign up for Devpost to join the conversation.