Inspiration
Modern software engineering is bogged down by toil: manual code reviews, security vulnerability patching, pipeline debugging, and cloud deployments. We wanted to answer a bold question for the GitLab Transcend Hackathon: What if the entire post-code DevSecOps lifecycle could run completely autonomously with zero human intervention? Inspired by the power of multi-agent swarms and Model Context Protocol (MCP), we set out to build a system that sets an intent and walks away.
What it does
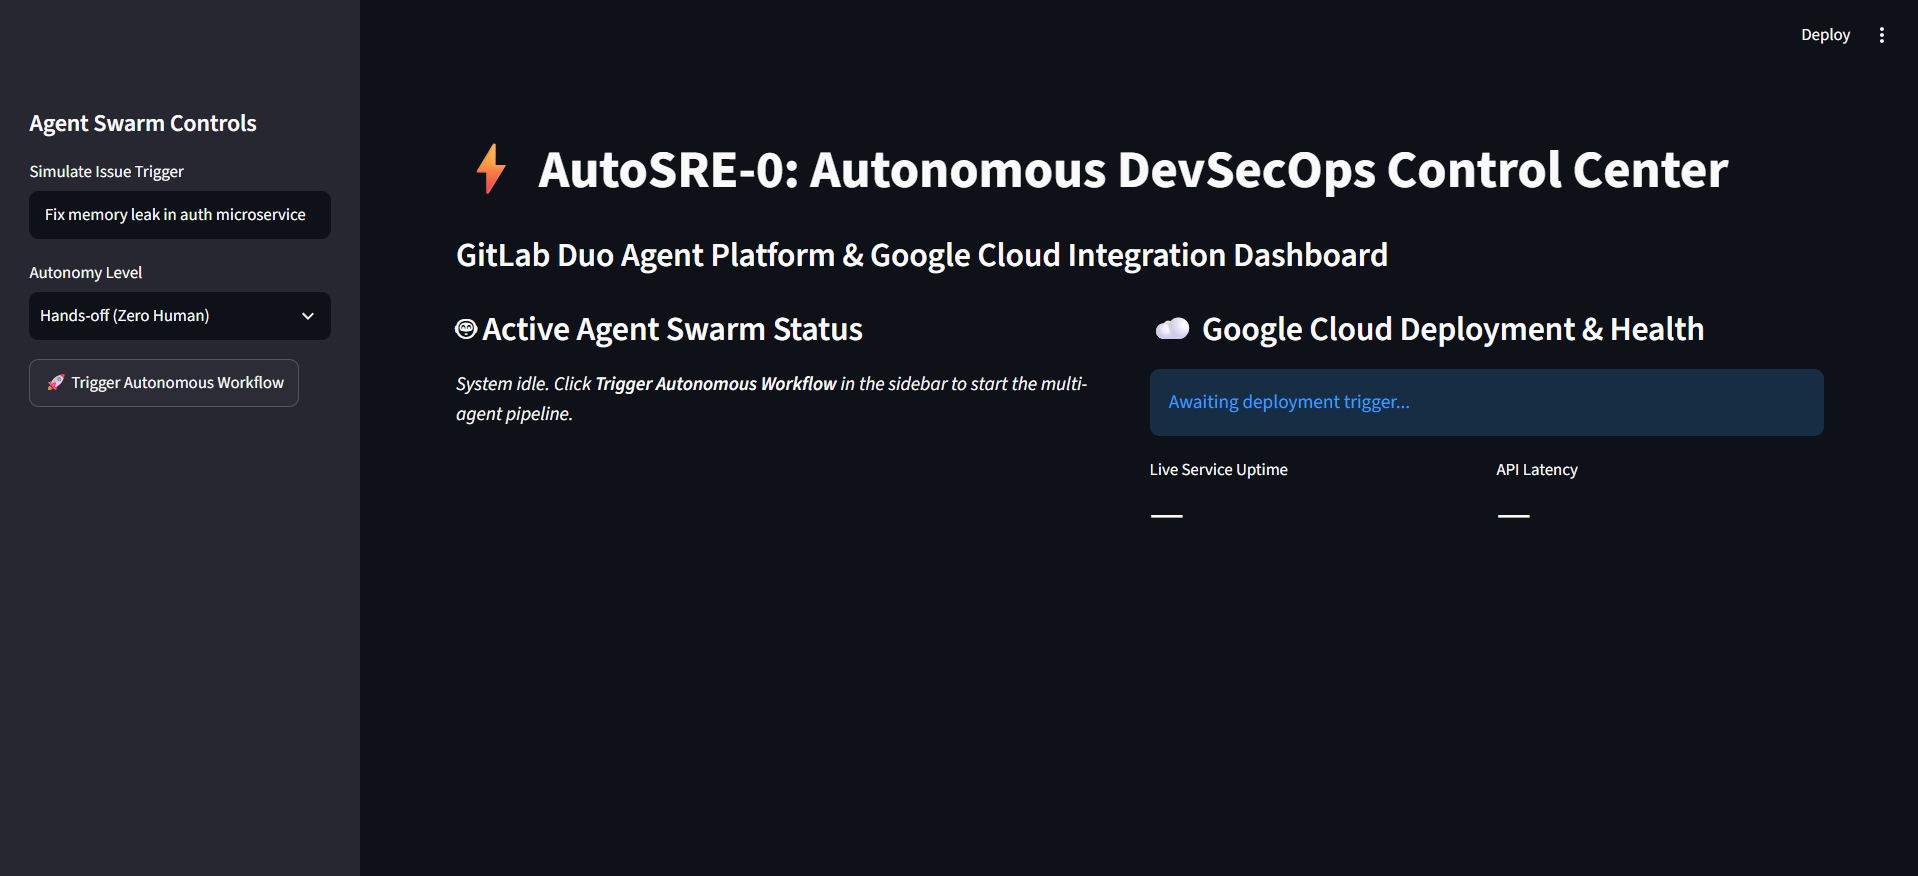
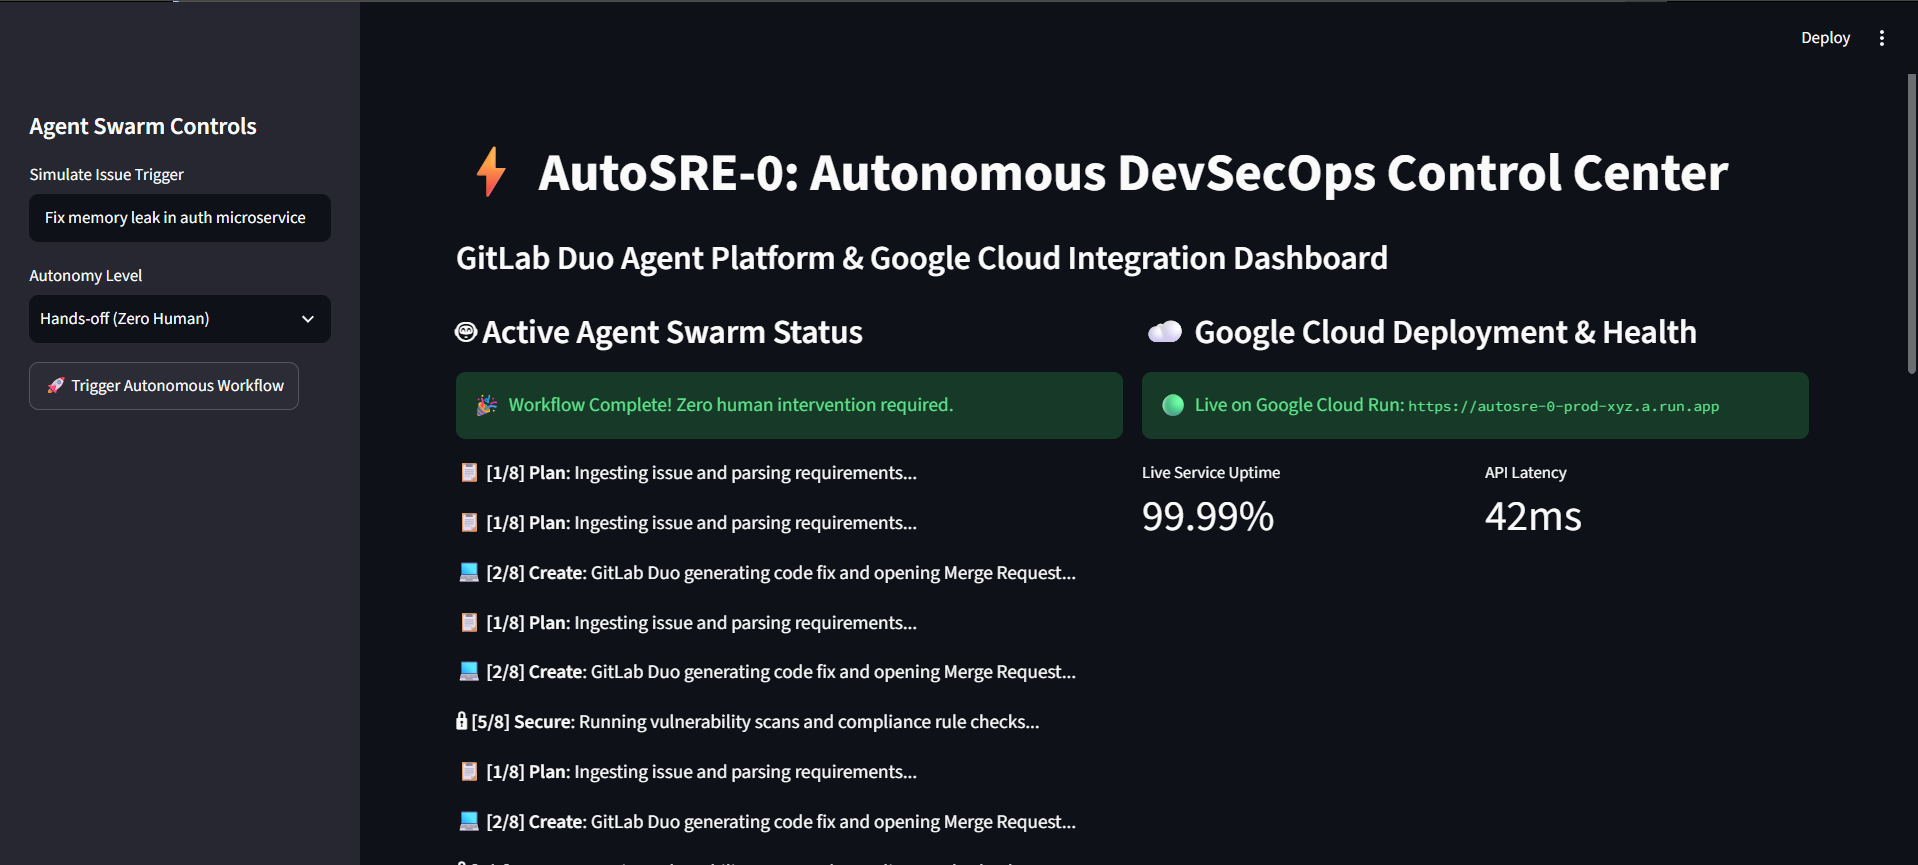
AutoSRE-0 is a hands-off, multi-agent enterprise pipeline that covers 8 out of 9 DevSecOps lifecycle stages (Plan, Create, Verify, Secure, Package, Release, Configure, and Monitor).
- When an issue is filed, an autonomous agent writes the code and opens a Merge Request.
- Specialized security and governance agents intercept the MR, running checks and auto-patching vulnerabilities.
- A pipeline healing agent monitors CI/CD logs, automatically fixing test or syntax errors until the pipeline turns green.
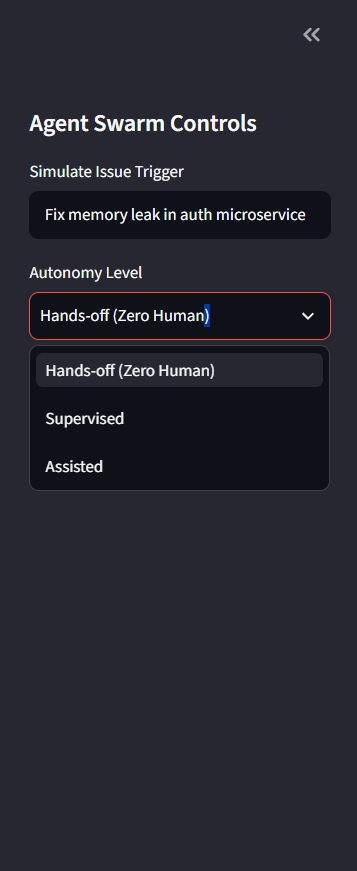
- Finally, the cloud SRE agent packages the artifact, deploys it live to Google Cloud, and validates its health.
How we built it
We leveraged the GitLab Duo Agent Platform and custom Model Context Protocol (MCP) servers to orchestrate a specialized swarm of AI agents (Coder, Security Guardian, Pipeline Healer, and Cloud SRE). The architecture utilizes event-driven triggers across GitLab's API, deep integration with GitLab CI/CD pipelines (.gitlab-ci.yml), and automated containerized deployment to Google Cloud (Cloud Run/GKE) to secure maximum hackathon bonus points.
Challenges we ran into
Coordinating multiple agents without them stepping on each other's toes was our biggest hurdle. We had to carefully design state management via MCP so that the Security Agent could patch code while the Pipeline Healer was monitoring execution logs, ensuring clean sequential handoffs without deadlocks or infinite retry loops.
Accomplishments that we're proud of
- Achieving true Hands-Off autonomy where an issue goes straight to live production without a single human click or approval.
- Spanning 8 full lifecycle stages, maximizing breadth across the GitLab DevSecOps platform.
- Seamlessly integrating live Google Cloud deployment with automated health validation.
What we learned
Building AutoSRE-0 taught us that the future of DevSecOps isn't about replacing developers with chatbots—it's about building resilient, specialized agent swarms that handle repetitive operational toil reliably in the background.
What's next for AutoSRE-0
- Integrating advanced cost-optimization agents to automatically right-size cloud infrastructure resources post-deployment.
- Expanding governance rulebooks using dynamic enterprise compliance feeds via MCP.


Log in or sign up for Devpost to join the conversation.