-
-
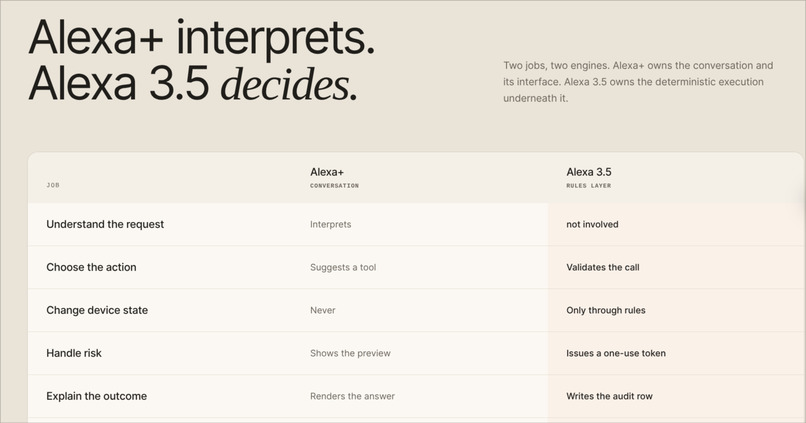
Contrast and comparison to Alexa+ latest version
-
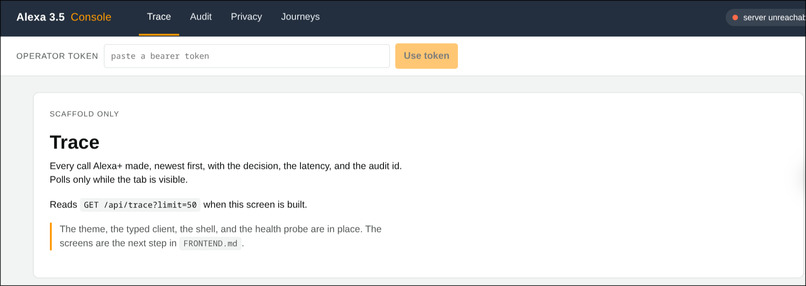
MCP Inspector
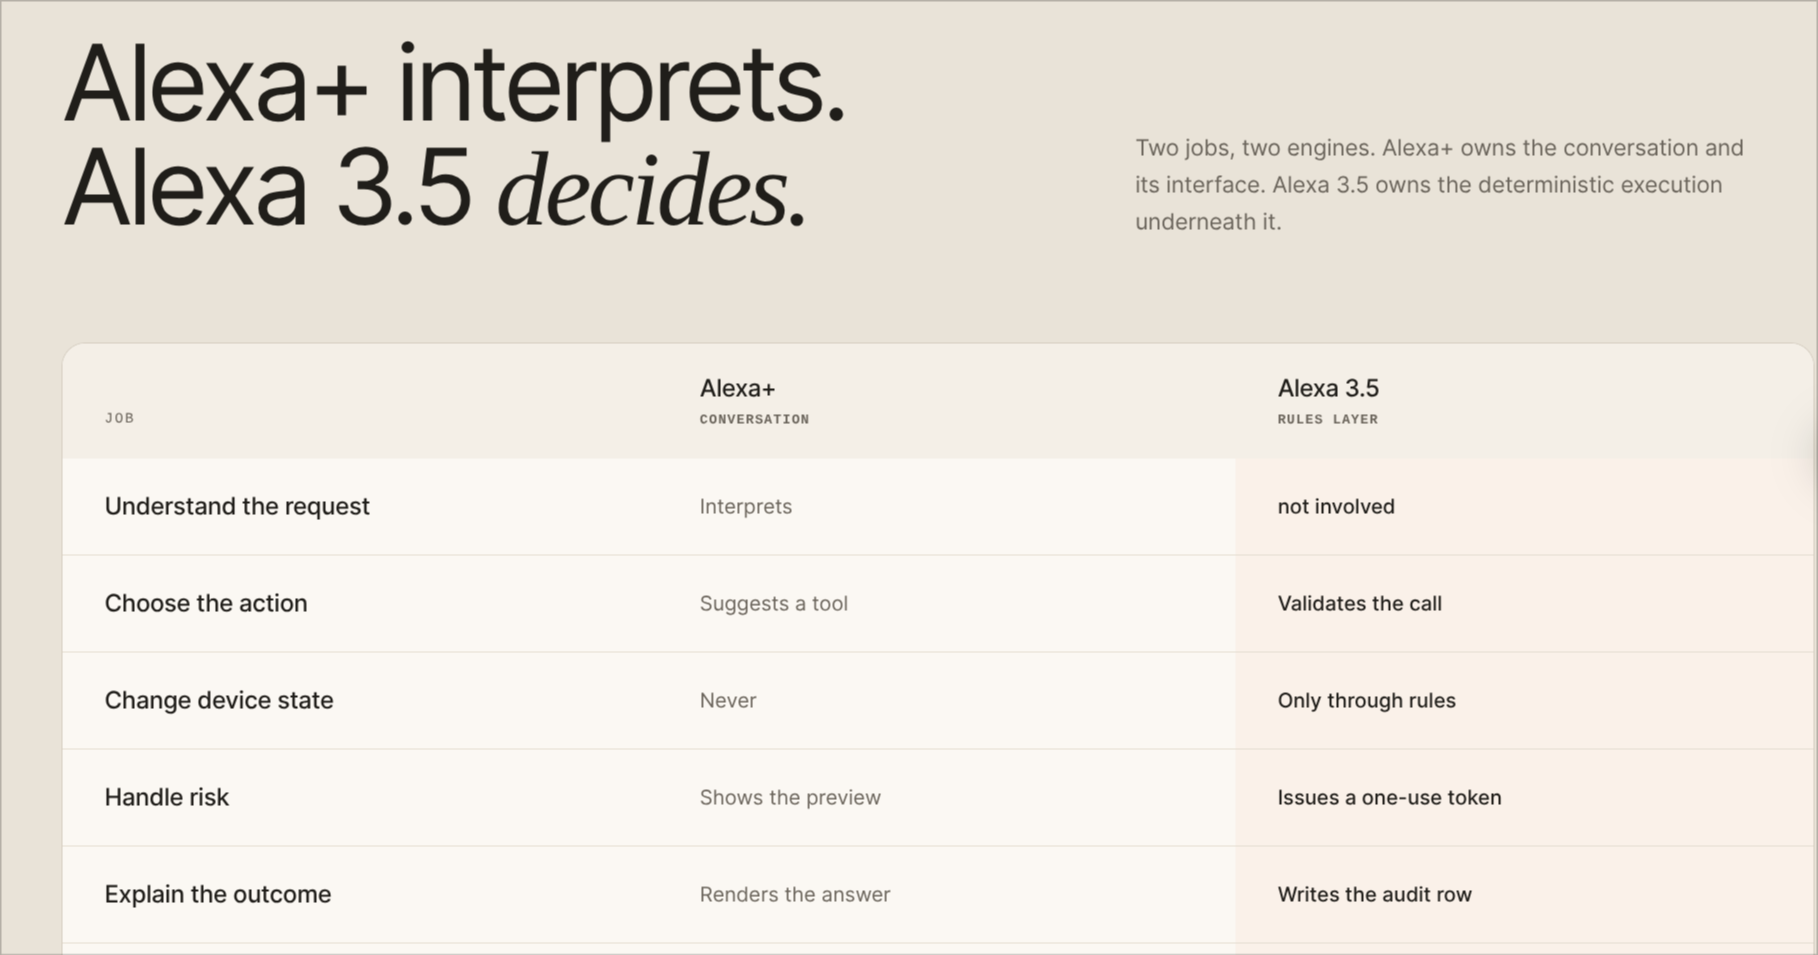
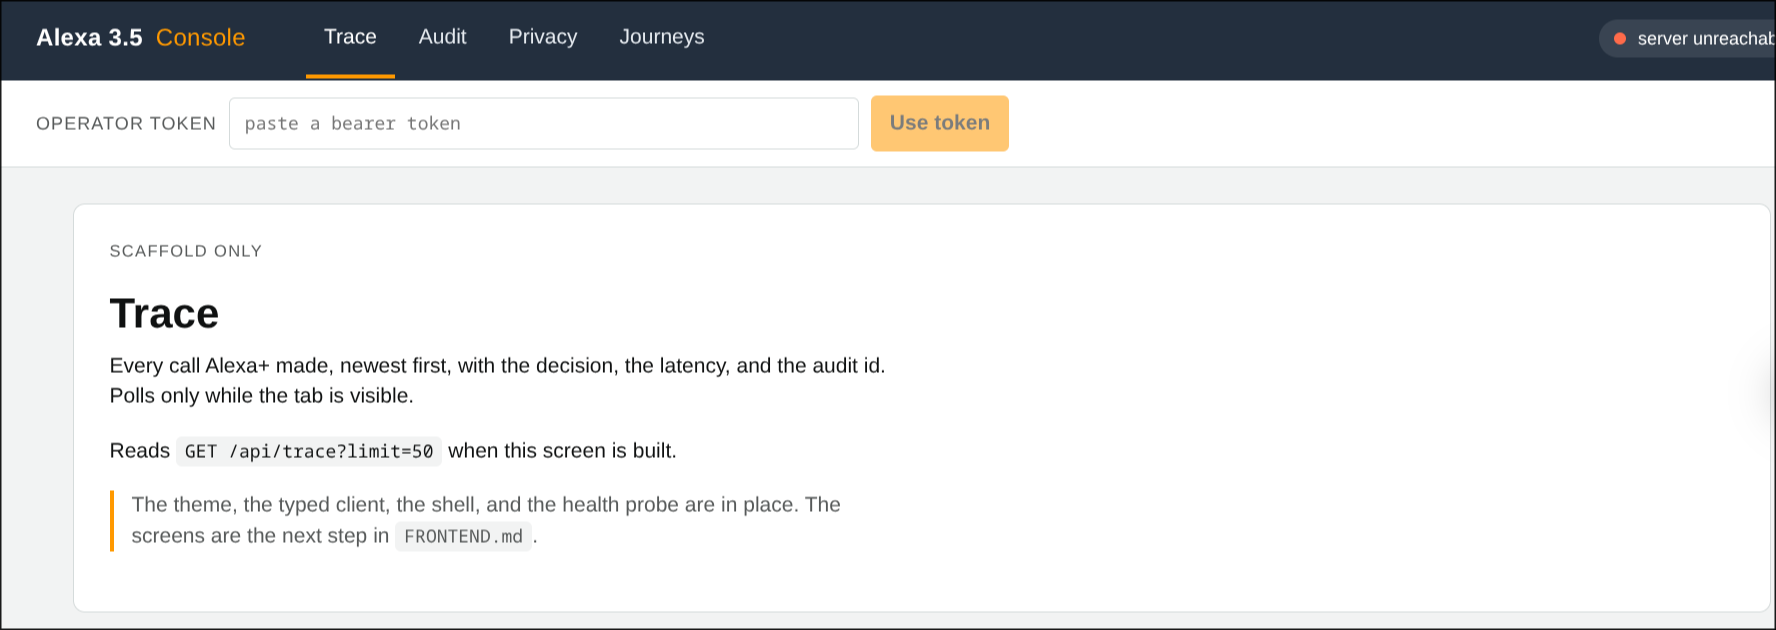
New Safety Layer Lets Alexa+ Act Without Letting AI Guess
Voice assistants like Alexa+ are moving from answering questions to booking, buying, and changing things, and a model's guess is a risky thing to trust with that. So I built Alexa 3.5, a self-hosted MCP server that sits behind Alexa+. Alexa+ interprets the request and picks one of eight tools. Every call then goes through a single path in Router.execute that checks authentication, scope, YAML parameter rules, and privacy. Risky actions return a preview and a single-use token tied to the exact parameters, and bad requests get a specific refusal with a follow-up hint. Everything lands in a hash-chained audit log, and reversible actions can be undone. The model interprets, and rules decide.
The hardest part was keeping all logic in that one path and making confirmations approve one exact action and nothing broader. I am proud of the shared execution path, the audit trail, and a design that complements Alexa+ instead of replacing it. I learned that safety comes from small, specific choices, and that friction should match risk. This is a hackathon prototype with simulated adapters, so next I want to integrate real devices and services, evaluate the full Alexa+ flow, and turn the pattern into a developer standard for high-risk MCP tools.


Log in or sign up for Devpost to join the conversation.