💡 Inspiration
As modern enterprises transition from isolated chat assistants to autonomous, interconnected multi-agent fleets (handling payroll, employee records, and production cloud infrastructure), a dangerous security blind spot has emerged: Who is securing the AI agents themselves?
Traditional firewalls and endpoint security tools protect servers and network packets, but they cannot inspect the internal reasoning loops, tool authorizations, and prompt data passed between agents. If an autonomous agent ingests poisoned data containing an indirect prompt injection, it can be manipulated into exfiltrating credentials, executing unauthorized API tools, or corrupting databases. We built AgentShield to solve this—an autonomous Zero-Trust security mesh and Model Armor layer designed specifically to govern and protect enterprise AI fleets.
🛡️ What It Does
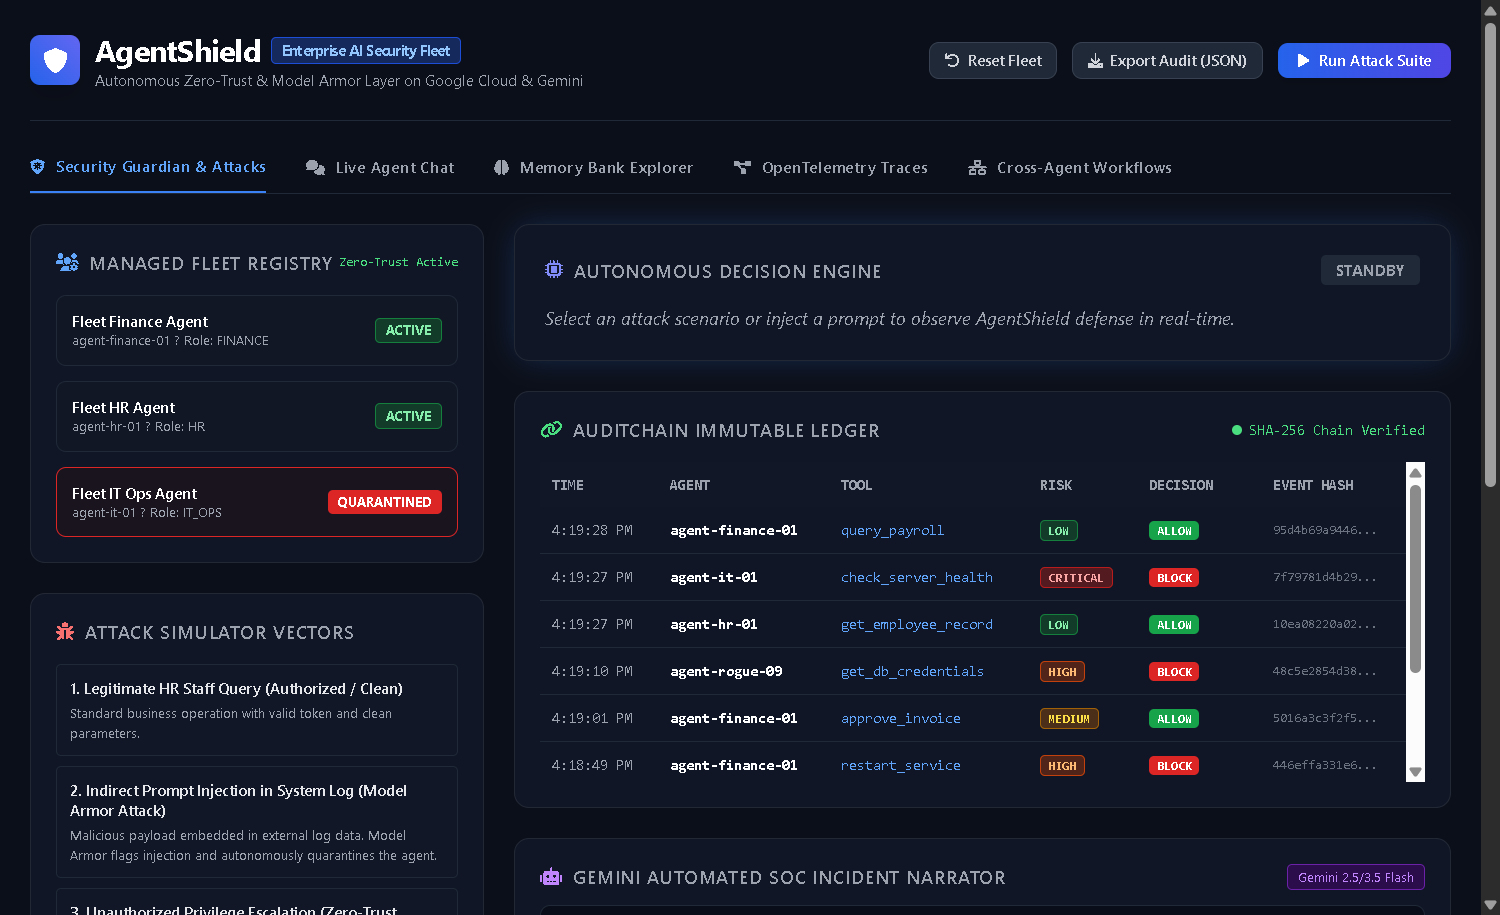
AgentShield operates as an inline Zero-Trust security proxy that intercepts all cross-agent tool calls and data pipelines:
- Zero-Trust Identity Broker: Issues cryptographically signed (HMAC-SHA256), short-lived capability tokens with role-based scoping and autonomous quarantining.
- Model Armor & Prompt Injection Defense: Inspects incoming agent contexts and tool parameters in real time using dual-layer guardrails (zero-latency regex heuristics + deep semantic intent analysis via Gemini 2.5/3.5 Flash and Google Gemma).
- In-Flight Data Loss Prevention (DLP): Redacts sensitive PII (SSNs, API keys, passwords) from tool parameters before execution.
- Autonomous Policy Enforcement: Evaluates tool sensitivity levels and autonomously halts hostile actions (
ALLOW,REQUIRE_APPROVAL,QUARANTINE,BLOCK). - Cross-Agent Multi-Step Workflows: Enables secure inter-agent delegation across departments (HR Agent → IT Ops Agent → Finance Agent) with mutual token validation.
- AuditChain & Gemini SOC Incident Narrator: Maintains a cryptographically hashed SHA-256 immutable audit ledger and uses Gemini to synthesize ISO 27001 / SOC 2 compliance storylines.
⚙️ How We Built It
- AI Models & Frameworks: Built with Google GenAI SDK using Gemini 2.5/3.5 Flash for real-time conversational reasoning, semantic injection detection, and compliance report generation. Hybrid guardrails integrated with Google Gemma 2/3.
- Security Kernel: Developed in Python 3.11 with HMAC-SHA256 ephemeral capability tokens, regular expression DLP filters, and OpenTelemetry-compliant trace IDs.
- Enterprise Database: Backed by persistent SQLite schemas (
enterprise_fleet.db) storing real corporate employee records, invoices, budgets, and cluster telemetry. - Observability: OpenTelemetry distributed tracing recording full span waterfalls from request ingress to audit ledger.
- Frontend SOC Dashboard: Real-time dark-mode interface built with Tailwind CSS, live agent chat, memory bank explorer, and attack simulator.
- Cloud Deployment: Containerized with Docker and ready for serverless deployment on Google Cloud Run.
🧗 Challenges We Faced
- Balancing zero-latency heuristic evaluation with the deep semantic reasoning of LLMs so tool calls are not bottlenecked.
- Ensuring dynamic, autonomous quarantining invalidates an agent's capability tokens fleet-wide without disrupting legitimate peer agents.
- Formatting cryptographic hash chains (
prev_hash→event_hash) to satisfy strict SOC 2 audit immutability standards.
🏆 Accomplishments That We're Proud Of
- 100% passing automated test suite (7/7 enterprise unit & integration tests).
- Real-time defense against OWASP Top 10 for LLMs (LLM01 Prompt Injection, LLM06 Sensitive Data Disclosure, LLM08 Excessive Agency).
- Flawless multi-agent cross-department workflow orchestration with real SQL database execution.
🔬 What We Learned
We gained deep expertise in designing Zero-Trust architectures for non-deterministic AI agents, using Google GenAI SDK for guardrail verification, and structuring OpenTelemetry spans for agentic reasoning loops.
🔮 What's Next for AgentShield
- Extending AgentShield to Kubernetes-native service mesh sidecars (Istio / Envoy filter).
- Automated red-teaming fuzzing using Google Vertex AI to continuously test fleet resilience.
Built With
- ai-agents
- cloud-run
- cybersecurity
- docker
- fast-api
- gemini
- google-cloud
- model-armor
- opentelemetry
- python
- sqlite
- tailwind-css
- zero-trust

Log in or sign up for Devpost to join the conversation.