-
-
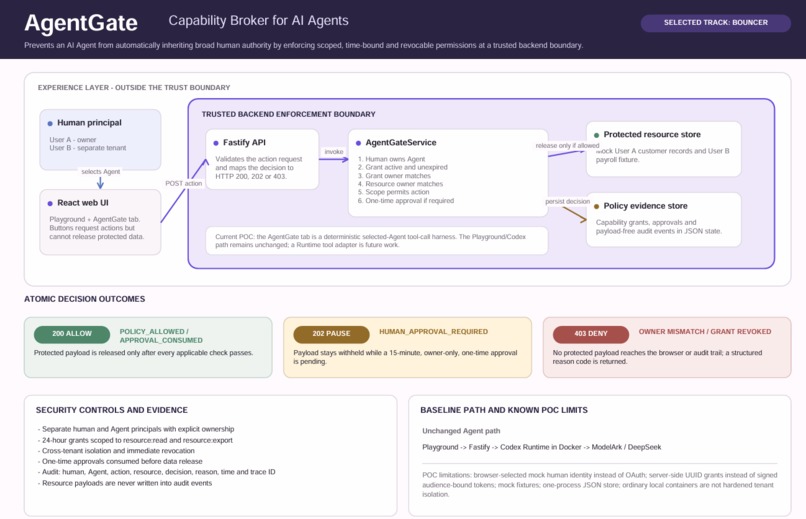
Architecture diagram
Inspiration
AI agents can act on behalf of users, but giving an agent unrestricted access creates serious security risks. AgentGate explores how agents can receive only the authority they actually need.
What it does
AgentGate is a capability broker for AI agents. It enforces delegated permissions at a trusted backend boundary, including resource ownership, scoped access, human approval for sensitive actions, immediate revocation, and an auditable decision trail.
Our demo shows a User A agent successfully accessing User A's resource, being blocked from User B's resource, requiring one-time human approval for an export, and being immediately denied after its capability is revoked.
How we built it
We built AgentGate with a TypeScript/Node.js backend and React frontend, integrated with the hackathon Agent Launchpad, Codex runtime, Docker, and BytePlus ARK. Protected resource requests are authorized server-side rather than trusting the agent or frontend.
Challenges and learnings
The main challenge was separating human identity, agent identity, delegated authority, and resource ownership while keeping revocation and approval decisions consistent. We learned that agent security needs enforcement outside the model itself: prompts are not an authorization boundary.
Built With
- access-control
- agent-security
- ai-agents
- audit-logging
- authorization
- byteplus-ark
- capability-security
- codex-cli
- cybersecurity
- docker
- fastify
- human-in-the-loop
- llm-security
- multi-tenant
- node.js
- react
- rest-api
- typescript
- vite
- vitest

Log in or sign up for Devpost to join the conversation.