Inspiration
AI agents can chain together many tool actions. Each action may look safe on its own, but the full sequence can expose sensitive data or send it to an untrusted destination.
Agent Action Firewall puts an enforcement gate directly before tool execution.
What it does
Agent Action Firewall is a self-hosted MCP execution gate for AI agents.
Before an agent executes a tool action, the firewall evaluates:
- Action type
- Data sensitivity
- Destination trust
- Privilege level
- Input provenance
- Prior actions in the same session
It returns one of three decisions:
- Allow
- Require confirmation
- Block
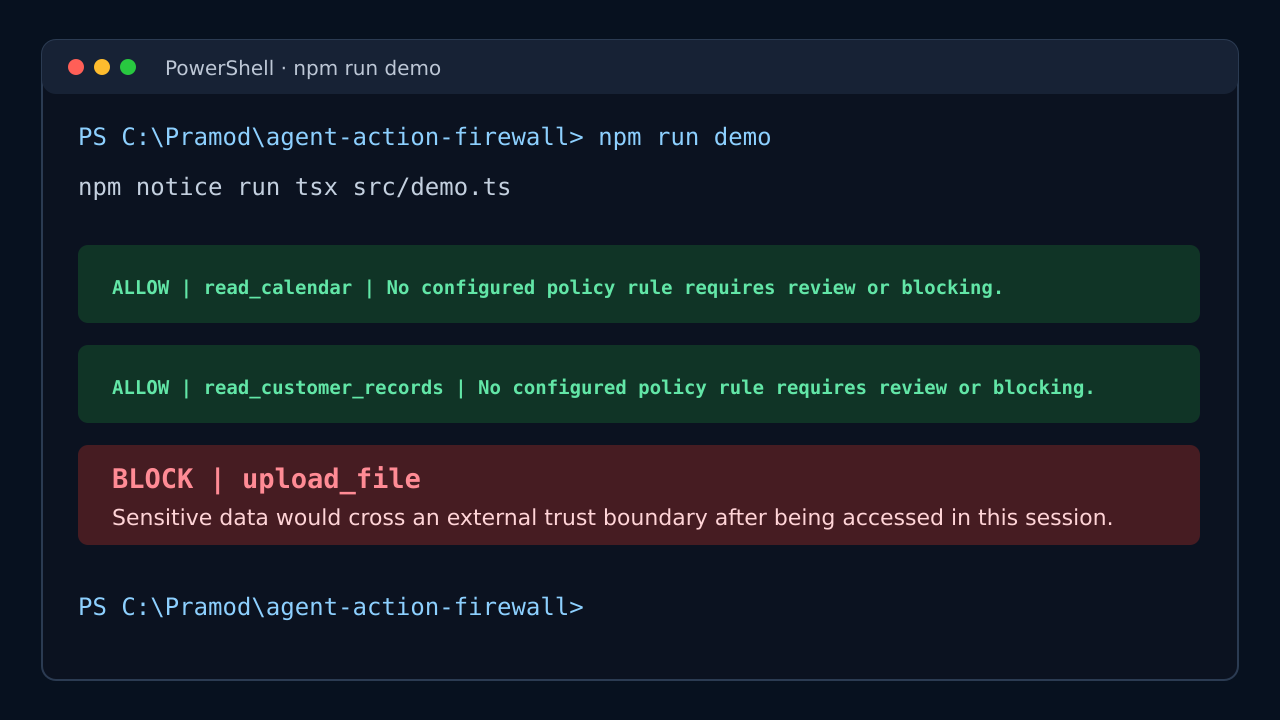
The firewall blocks a risky external export after sensitive data has already been accessed in the same session. It blocks the action before the tool runs.
How we built it
We built the service with TypeScript and Node.js.
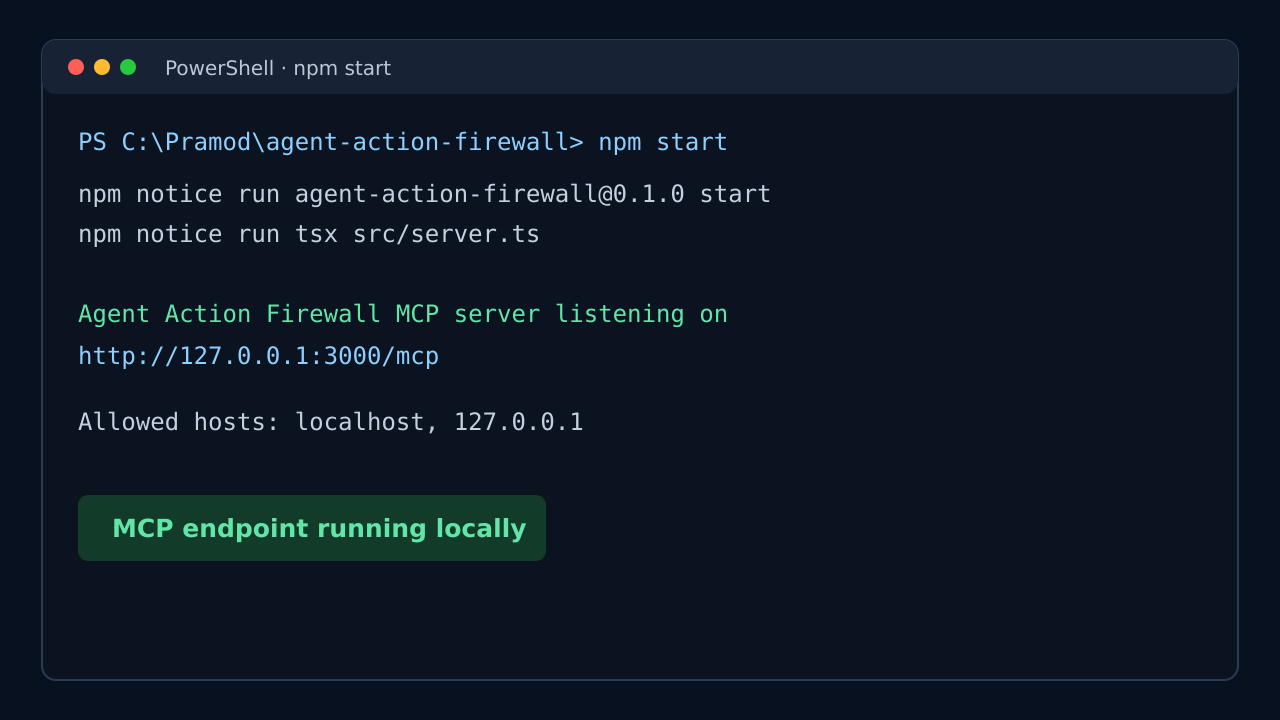
The MCP server runs locally at:
http://127.0.0.1:3000/mcp
The policy engine records structured action metadata and uses trusted session history to evaluate multi-step risk. The execution gate stays separate from agent reasoning. An agent proposes an action. The firewall evaluates it. The protected tool only runs after an allow decision.
The project includes:
- An MCP endpoint
- A policy engine for allow, review, and block decisions
- Session-history protection
- Guarded execution that prevents blocked tools from running
- Automated tests and a terminal demo
Challenges we ran into
Single-action rules are not enough. A normal read can become risky when a later action exports the data to an external destination.
We also had to prevent model-authored session identifiers from changing trusted session history. Review-only attempts and failed protected callbacks must not become executed history.
Accomplishments that we're proud of
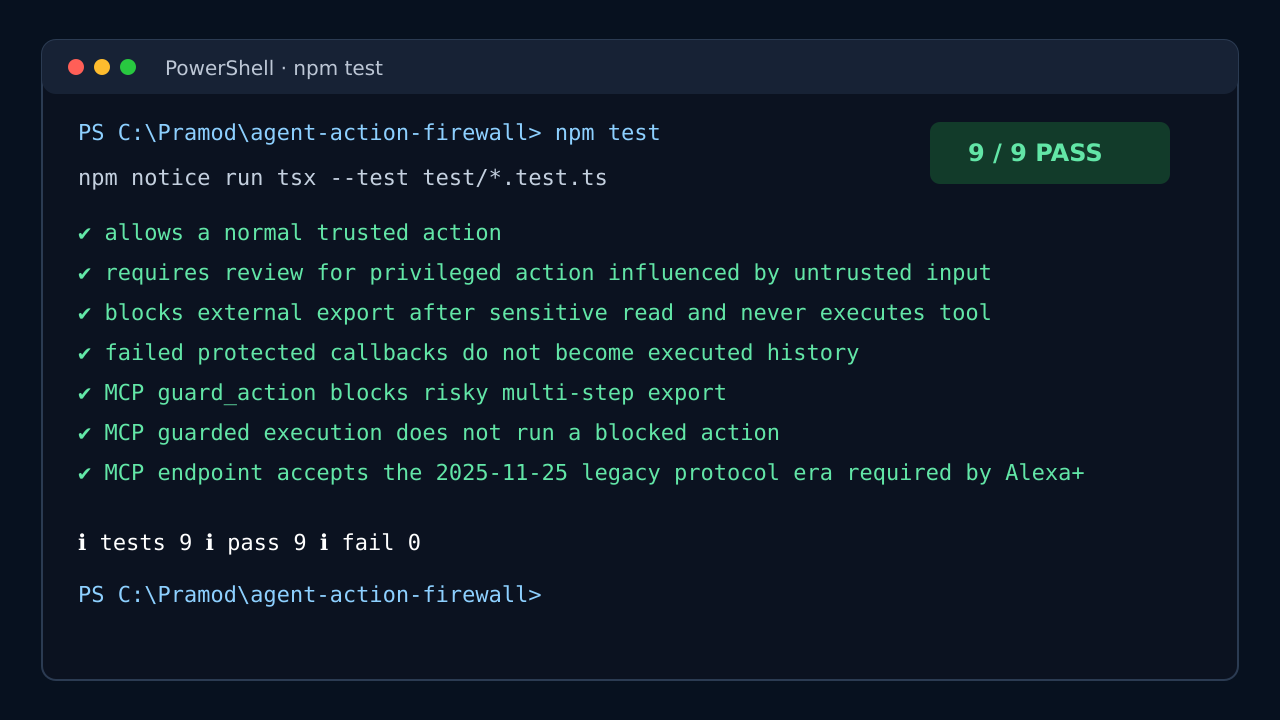
The project passed all 9 automated tests.
The tests verify that the firewall:
- Allows normal trusted actions
- Requires review for privileged actions influenced by untrusted input
- Blocks sensitive external exports before tool execution
- Preserves trusted session identity
- Blocks risky multi-step actions through the MCP endpoint
- Supports the MCP
2025-11-25protocol era required for the Alexa+ track
What we learned
Agent safety needs enforcement at execution time. Detecting a problem after a tool runs is too late.
Session history, data flow, and destination trust change the meaning of an action. A clear policy decision also makes the system easier to test, review, and explain.
What's next for Agent Action Firewall
Next steps include:
- Connect the MCP server to an Alexa+ agent workflow
- Add more policy rules for sensitive data and external destinations
- Add human approval for review decisions
- Build reproducible attack scenarios
- Measure false positives and false negatives
Built With
- alexa+
- azurecontainerapps
- docker
- github
- mcp
- node.js
- streamable-http
- typescript

Log in or sign up for Devpost to join the conversation.